• category
Every post filed under this category, newest first.
Attack surface drift leaves inventories out of step with what attackers see. Learn the 7 causes, the signals to watch and a 30-day plan to close the gap.
Domain spoofing detection needs more than DMARC. Five signals that surface lookalike domains early, how to triage them, and what gets a takedown.
NCSC hacktivist alert: find the exposed control panels, remote access and lookalike domains attackers scan for. See what to check first.
Unknown asset discovery, explained: the seven places forgotten internet-facing assets hide, how to attribute them and who fixes them. See the process.
Glasgow Council cyber attack explained: what was confirmed, why supplier-hosted assets go unmapped, and how to find yours. See the practical steps.
Attack surface monitoring software compared by what matters: discovery, noise, human triage, takedowns and reporting. See the 9 questions to ask vendors.
ServiceNow vulnerabilities are only half the problem. Learn how to inventory every exposed instance, test safely and respond in 72 hours.
PaperCut NG vulnerability response beyond patching: fingerprint exposed print servers, check for compromise and prove it’s closed.
Digital ID security risks explained through the real attack paths: stolen sessions, spoofed portals and supplier gaps. See how to monitor and respond.
Shadow IT risks explained from the attacker’s view: 7 exposures, how each one is discovered from outside, and what to fix first. See how to find yours.
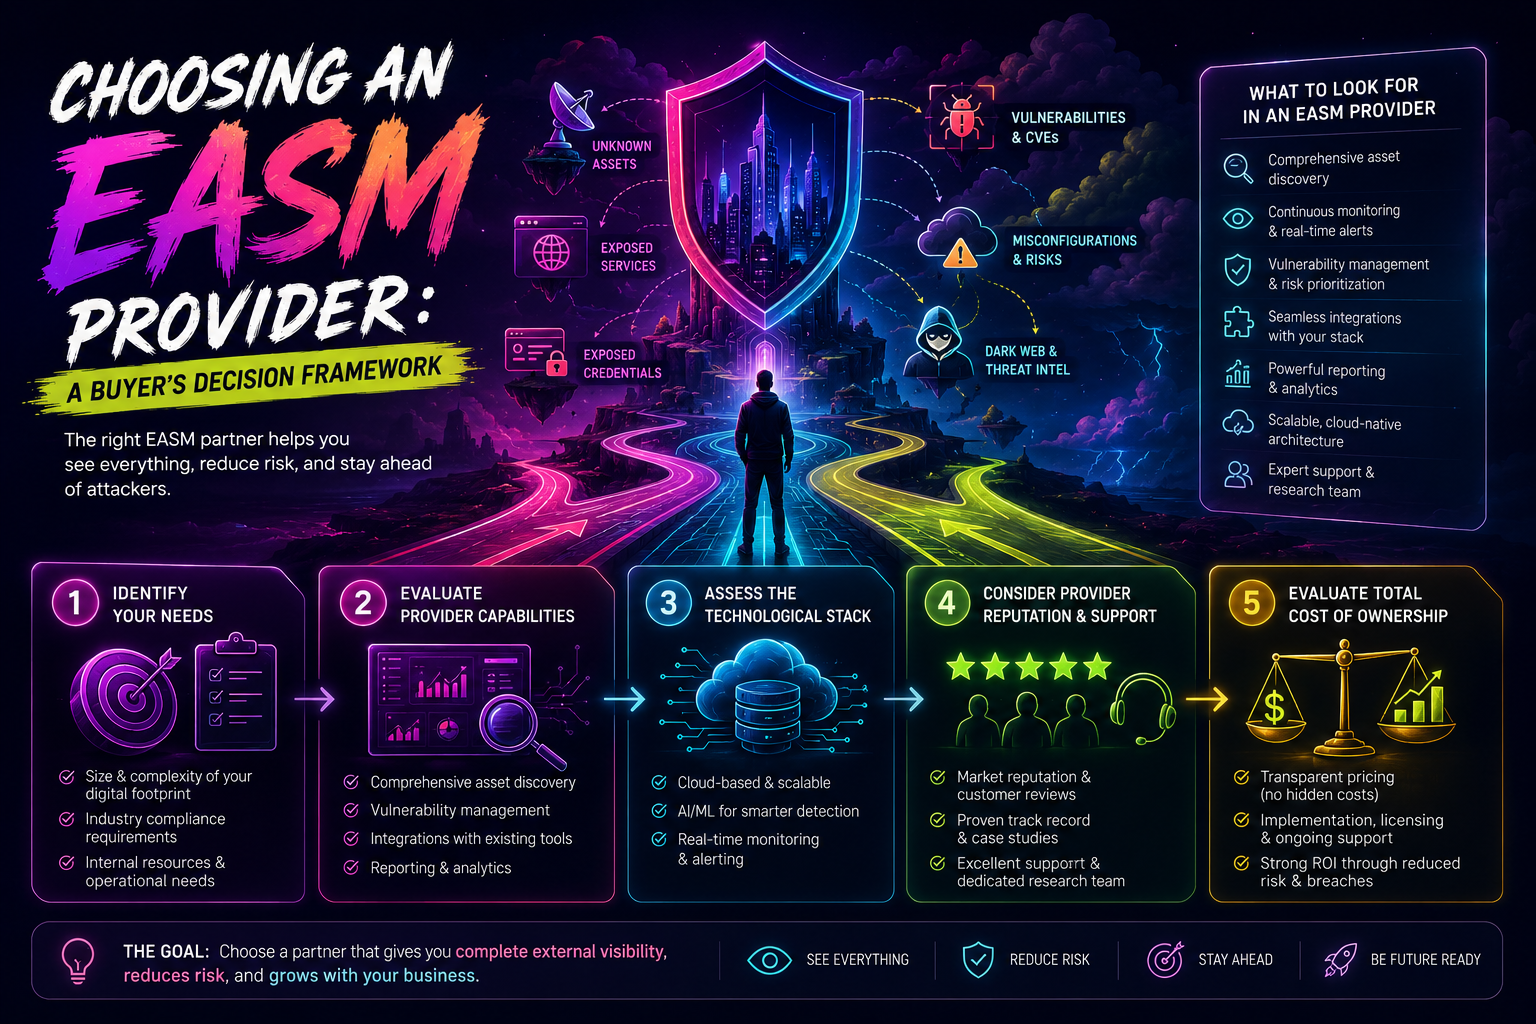
Explore a comprehensive framework to select the right External Attack Surface Management (EASM) provider, ensuring robust cybersecurity and safeguarding digital assets.
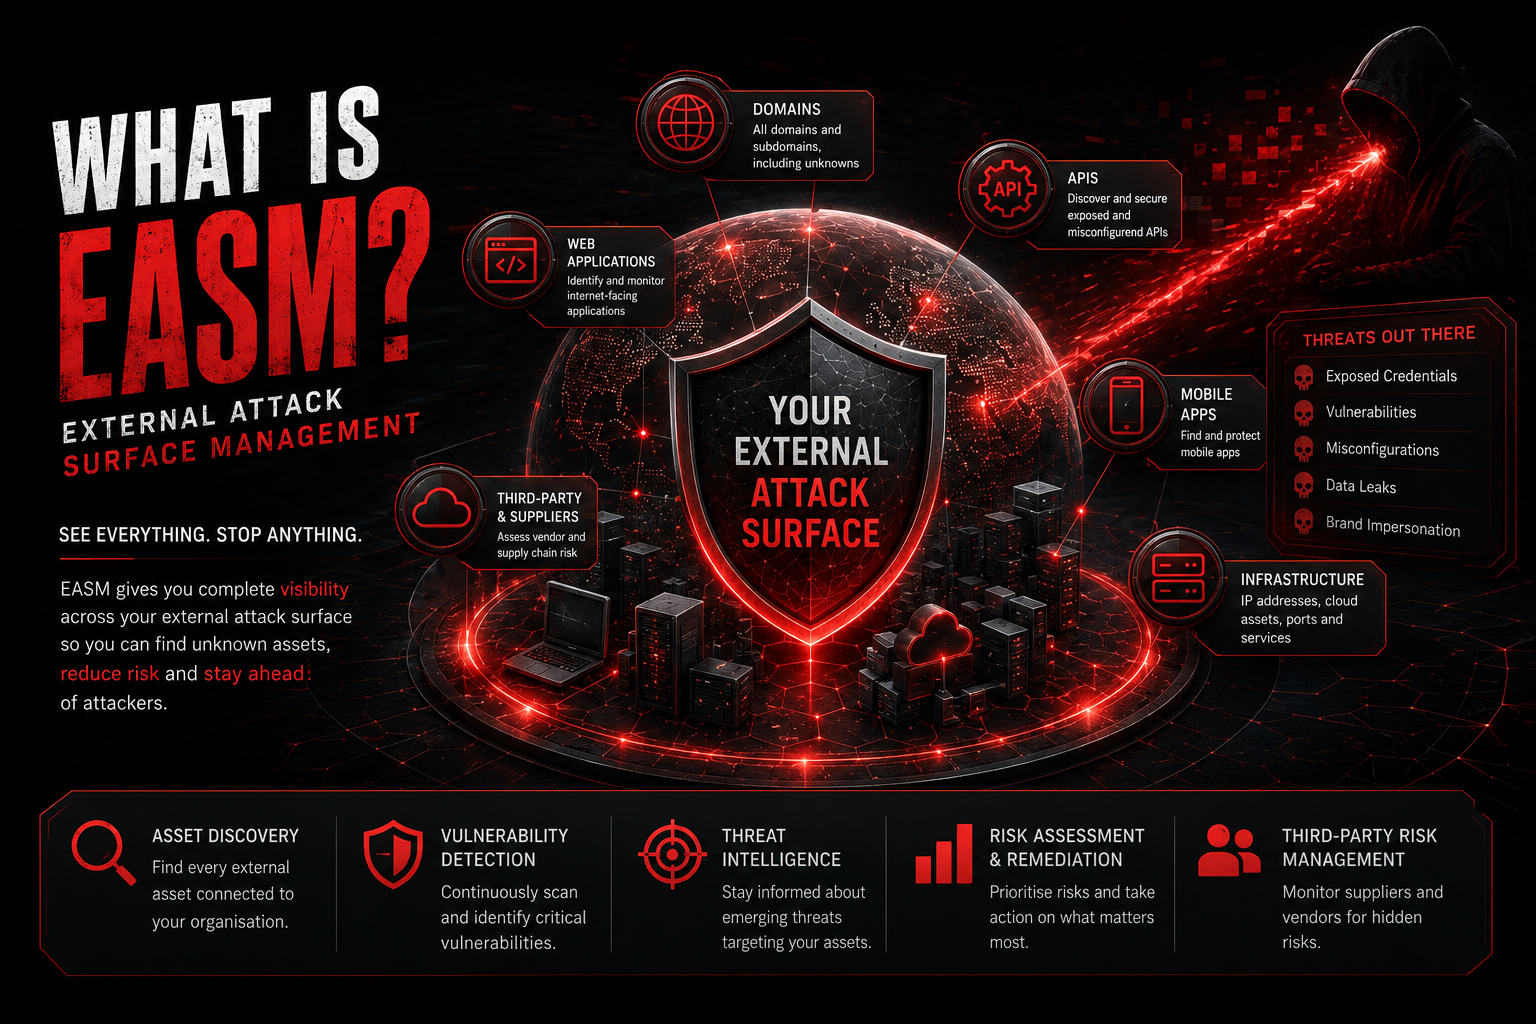
In the world of cybersecurity, External Attack Surface Management (EASM) is a proactive strategy to monitor and manage digital vulnerabilities. Learn why it’s essential for protecting modern enterprises.
Learn about the factors affecting the cost of External Attack Surface Management (EASM) and how to choose a value-driven solution.
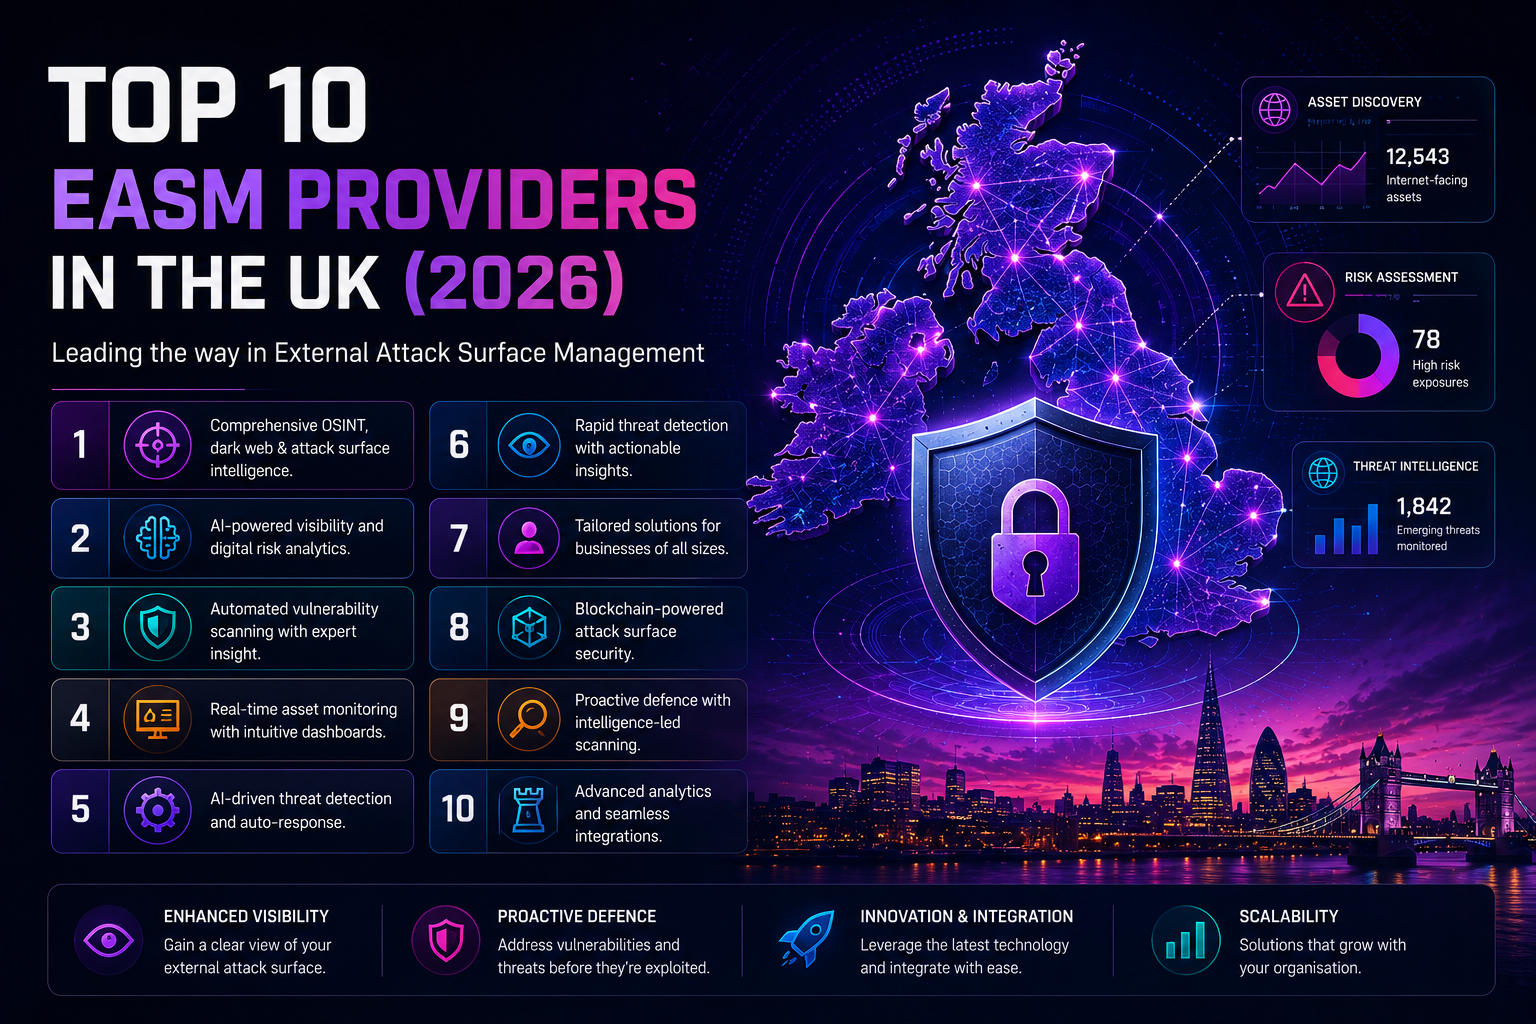
Ten real EASM providers UK organisations can buy in 2026, including our own platform, with what each does, its UK presence and how to choose.
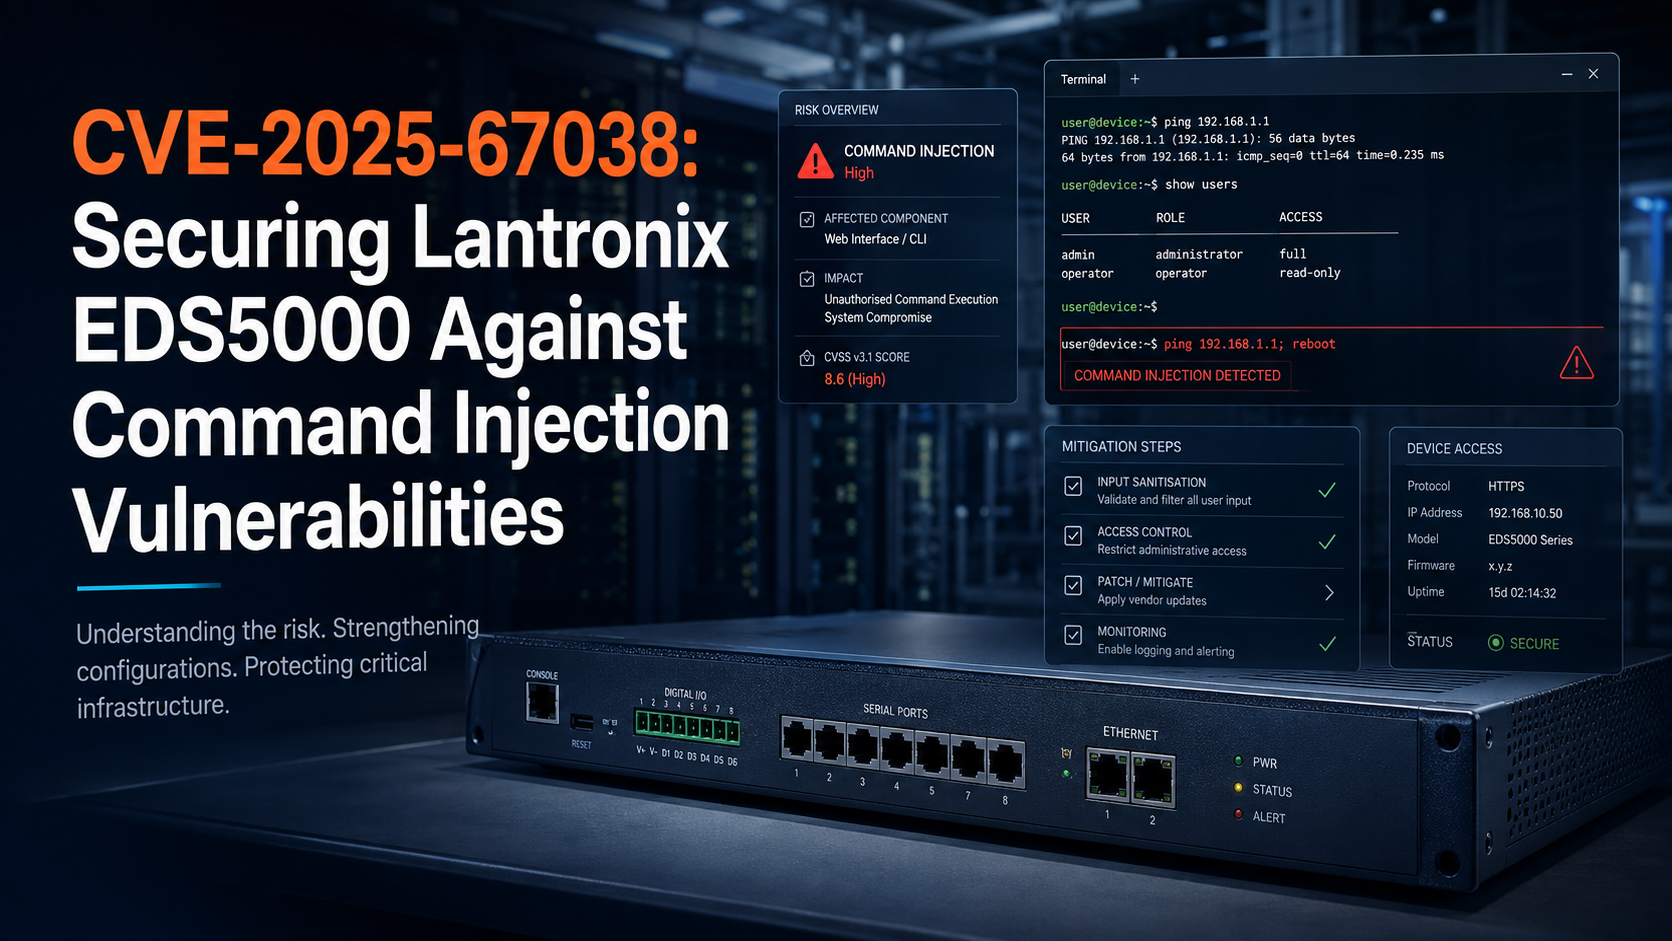
CVE-2025-67038 is a critical command injection vulnerability affecting the Lantronix EDS5000 series. Learn about the risks and mitigation strategies.
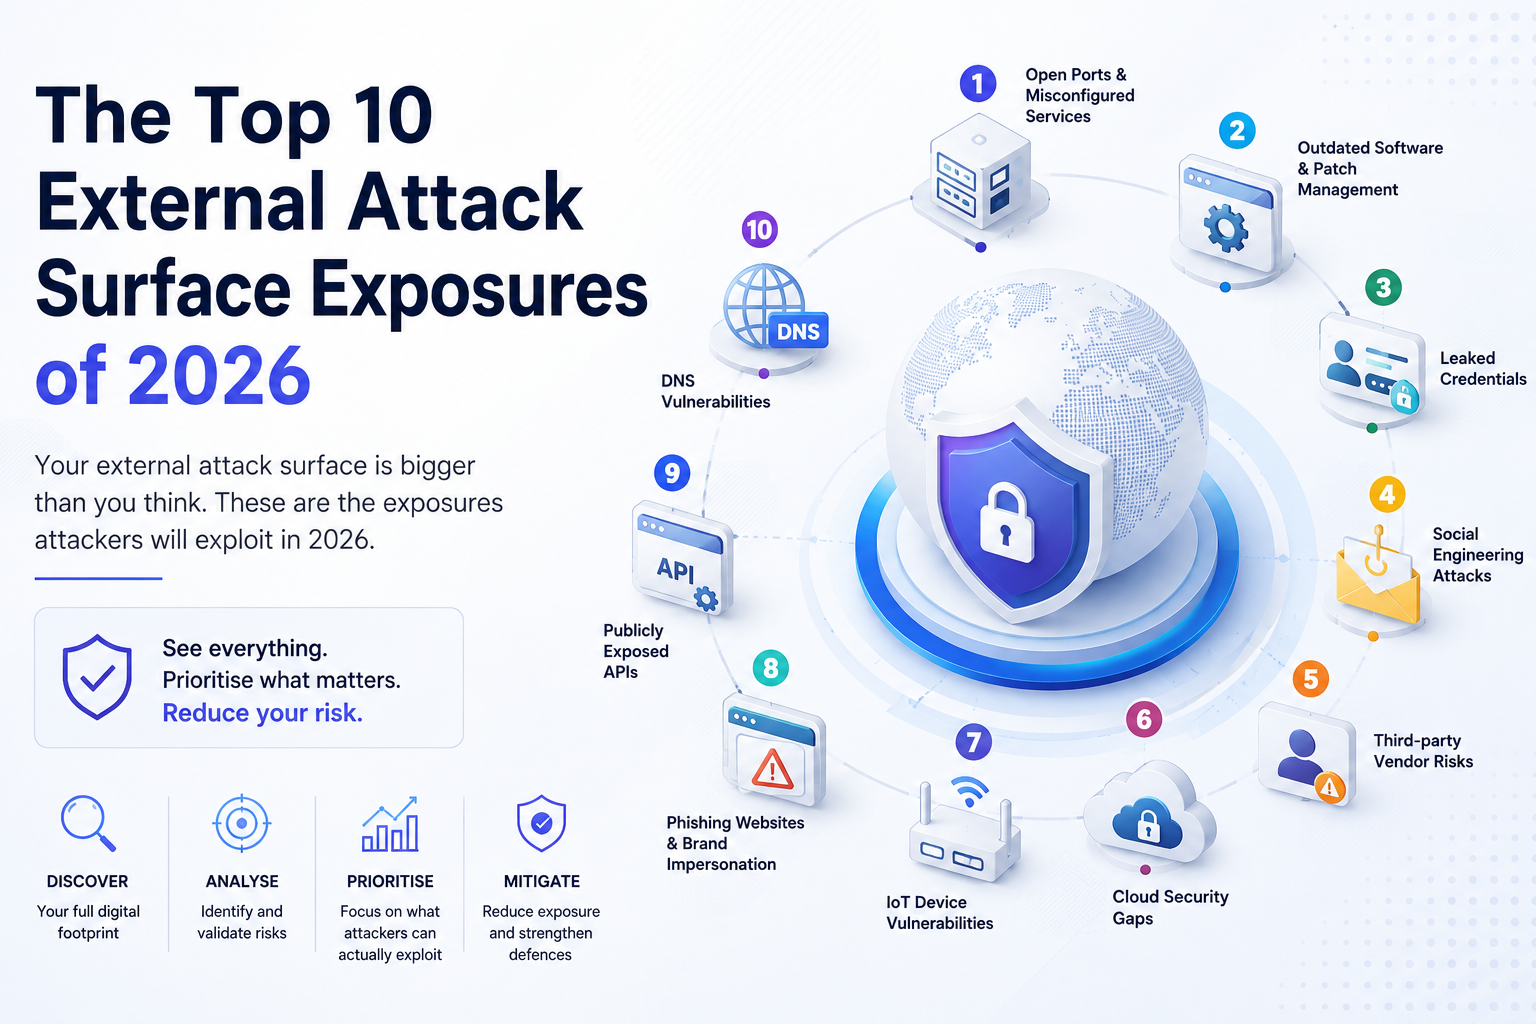
Explore the top 10 external attack surface exposures in 2026 and how to mitigate these cybersecurity risks.
Explore the critical Joomla JCE CVE-2026-48907 vulnerability, its impacts, and protective measures for organisations.
Explore the FortiBleed mass Fortinet credential-harvesting campaign, its impact, and how to defend against such threats.
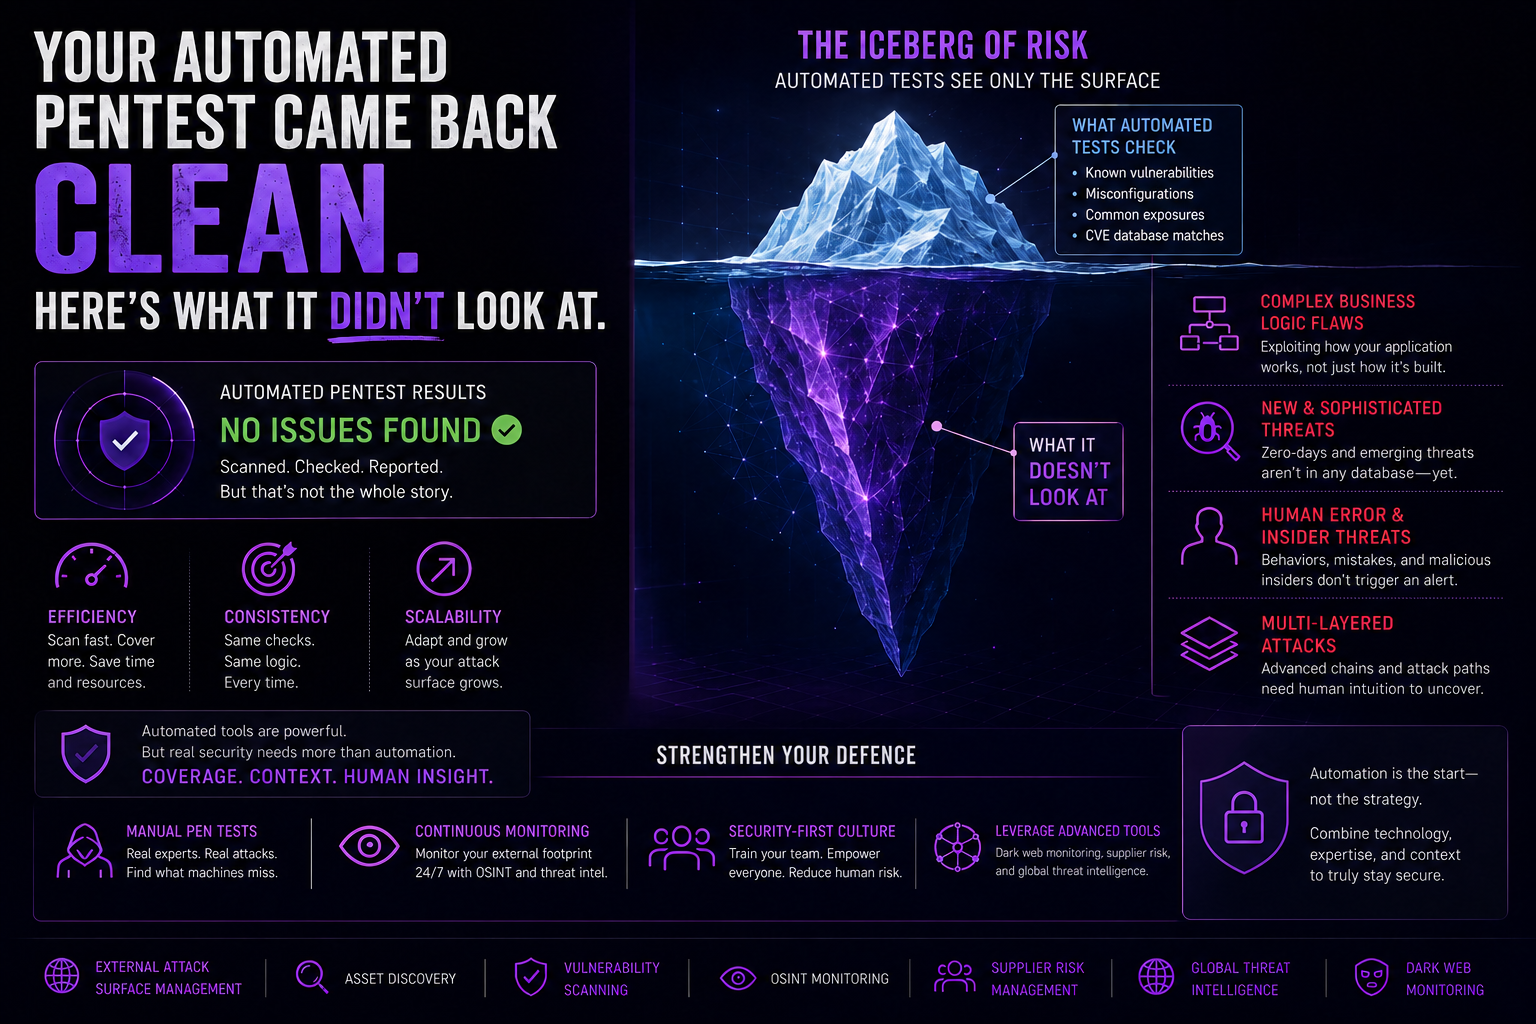
Explore the unseen gaps in automated pentesting and discover how continuous EASM can enhance your cybersecurity strategy.
Explore how the World Cup scam wave reveals vulnerabilities in domain protection, and learn effective EASM strategies for brand safety.
A zero-day vulnerability in Cisco’s SD-WAN has been exploited, stressing the urgency of proactive cybersecurity measures as per NCSC’s warnings.
Megalodon backdoored 5,561 GitHub repos in six hours in May 2026 using stolen tokens, likely from infostealer logs. What happened and how to respond.
CVE-2026-9082 is a critical Drupal vulnerability. Exploitation began within 48 hours of disclosure. Act now to protect your sites.
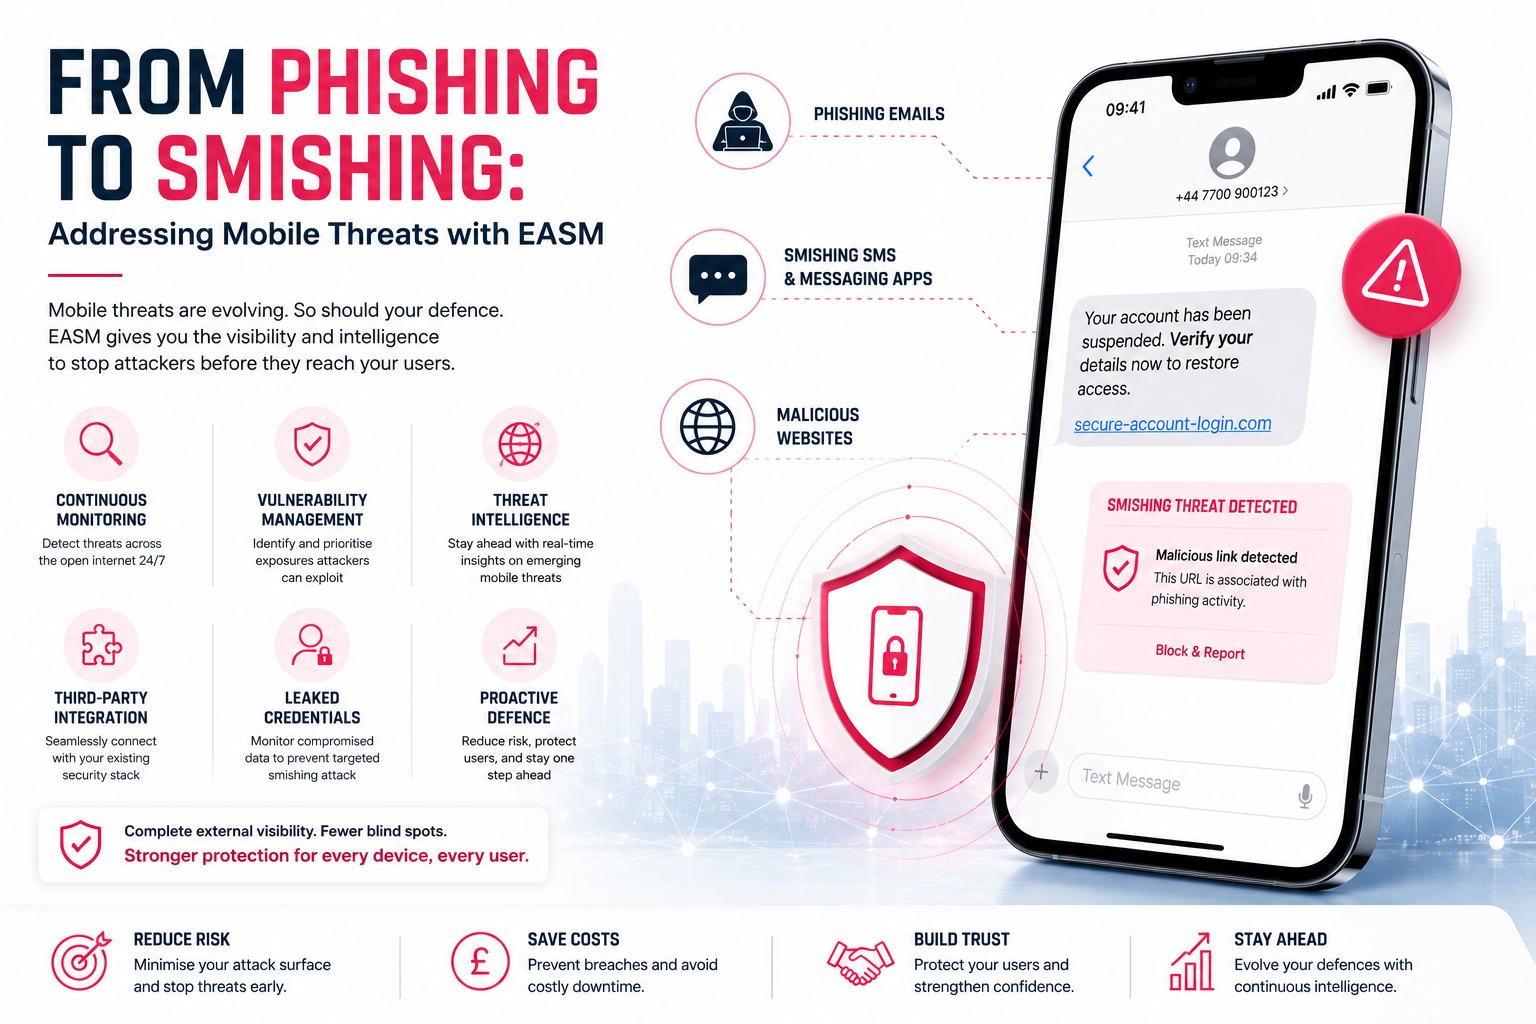
Explore the evolution from phishing to smishing in mobile threats and discover how External Attack Surface Management (EASM) provides proactive protection.
Explore cybersecurity predictions for 2026, focusing on how External Attack Surface Management (EASM) will play a pivotal role in shaping the future of digital security.
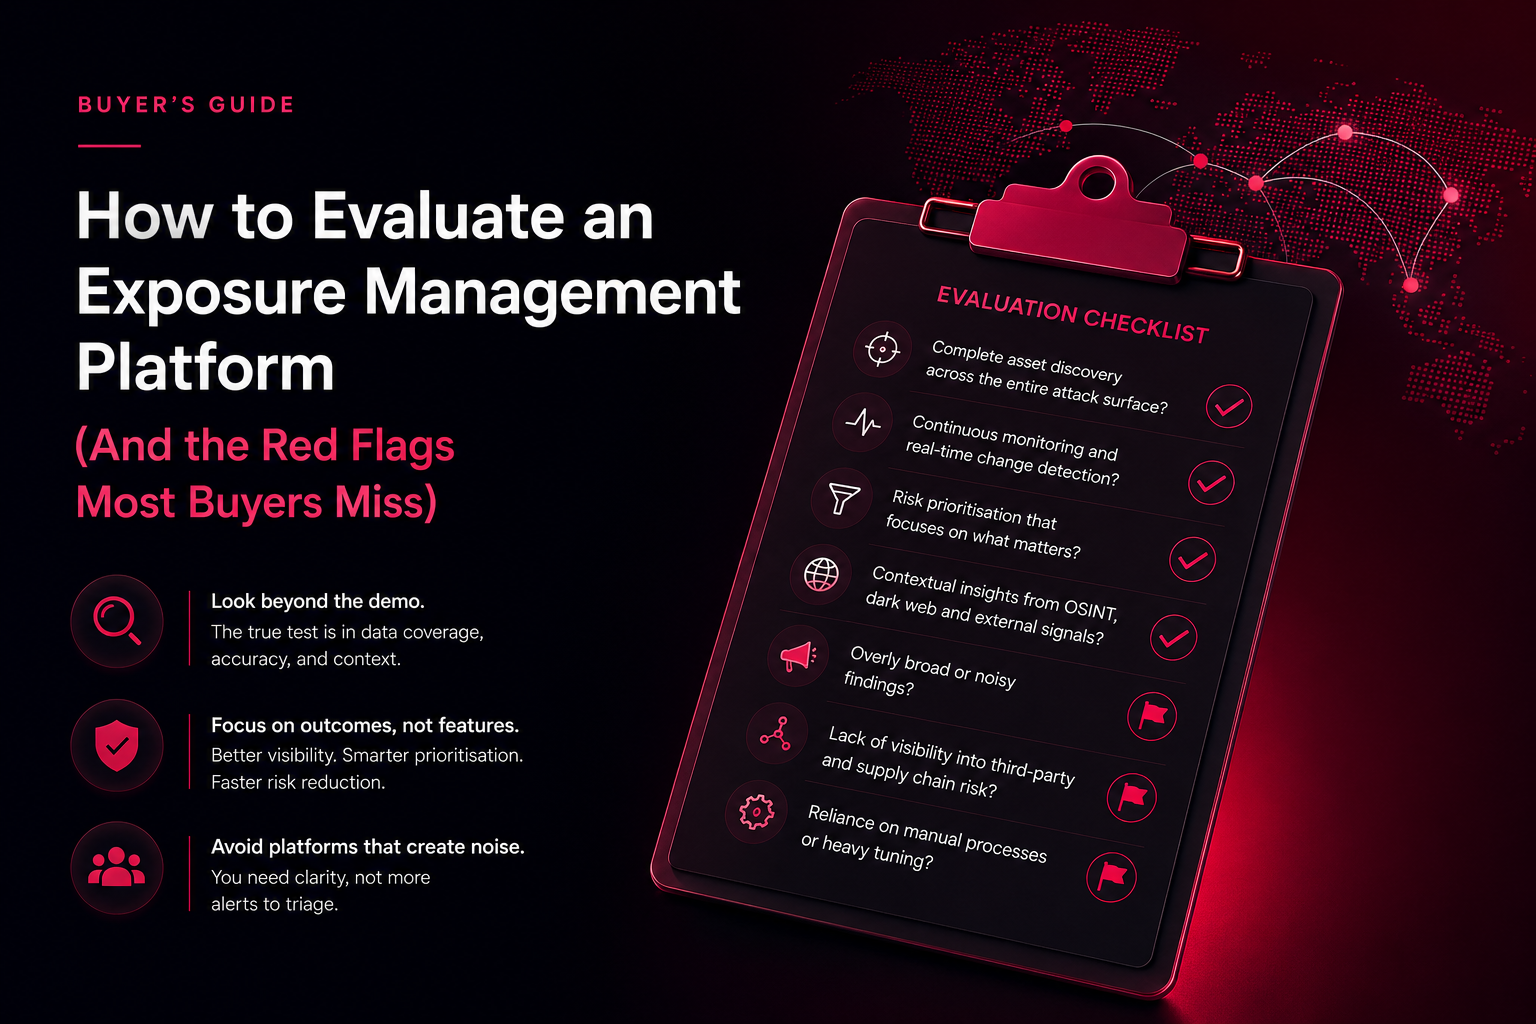
A contrarian buyer’s guide to evaluating exposure management platforms, highlighting the critical features and red flags most buyers overlook.
Nyx is the new AI security consultant inside DarkInvader. It analyses every risk on your external attack surface, explains what it means, and tells you what to ask next.
Explore how combining AI and EASM transforms real-time threat intelligence and modern cybersecurity practices, enhancing detection, prediction, and response.
Exploring how External Attack Surface Management (EASM) strengthens security posture in 2026 through continuous monitoring, real-time threat detection, risk management, and incident response.
This blog discusses the critical role of Telegram monitoring in External Attack Surface Management, highlighting the importance of monitoring Telegram to anticipate cyber threats and protect digital assets effectively.
Exploring how EASM can address the surge in trojanized gaming tools and RATs by enhancing detection, automation, and collaboration.
Explore how AI vulnerabilities increase attack surfaces and the role of External Attack Surface Management in mitigating these risks. Discover strategies to protect your organisation.
Explore how External Attack Surface Management (EASM) safeguards AI systems against vulnerabilities, ensuring robust cyber resilience.
The React2Shell vulnerability allows unauthenticated remote code execution on React and Next.js frameworks, posing a significant risk to enterprise attack surfaces. This blog explains the nature of the threat and how EASM platforms like DarkInvader help organisations discover, prioritise, and remediate these vulnerabilities in real time, ensuring enhanced protection for their digital assets.
Credential theft via npm preinstall attacks is an emerging and widespread threat in software supply chains. Attackers exploit npm package preinstall scripts to silently steal credentials, affecting over 25,000 repositories. External Attack Surface Management (EASM) helps organisations discover vulnerable packages, monitor exposed assets, and respond quickly to such threats. DarkInvader’s EASM platform provides vital visibility and mitigation capabilities to safeguard credentials and reduce attack surface risks today.
SOC 2 compliance is all about ongoing security and risk management, and EASM makes this process significantly easier. By regularly scanning for risks, identifying external vulnerabilities, and helping teams address exposures before they become security incidents. Instead of treating compliance as a one-off project, EASM enables organisations to maintain continuous security readiness, which auditors, customers, and security teams all appreciate.
Aligning with DORA doesn’t have to be a headache. With EASM, financial institutions can confidently support DORA’s requirements, from ICT risk management to third-party oversight and incident reporting. By continuously monitoring your digital footprint and reducing vulnerabilities, EASM isn’t just a compliance tool – it’s your ally in building resilience.
EASM platforms provide organisations with real-time visibility, risk assessment, and vulnerability management for their external-facing assets. These capabilities directly support compliance with key ISO 27001 clauses, including risk assessment, risk treatment, monitoring, and technical vulnerability management. By integrating EASM into your compliance strategy, you can streamline accreditation, simplify audits, and maintain ongoing alignment with the standard.
browse by tag
browse by category
browse by year
free trial
Try DarkInvader Pro free. No payment details required.