• category
Every post filed under this category, newest first.
Fraudulent data requests, from forged police emails to fake DSARs, trick staff into handing over data. See the exact checks that stop them.
Manchester Airports cyber attack: what was stolen, why WiFi and number plate data matters, and a 10-day plan to check your own exposure.
CVE-2026-19478 is a critical code injection vulnerability in GitLab. Rated 9.4, it permits unauthenticated deletion of public projects. GitLab has released patches for affected versions.
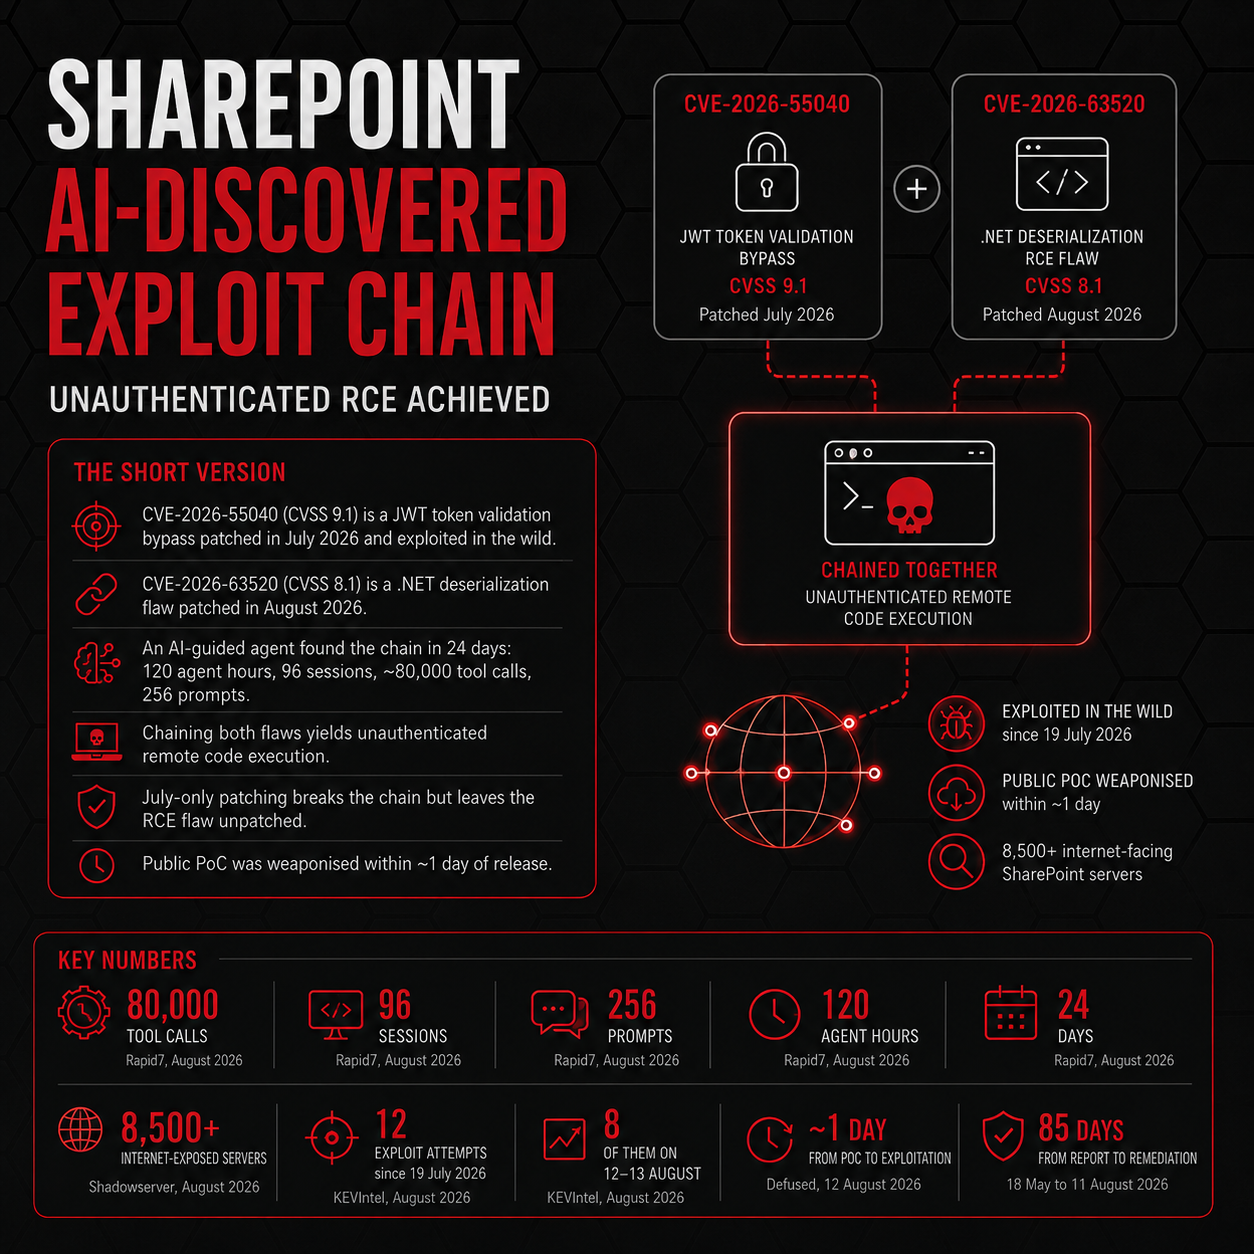
In cybersecurity, anticipating future trends means understanding current discoveries. The agent-discovered SharePoint vulnerability chain illuminates how exploitation could evolve and how organisations can prepare.
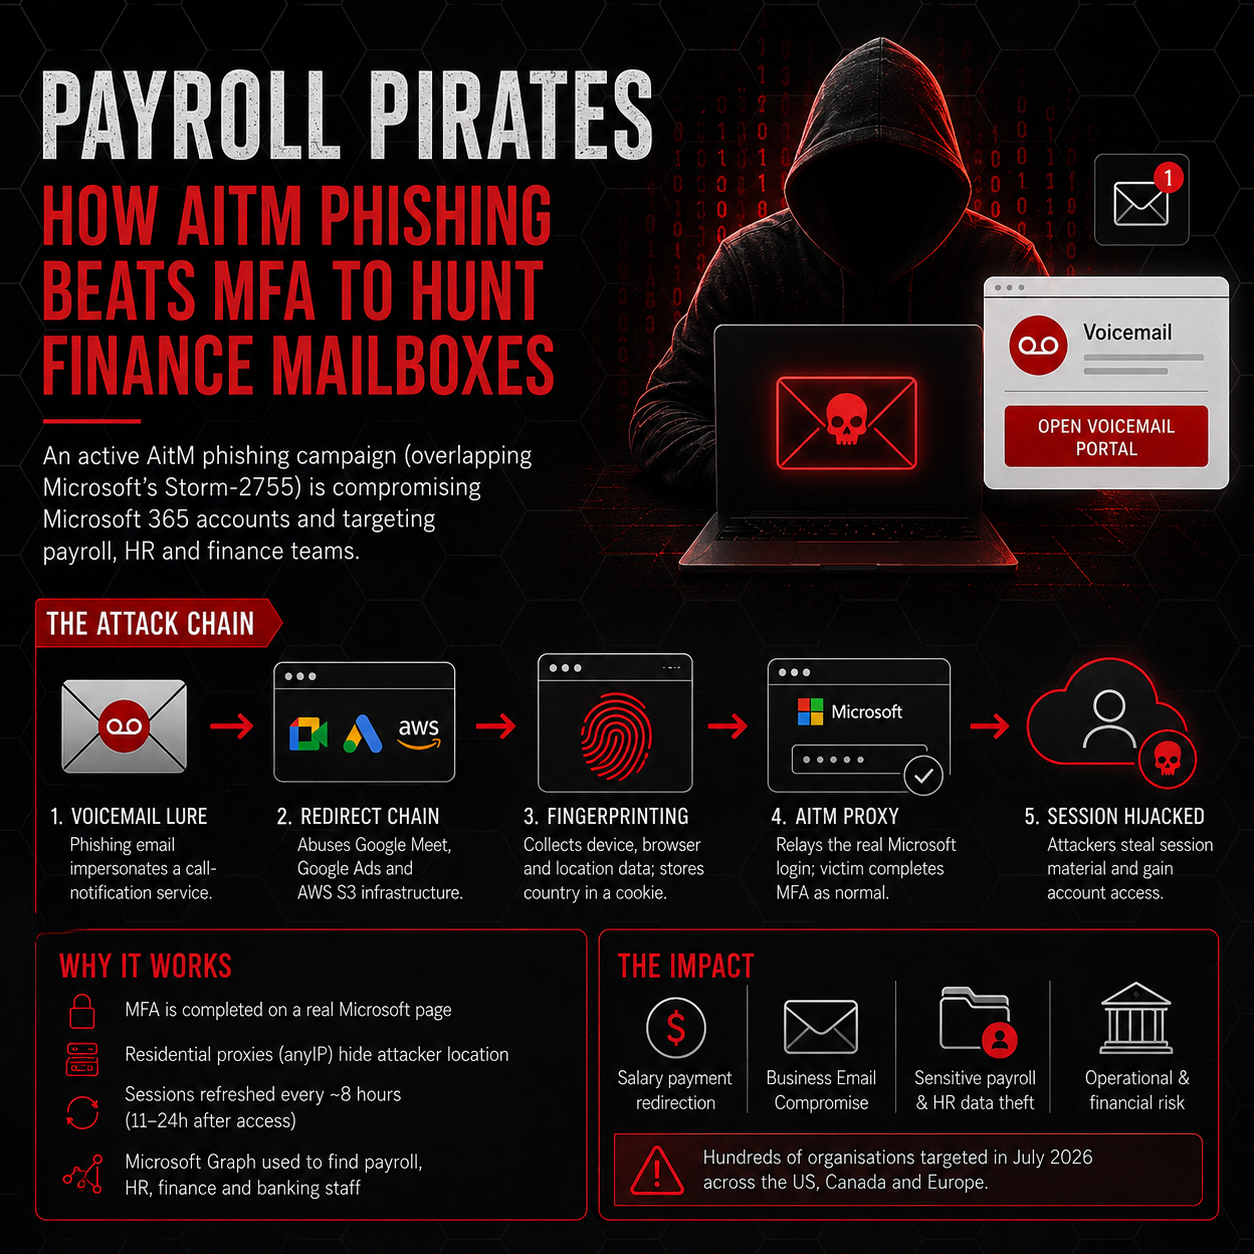
An exploration of the "Payroll Pirates" AitM phishing campaign, highlighting its techniques and providing guidance for detection and defense.
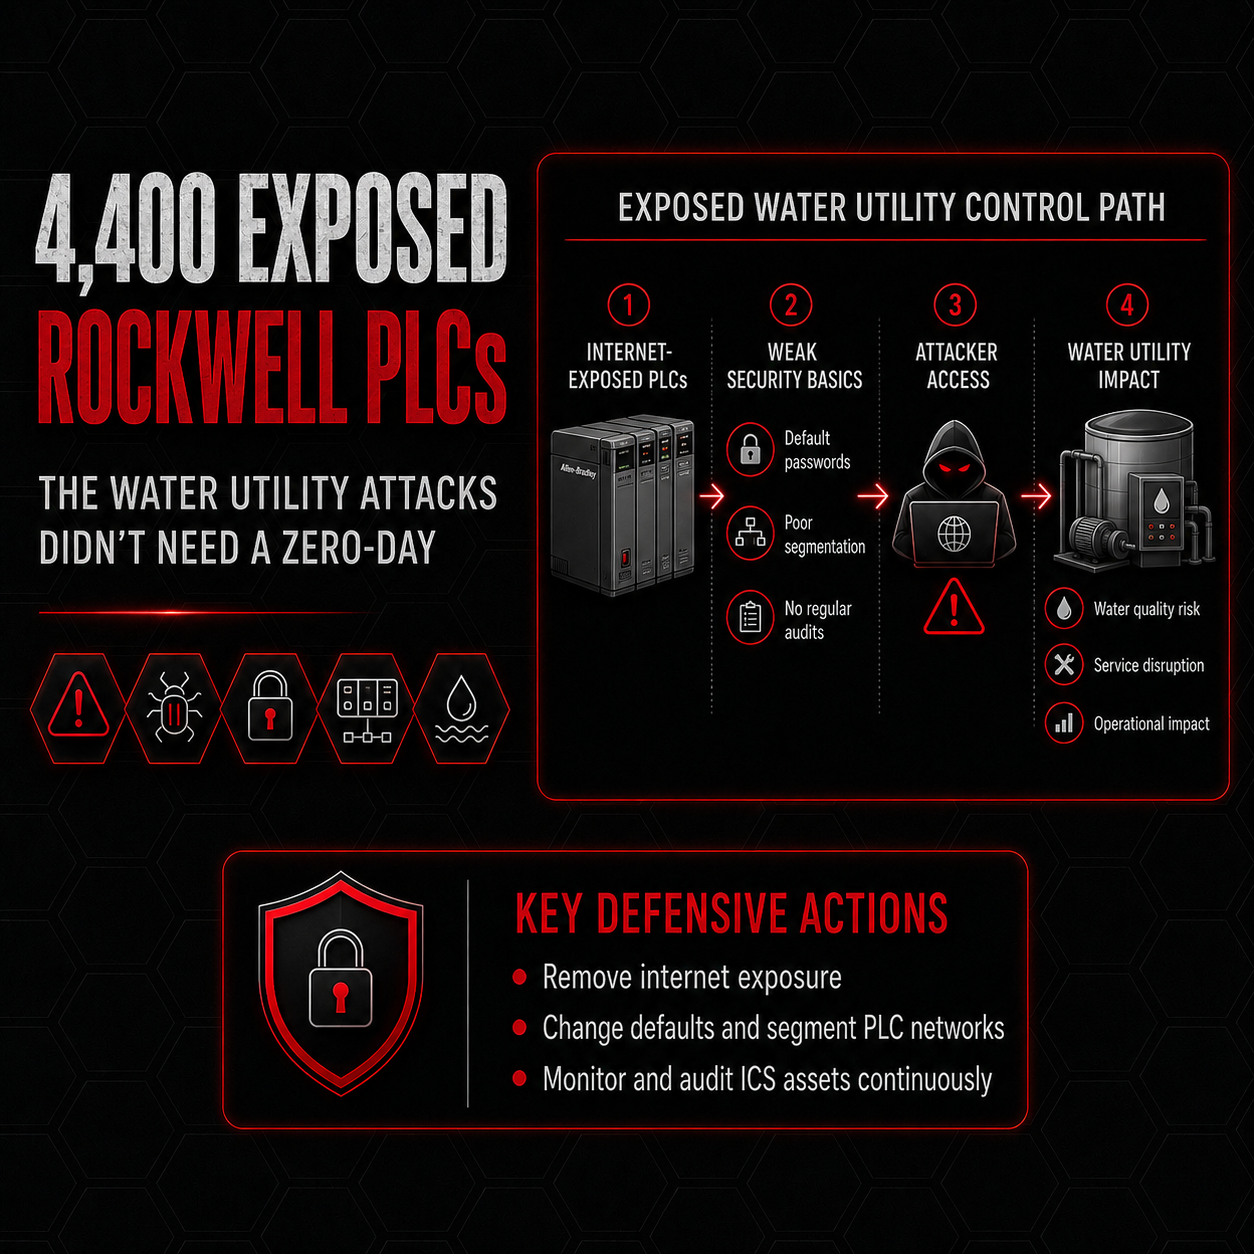
Forescout’s Vedere Labs identified 4,407 internet-exposed Rockwell Automation/Allen-Bradley PLCs in an August 2026 scan, including 22 in cities affected by coordinated attacks on US water utilities. Attackers achieved disruption without exploiting any vulnerability: they changed IP addresses and set passwords on controllers that were already publicly reachable.
Cl0p ransomware exploits vulnerabilities in PTC Windchill and FlexPLM, enabling unauthenticated RCE and data theft. Critical patching is essential.
NCSC alerts to Russian state-backed LAUNDRY BEAR zero-click attacks on Zimbra email platforms. Learn detection signals and patching priorities for your organisation.
Explore the StrikeShark campaign, a sophisticated cyber threat targeting businesses. Learn how to protect exposure with advanced cybersecurity strategies.
A Dutch raid uncovered a staggering 17 million routers used in cybercrime, revealing a quiet economy where criminals exploit connectivity without users knowing. Learn how it happened and how to protect yourself.
Explores CVE-2026-0257, a critical vulnerability in VPNs that could allow forged cookie attacks, posing serious security threats.
EASM is a vital tool in defending businesses against sophisticated phishing techniques by continuously monitoring internet-facing assets, discovering vulnerabilities, and providing threat intelligence to proactively reduce risks.
Discover how to protect your organisation from PyStoreRAT, a malware threat hiding within fake GitHub repositories. Learn about its workings and how to safeguard your systems effectively.
In summary: a large scale Russian-speaking phishing campaign registered thousands of fake travel and hotel booking websites to steal payment card data. Artificial intelligence is making such scams easier, faster and more convincing. Businesses must recognise the importance of their external attack surface, including look-alike domains and fake websites, and employ platforms like DarkInvader’s EASM solution to monitor, detect and respond effectively.
Hackers have changed again. They are quieter, younger, and more strategic. They automate their work, manipulate people, and blend into digital systems with unnerving precision. In this new era of cybercrime, defence is not about waiting for the breach; it’s about anticipating it. The best protection now comes from visibility and intelligence. With DarkInvader’s EASM platform, organisations can finally see their attack surface the way hackers do, and act before the damage is done.
Attack surface is far more than just networks and servers. It includes people, open source intelligence, social media, and the business brand itself. Attackers can cause real damage by impersonating a brand, tricking customers, and eroding trust. DarkInvader believes that what can be attacked is part of the attack surface, and that includes the brand. With DarkInvader’s EASM platform, businesses can monitor for fake websites, reduce false positives, and respond quickly to protect their reputation.
Social engineering attacks like the one that hit M&S keep happening because businesses rely too heavily on awareness training and technical controls. The real fix lies in smarter processes: ones that assume attackers will try to manipulate staff, and make it significantly harder for them to succeed. Policies like mandatory callbacks, multifactor authentication, and manager alerts are not just helpful. They are essential.
The rapid development of artificial intelligence (AI) and machine learning has brought numerous benefits to businesses, but it has also introduced new risks. One of the most alarming technological advancements is the creation of deepfakes: realistic but fabricated audio, video, or images generated by AI. Deepfakes are no longer a niche curiosity; they have the potential to cause significant damage to businesses, from financial fraud to reputation damage. In this blog, we’ll explore the risks that deepfakes pose to businesses and outline strategies that can help reduce these risks.
This blog summarises the Neiman Marcus data breach after the Snowflake account hack and discusses the implications and next steps for those affected.
This blog highlights the most recent news of the NHS hospital attack and how London hospitals may take many months to resolve. The effects of this attack fear cancer patients have operations cancelled after NHS cyber-attacks.
Ticketmaster have been hacked in breaking news today. Alongside the BBC, their sensitive data is at risk on hundreds of millions of users. This blog highlights what happened, how it happened and what you can do to protect yourself if you think you may be affected.
Recently, one of the largest ransomware gangs, ‘LockBit,’ has been dismantled in an operation named Operation Cronos, led by the NCA, the FBI, Europol, and multiple other countries.
This blog breaks down how Threat Actors choose their victims and all the tactics they use. This blog provides a helpful insight of how to spot these methods and avoid them.
This blog outlines unmasking threat actors and protecting your business and employees from these risks and threats. Have a read of the ways you can protect your employees, through staff training and education.
This blog summarises who the LockBit Ransomware gang are, how they operate and what makes them differ from other cyber gangs.
This blog covers cyber criminals and how they stay anonymous online and the dangers of this to online users.
This blog post covers the new ransomware group: Akira and how they have become known in cybercrime for their Ransomware Group.
This blog post covers the Capita Hack and what happened when a severe data breach hit them. This blog explains what customers can do to protect themselves against these breaches.
This blog post covers the Monopoly Attack and the consequences of the attack & how organisations can protect themselves from these types of attacks.
This blog post covers the recent ‘CACTUS’ Ransomware strain and what organisations can do to protect themselves from this attack. Have a listen to our ThreatBite to hear expert advice from our consultants.
This blog covers the recent hack of Dark Pink APT Group and how they used phishing emails to lure military and government organisations to deliver KamiKakaBot. Read our blog to uncover the full story.
Russian-speaking hacking group ‘Black Basta’ has recently been in the news due to a giant cyber attack on the UK-based corporation Capita. This blog talks through what happened and what this means going forward.
This blog covers the most recent arrest and the shutdown of Genesis and breached websites. Read this blog to find out more about the breached forums and how the shutdown of Genesis Market began.
This blog covers the 3cx attack, what happened and what we leant from the huge impact of this attack. For more depth, listen to our consultants discuss this in our ThreatBite.
This blog summarises the recent TikTok cyber security concerns that has been announced this week. What does this mean for the future of TikTok?
This blog covers the overcoming challenges to solve crypto crimes and how it’s used for legal purposes as well as illegal purposes. Read this blog for a more depth view to how the Bitcoin industry works.
This blog is about the DarkNet Drug markets and how they operate. This blog acts as a breakdown of what goes on and how to protect yourself from these DarkNet markets.
This blog covers the recent Ransomware gang, Hive, who have been caught by International Law Enforcement and FBI for being the most dangerous and profolic hacker gangs in the country. Read more to find out how they were caught out.
This week, two of our researchers discuss the recent rise in ransomware attacks, focusing on some recent stories and first-hand knowledge on why we’ve seen such an increase in these attacks. Read this blog for more detail.
With Christmas soon approaching we’ve decided to go on a slightly different tangent and focus on the typical scams you can expect during this festive season and what to look out for. After all, we want you all to be safe this time of year.
browse by tag
browse by category
browse by year
free trial
Try DarkInvader Pro free. No payment details required.