
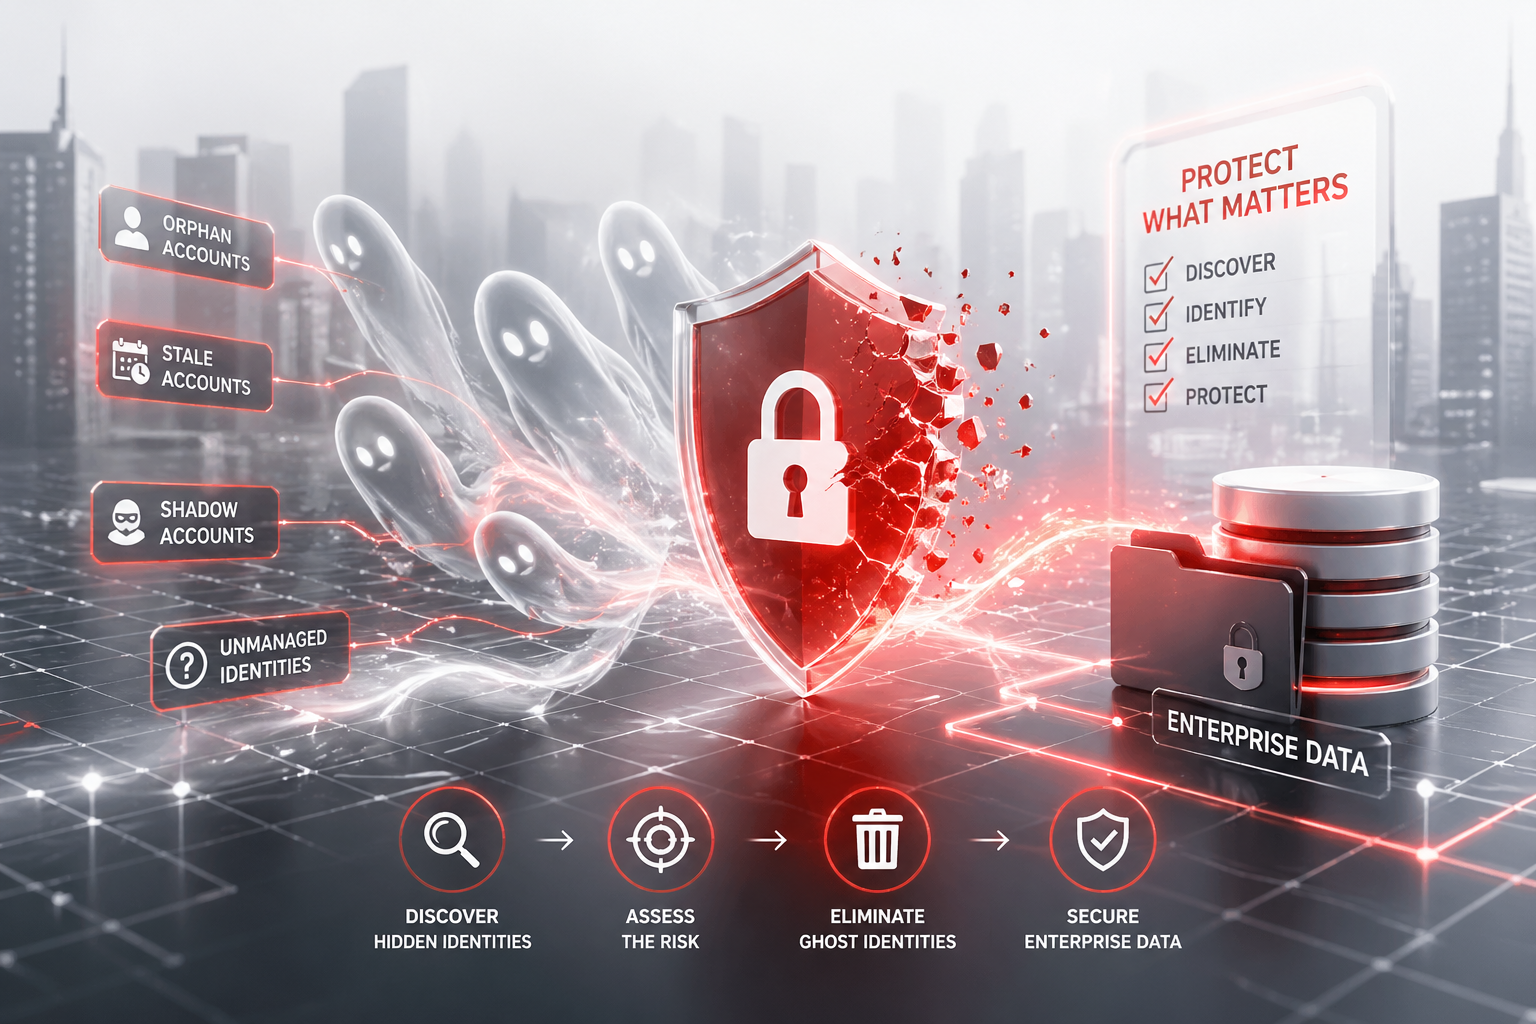
In today's digital age, the security of enterprise data has never been more crucial. As organisations embrace digital transformation, they must also contend with an array of cyber threats. Among these perils, "ghost identities" have emerged as a formidable challenge. But what are ghost identities, and how can they be tackled effectively to safeguard your valuable data?
Understanding Ghost Identities
Ghost identities refer to obsolete, unused, or hidden user accounts within a company’s IT infrastructure that have access privileges to sensitive data. These accounts can be a gateway for cybercriminals if not promptly identified and managed. They may result from employees leaving the organisation, vendors’ credentials not being revoked, or simply outdated accounts not being deactivated.
The Risks Posed by Ghost Identities
- Unauthorised Access: Ghost identities may be exploited by malicious actors to gain unauthorised access to sensitive information.
- Data Leakage: These identities can lead to data breaches, where confidential information is exposed or compromised.
- Regulatory Non-compliance: Organisations may face hefty penalties if they fail to protect personal data as per regulatory requirements.
- Increased Attack Surface: Ghost identities expand the attack surface, providing more opportunities for cybercriminals to infiltrate the network.
Identifying and Eliminating Ghost Identities
To mitigate the risks associated with ghost identities, organisations must adopt a comprehensive approach to identify and eliminate these threats. Here's how:
Implement Regular Audits
Routine audits of user accounts should be conducted to ensure that no unnecessary or dormant identities exist. Regular audits help maintain an up-to-date inventory of all accounts, facilitating the swift identification and deactivation of ghost identities.
Utilise Automated Tools
Leveraging automated identity and access management (IAM) tools can significantly streamline the process. These tools efficiently track user accounts, monitor access patterns, and flag anomalies, ensuring ghost identities do not persist unnoticed.
Enforce Strict Access Controls
Implement role-based access controls (RBAC) that allow users access only to the resources necessary for their role. By minimising permissions, the risk of data being exposed through ghost identities is reduced.
Enhance Employee Offboarding Procedures
A robust offboarding process is essential. Ensure that when employees leave, their credentials are deactivated immediately. This includes contractor and vendor accounts as well.
Read more about how we can help with leaked credentials monitoring.
Monitor for Anomalies
Continuous monitoring of user activity and access logs is vital. Look for unusual access patterns which could indicate the misuse of a ghost identity.
The Role of Technology in Managing Ghost Identities
Embracing advanced solutions can drastically improve an organisation's response to ghost identities. DarkInvader provides comprehensive asset monitoring and management solutions that can be instrumental in this regard.
Leveraging EASM
External Attack Surface Management (EASM) tools are crucial for identifying and managing both external and internal threats, including ghost identities. They enhance visibility into all assets and identities, facilitating prompt action.
Integrating with Cybersecurity Frameworks
Ensure your IAM solutions integrate with broader cybersecurity frameworks. This ensures a more holistic approach to threat management and aligns with best practices.
Summary
Ghost identities are a tangible threat to enterprise data security. By understanding the risks they pose and implementing robust measures to identify and manage these identities, organisations can significantly bolster their cybersecurity posture. Regular audits, automated tools, and strict access controls are crucial components of an effective strategy against ghost identities.
Secure your data and minimise risks with DarkInvader's comprehensive solutions.
FAQ
What are ghost identities in cybersecurity?
Ghost identities are dormant, unused, or obsolete user accounts within a company's IT infrastructure that can potentially be exploited by hackers to gain unauthorised access to sensitive information.
How can organisations detect ghost identities?
Organisations can detect ghost identities through regular audits, employing automated identity management tools, and monitoring user activity for anomalies.
Why are ghost identities a risk to enterprise data?
Ghost identities pose a risk because they can be used by cybercriminals to access sensitive data without detection, leading to data breaches and regulatory non-compliance.
How does DarkInvader help in managing ghost identities?
DarkInvader offers solutions that enhance asset monitoring and management, which are vital for identifying and eliminating ghost identities, thus reducing the risk to enterprise data.
By addressing ghost identities, organisations can protect their information assets, ensuring compliance and securing their digital transformations.