• tagged
Every post filed under this tag, newest first.
Third party breach hitting your data? Get the early warning signals, a 72-hour UK response runbook and the contract fixes that stop a repeat.
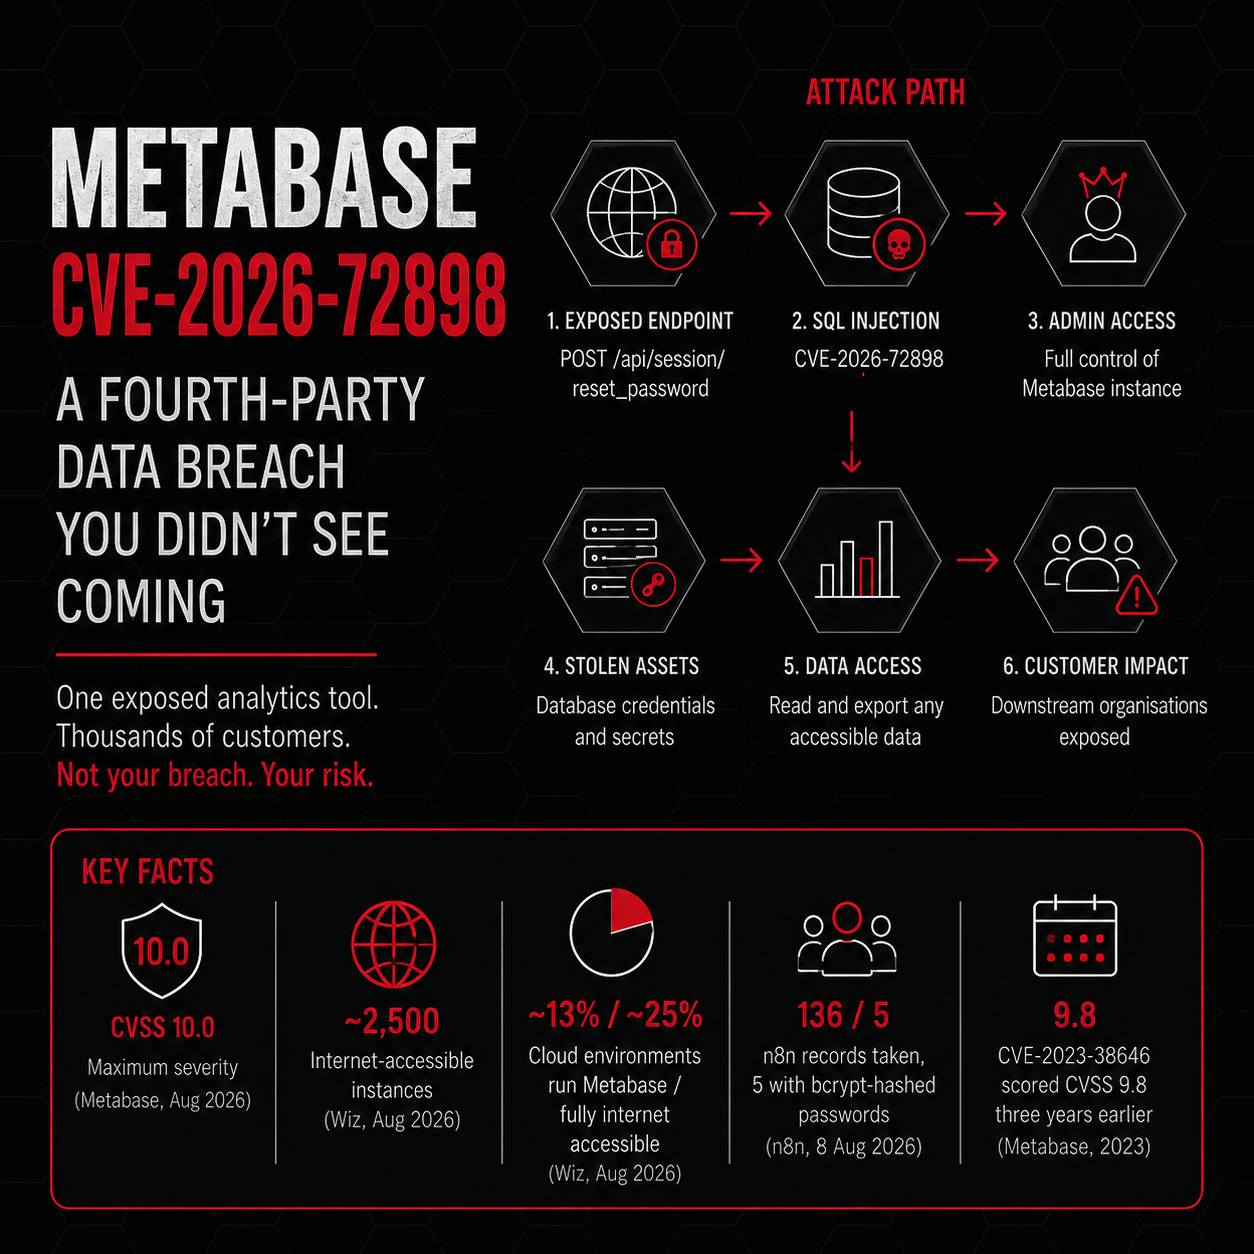
Explore the anatomy of a fourth-party data breach, examining the risks associated with Metabase, Framework, and n8n and how to mitigate them.
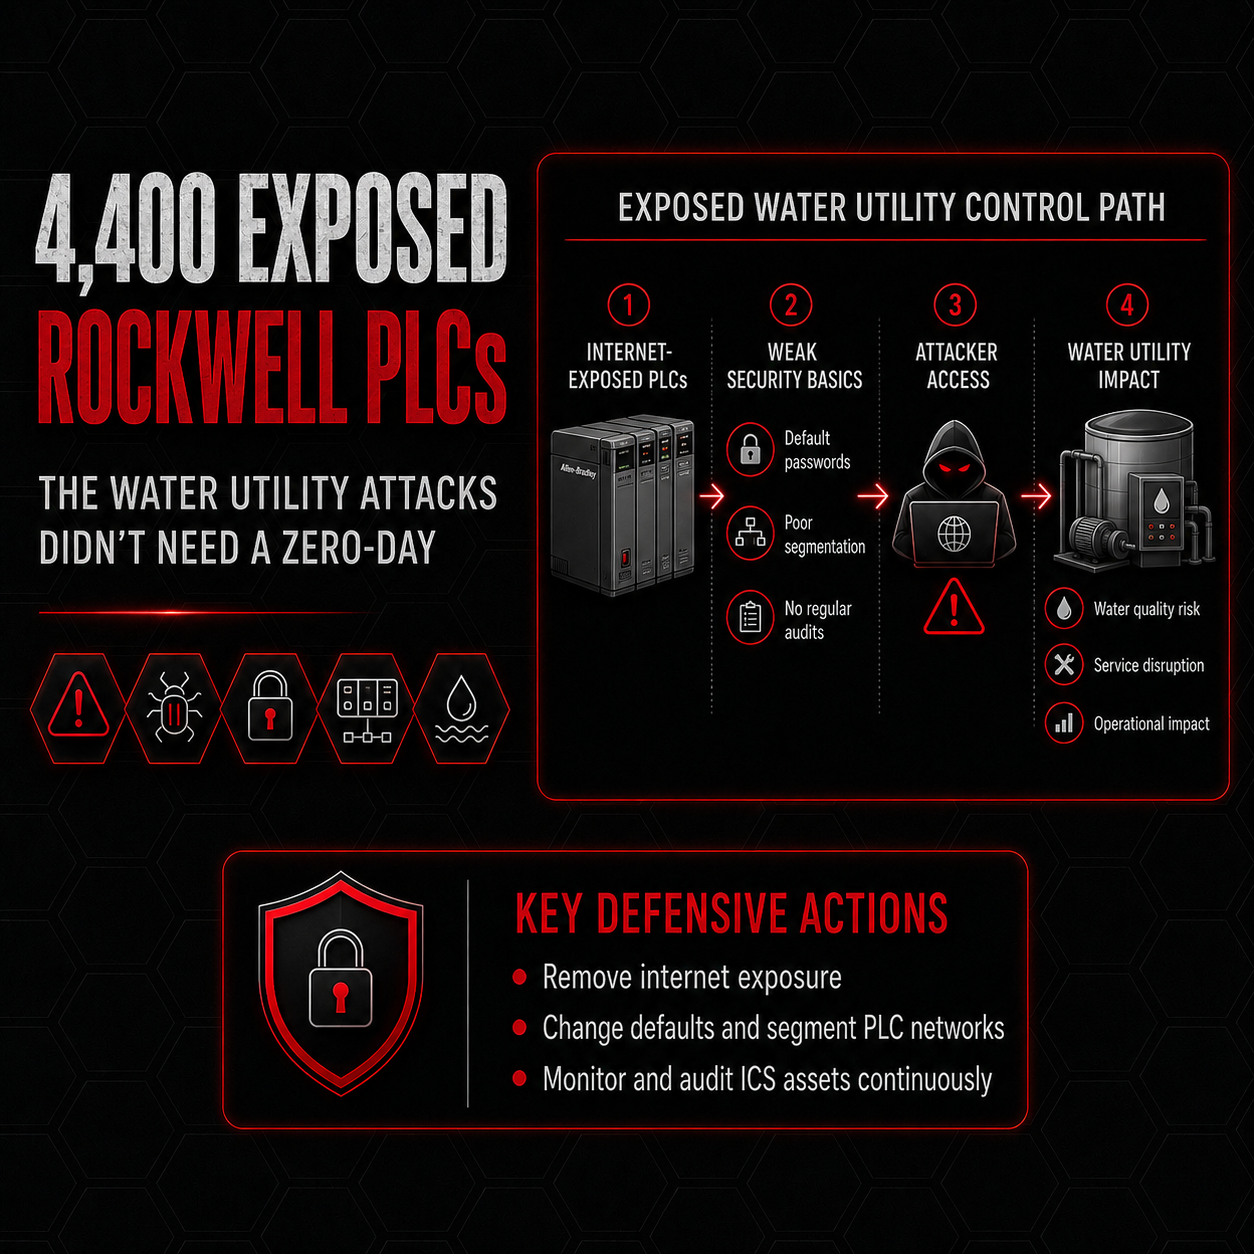
Forescout found 4,407 internet-exposed Rockwell PLCs. Attackers disrupted US water utilities with no exploit, just by changing IPs and passwords.
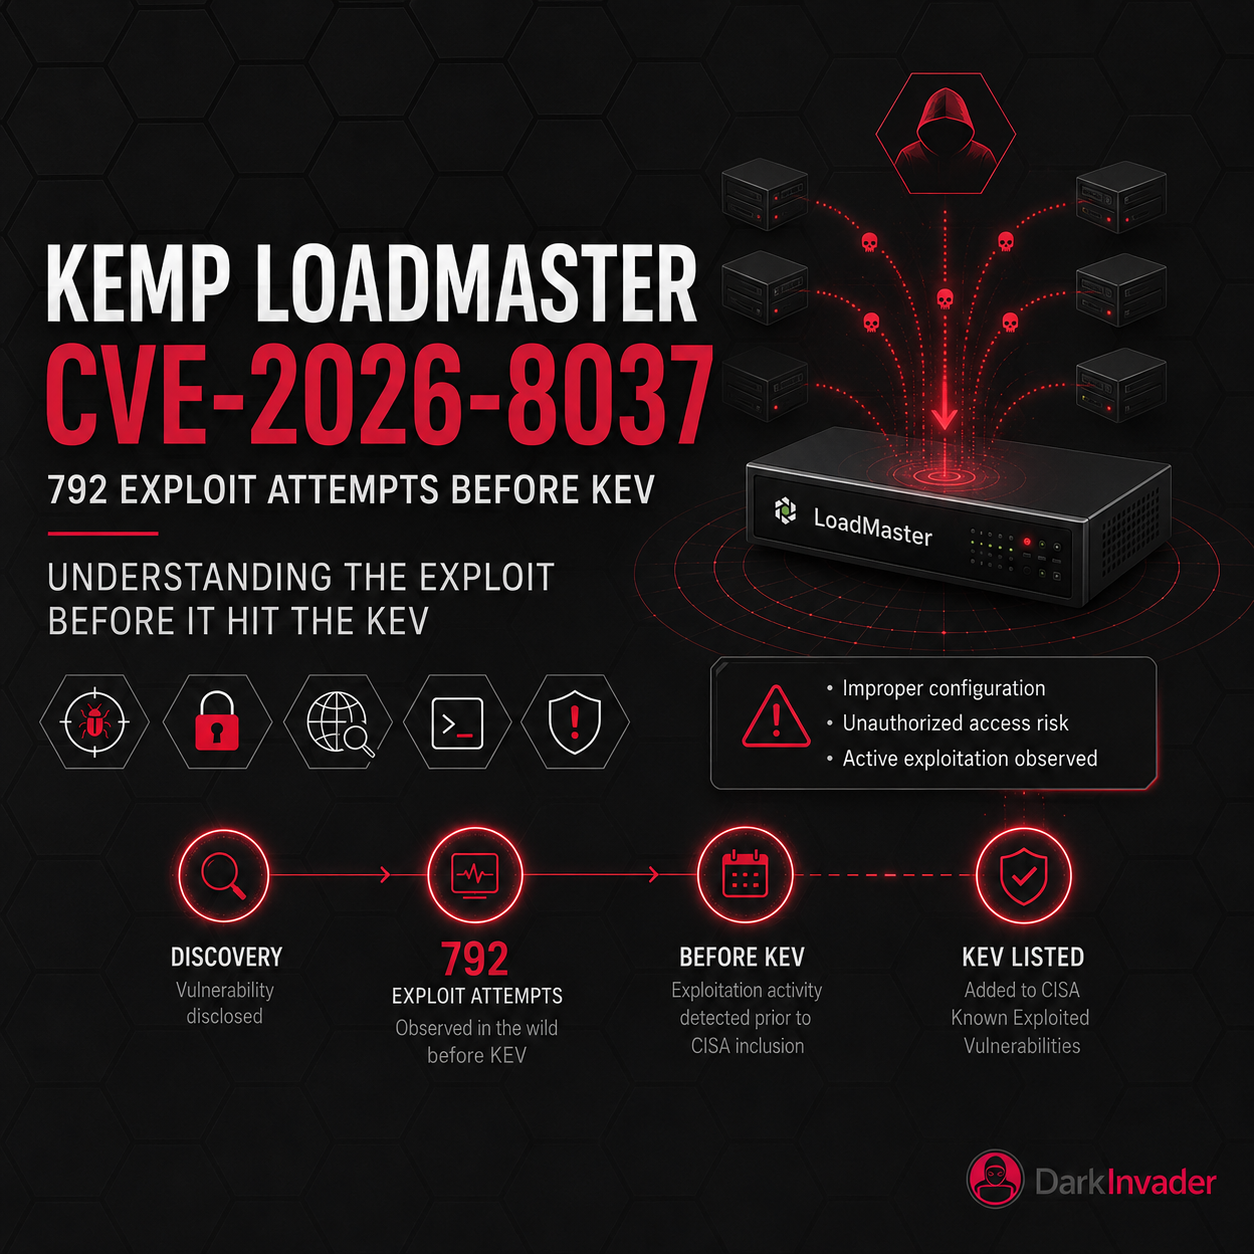
CVE-2026-8037 is a critical unauthenticated command injection flaw in Progress Kemp LoadMaster, added to CISA's KEV catalogue on 7 August 2026.
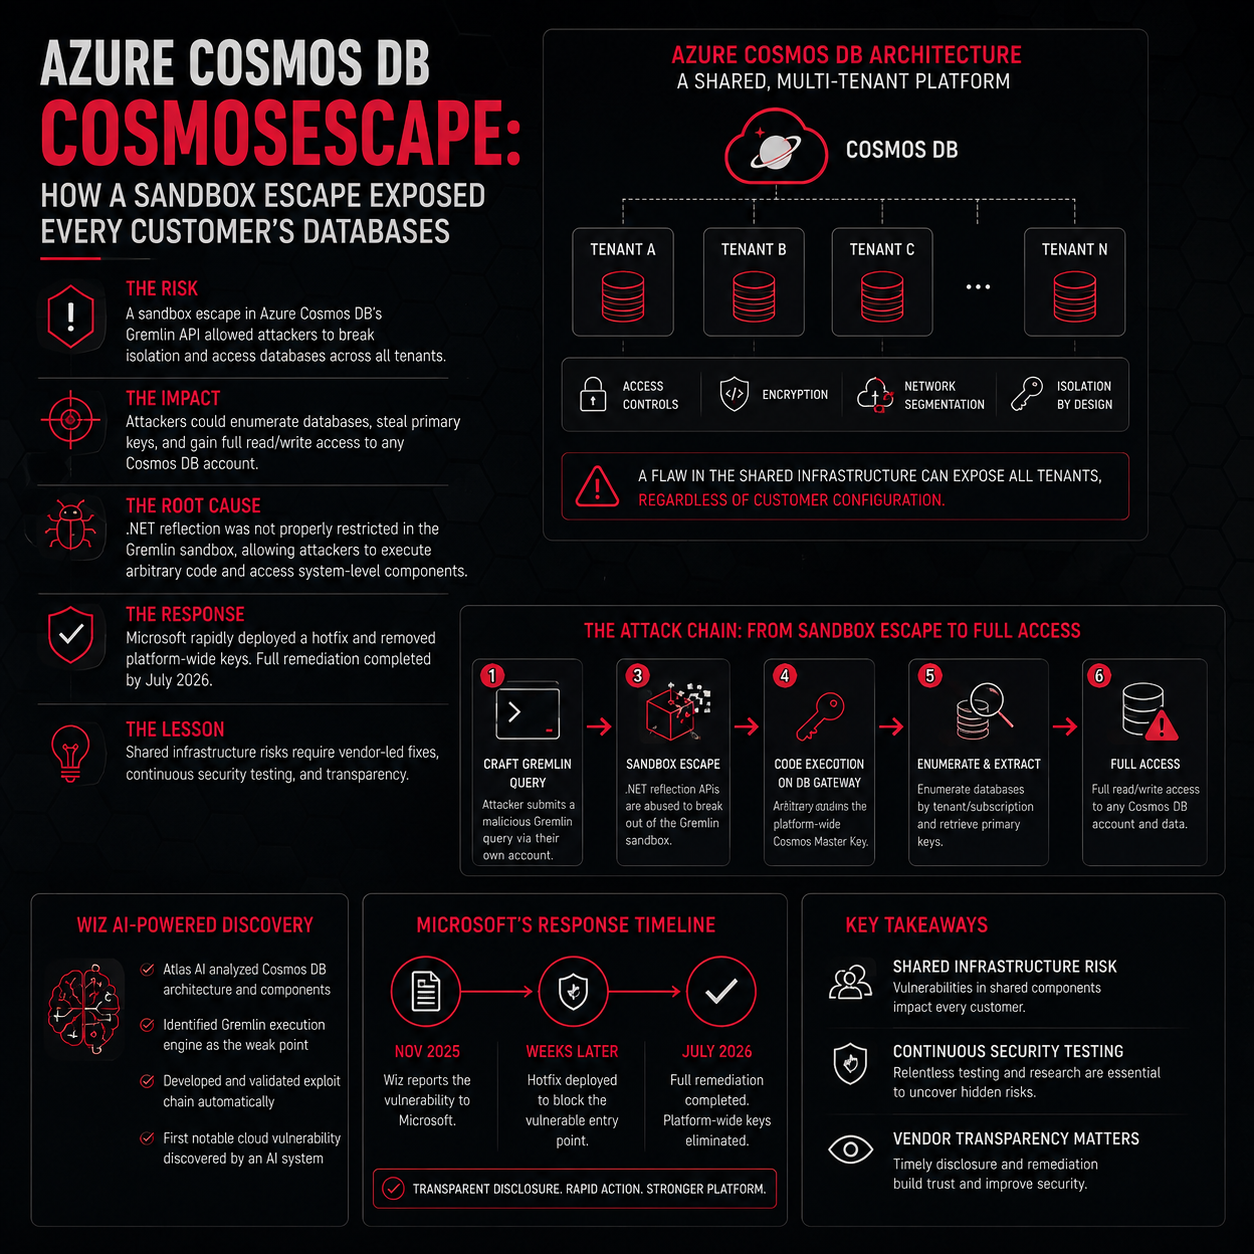
Exploration of Azure Cosmos DB critical vulnerability, CosmosEscape, highlighting the risks of shared infrastructure in cloud computing.
AI is a double-edged sword on the attack surface. Explore its role in offence and defence, the new risks it creates and strategies to mitigate them.
Explore the StrikeShark campaign, a sophisticated cyber threat targeting businesses. Learn how to protect exposure with advanced cybersecurity strategies.
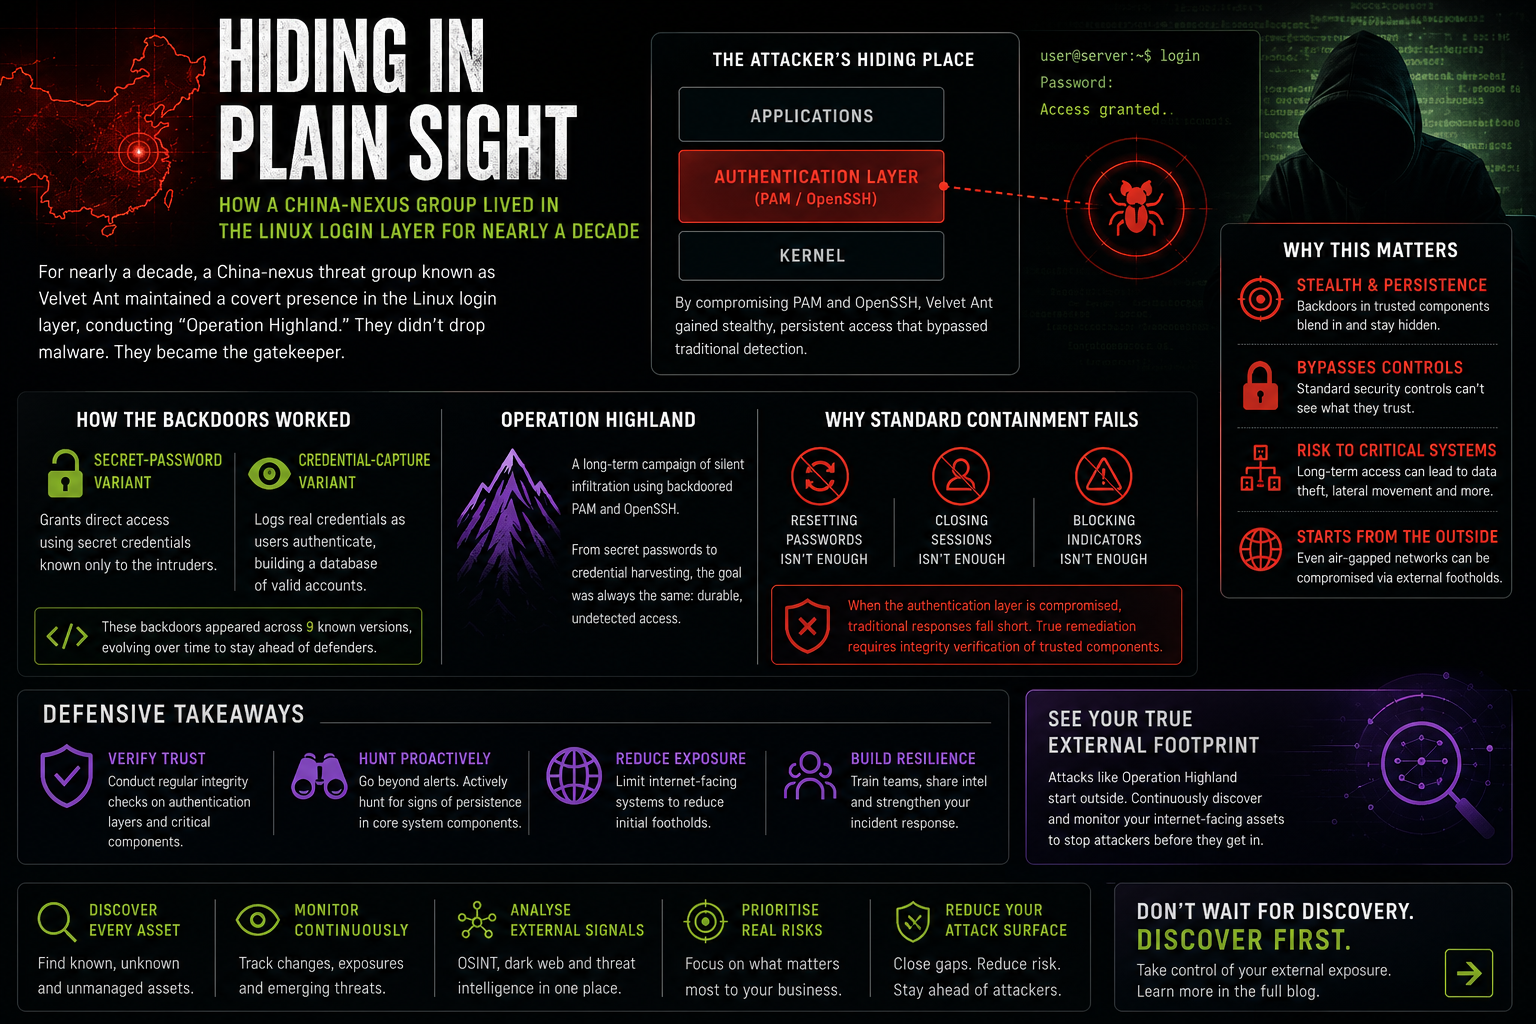
How China-nexus group Velvet Ant spent nearly a decade inside Linux login systems, using PAM and OpenSSH backdoors to keep persistent access.
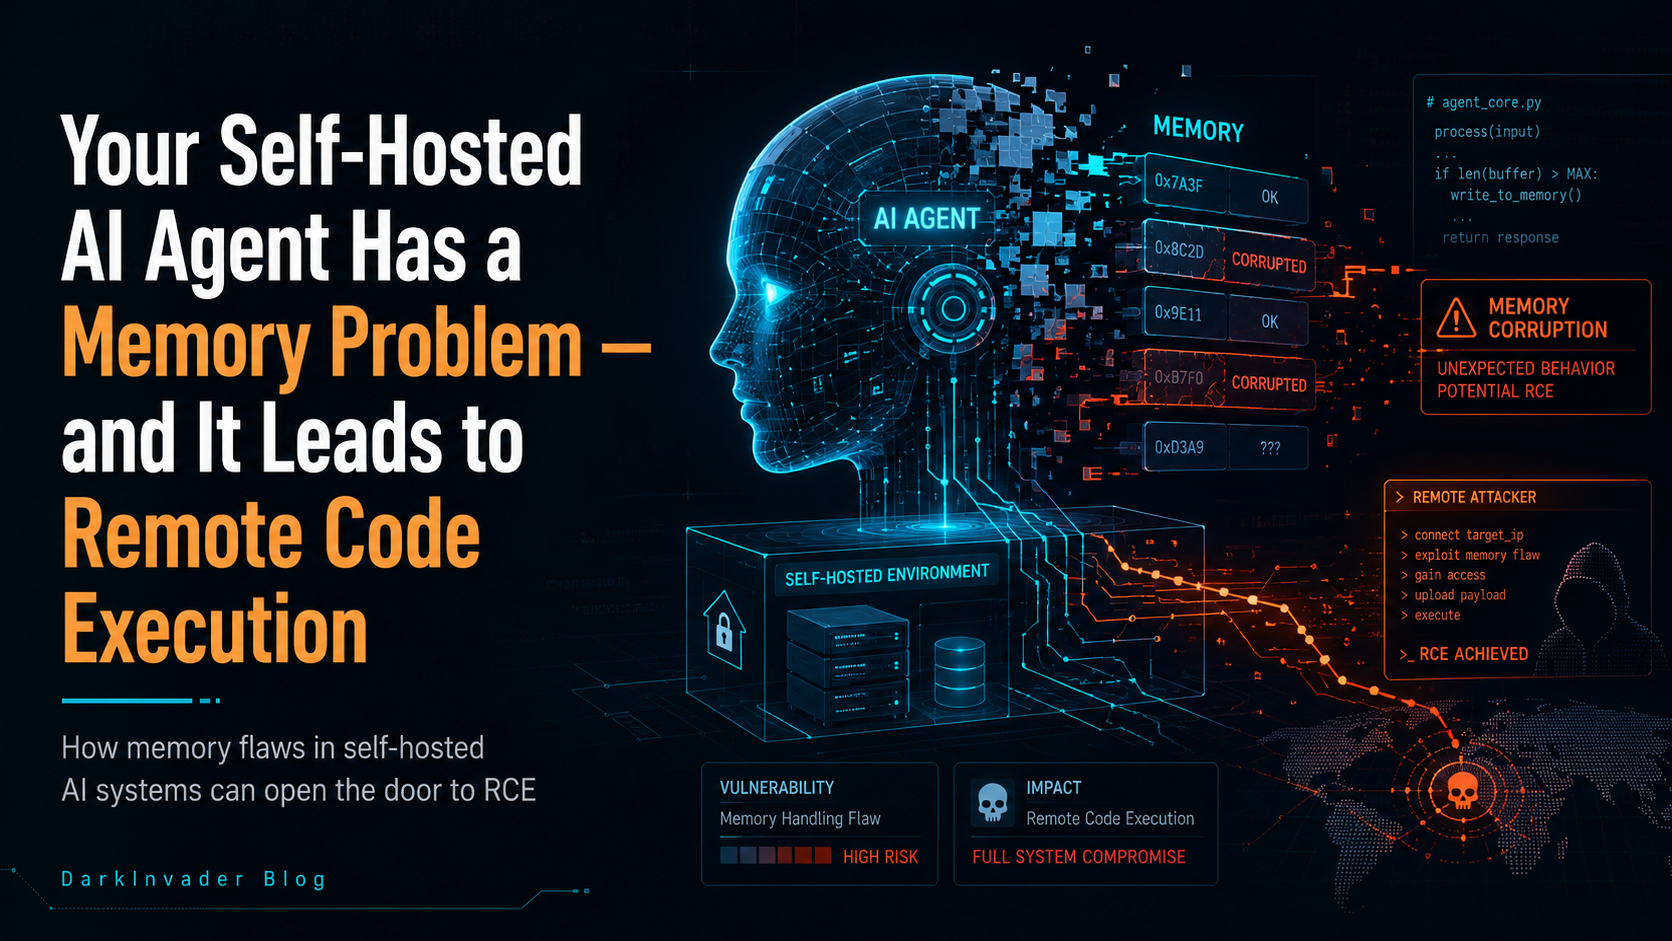
Explore how memory issues in self-hosted AI agents lead to vulnerabilities like remote code execution, and discover strategies to mitigate these risks.
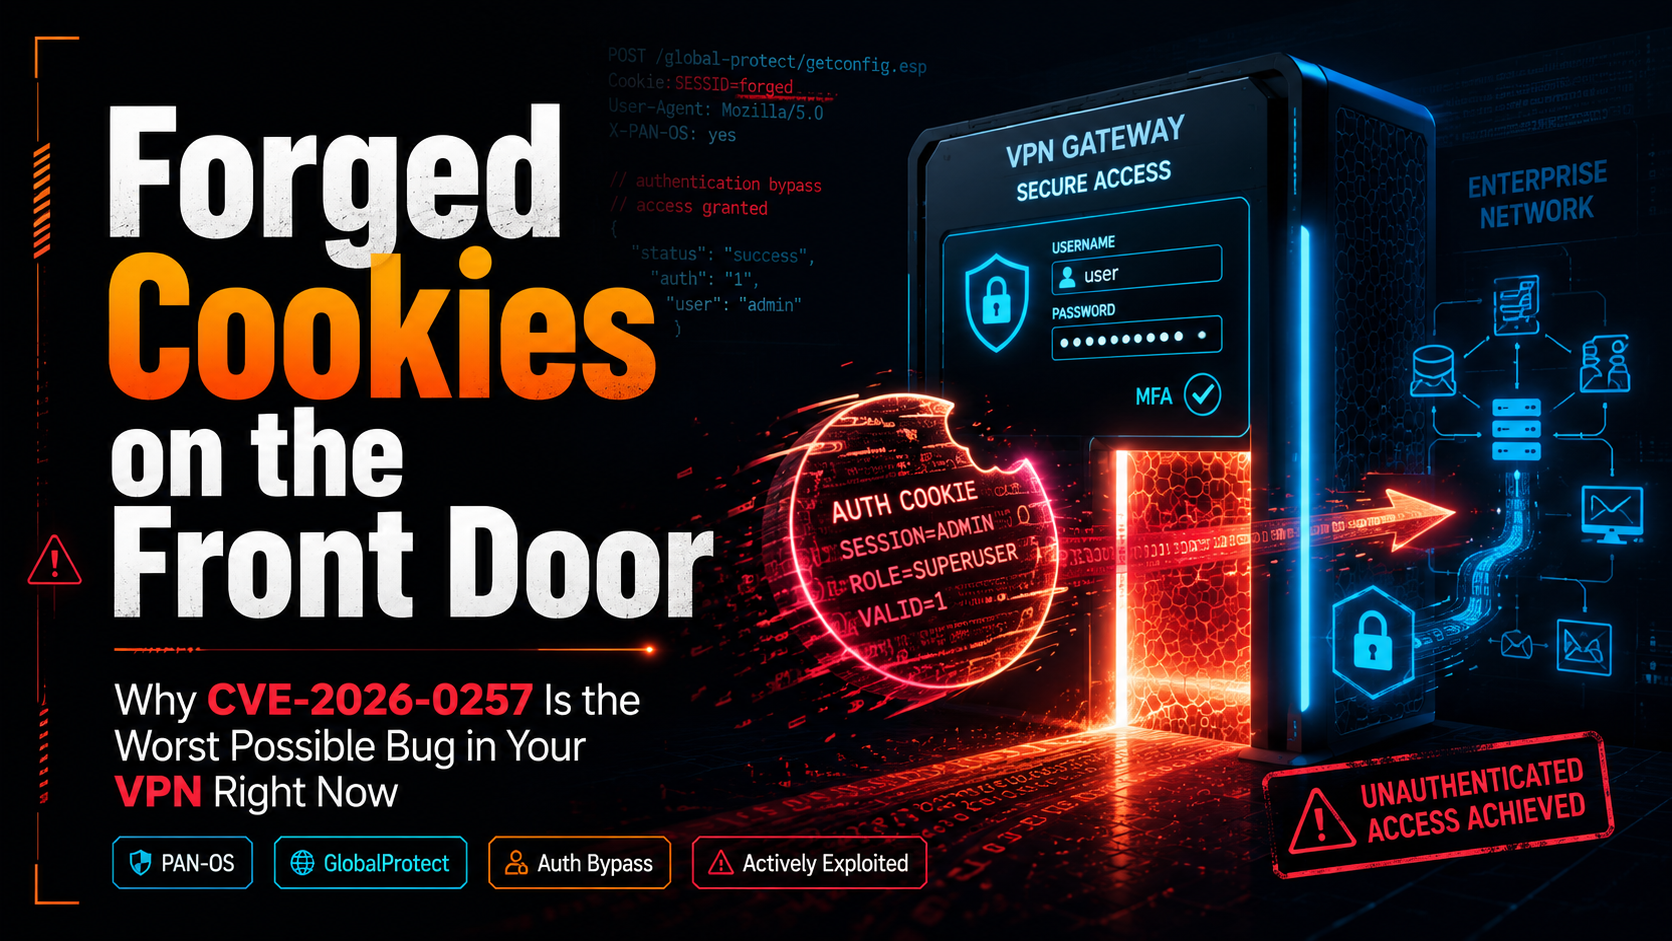
Explores CVE-2026-0257, a critical vulnerability in VPNs that could allow forged cookie attacks, posing serious security threats.
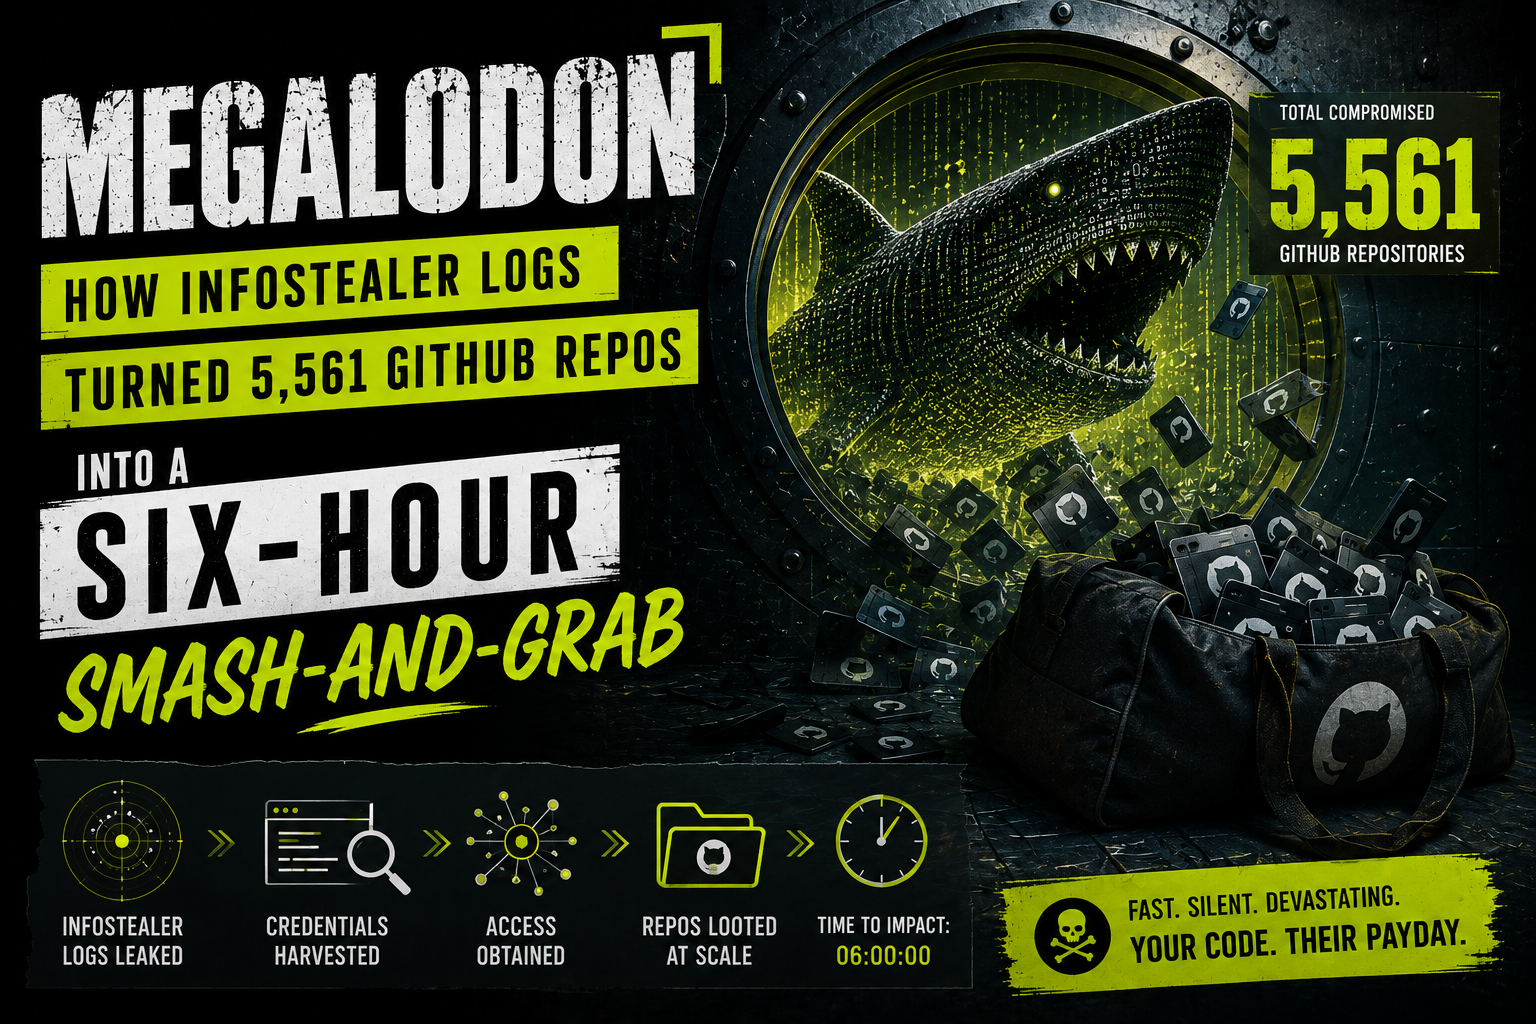
Megalodon backdoored 5,561 GitHub repos in six hours in May 2026 using stolen tokens, likely from infostealer logs. What happened and how to respond.
Exploring the implications of AI-driven zero-day 2FA bypass for mass exploitation and its impact on cybersecurity strategies.
Most remediation programmes never verify that a vulnerability fix worked. Learn the risks of this verification gap and a framework to close it.
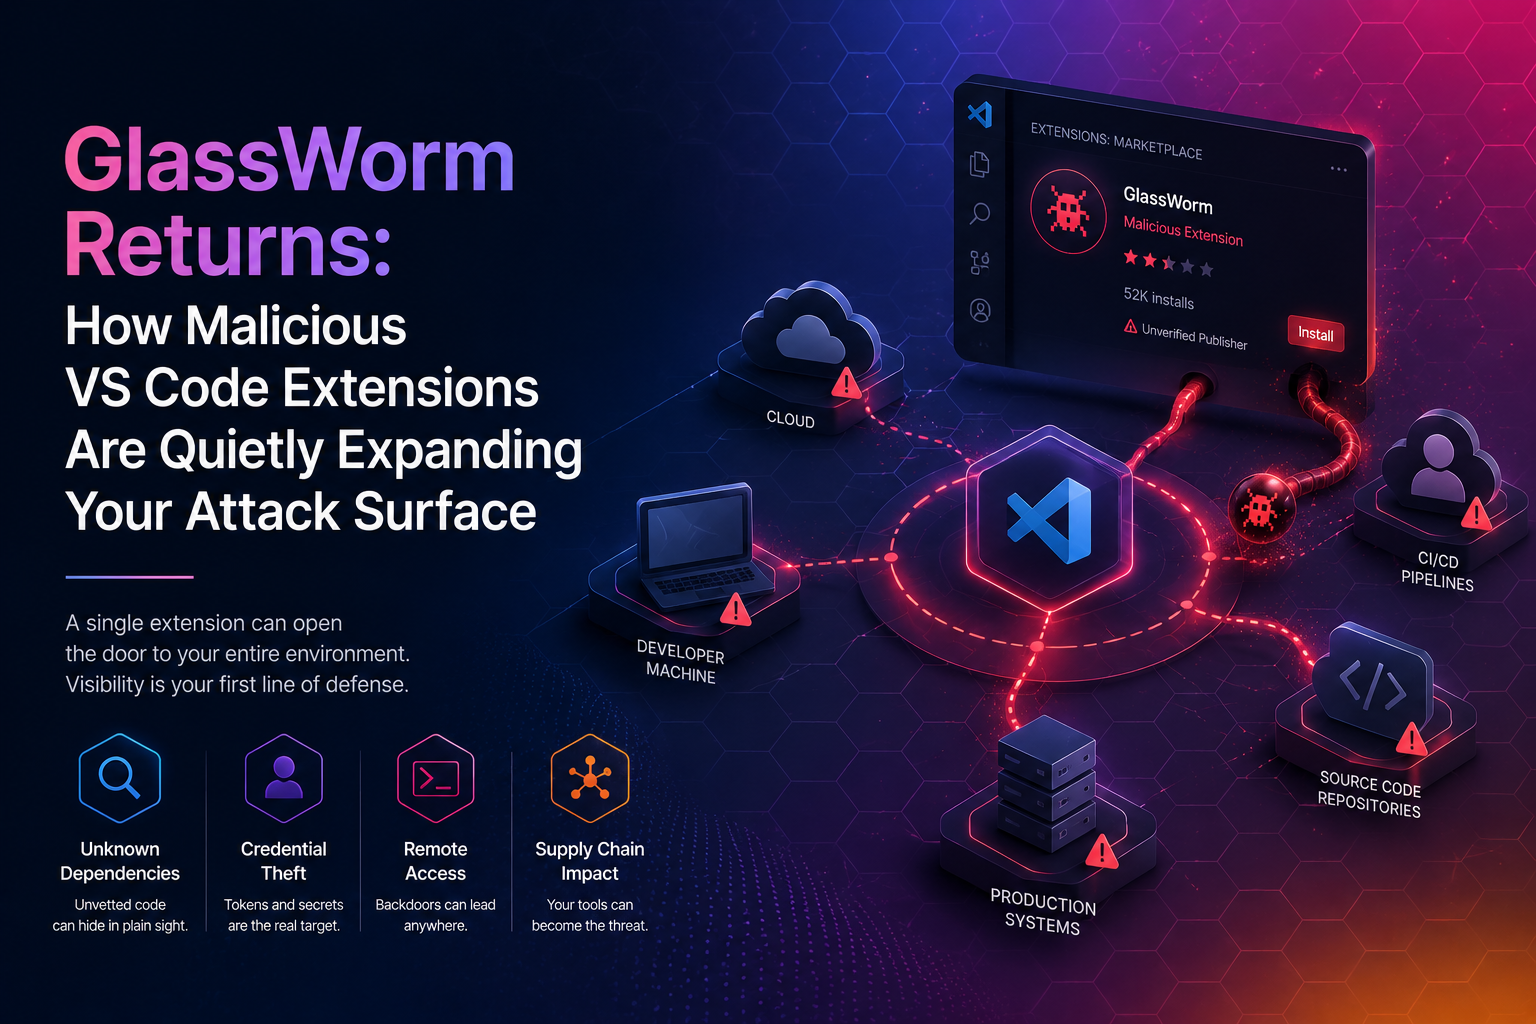
GlassWorm is back: malicious VS Code extensions target developer machines holding credentials and code. Learn how to detect and mitigate them.
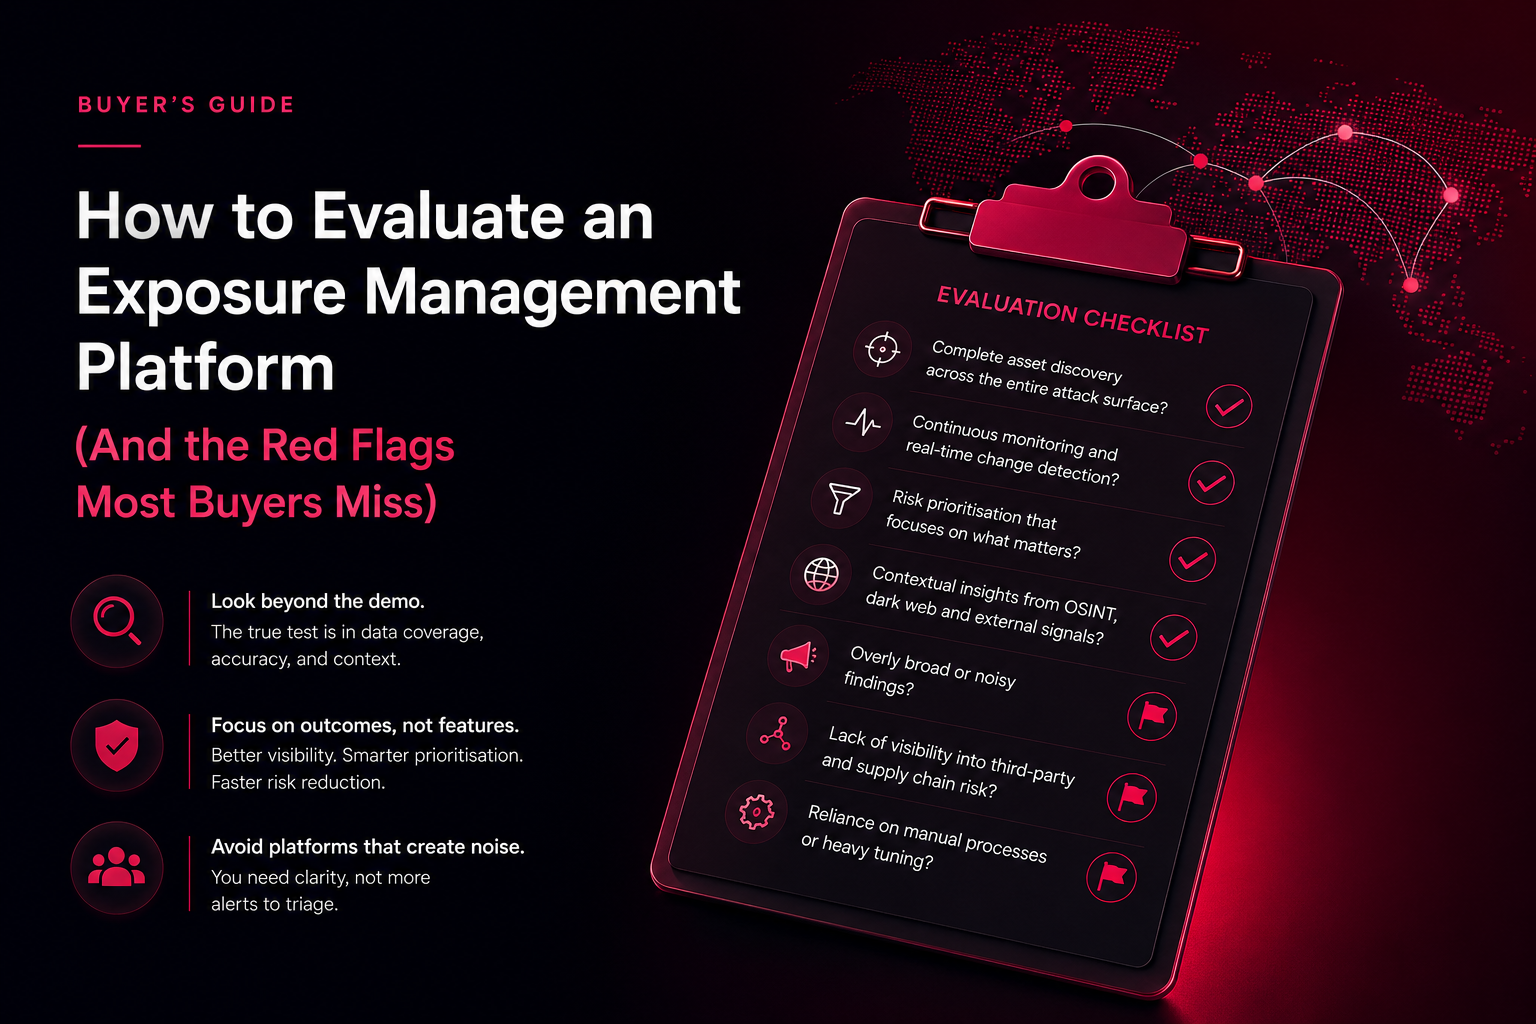
A contrarian buyer’s guide to evaluating exposure management platforms, highlighting the critical features and red flags most buyers overlook.
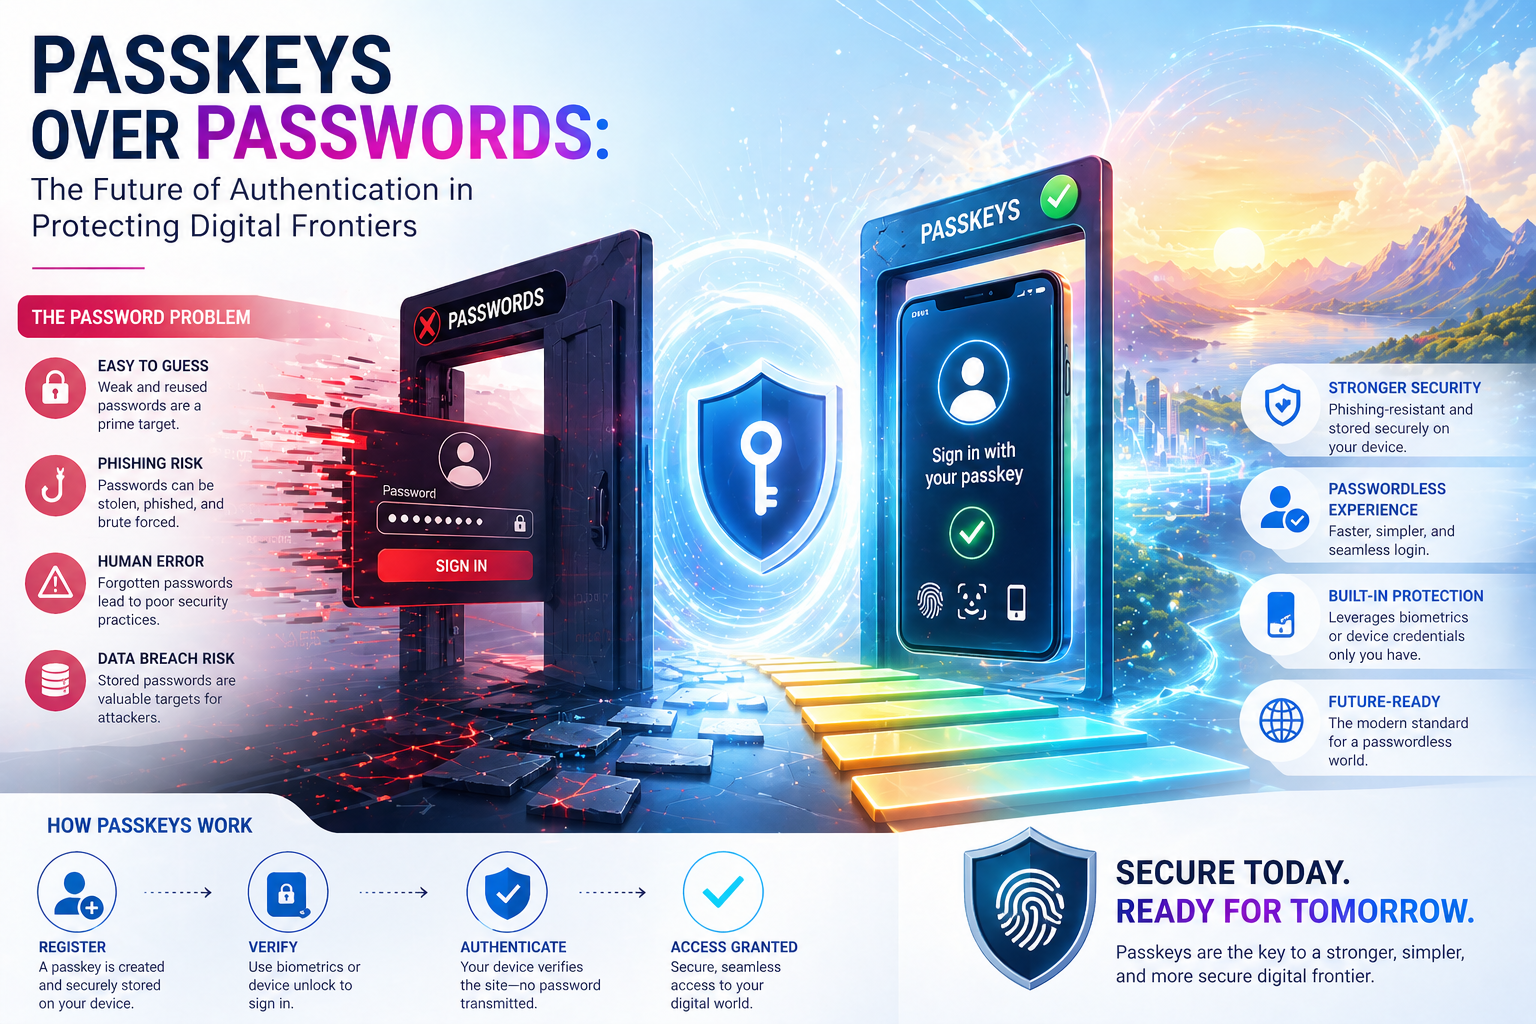
Passkeys replace vulnerable passwords with device-specific cryptographic keys and biometrics, offering stronger security and easier sign-in.
Ghost identities are dormant or obsolete accounts that put enterprise data at risk. Learn how to find and remove them with audits and access controls.
EASM helps defend against the latest phishing techniques by continuously monitoring internet-facing assets and surfacing threat intelligence early.
AI tools make it easy to clone brands and turn fake websites on customers. Learn why your brand is part of your attack surface and how to protect it.
Your brand is part of your attack surface. Learn how attackers impersonate brands to trick customers, and how monitoring fake sites protects trust.
Website takedowns protect brands from fraud but need evidence, detail and careful registrar communication. Learn how the process really works.
Combining reverse image search with typosquatting checks helps you detect fake websites early, protect your brand and act quickly to take them down.
Social media poses hidden IT security risks, from phishing and data leakage to espionage. Learn the policies and training that reduce exposure.
This blog outlines what Typo Squatting is and the dangers associated with it as well as how to protect yourself against all types of TypoSquatting.
browse by tag
browse by category
browse by year
free trial
Try DarkInvader Pro free. No payment details required.