• tagged
Every post filed under this tag, newest first.
ServiceNow vulnerabilities are only half the problem. Learn how to inventory every exposed instance, test safely and respond in 72 hours.
CVE-2026-19490 is a critical authentication bypass in NetScaler ADC and Gateway. Learn the risk and why it needs fixing before exploitation starts.
Shadow IT risks explained from the attacker’s view: 7 exposures, how each one is discovered from outside, and what to fix first. See how to find yours.
CVE-2026-19478 is a critical GitLab code injection flaw, rated 9.4, that allows unauthenticated deletion of public projects. Patches are available.
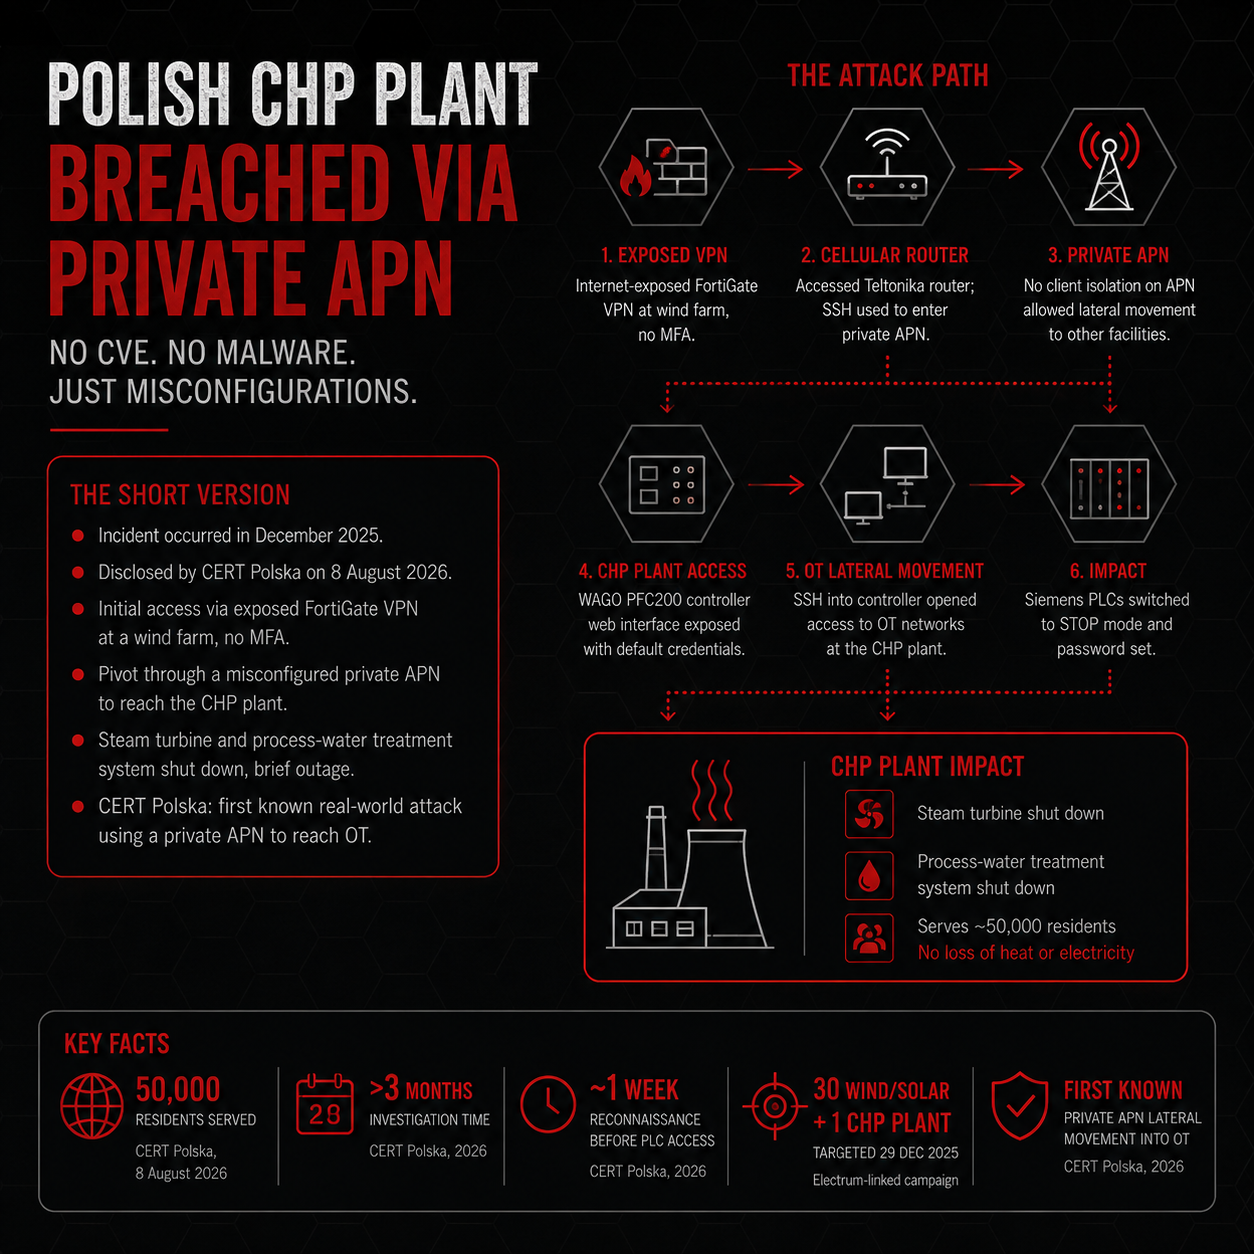
How a forgotten VPN at a wind farm gave attackers a route to Siemens PLCs at a heat plant, and what it teaches about securing industrial operations.
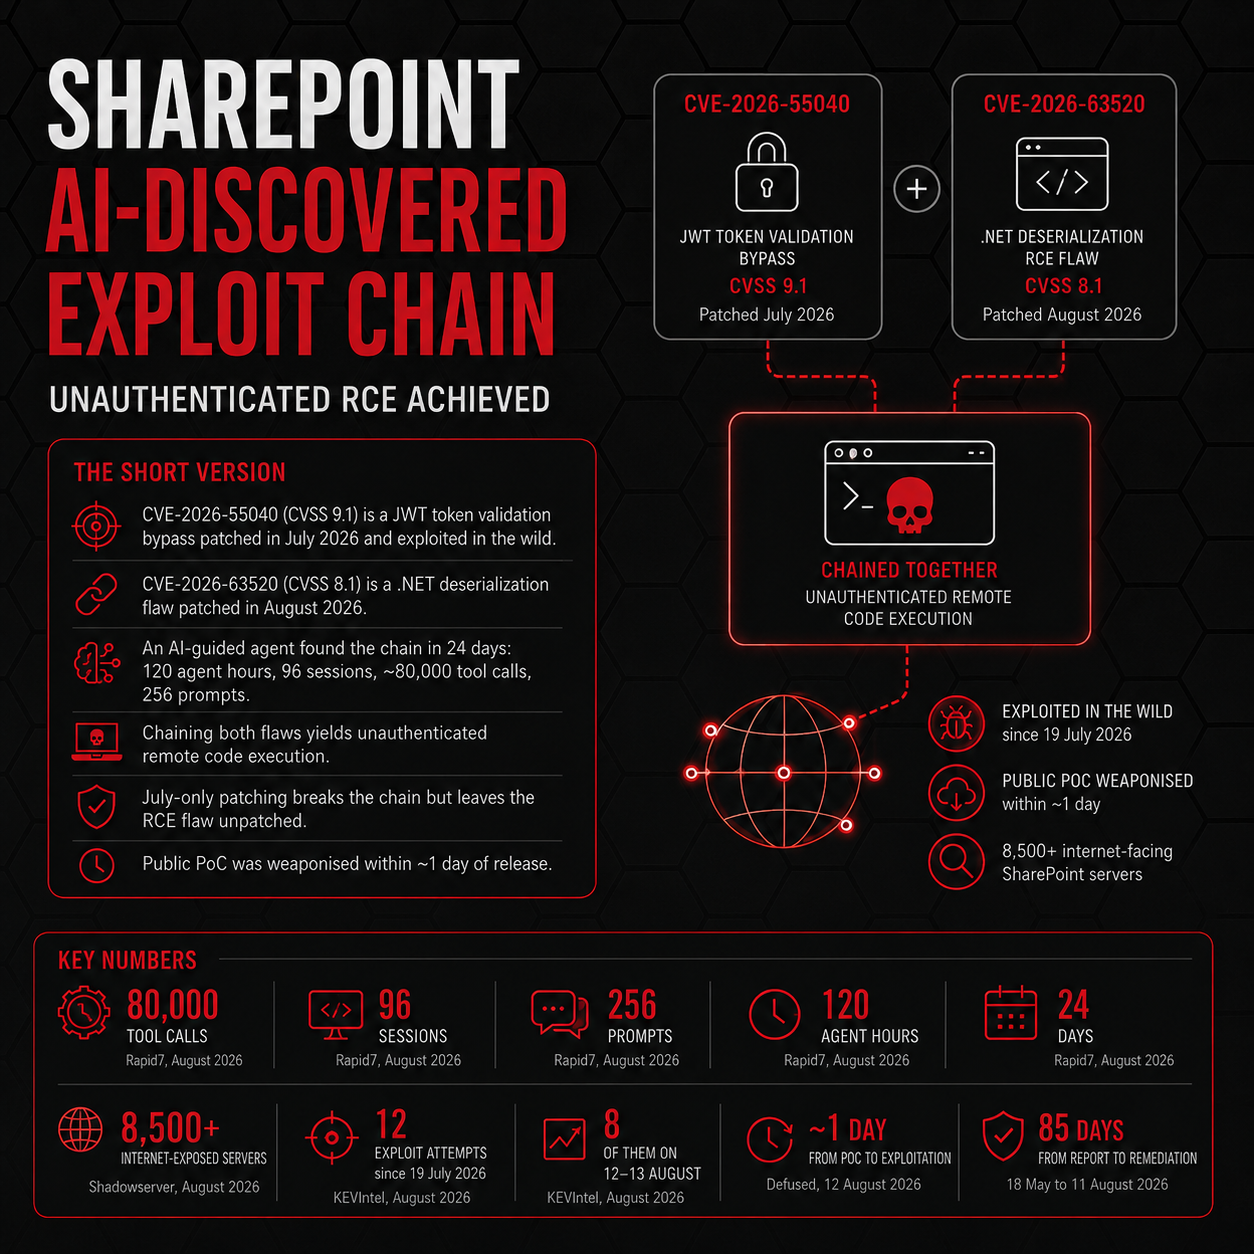
An agent-discovered SharePoint vulnerability chain shows how exploitation could evolve over the next decade, and how organisations can prepare now.
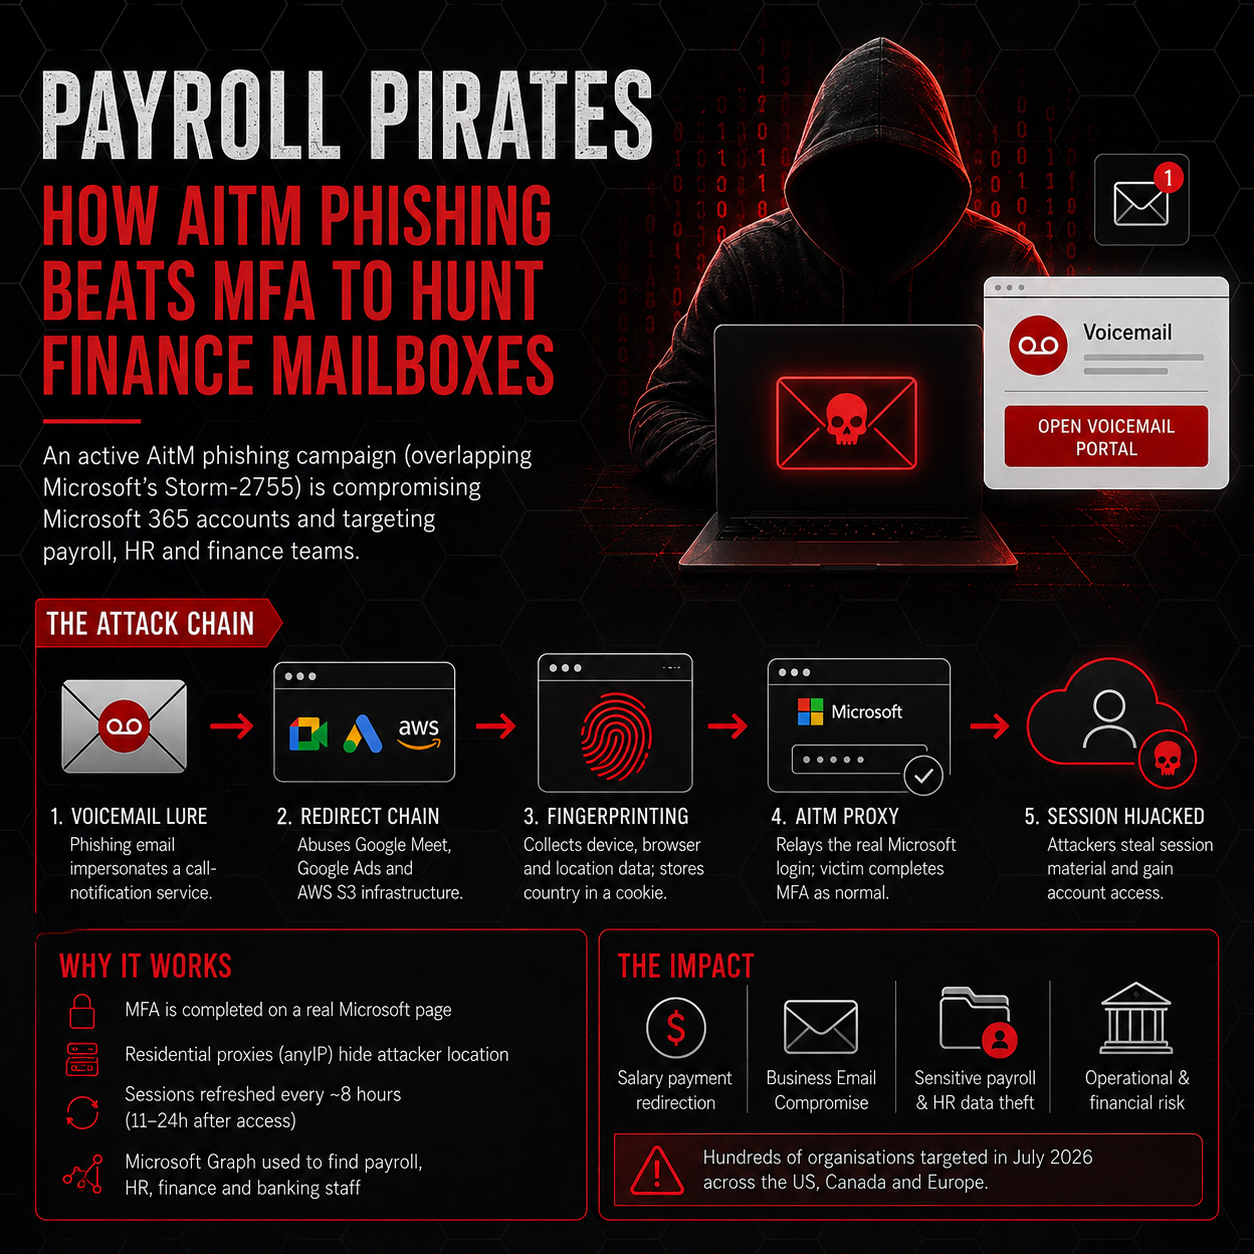
An exploration of the "Payroll Pirates" AitM phishing campaign, highlighting its techniques and providing guidance for detection and defense.
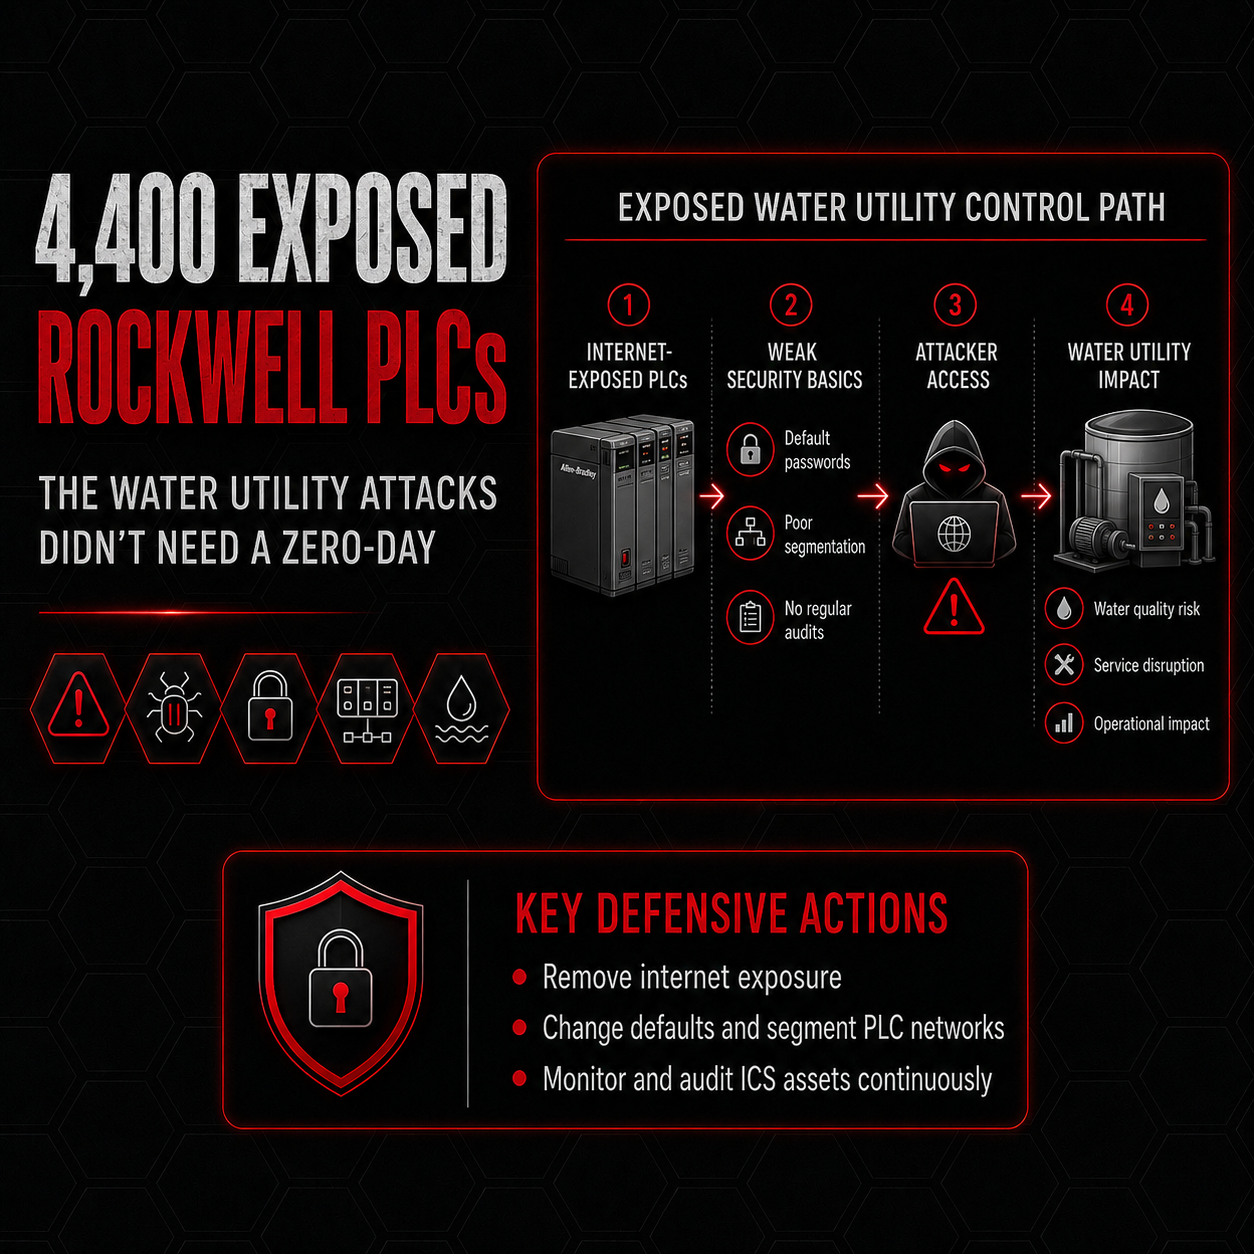
Forescout found 4,407 internet-exposed Rockwell PLCs. Attackers disrupted US water utilities with no exploit, just by changing IPs and passwords.
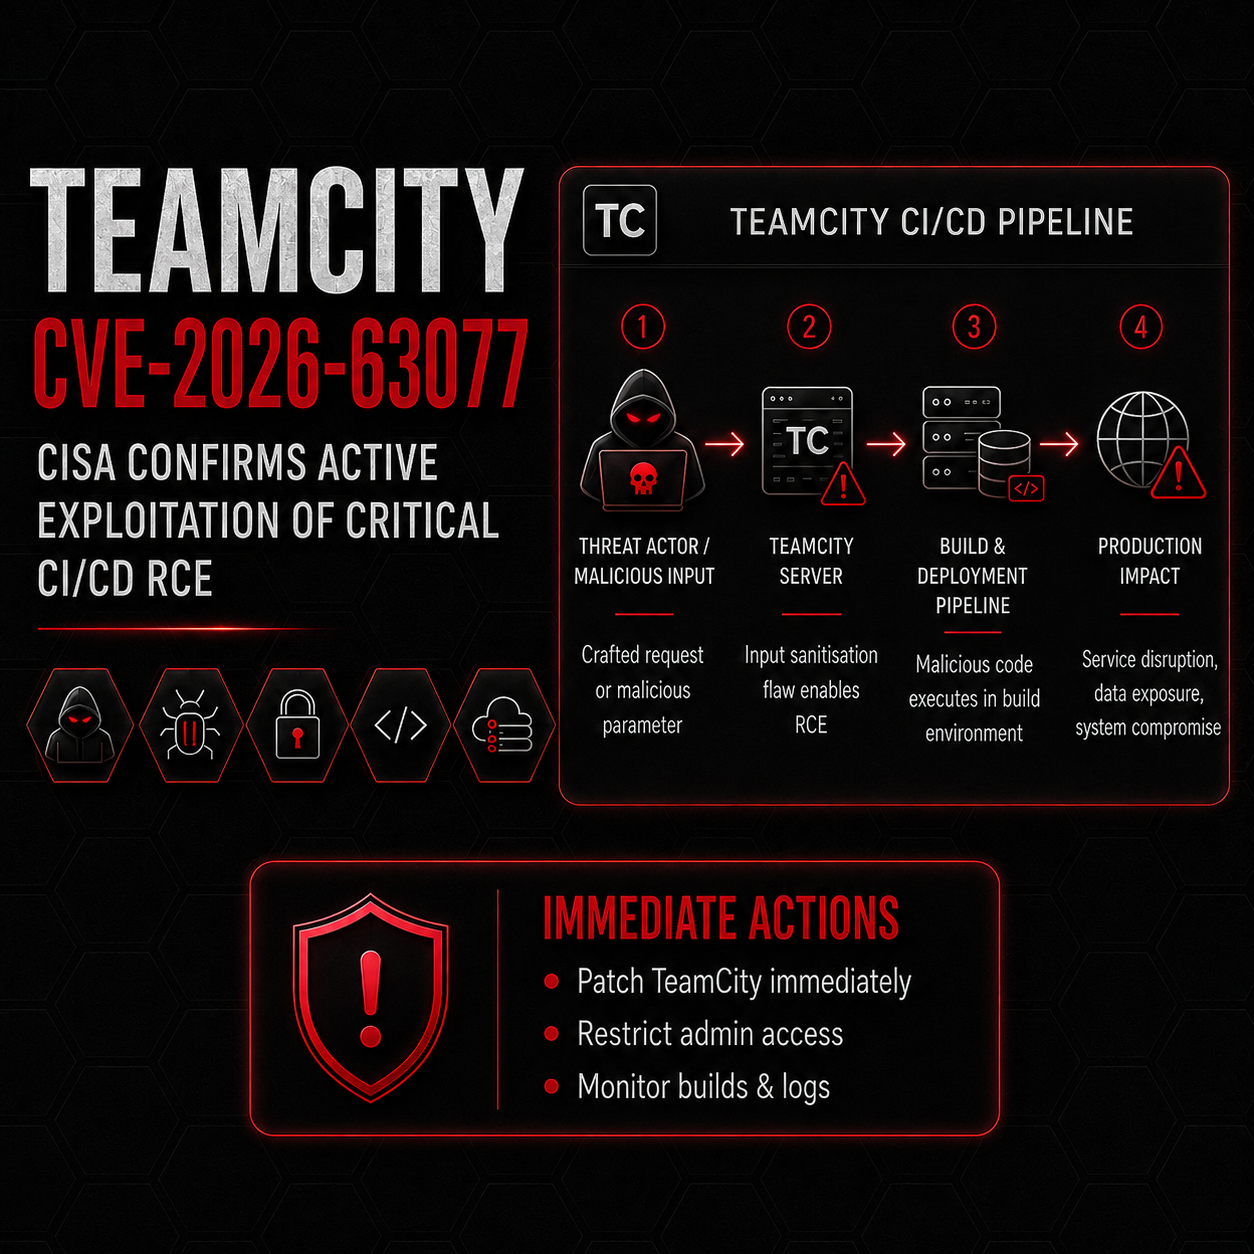
TeamCity CVE-2026-63077 is a critical CI/CD remote code execution flaw that CISA confirms is actively exploited. Learn the impact and how to mitigate it.
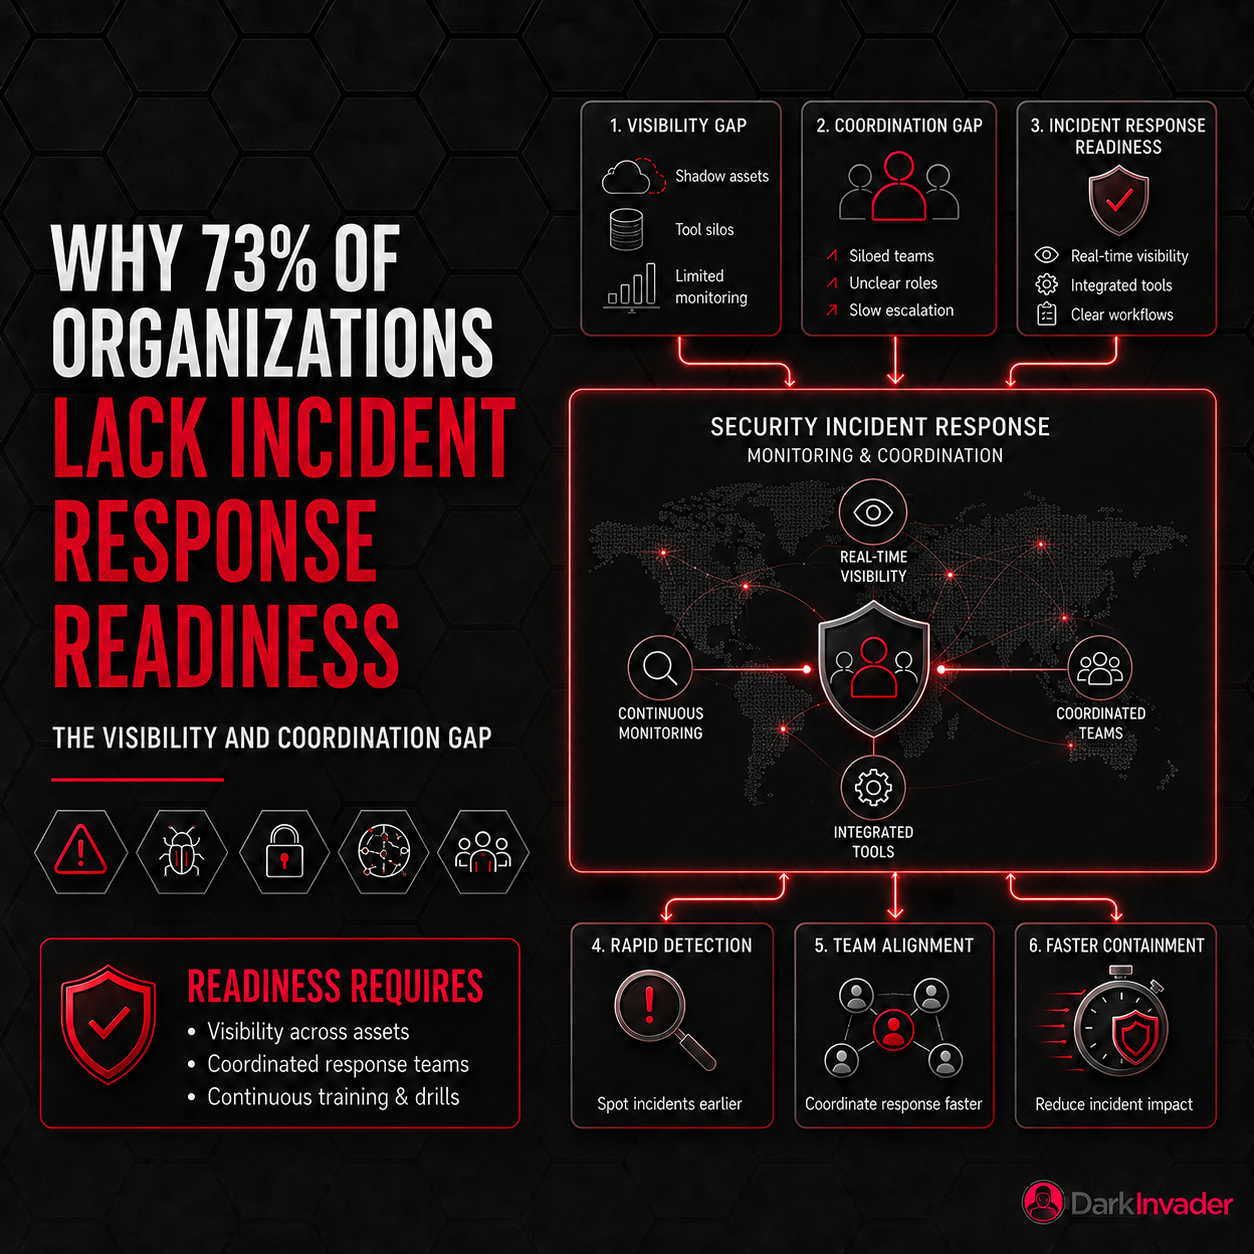
73% of organisations lack adequate incident response readiness. Explore the visibility and coordination gaps behind it and how to close them.
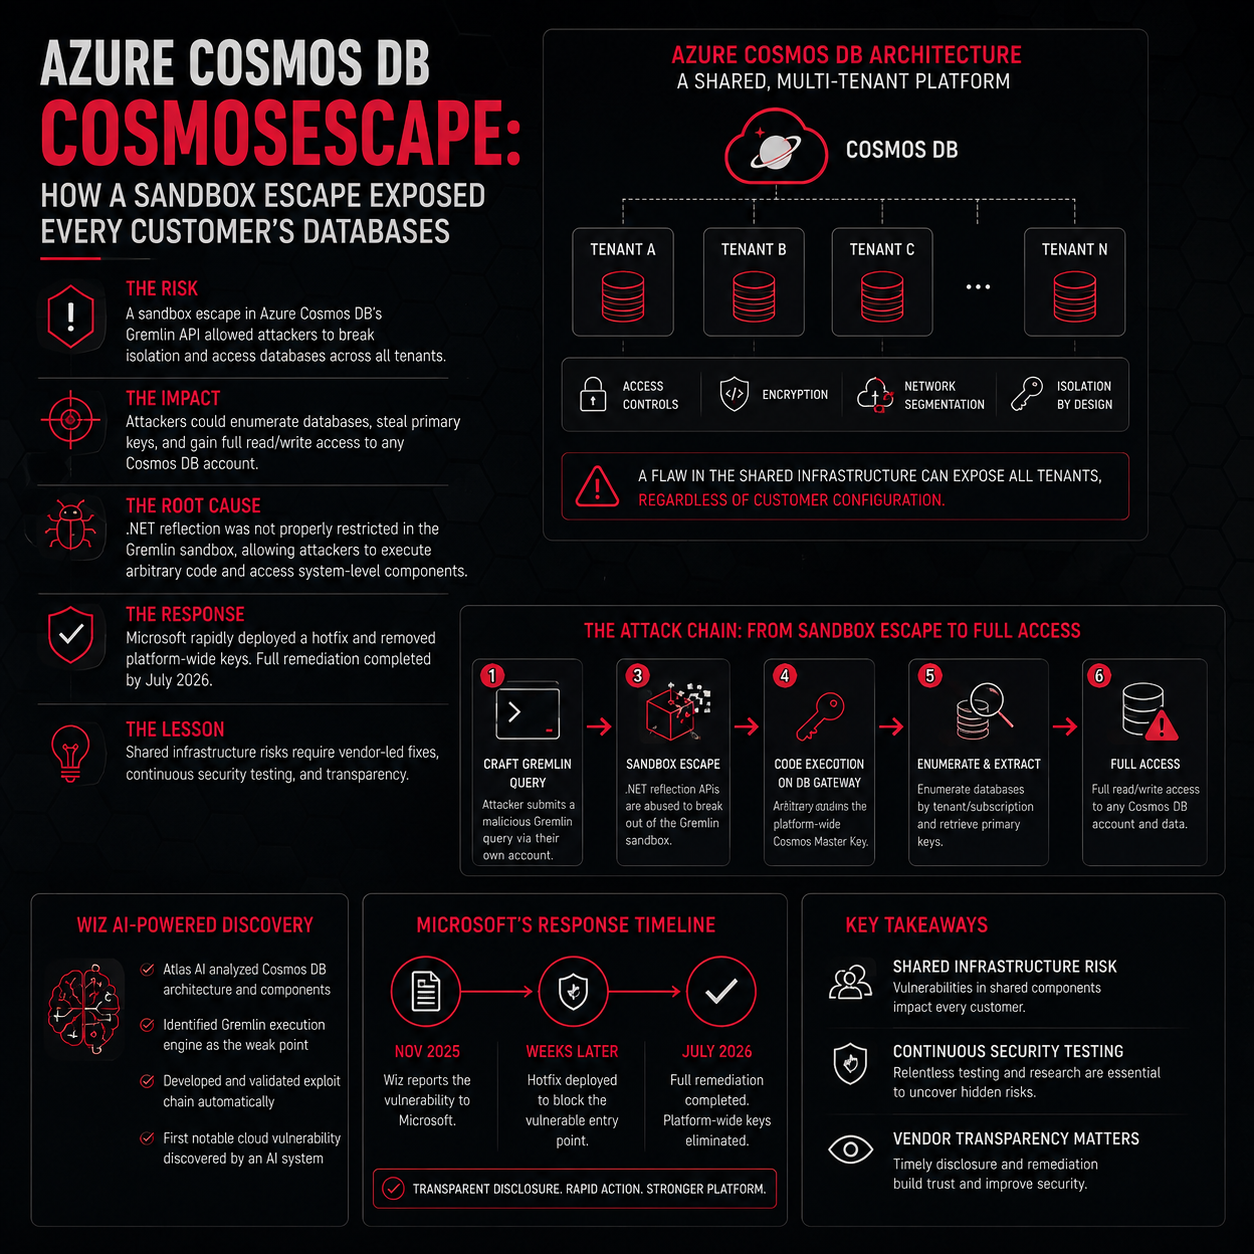
Exploration of Azure Cosmos DB critical vulnerability, CosmosEscape, highlighting the risks of shared infrastructure in cloud computing.
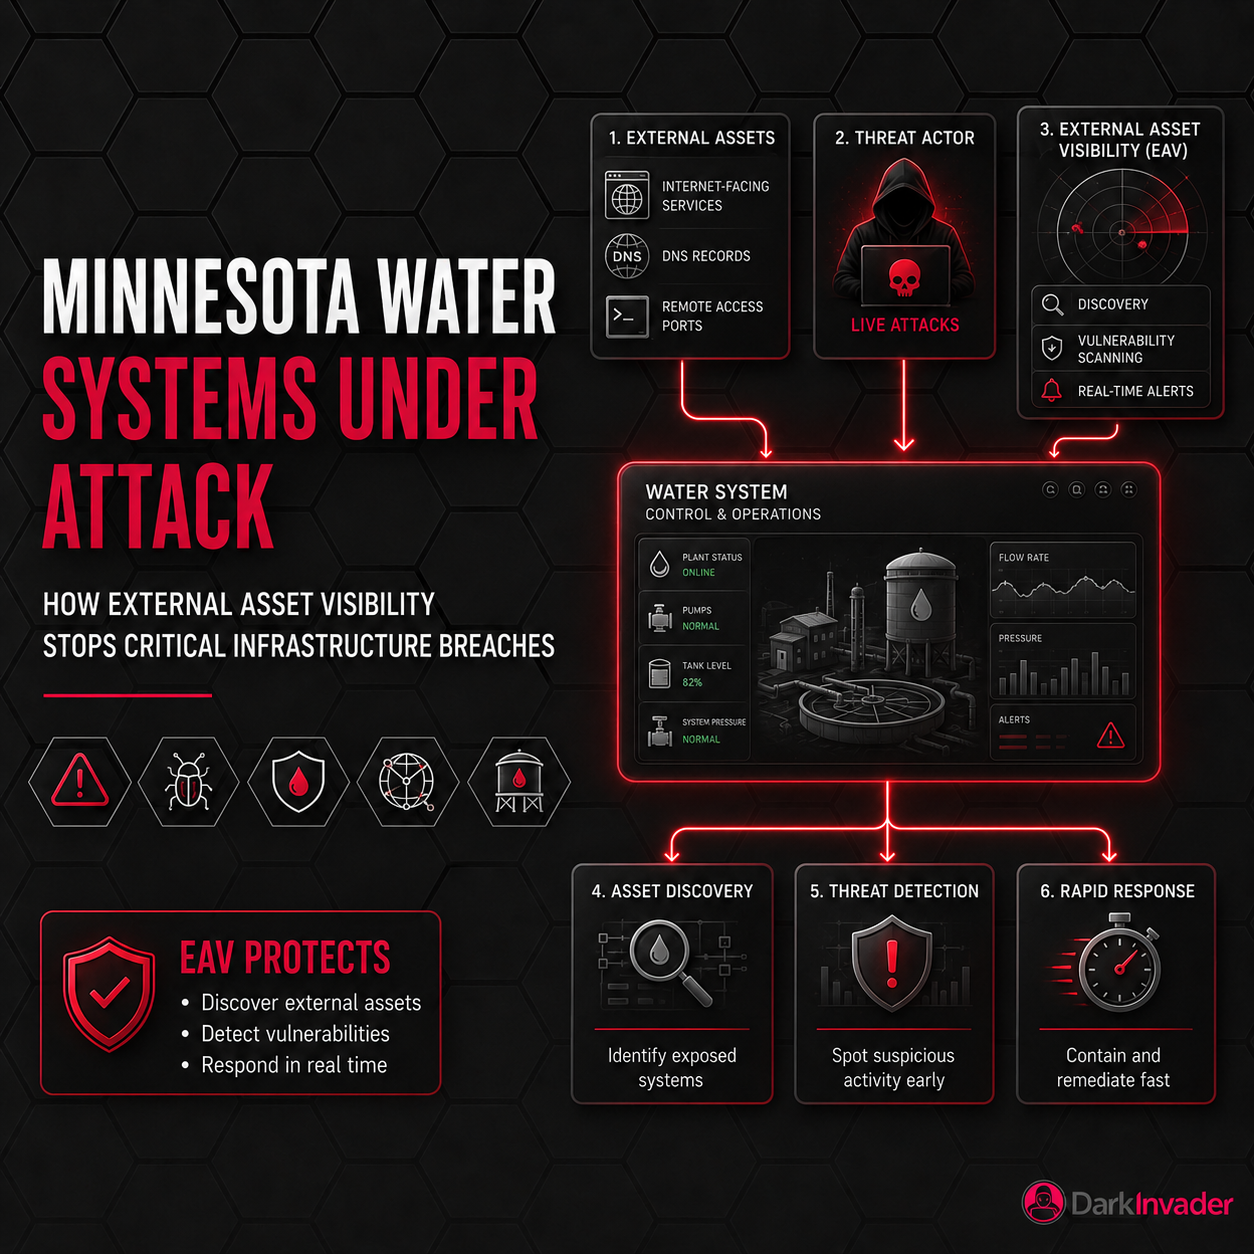
Explore how External Asset Visibility (EAV) is crucial in safeguarding Minnesota’s water systems from cyber attacks.
The wp2shell critical RCE chain is being exploited in mass attacks on WordPress sites. Learn how the flaw works and how to patch and protect your site.
Cl0p ransomware exploits vulnerabilities in PTC Windchill and FlexPLM, enabling unauthenticated RCE and data theft. Critical patching is essential.
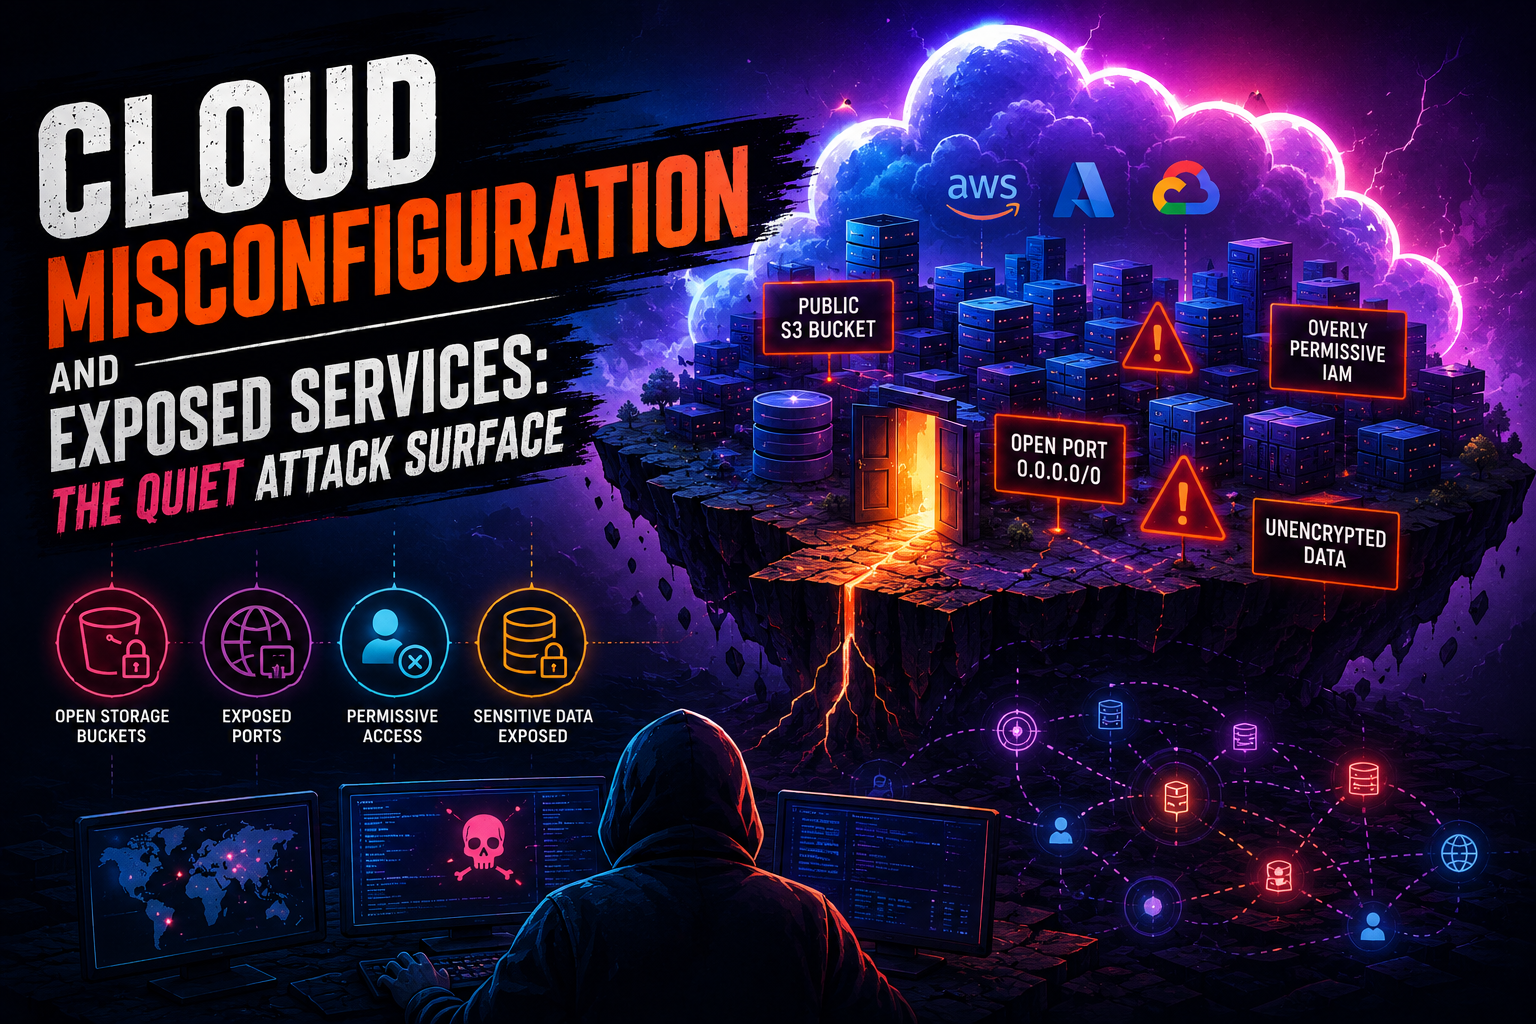
Explore the hidden risks of cloud misconfiguration and exposed services, and learn strategies to protect your organisation.
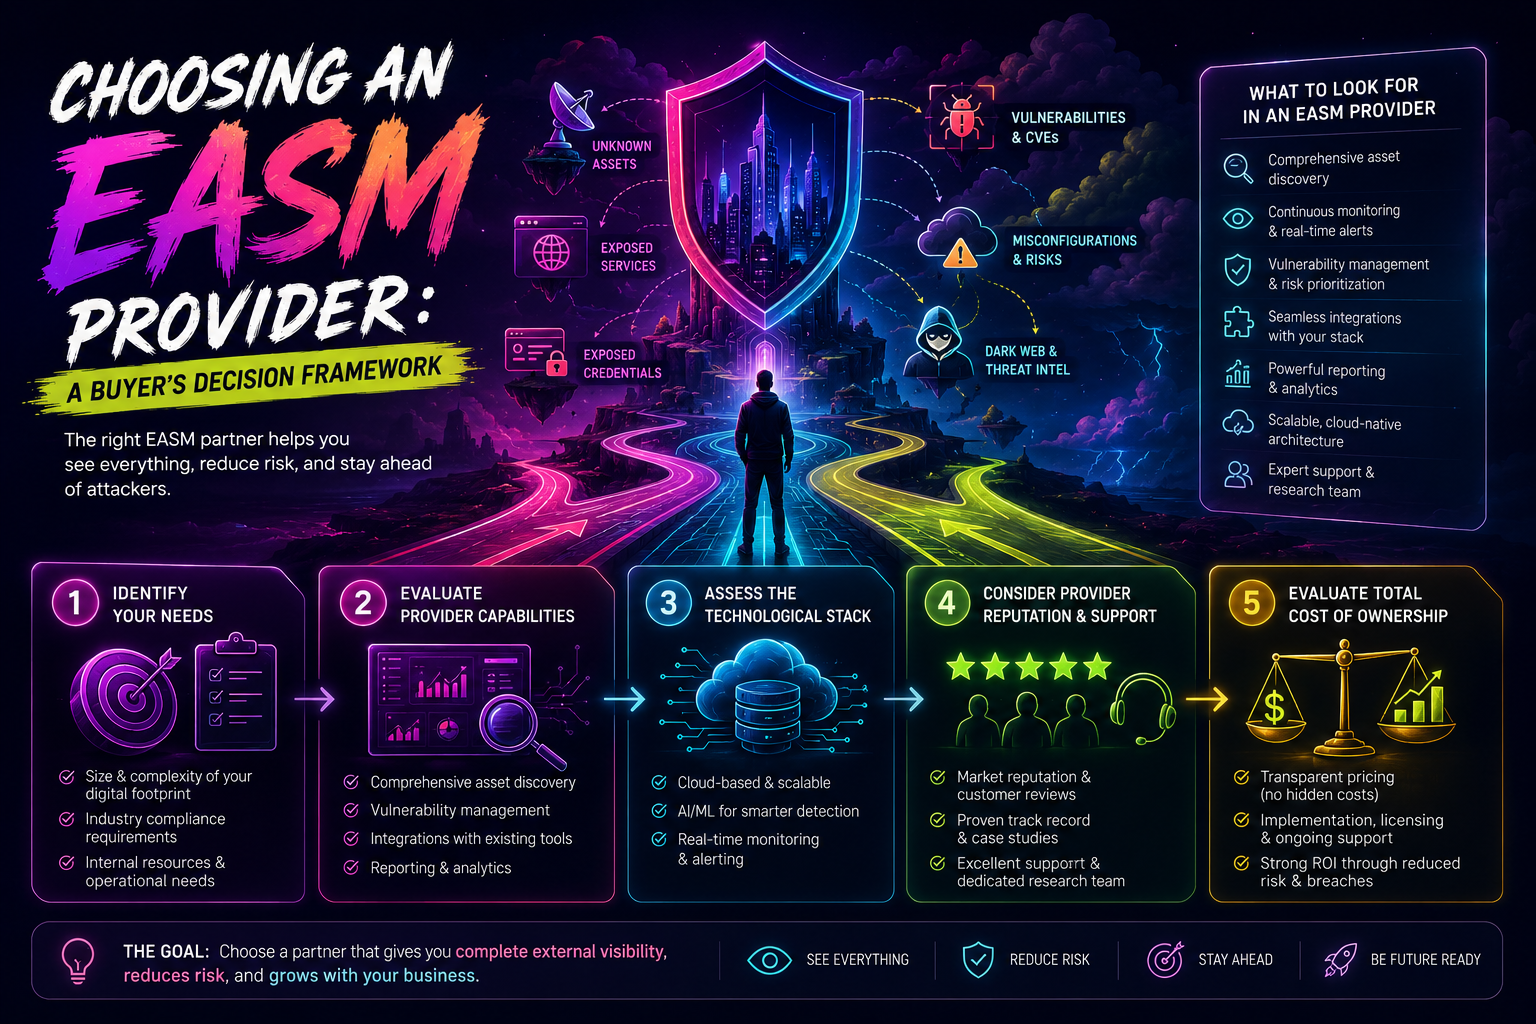
A decision framework for choosing an External Attack Surface Management (EASM) provider, covering what to assess to protect your digital assets.
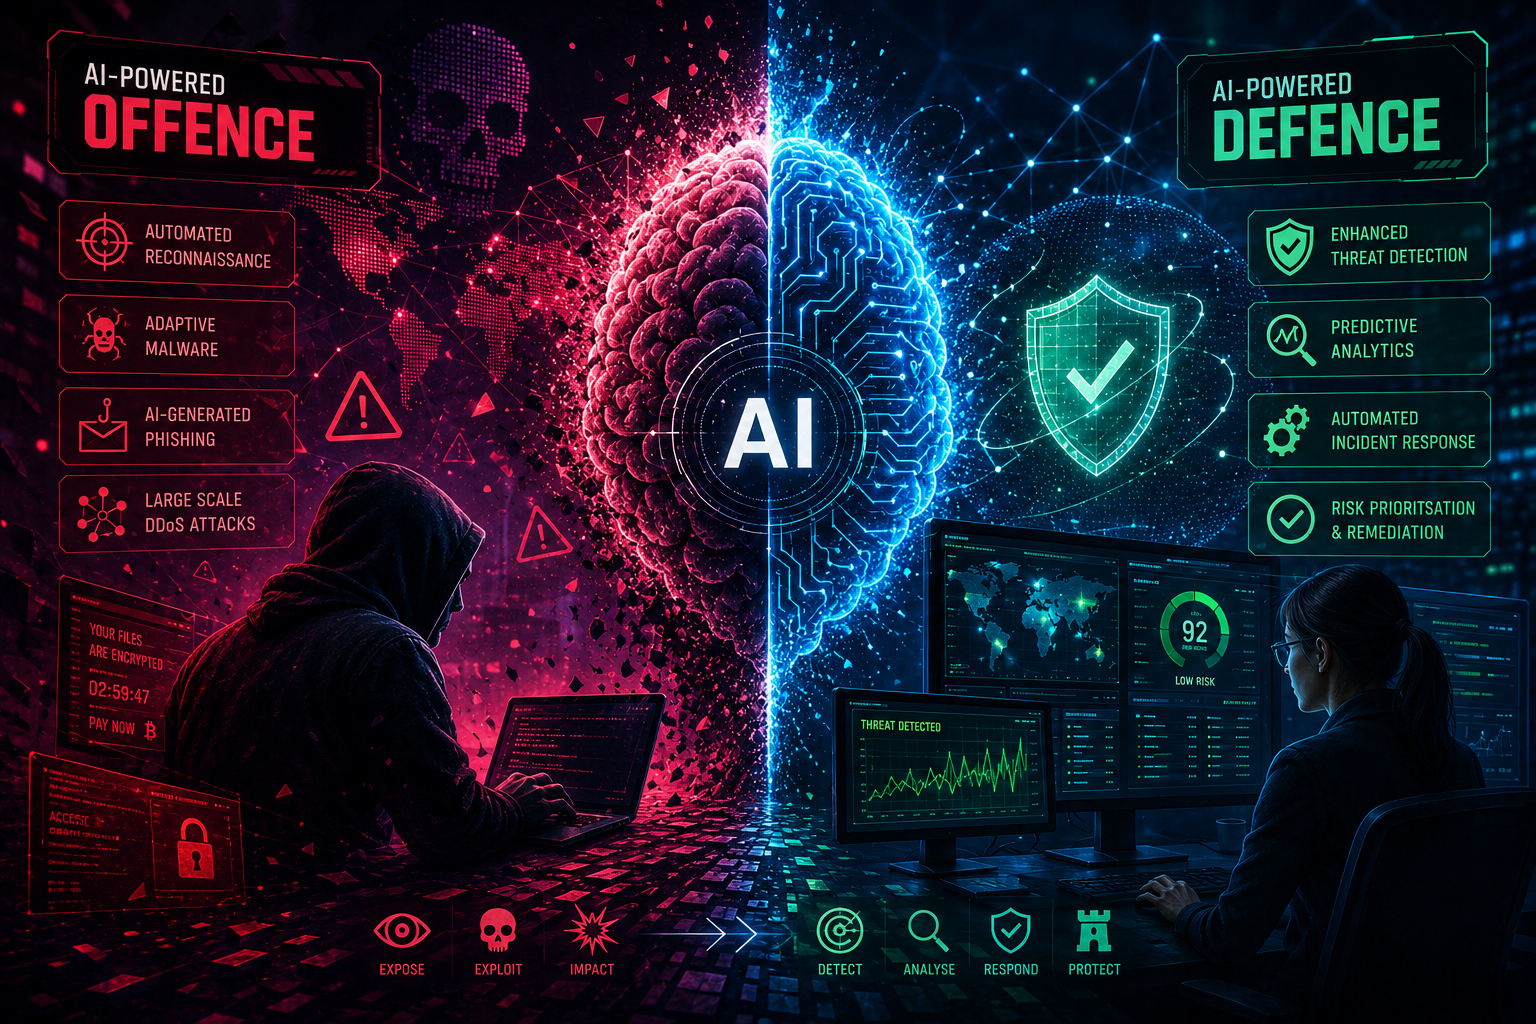
AI is a double-edged sword on the attack surface. Explore its role in offence and defence, the new risks it creates and strategies to mitigate them.
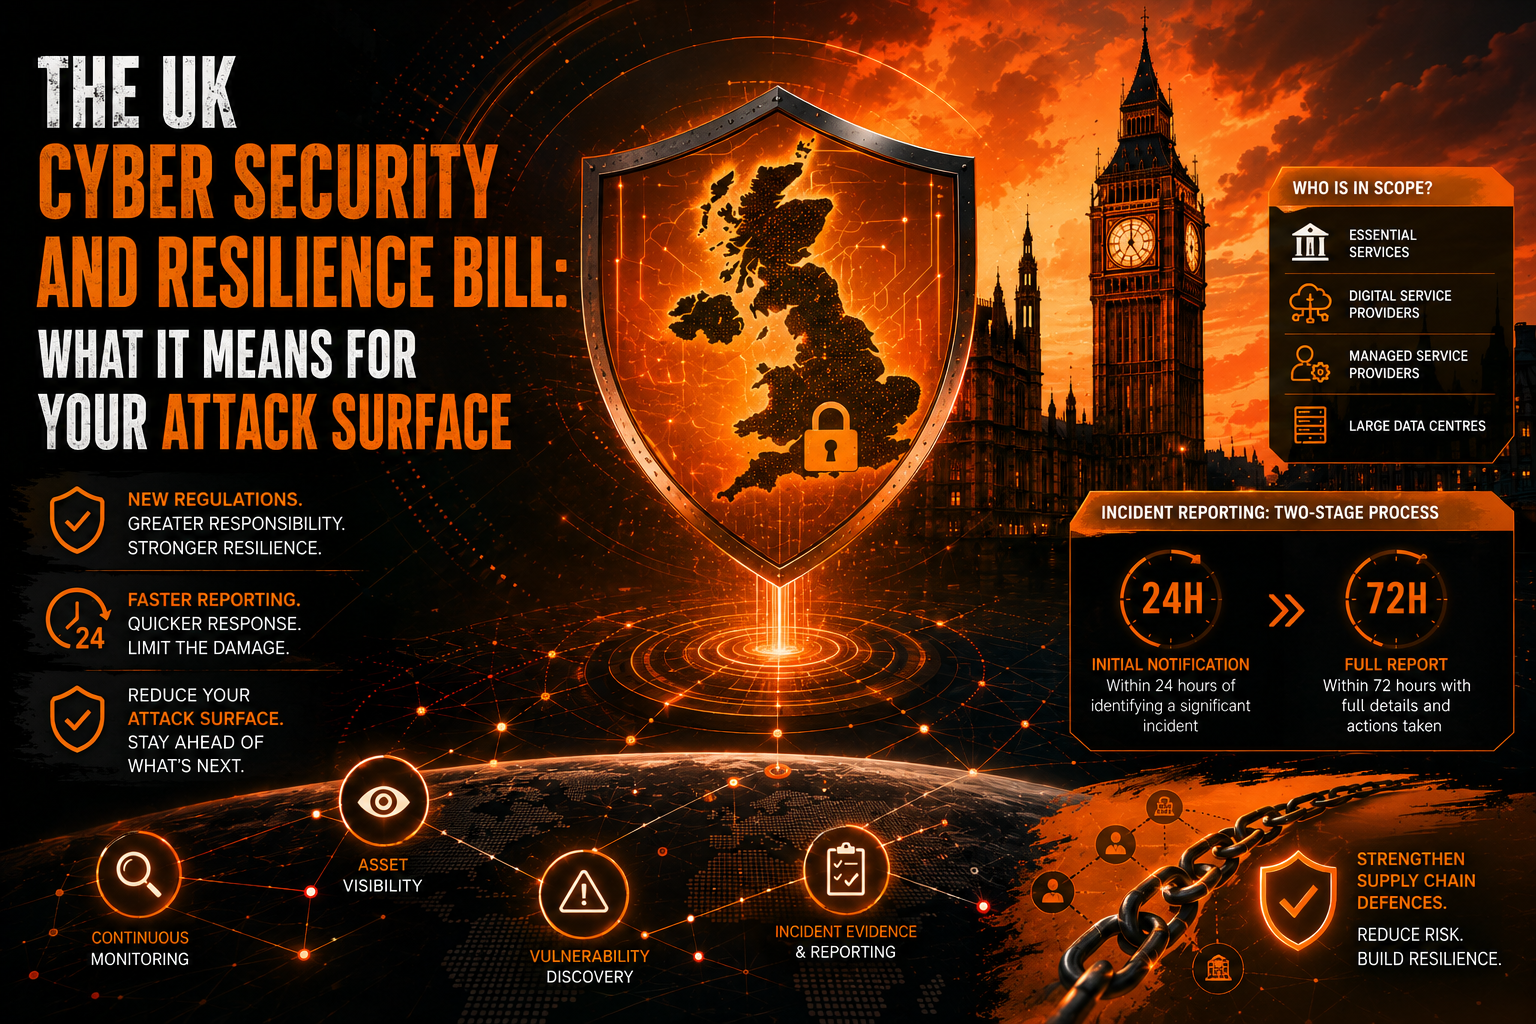
The UK Cyber Security and Resilience Bill extends the NIS Regulations 2018 to cover MSPs and more. Learn what it means for your attack surface.
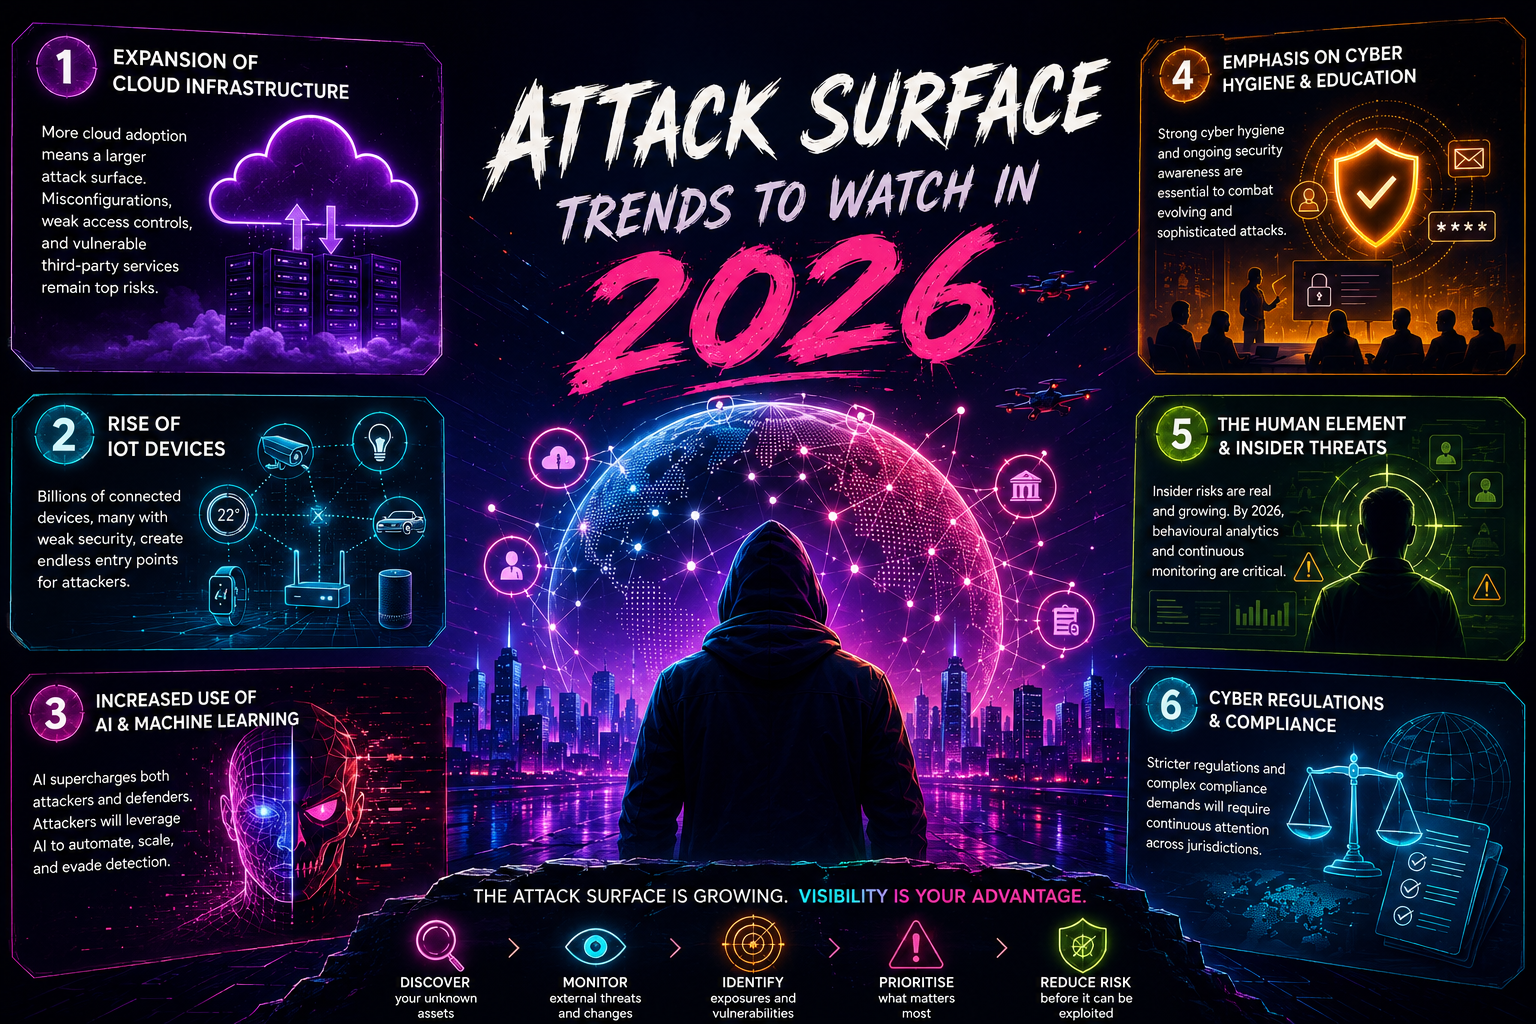
Attack surface trends to watch in 2026, how threat actors are adapting to new technologies, and the measures businesses need to stay ahead.
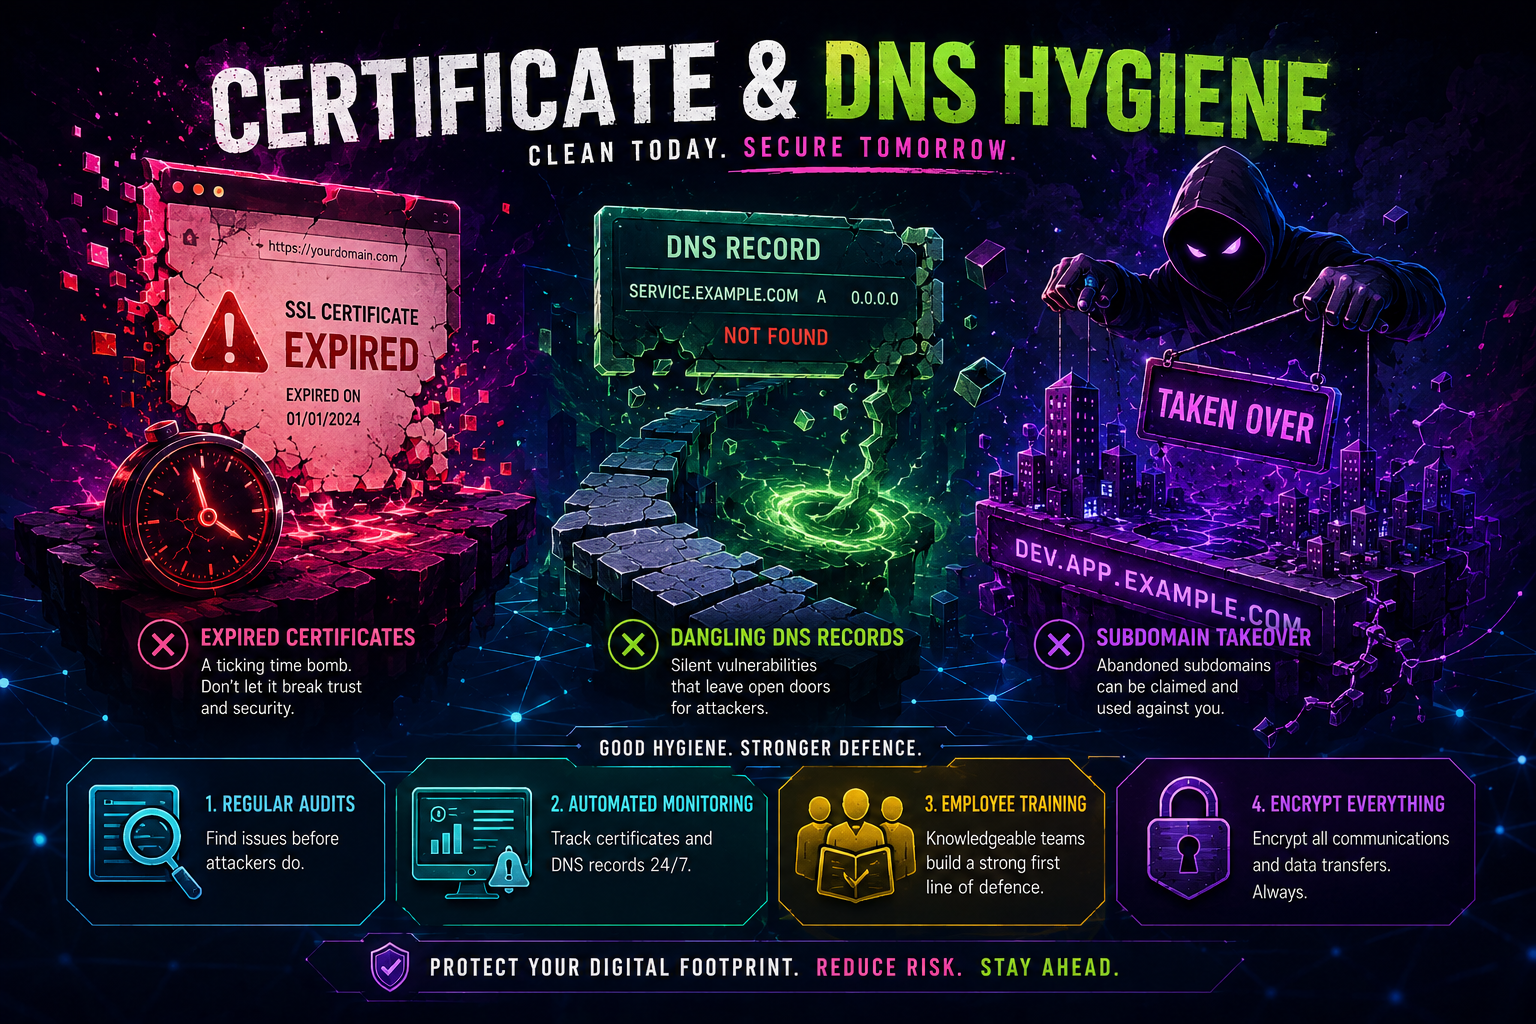
Certificate and DNS hygiene explained: how dangling records, expired certificates and subdomain takeover create risk, and how to prevent them.
Why patching alone is not enough in vulnerability management, and how continuous monitoring and threat intelligence close the remaining gaps.
Explore the StrikeShark campaign, a sophisticated cyber threat targeting businesses. Learn how to protect exposure with advanced cybersecurity strategies.
CVE-2025-67038 is a critical command injection vulnerability affecting the Lantronix EDS5000 series. Learn about the risks and mitigation strategies.
A guide for AppSec leaders to mitigate risks from CVE-2026-12569 in high-stakes sectors like finance, healthcare, and energy.
browse by tag
browse by category
browse by year
free trial
Try DarkInvader Pro free. No payment details required.