• category
Every post filed under this category, newest first.
Executive protection cyber monitoring gives close protection teams early warning from leaks, fake domains and threat chatter. See how to start.
Monitoring Telegram for threats, explained end to end: channel collection, noise reduction, verification and escalation. See how to build the workflow.
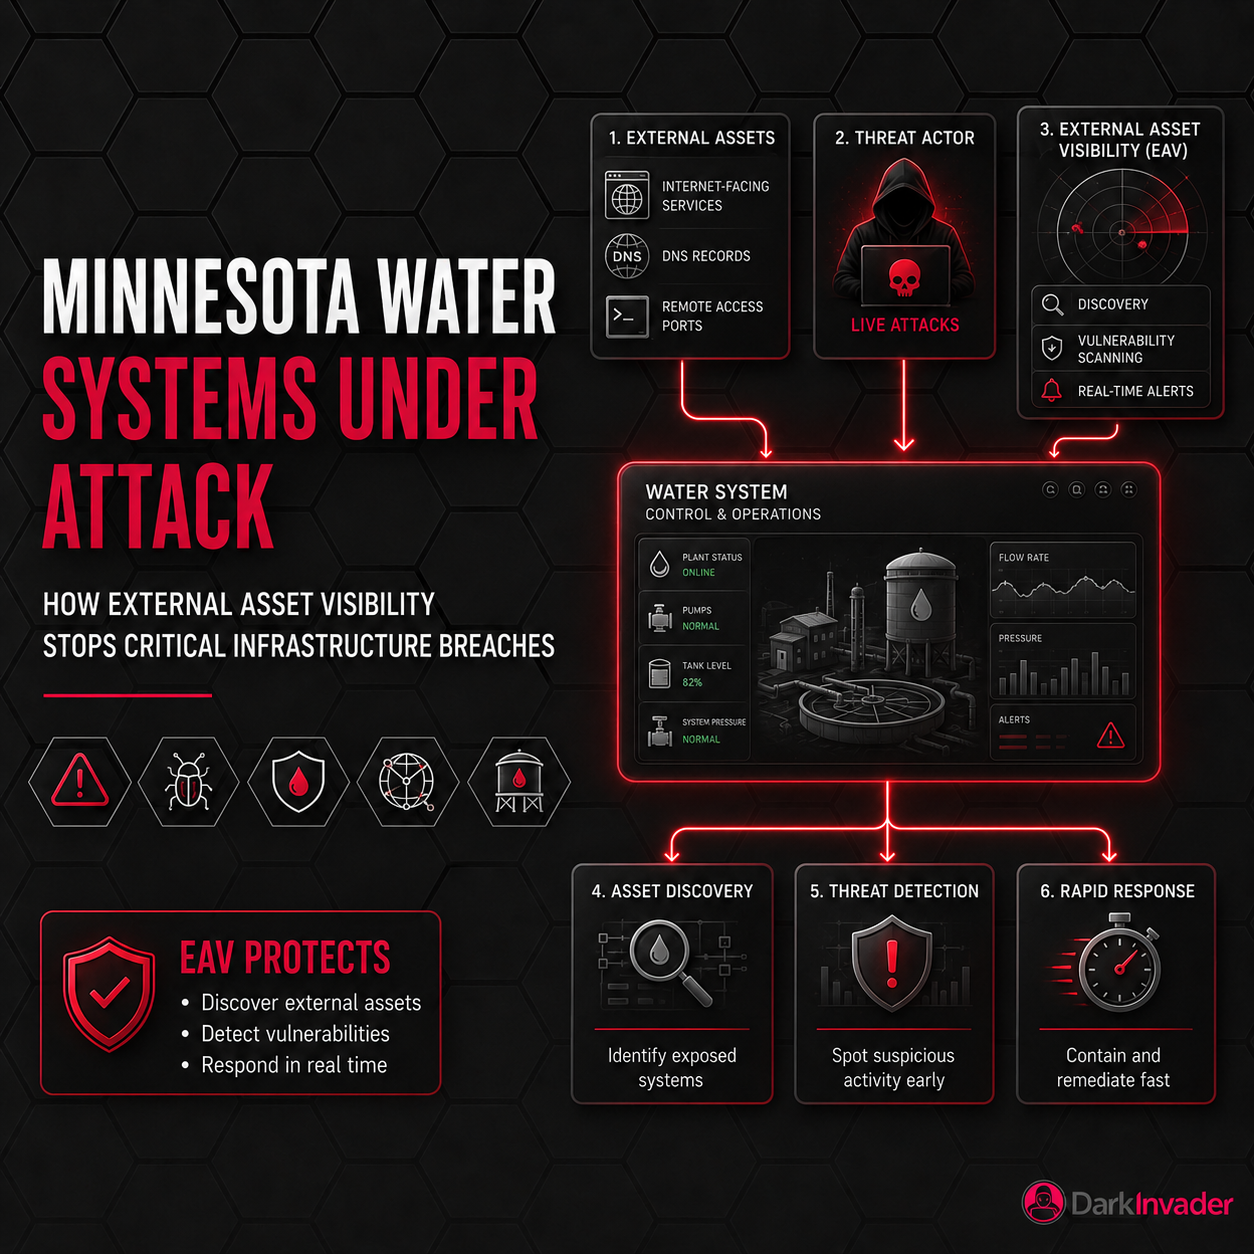
Explore how External Asset Visibility (EAV) is crucial in safeguarding Minnesota’s water systems from cyber attacks.
The wp2shell critical RCE chain is being exploited in mass attacks on WordPress sites. Learn how the flaw works and how to patch and protect your site.
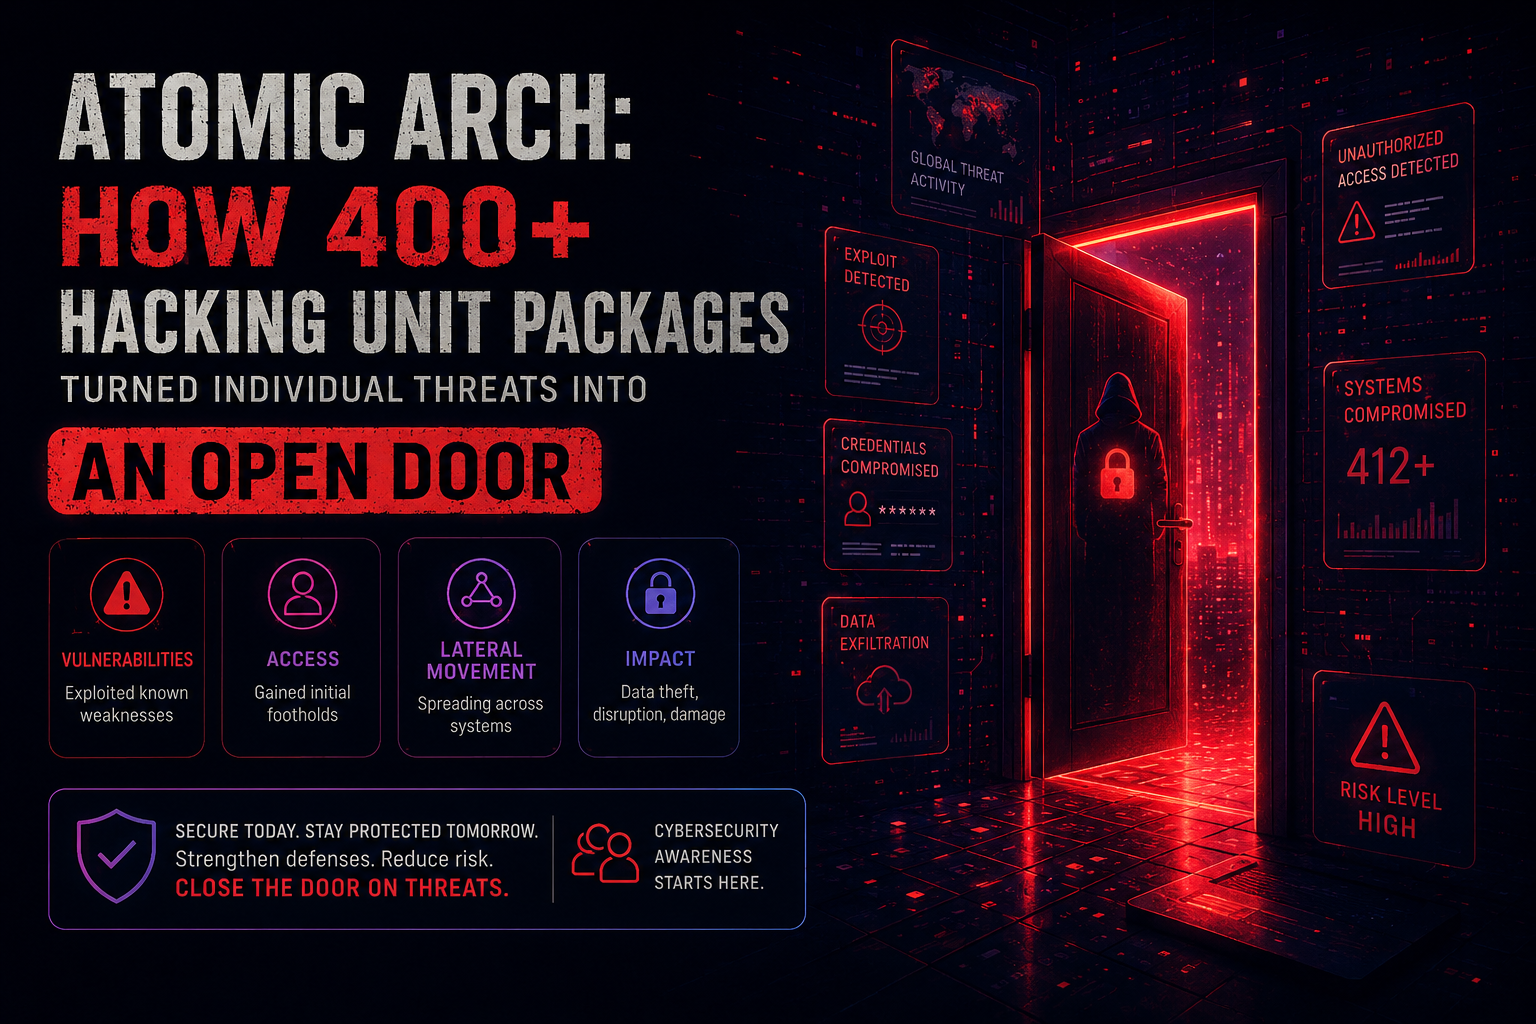
How over 400 hijacked Linux packages turned developer machines into an open door for attackers, and the measures needed to protect your ecosystem.
Exploring how Nexcorium targets IoT devices for attacks, their tactics, and strategies to mitigate these cyber threats.
Living off the land attacks use familiar tools to blend in. Learn how attackers hide in plain sight and how seeing yourself as they do reduces risk.
OSINT in 2025 is expanding beyond familiar sources to blockchain, decentralised networks and the metaverse. Learn how to use them to anticipate threats.
Your marketing website can fuel phishing, supply chain attacks and password guessing. Learn why it deserves the same caution as your other assets.
LinkedIn encourages oversharing, from tech stacks to ID badge photos. Learn the security risks it creates and how to share more smartly.
Reconnaissance is where every attack begins. Learn how seeking out the same information attackers would gives you visibility of your true external risk.
OSINT research should go beyond VIPs. App usage, credential reuse and shadow IT across the wider team create risks attackers can exploit at scale.
Shadow IT, from unauthorised apps to forgotten infrastructure, is a major blind spot. Learn how to detect and respond to it before attackers do.
Document metadata can leak usernames, emails and software details that aid phishing. Learn how attackers exploit it and how to sanitise files.
Low-risk OSINT data points can be linked into serious threats. Learn to think like an attacker and see how dangerous your digital breadcrumbs can be.
Subdomain takeover, dangling DNS and orphaned IPs are low-effort, high-impact attacks. Learn why mapping and monitoring your footprint matters.
AI is changing OSINT for defenders and attackers alike. Learn how AI speeds up intelligence gathering and why your security needs to keep pace.
VIPs are prime cyber attack targets due to their access and habits. Learn how attackers research them and how monitoring and planning reduce the risk.
Combining reverse image search with typosquatting checks helps you detect fake websites early, protect your brand and act quickly to take them down.
Social media poses hidden IT security risks, from phishing and data leakage to espionage. Learn the policies and training that reduce exposure.
OSINT is transforming intelligence and police work, from tracking crime to identifying terrorist networks. Explore its growing role, challenges and future.
Why OSINT is important for your business: the benefits of open source intelligence and the types of OSINT techniques used at DarkInvader.
How organisations can use open source intelligence (OSINT) to gain insight into their external attack surface, strengthen defences and fix weaknesses.
This blog covers how IT teams can identify unknown public attack vectors through OSINT gathering. This blog outlines what OSiNT is and the purpose of this.
browse by tag
browse by category
browse by year
free trial
Try DarkInvader Pro free. No payment details required.