
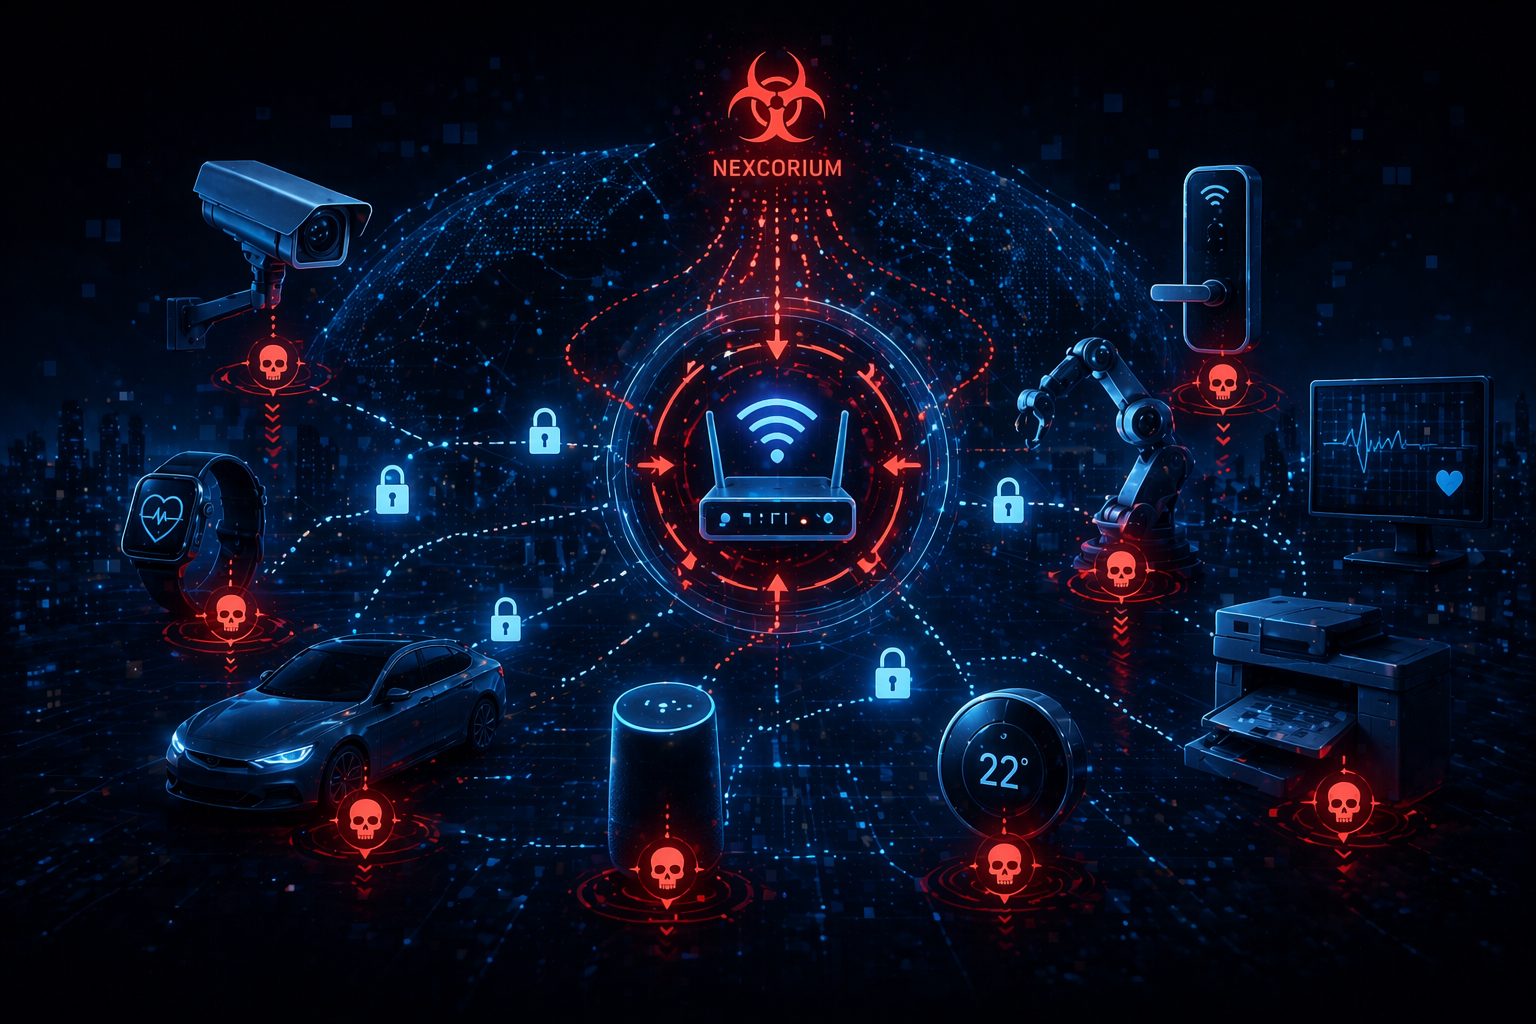
In the ever-evolving landscape of cybersecurity threats, Nexcorium has emerged as a noteworthy adversary, particularly in their approach to targeting Internet of Things (IoT) devices. These devices, integral to modern life, pose unique security vulnerabilities that Nexcorium exploits with increasing sophistication. This blog post delves into the methods used by Nexcorium to target IoT devices, explores their motivations, and suggests strategies to mitigate these threats.
Understanding IoT Devices and Their Vulnerabilities
IoT devices range from simple sensors and home automation systems to complex industrial machines. These devices are characterised by limited processing power and storage, often running on outdated software without regular updates. Such characteristics make them vulnerable targets for cyber attacks.
Key Vulnerabilities in IoT Devices
- Lack of Regular Updates: IoT devices often run on software that rarely receives updates, making them susceptible to known vulnerabilities.
- Default Credentials: Many devices still operate using default factory settings, including credentials, which are easy for attackers to bypass.
- Weak Encryption Standards: Some devices utilise minimal encryption, if any, facilitating easy data interception.
Nexcorium's Targeting Tactics
Nexcorium employs various tactics to compromise IoT devices. These methods are constantly evolving, but some prevalent strategies include:
1. Network Scanning
Nexcorium uses network scanning tools to locate IoT devices connected to the internet. These tools identify devices by IP addresses and assess their potential vulnerabilities. The attackers can thereby discern which devices are most susceptible to infiltration.
2. Exploiting Default Settings
Hackers exploit factory defaults like unchanged passwords and unsecured Wi-Fi connections to gain access to IoT ecosystems. This strategy remains effective given the widespread neglect of basic security measures by users and manufacturers alike.
3. Malware Injections
Malicious software specifically designed for IoT environments is used by Nexcorium to gain control over devices. Botnets, for example, commandeer large numbers of devices, turning them into a network capable of launching DDoS attacks or mining cryptocurrencies.
4. Device Configuration Manipulation
Once access is achieved, attackers can alter the configurations of devices to perform tasks surreptitiously, collect sensitive information, or disrupt regular operations.
The Implications of IoT Attacks
An attack on IoT infrastructure by Nexcorium has far-ranging consequences. Beyond mere data theft, these attacks can lead to significant operational disruptions. In scenarios where IoT is part of critical infrastructure, such as healthcare or utilities, the stakes are exponentially higher.
Mitigation Strategies Against IoT Threats
While the threat landscape appears daunting, several strategies can be adopted to improve IoT security:
Regular Software Updates
Ensure that all devices receive the latest firmware updates. This is vital to patch known vulnerabilities and enhance device resilience against emerging threats.
Secure Network Configurations
Adopt robust encryption standards and secure network settings to guard against unauthorised access. Changing default settings and employing strong, unique passwords for each device can significantly reduce vulnerability.
DarkInvader's Role
Solutions like DarkInvader's vulnerability scanning services play a crucial role in identifying potential threats early. By leveraging such resources, organisations can proactively address vulnerabilities before exploitation by entities like Nexcorium.
Educating Users
Educating users about the importance of IoT security cannot be overstated. Awareness and training can foster an environment where best practices are routinely observed, further limiting opportunities for attackers.
Implementing Intrusion Detection Systems
Deploying sophisticated intrusion detection systems that are capable of recognising unusual behaviours within IoT networks can serve as an early warning system, allowing for prompt countermeasures.
Conclusion
Nexcorium's targeting of IoT devices underscores the importance of vigilant security practices. As IoT continues to proliferate, the scope of potential vulnerabilities expands, and with it, the necessity for robust security frameworks. By understanding the tactics used by adversaries like Nexcorium and implementing comprehensive mitigation strategies, individuals and organisations can better defend against these persistent threats.
FAQs
What is the primary method used by Nexcorium to attack IoT devices?
Nexcorium often employs network scanning to identify vulnerable IoT devices. This enables them to target devices with outdated software or default credentials easily discoverable online.
How can IoT device owners protect their devices from Nexcorium attacks?
Owners should regularly update device firmware, change default settings, and implement strong passwords. Employing DarkInvader's vulnerability scanning services can also aid in identifying security weaknesses.
Why are IoT devices more vulnerable to cyber attacks?
IoT devices typically have limited processing capabilities and often lack regular security updates. These factors, combined with frequent use of default factory settings, make them attractive targets for attackers like Nexcorium.
What role does malware play in Nexcorium’s strategy?
Malware is used to gain control of IoT devices, often incorporating them into botnets that can be utilised for various malicious activities, such as DDoS attacks or data theft.