
In the ever-evolving landscape of cybersecurity threats, the FortiBleed credential-harvesting campaign has emerged as a significant concern for organisations reliant on Fortinet's widely utilised security solutions. This campaign has been designed to exploit vulnerabilities, specifically targeting the authentication mechanisms of Fortinet devices. In this post, we'll explore the intricacies of FortiBleed, its implications, and how organisations can defend against such threats.
Understanding FortiBleed
What is FortiBleed?
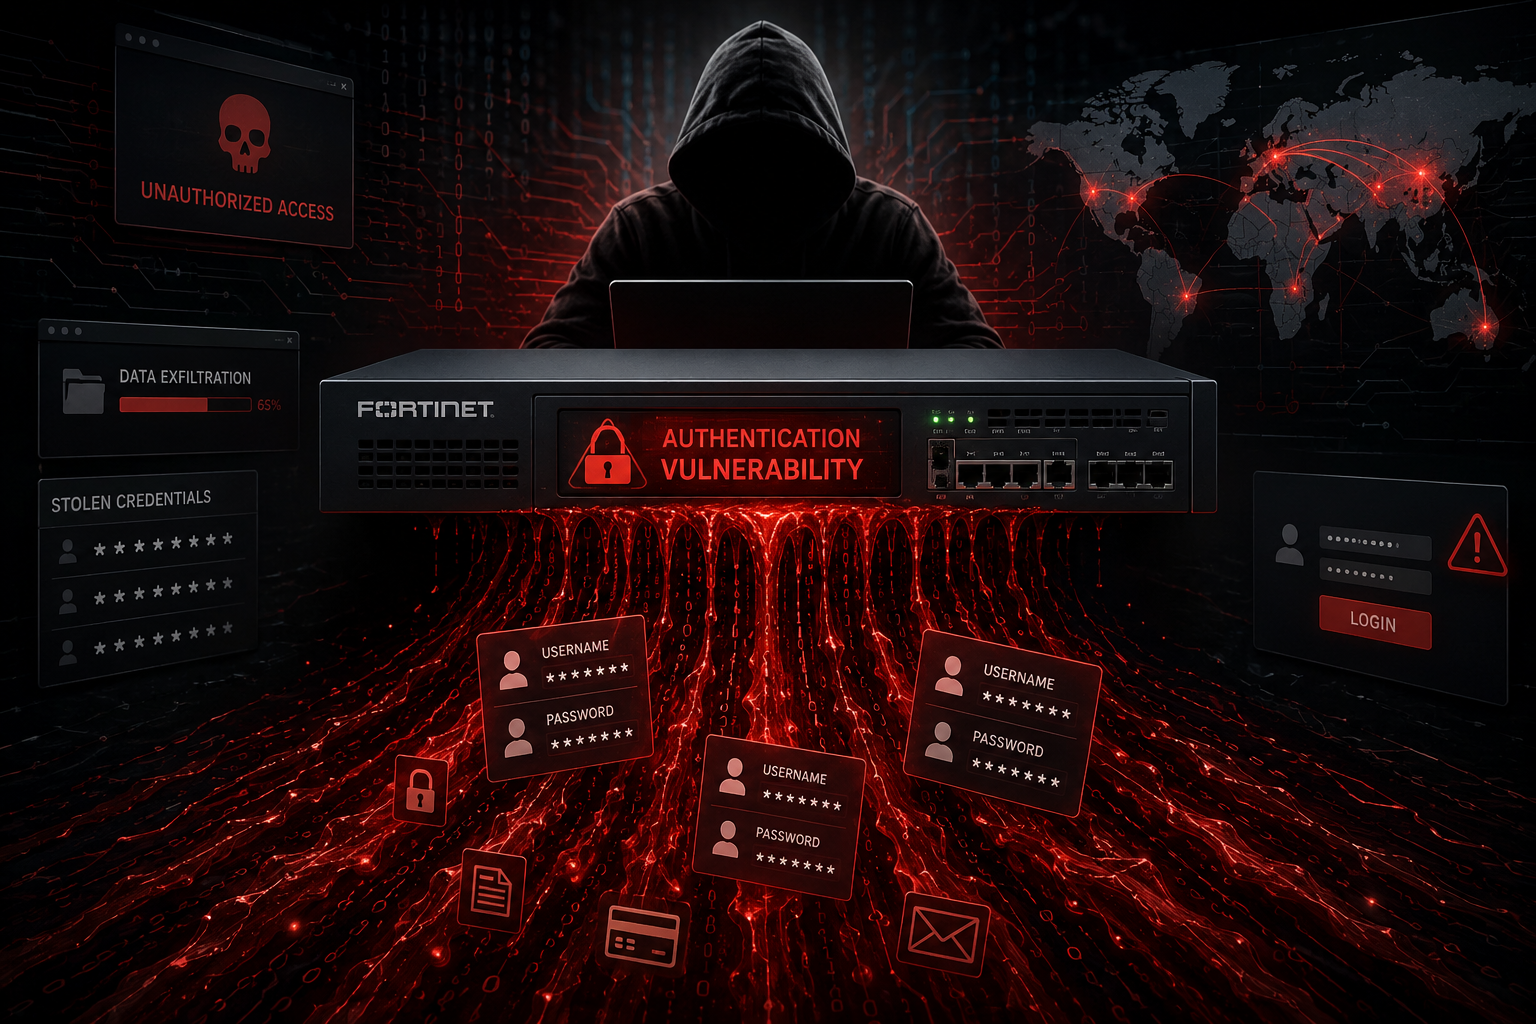
FortiBleed is a sophisticated campaign aimed at harvesting credentials from Fortinet security devices. It primarily focuses on exploiting weaknesses in the authentication process, allowing attackers to gain unauthorized access to networks and sensitive data. With the increasing reliance on Fortinet's security solutions across various sectors, this campaign poses a serious threat to enterprise security.
The Anatomy of the Attack
The FortiBleed attack methodically exploits specific vulnerabilities within Fortinet's authentication process. Attackers use various techniques, including phishing and malware, to trick users into revealing credentials. These stolen credentials are then used to access networks and potentially exfiltrate data. One key aspect of FortiBleed is its ability to remain undetected while carrying out its operations, making it exceptionally dangerous.
Potential Impact
The impact of the FortiBleed campaign can be catastrophic. Unauthorised access to a network can lead to data breaches, financial loss, and reputational damage. In some cases, it may also pave the way for further cyber-attacks, like ransomware or advanced persistent threats.
Defending Against FortiBleed
Fortinet's Response
Fortinet has been actively working to patch the vulnerabilities exploited by FortiBleed. Regular updates and patches are critical components of their defence strategy. It's essential for users of Fortinet products to keep their systems updated with the latest patches.
Proactive Security Measures
Organisations must adopt a proactive stance to defend against FortiBleed-like threats. Here are a few strategies that can help:
- Implement Multi-Factor Authentication (MFA): MFA adds an extra layer of security, making it more difficult for attackers to gain access even if they have valid credentials.
- Regular Security Audits: Conducting frequent audits can help identify and rectify potential vulnerabilities before they can be exploited.
- User Training and Awareness: Educating users about phishing and social engineering attacks is critical in reducing the risks associated with credential theft.
Specialised Monitoring Solutions
Utilising services like the Dark Web Monitoring offered by DarkInvader can provide an additional layer of protection by tracking and monitoring potential threats that may arise from compromised credentials.
The Role of External Support
Engaging Cybersecurity Experts
Leveraging the expertise of cybersecurity professionals can significantly bolster an organisation’s defences against sophisticated campaigns like FortiBleed. These experts can offer insights and tailor strategies that align with specific needs.
Utilising Third-Party Integrations
Integrations with other security platforms can enhance overall protection. For instance, DarkInvader provides solutions involving third-party integrations that can seamlessly work with existing security infrastructures.
Summary
The FortiBleed campaign serves as a stark reminder of the persistent threats within the cybersecurity realm. As attackers continue to evolve their methods, it is imperative for organisations to stay vigilant and proactive in their defence strategies. Regular updates, user education, advanced security measures, and the right external support are key to defending against such malicious campaigns.
FAQ
What is FortiBleed?
FortiBleed is a mass credential-harvesting campaign targeting vulnerabilities in Fortinet's authentication processes, leading to unauthorized access to networks and sensitive data.
How can organisations protect themselves from FortiBleed?
Protective measures include implementing MFA, conducting regular security audits, enhancing user awareness, and using specialised monitoring solutions like those offered by DarkInvader.
Are there any tools to detect compromised credentials?
Yes, services such as DarkInvader's leaked credentials monitoring can help detect if your organisation's credentials have been compromised and are available online.
What should be done if credentials are suspected to be compromised?
Immediate actions should include changing all potentially affected passwords, notifying relevant stakeholders, and conducting a thorough investigation to assess any further exposure or damage.
By understanding and proactively managing the risks associated with FortiBleed, organisations can minimise the likelihood of successful attacks and protect their assets from detrimental exposure.