Insight on cybercrime, dark web activity, OSINT and attack surface management from the DarkInvader research team.
browse by category
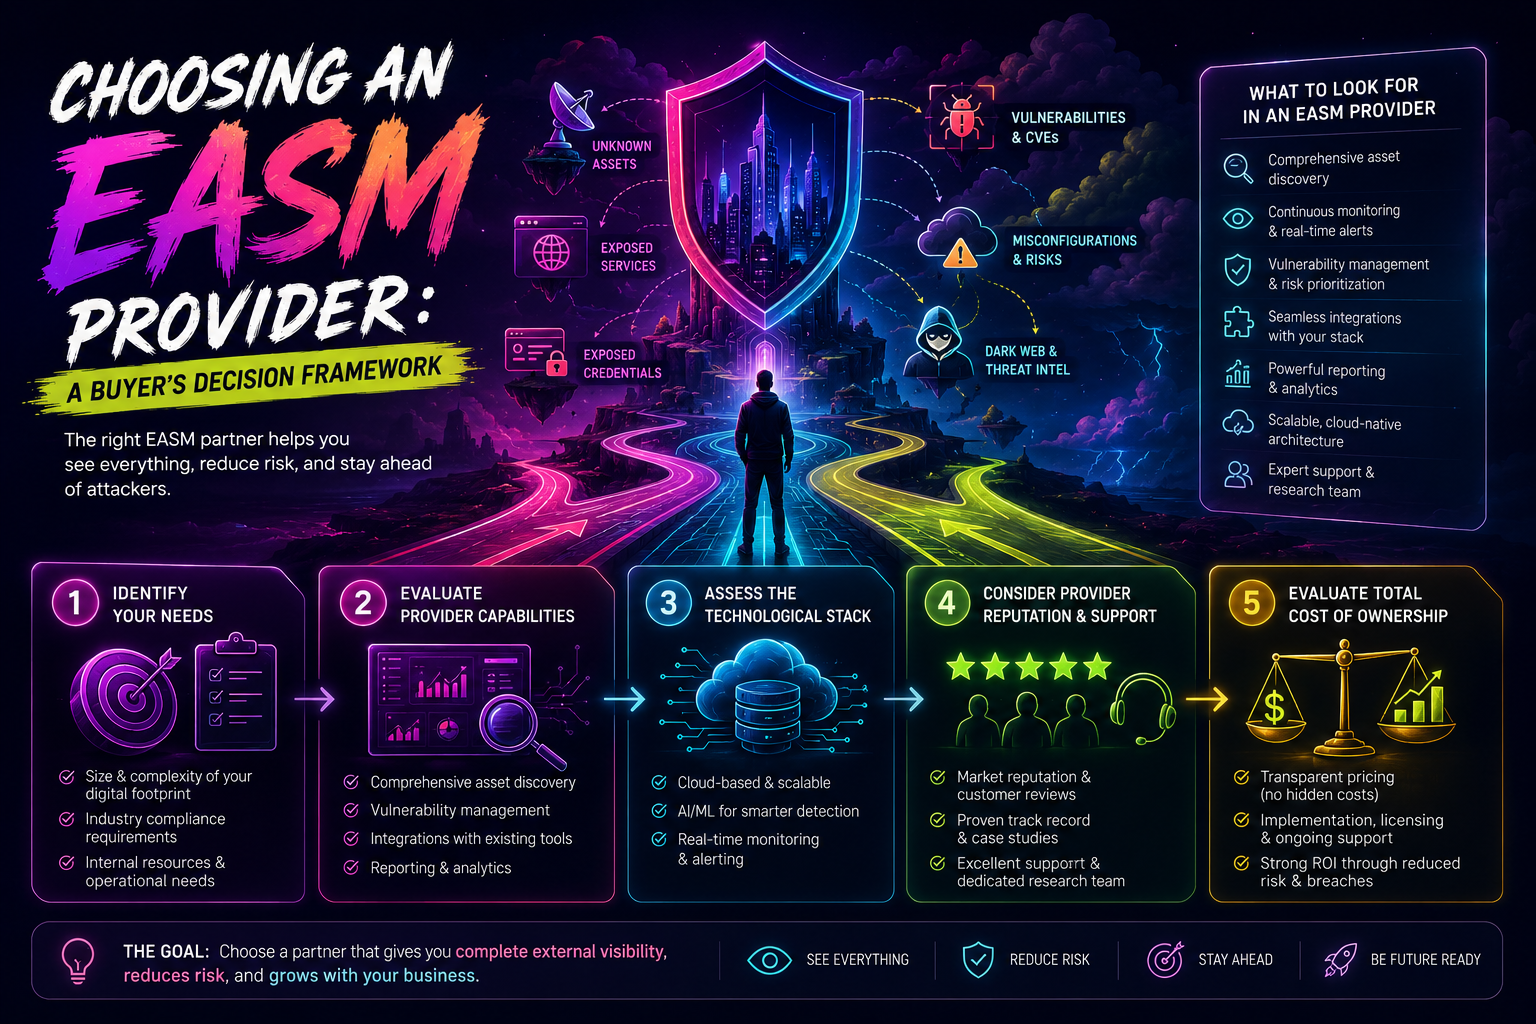
Explore a comprehensive framework to select the right External Attack Surface Management (EASM) provider, ensuring robust cybersecurity and safeguarding digital assets.
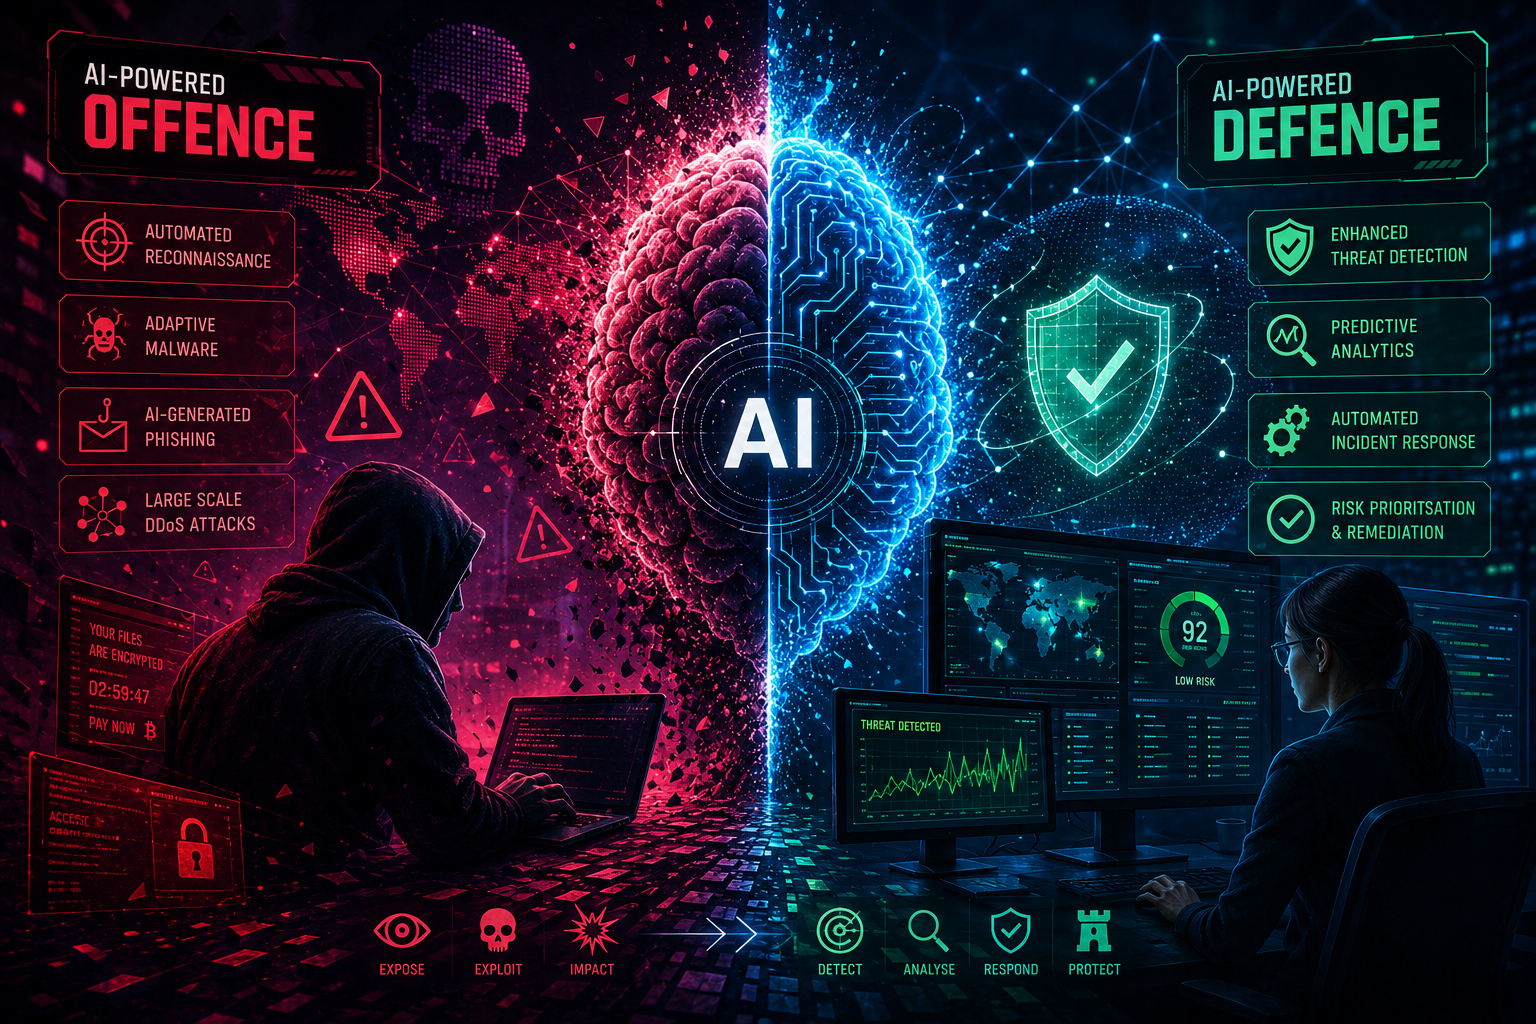
Explore the dual nature of AI in cybersecurity, highlighting its roles in offense and defence, challenges on the attack surface, and strategies to mitigate risks.
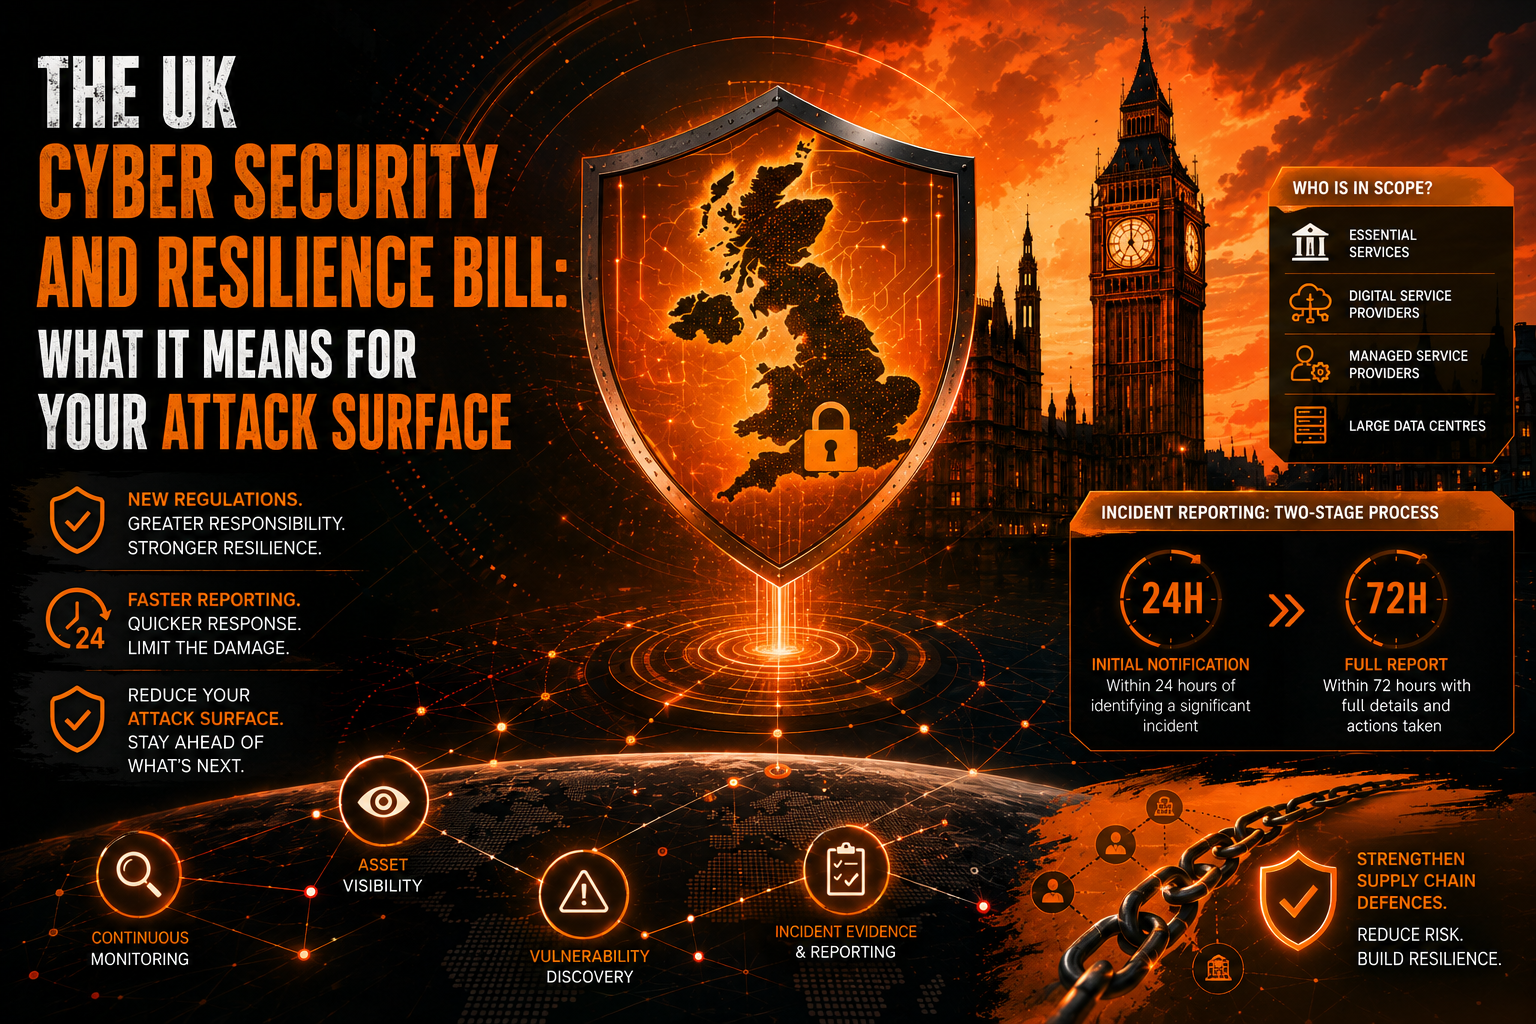
Explore the UK’s Cyber Security and Resilience Bill and its impact on your organisation’s attack surface.
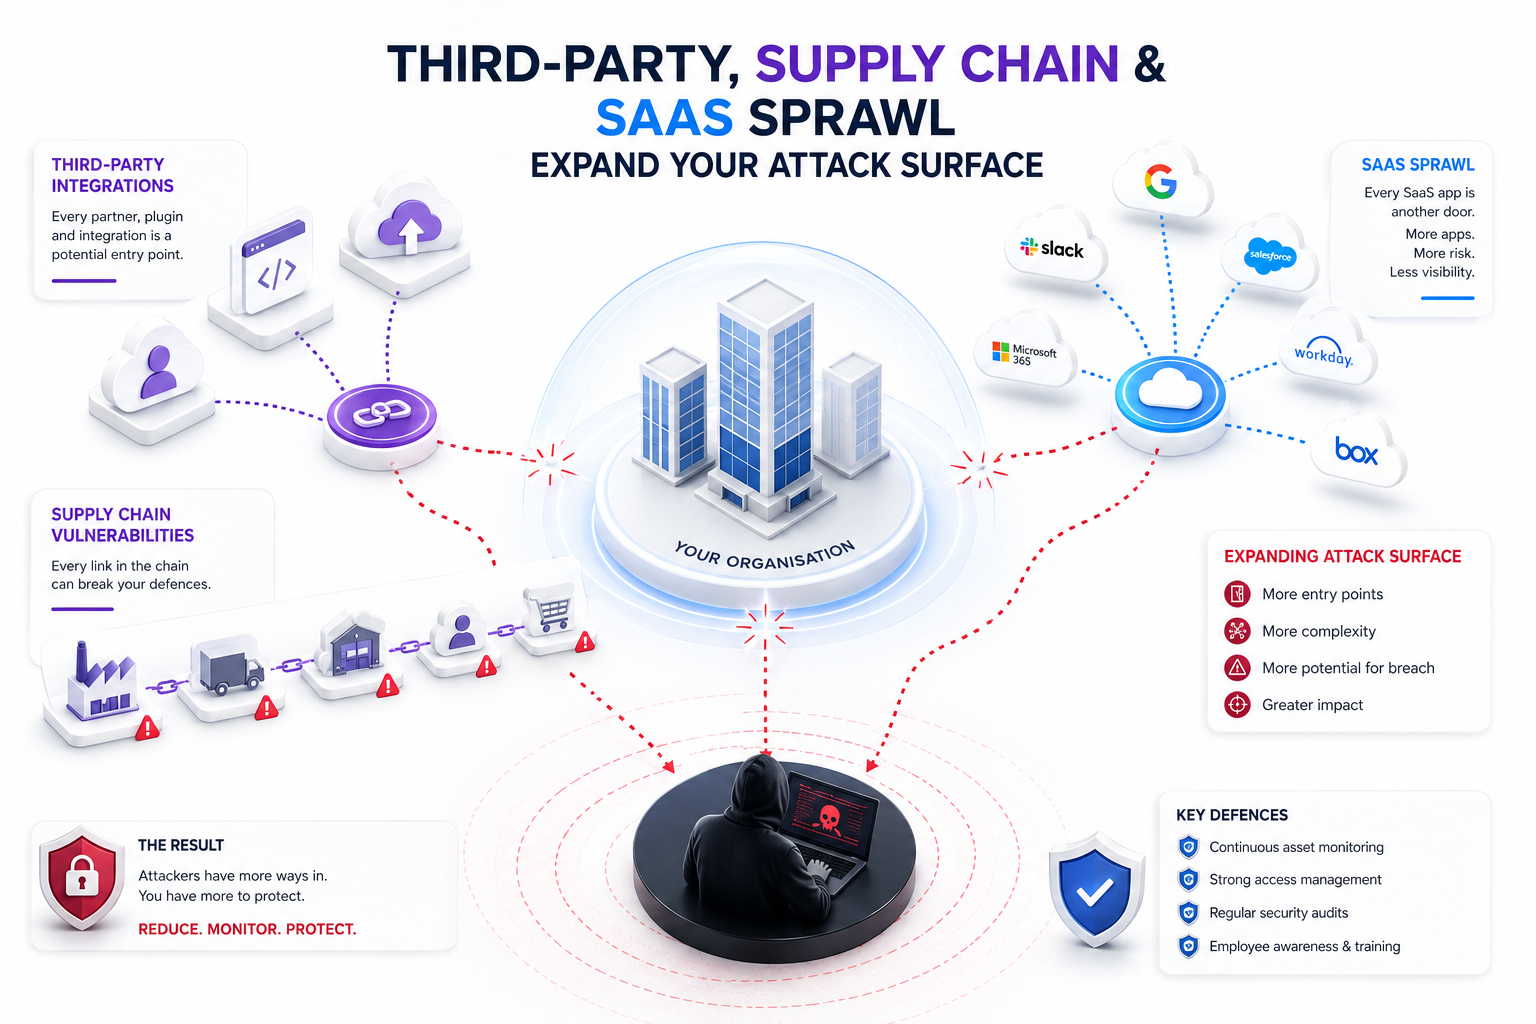
Explore how third-party vendors, supply chains, and SaaS applications contribute to attack surface expansion and discover strategies for minimisation.
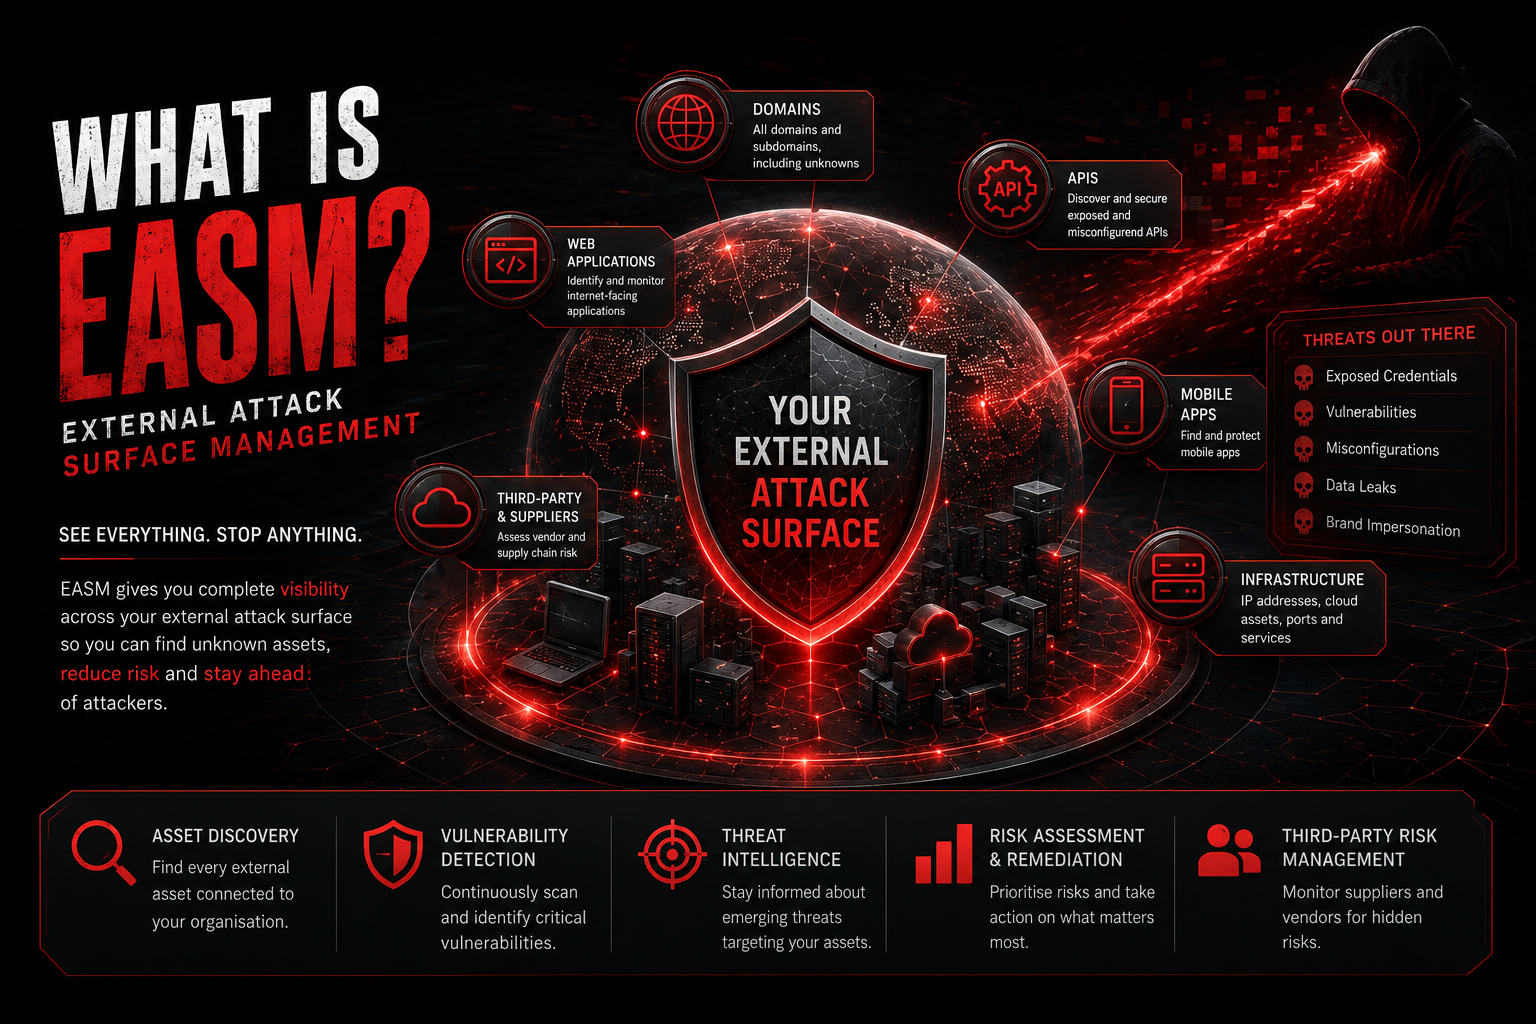
In the world of cybersecurity, External Attack Surface Management (EASM) is a proactive strategy to monitor and manage digital vulnerabilities. Learn why it’s essential for protecting modern enterprises.
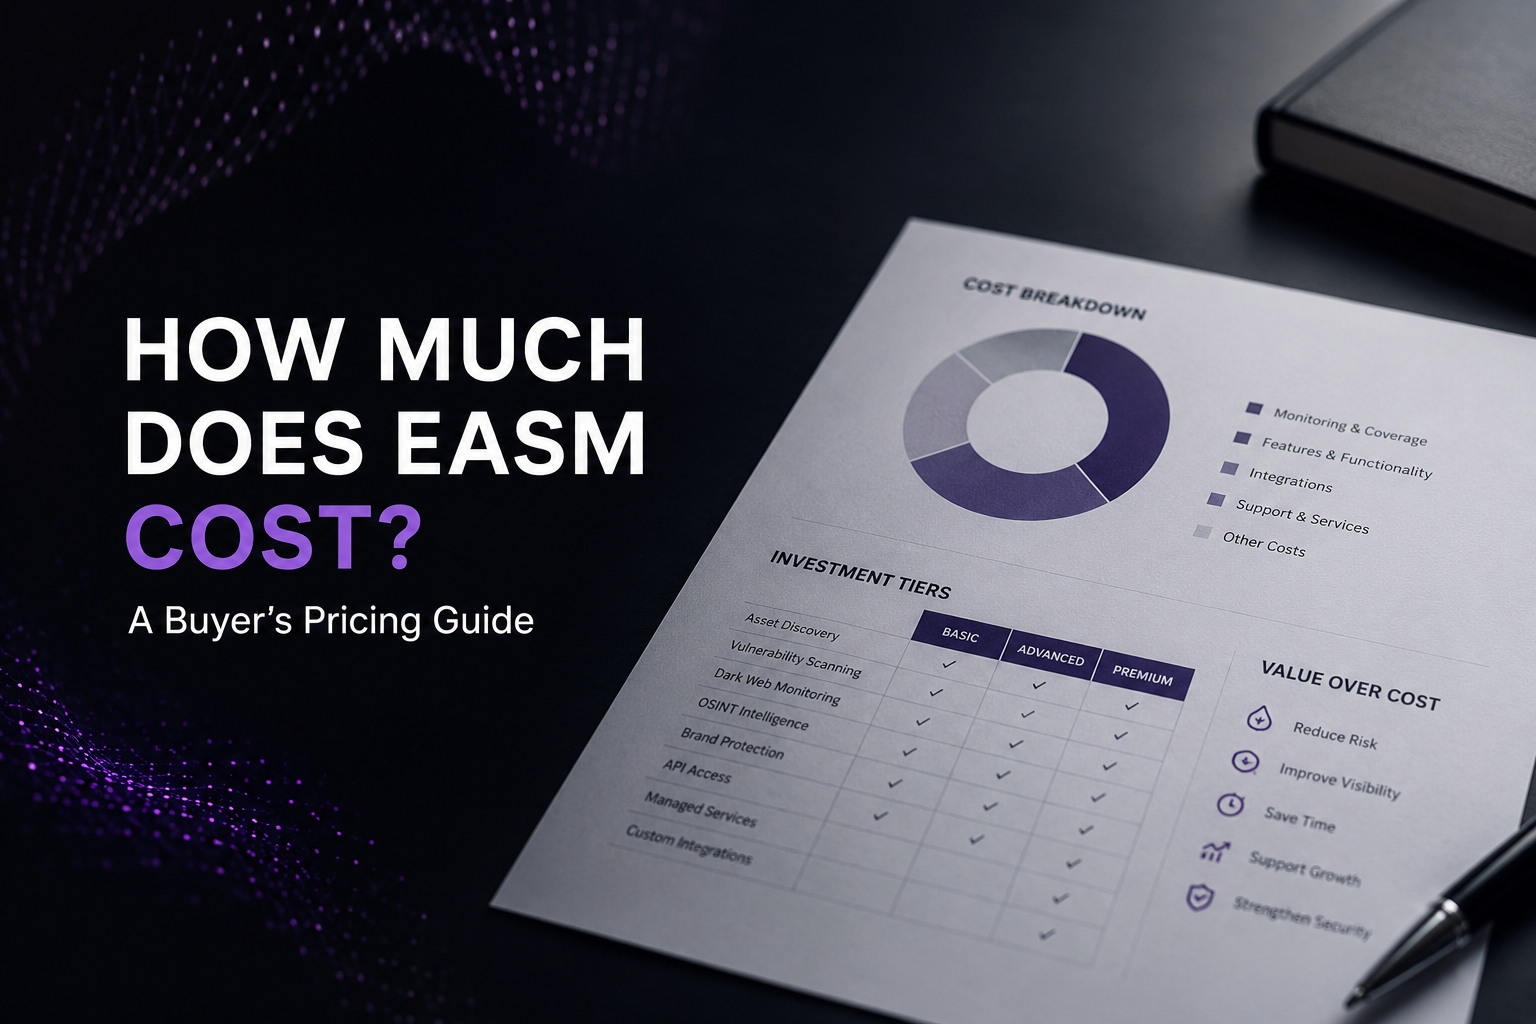
Learn about the factors affecting the cost of External Attack Surface Management (EASM) and how to choose a value-driven solution.
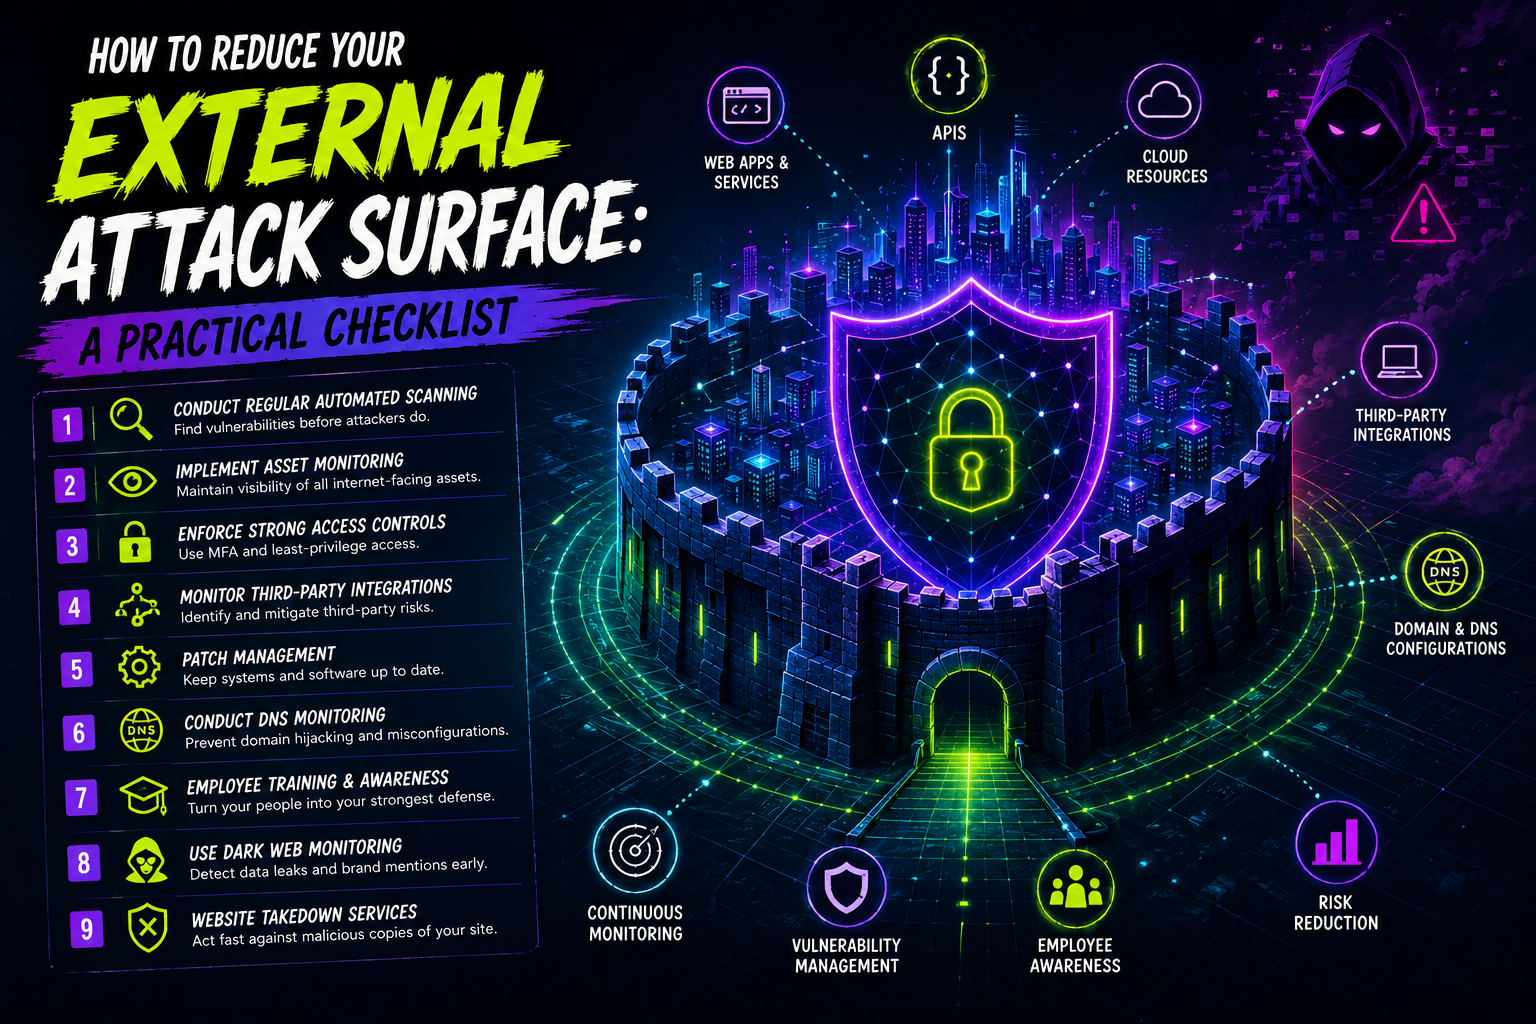
Learn practical steps to reduce your external attack surface and enhance cybersecurity.
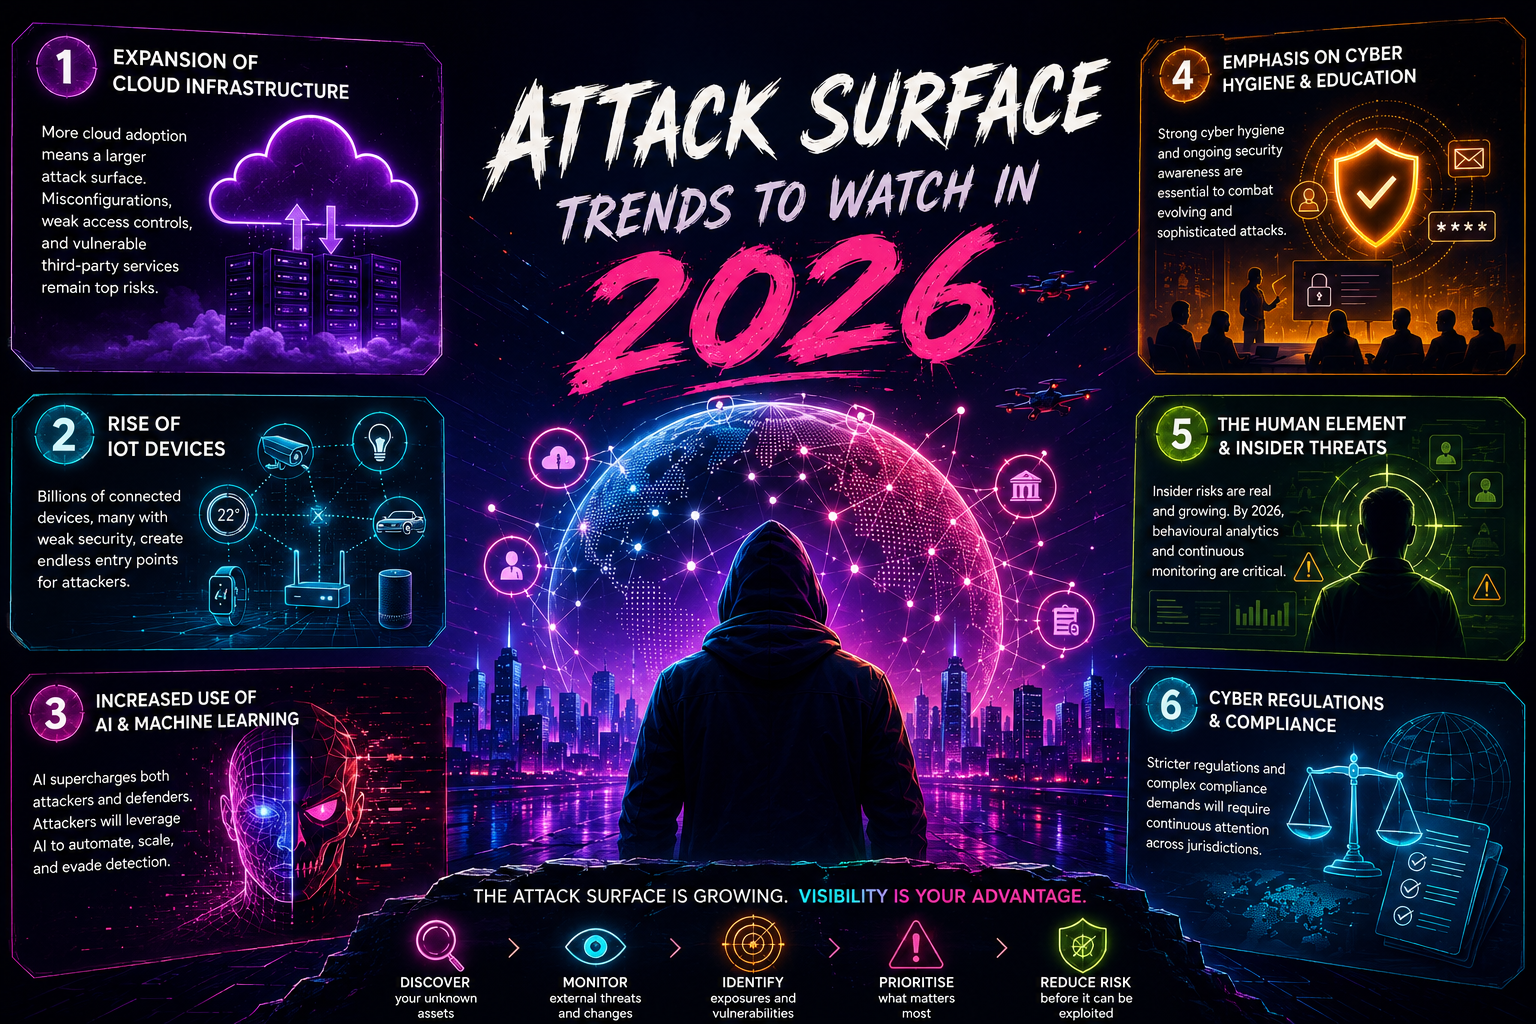
Exploring the cyber attack surface trends of 2026 and how businesses can mitigate potential threats.
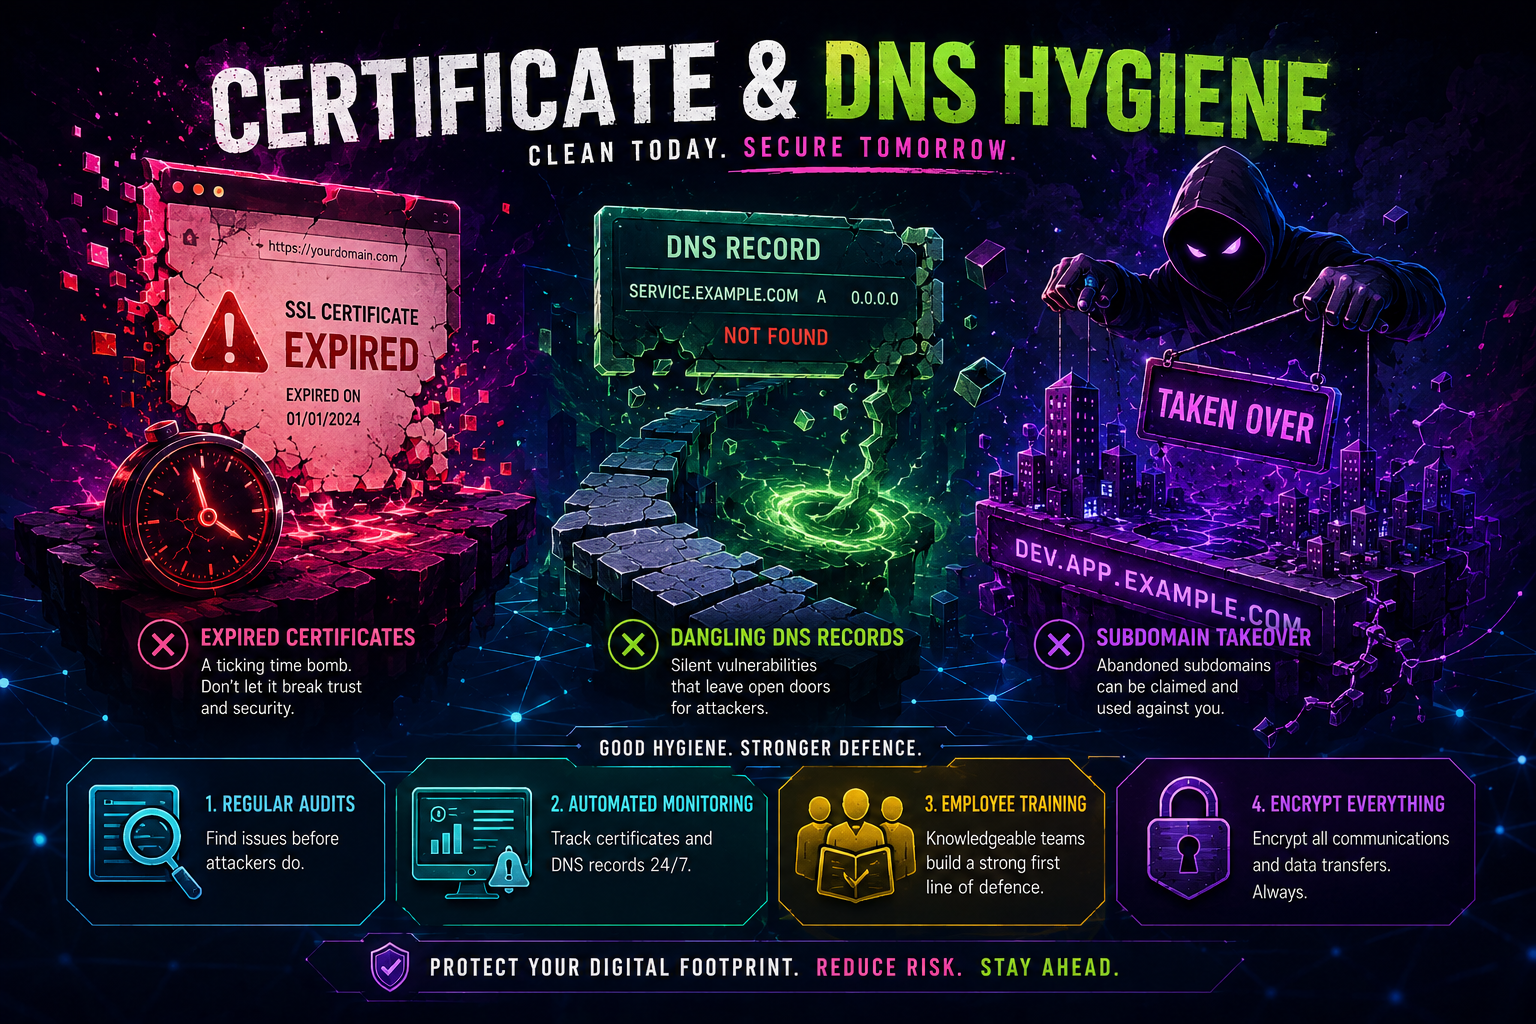
This blog emphasises the importance of maintaining certificate and DNS hygiene to prevent cyber threats such as dangling records, expired certificates, and subdomain takeover.
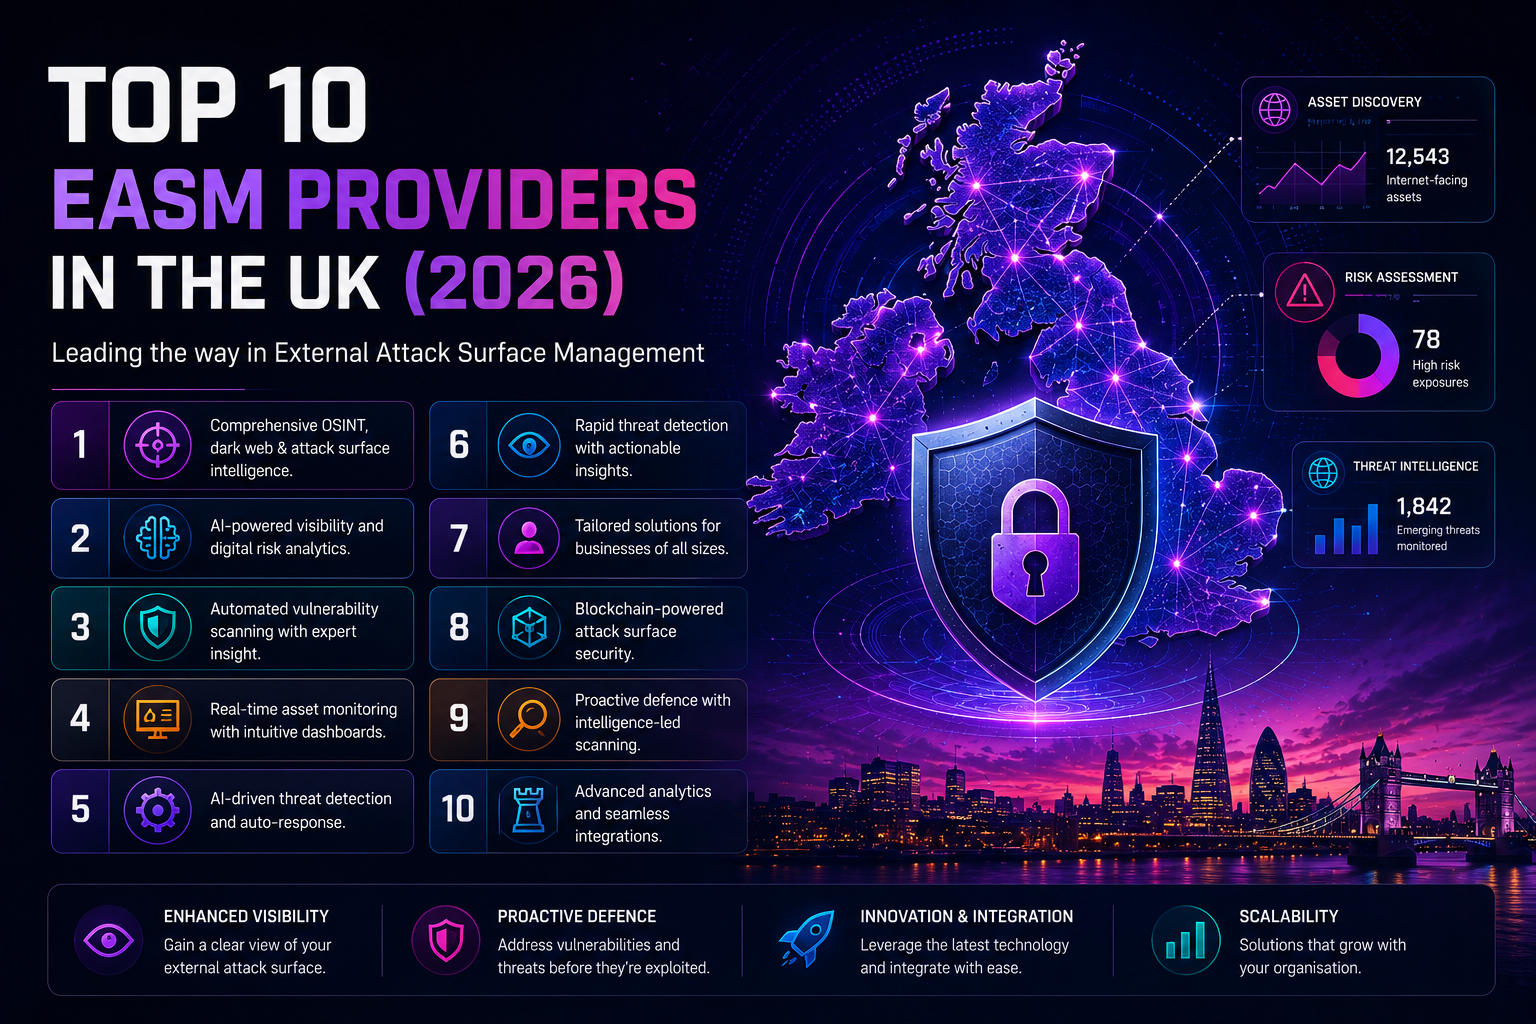
Ten real EASM providers UK organisations can buy in 2026, including our own platform, with what each does, its UK presence and how to choose.
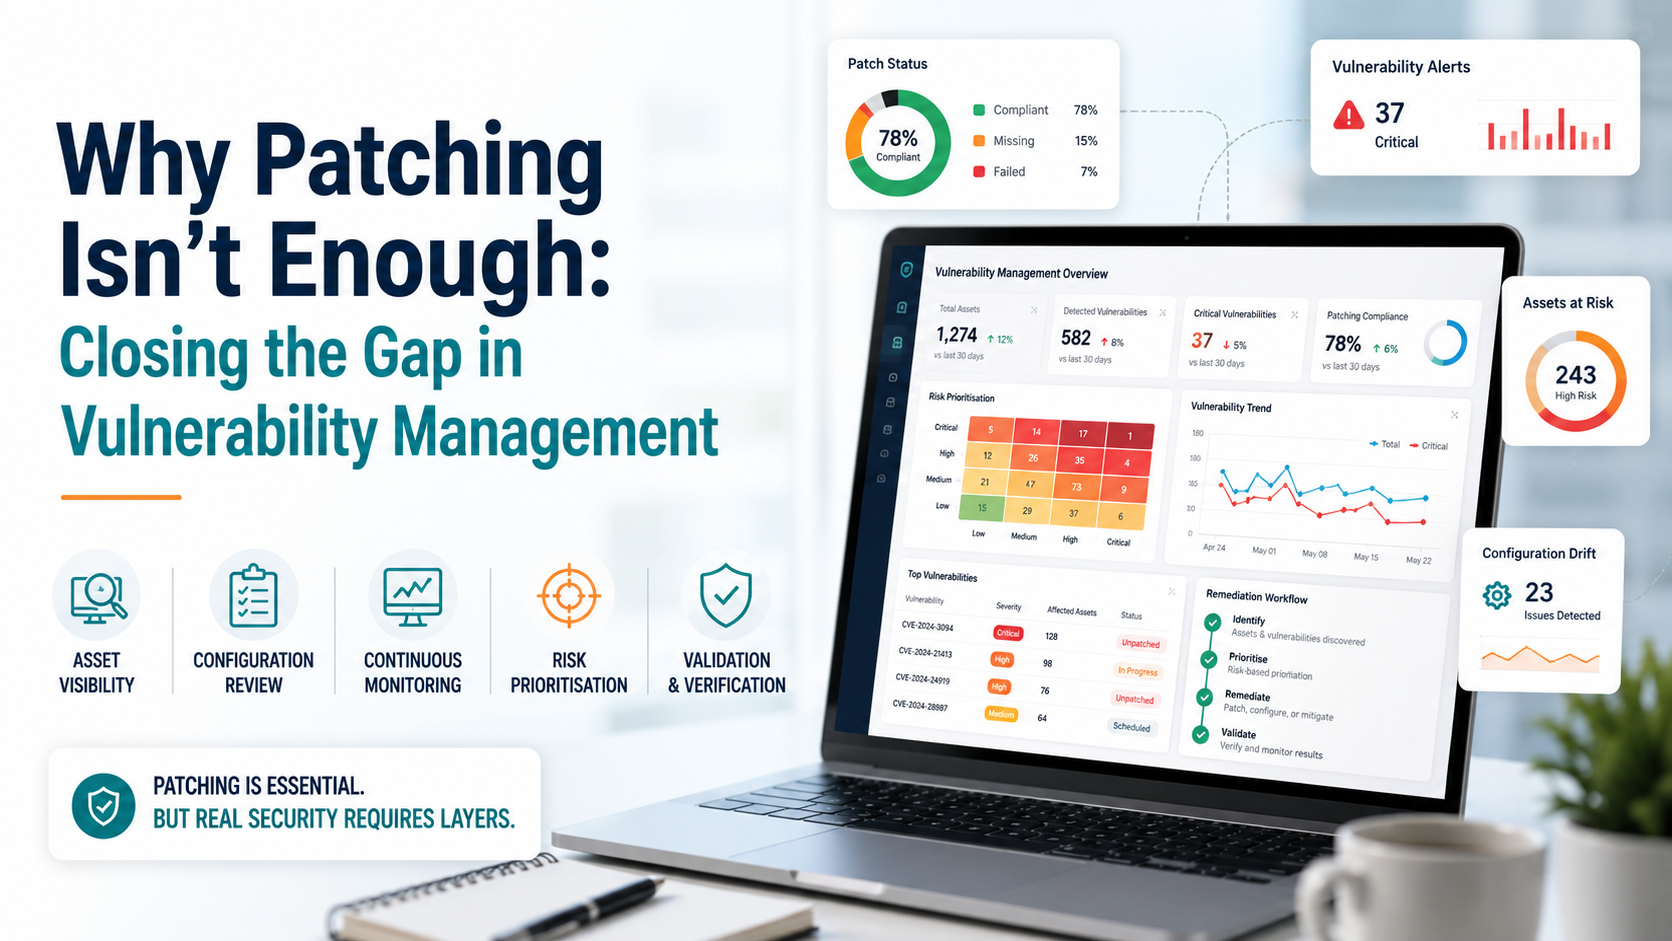
This article discusses the limitations of patching in vulnerability management and explores comprehensive strategies for improving security posture, such as continuous monitoring and threat intelligence.
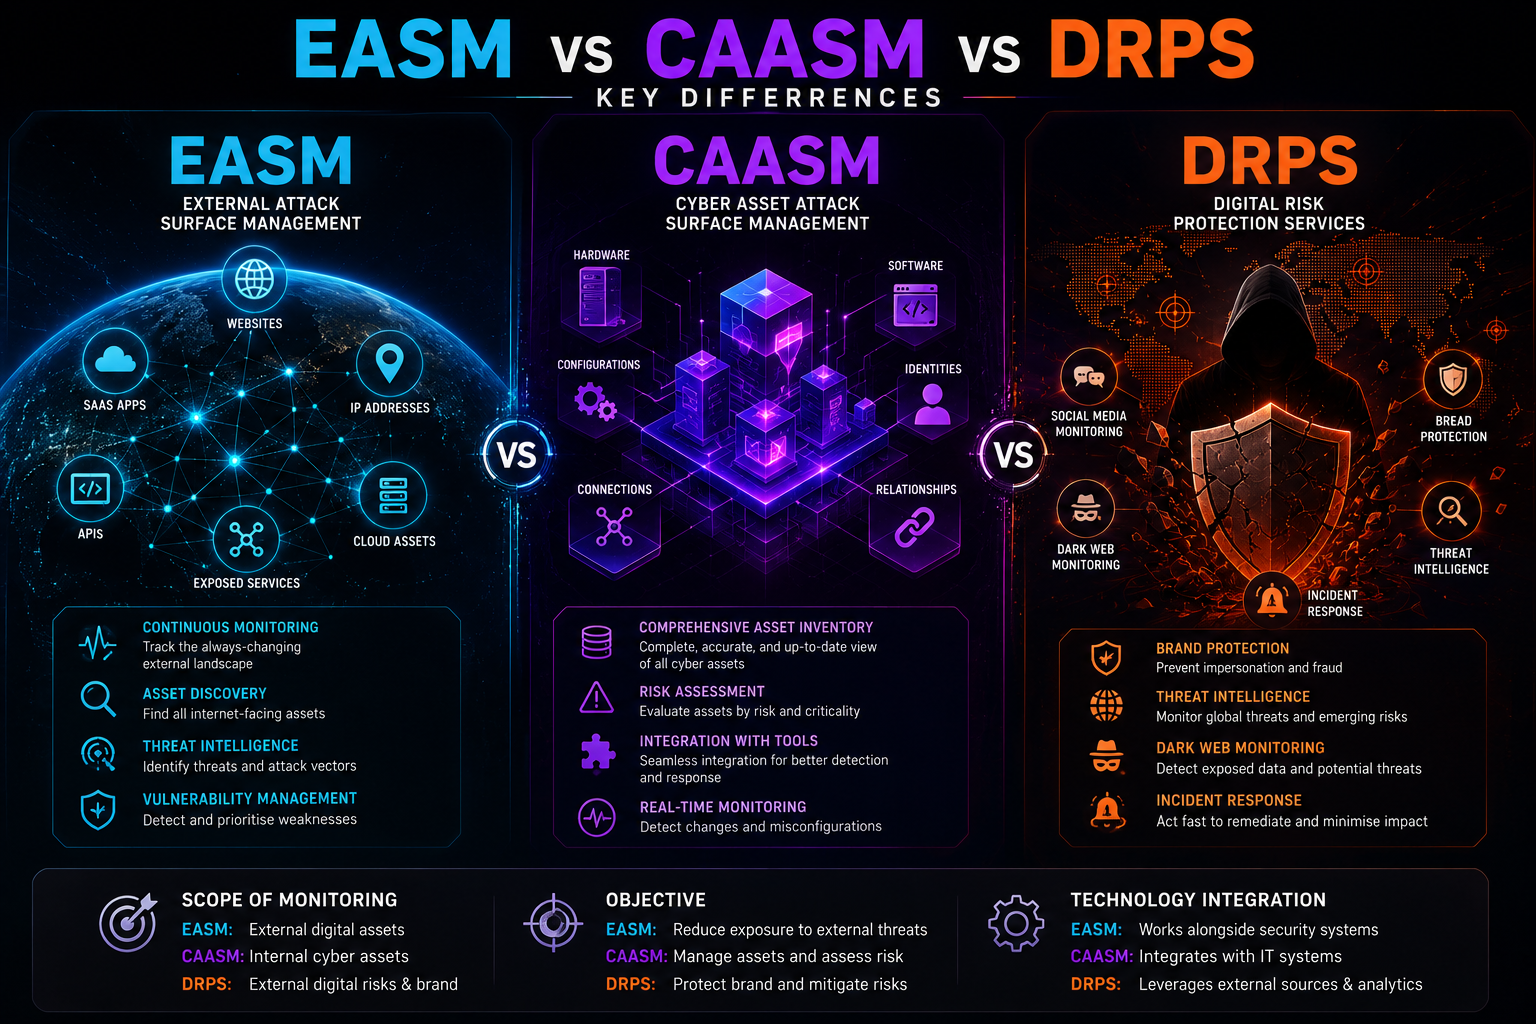
Explore the key differences between EASM, CAASM, and DRPS in cybersecurity to make informed decisions for your organisation’s security strategy.
Explore the StrikeShark campaign, a sophisticated cyber threat targeting businesses. Learn how to protect exposure with advanced cybersecurity strategies.
CVE-2025-67038 is a critical command injection vulnerability affecting the Lantronix EDS5000 series. Learn about the risks and mitigation strategies.
A guide for AppSec leaders to mitigate risks from CVE-2026-12569 in high-stakes sectors like finance, healthcare, and energy.
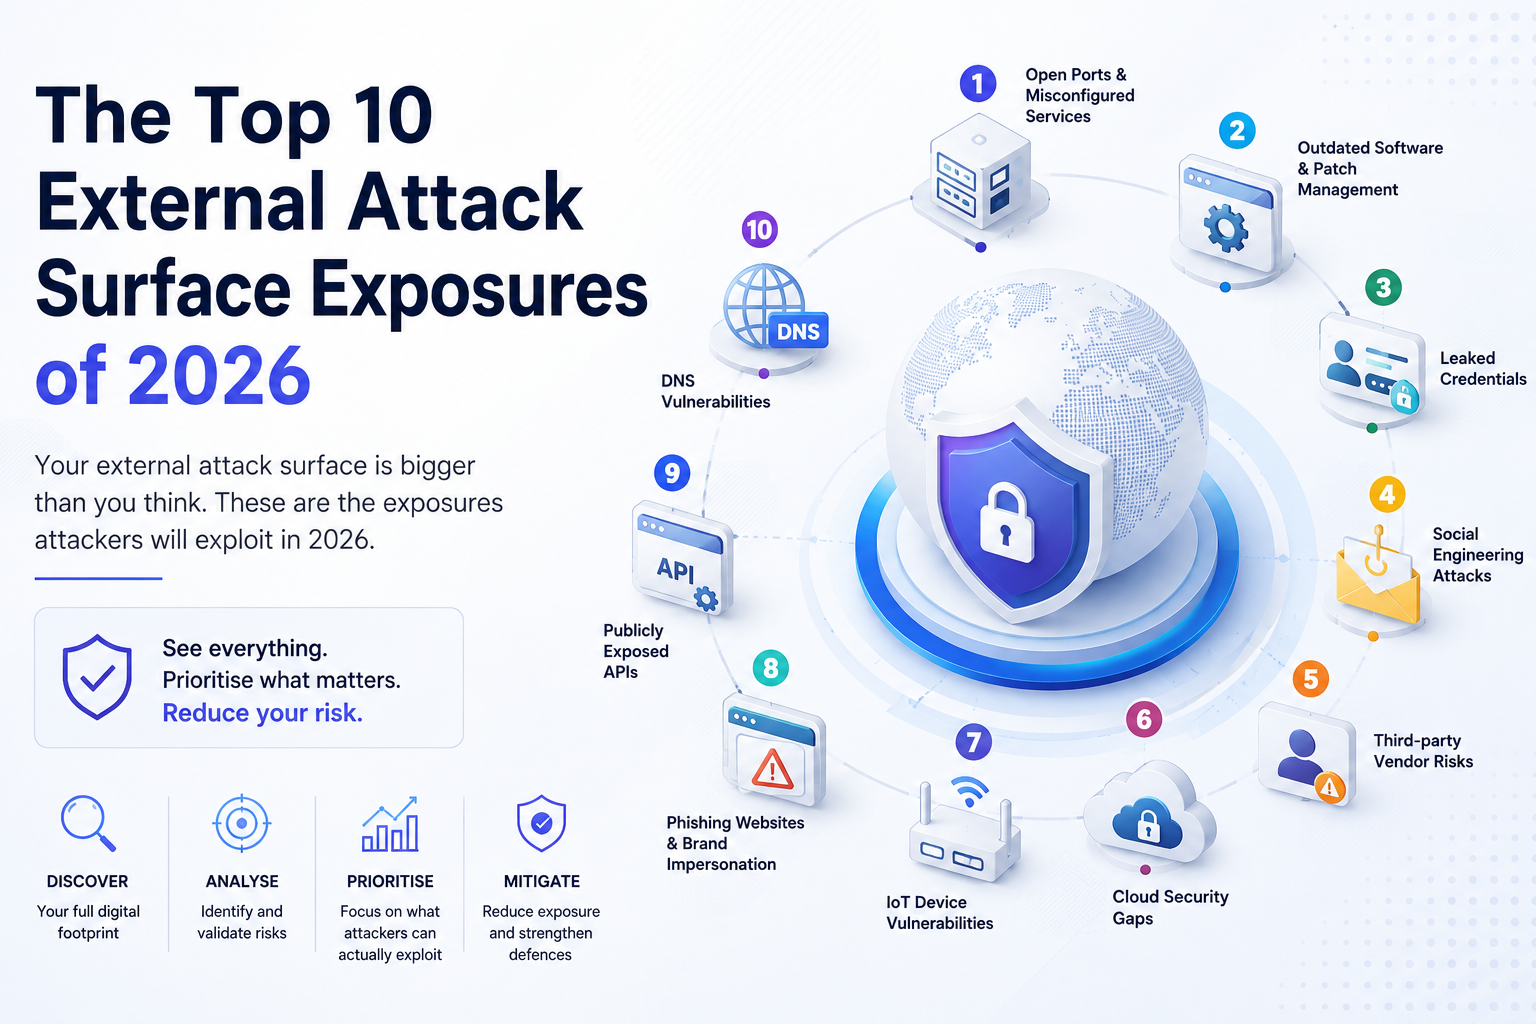
Explore the top 10 external attack surface exposures in 2026 and how to mitigate these cybersecurity risks.
Explore Adversarial Exposure Validation (AEV) and its role in Continuous Threat Exposure Management (CTEM) for prioritizing real exploitability over mere visibility in cybersecurity.
Explore the critical Joomla JCE CVE-2026-48907 vulnerability, its impacts, and protective measures for organisations.
Explore the FortiBleed mass Fortinet credential-harvesting campaign, its impact, and how to defend against such threats.
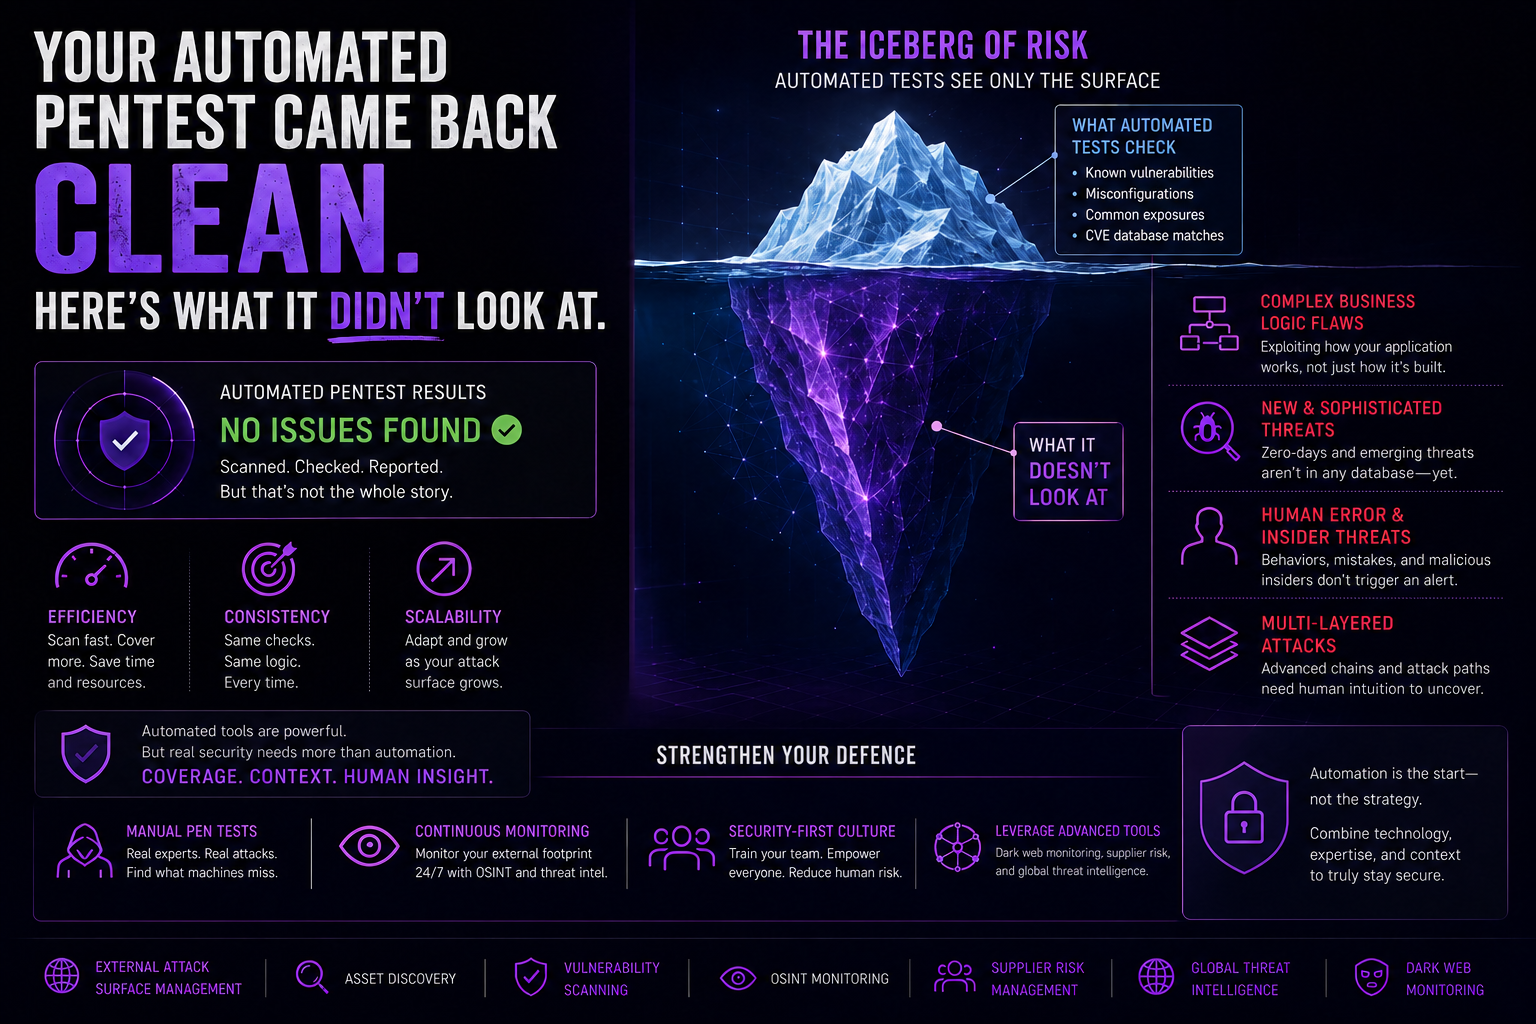
Explore the unseen gaps in automated pentesting and discover how continuous EASM can enhance your cybersecurity strategy.
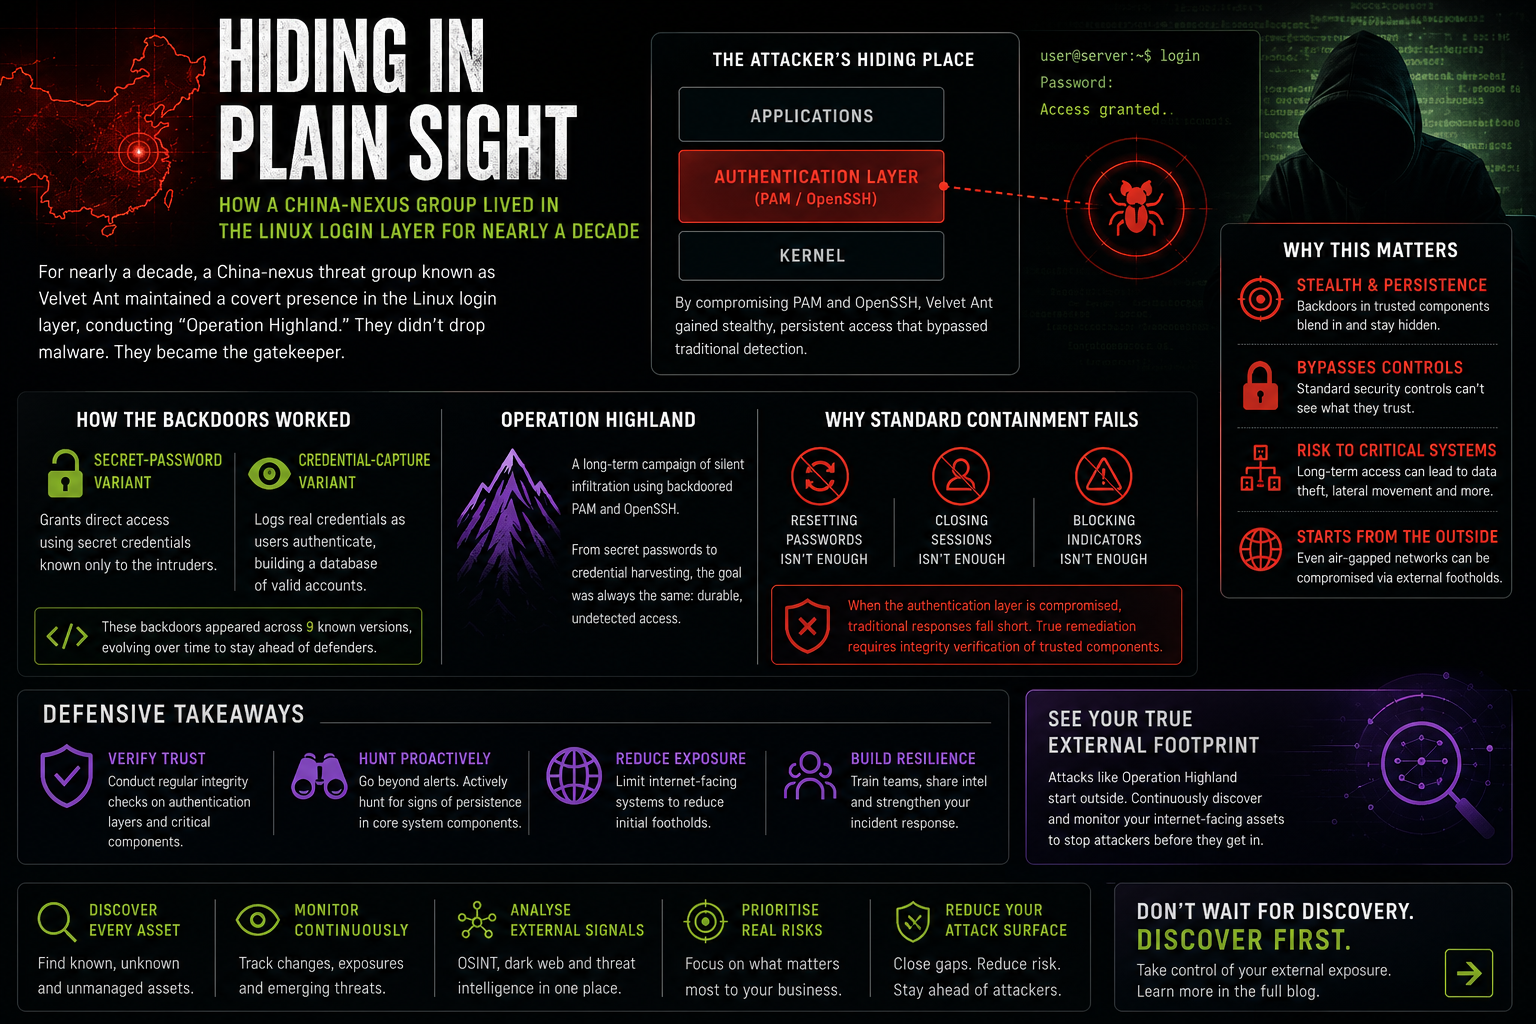
Discover how the China-nexus group Velvet Ant conducted a decade-long infiltration of Linux login systems in "Operation Highland," using backdoors in PAM and OpenSSH to maintain persistence.
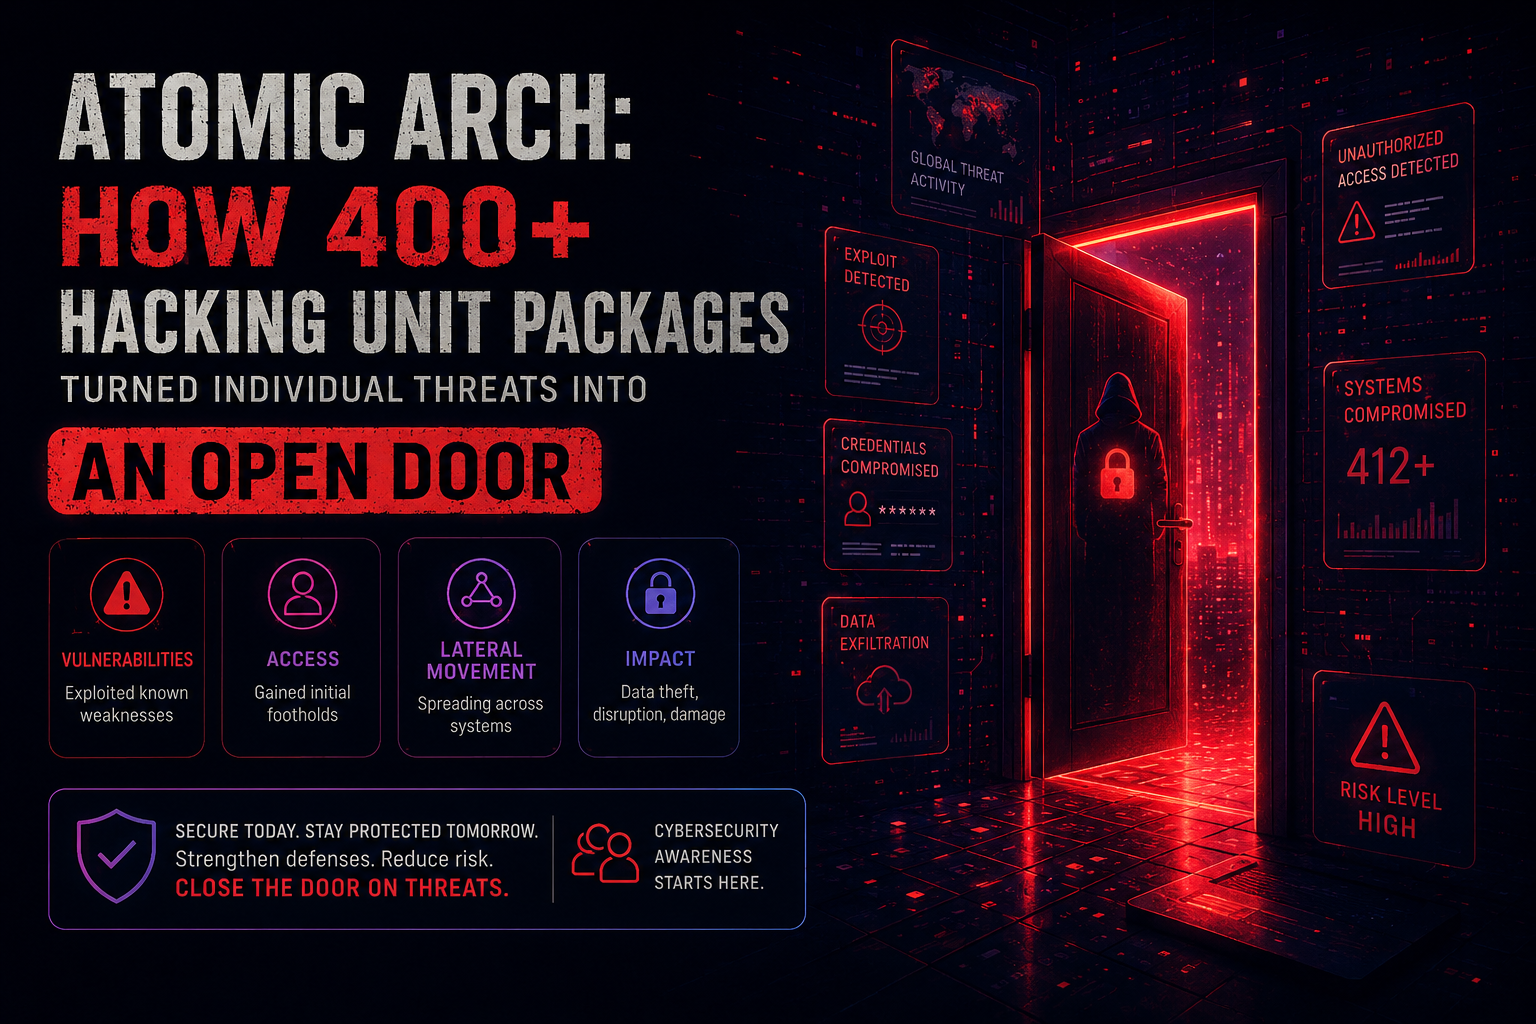
Explore how over 400 hijacked Linux packages turned developer machines into gateways to unauthorised access, and the crucial cybersecurity measures needed to safeguard the digital ecosystem.
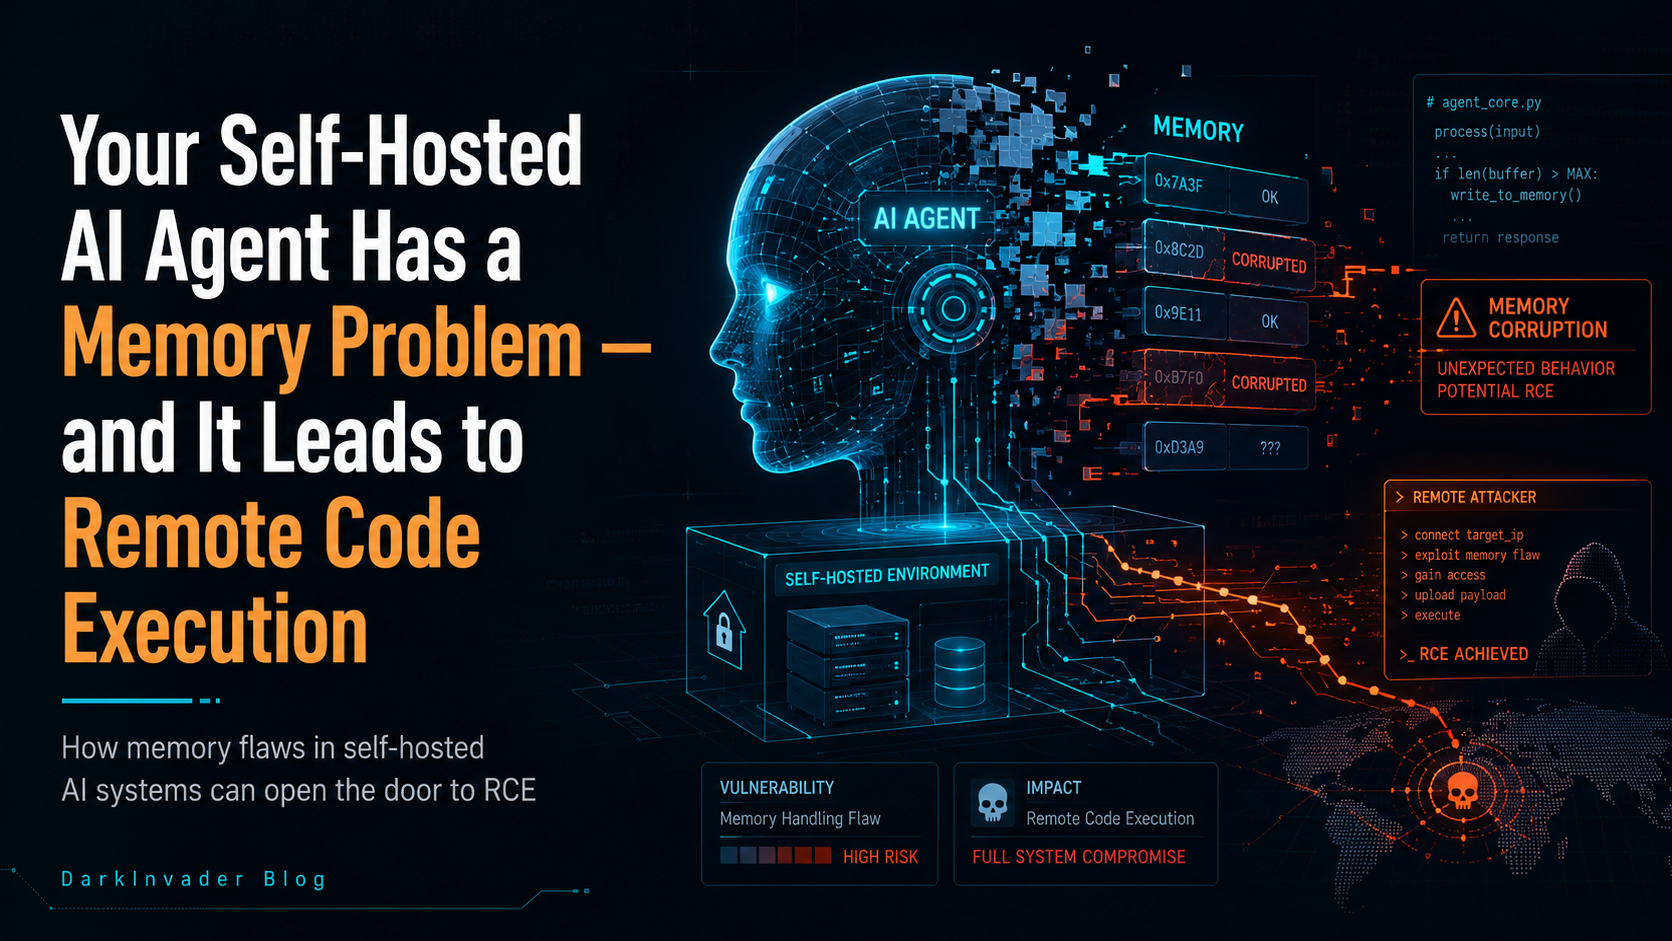
Explore how memory issues in self-hosted AI agents lead to vulnerabilities like remote code execution, and discover strategies to mitigate these risks.
Explore how the World Cup scam wave reveals vulnerabilities in domain protection, and learn effective EASM strategies for brand safety.