• tagged
Every post filed under this tag, newest first.
ServiceNow vulnerabilities are only half the problem. Learn how to inventory every exposed instance, test safely and respond in 72 hours.
PaperCut NG vulnerability response beyond patching: fingerprint exposed print servers, check for compromise and prove it’s closed.
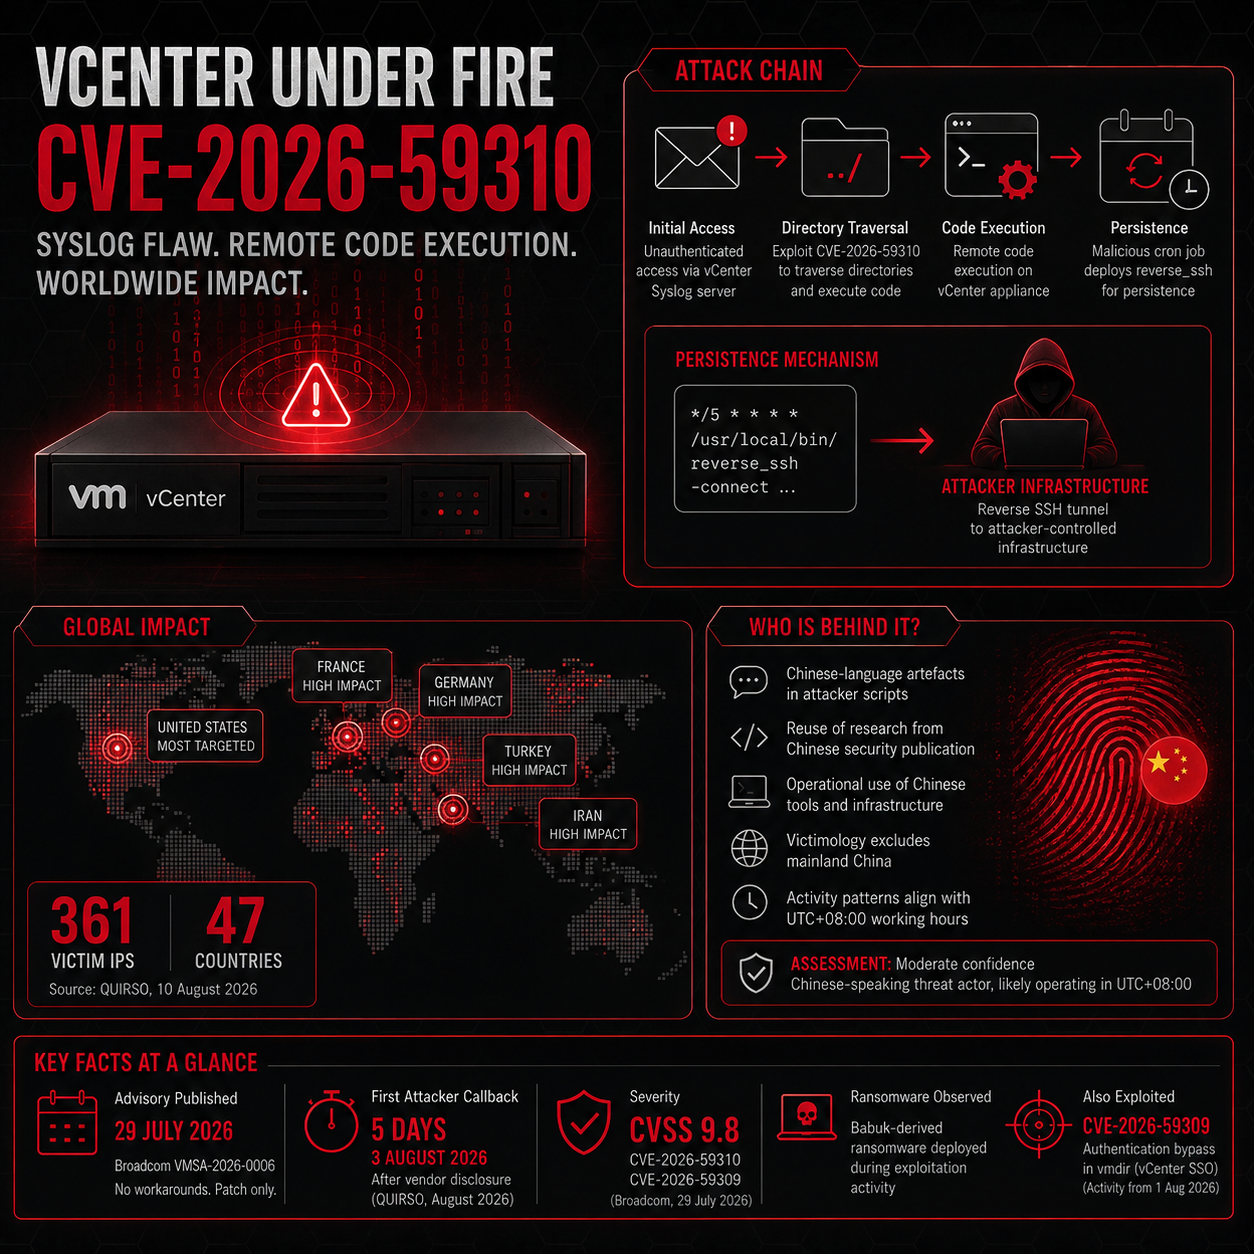
The vCenter Syslog Flaw is being used to backdoor virtual estates. Learn how it works, its impact on vSphere environments and how to defend against it.
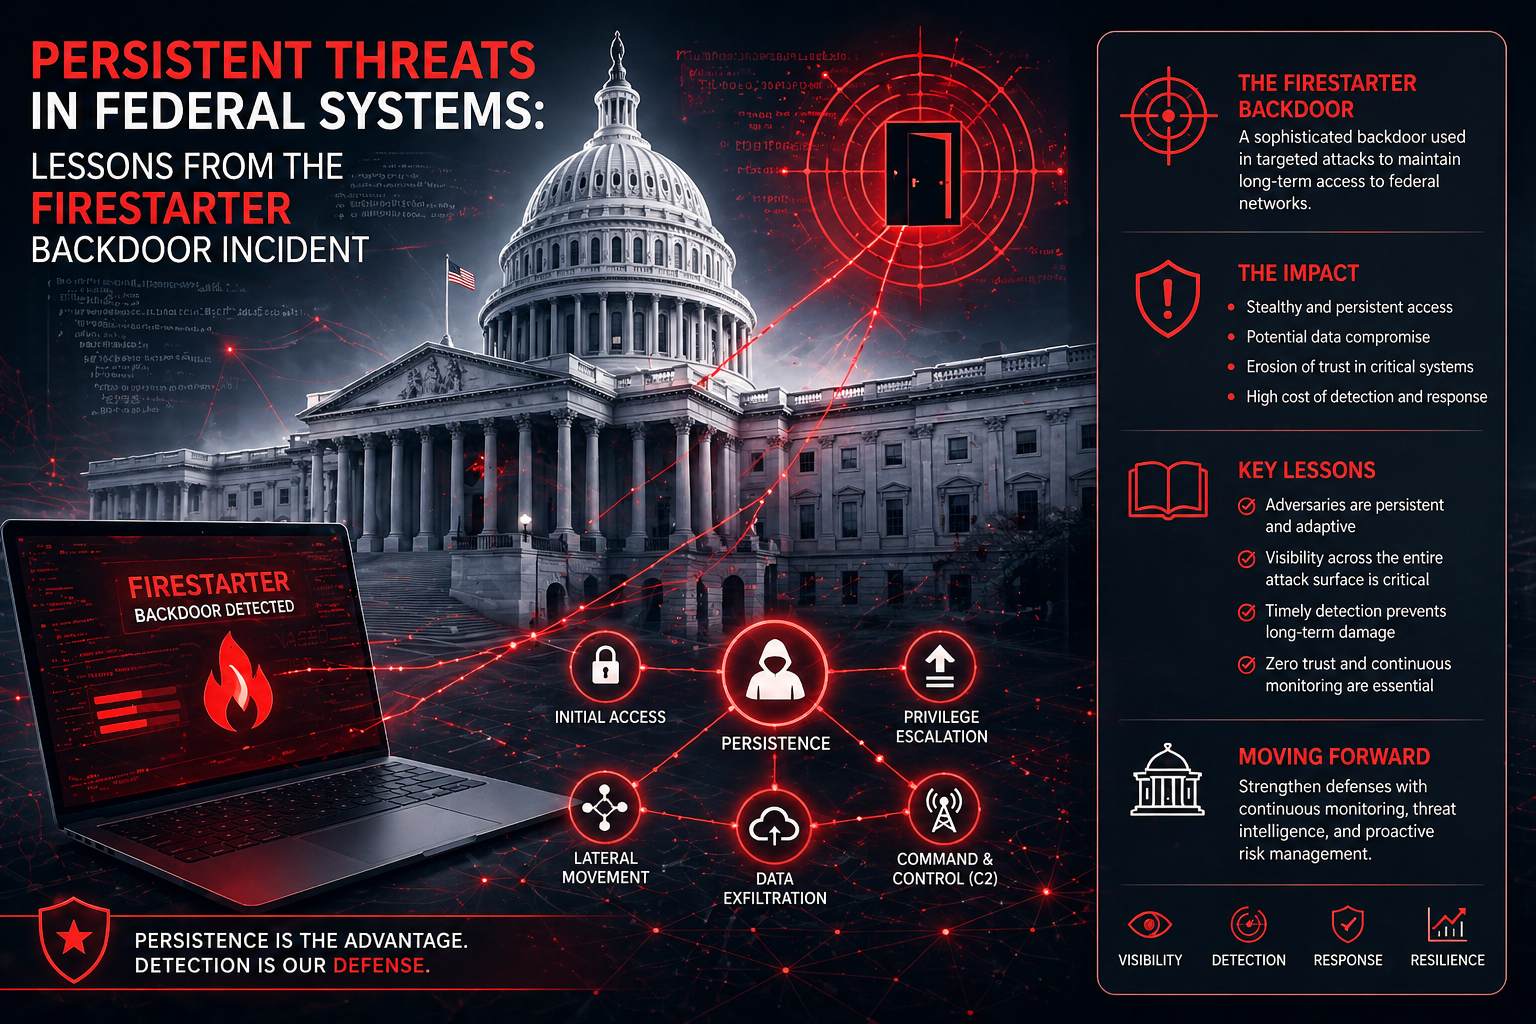
Lessons from the FIRESTARTER backdoor incident in federal systems, with the key strategies organisations can use to strengthen cyber resilience.
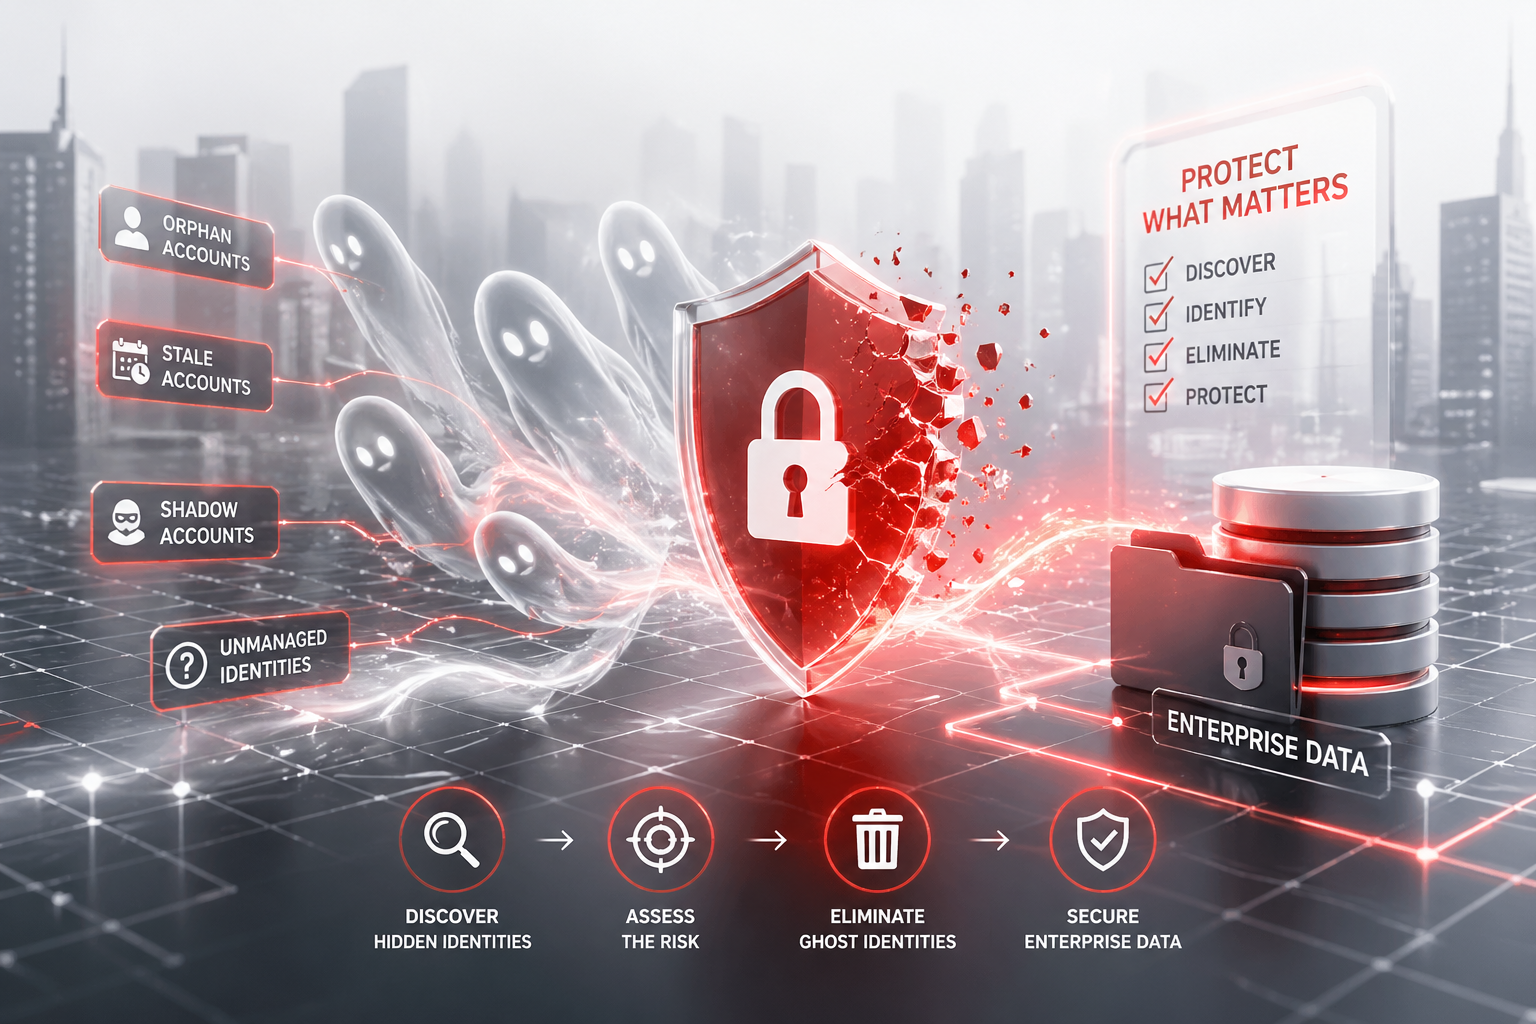
Ghost identities are dormant or obsolete accounts that put enterprise data at risk. Learn how to find and remove them with audits and access controls.
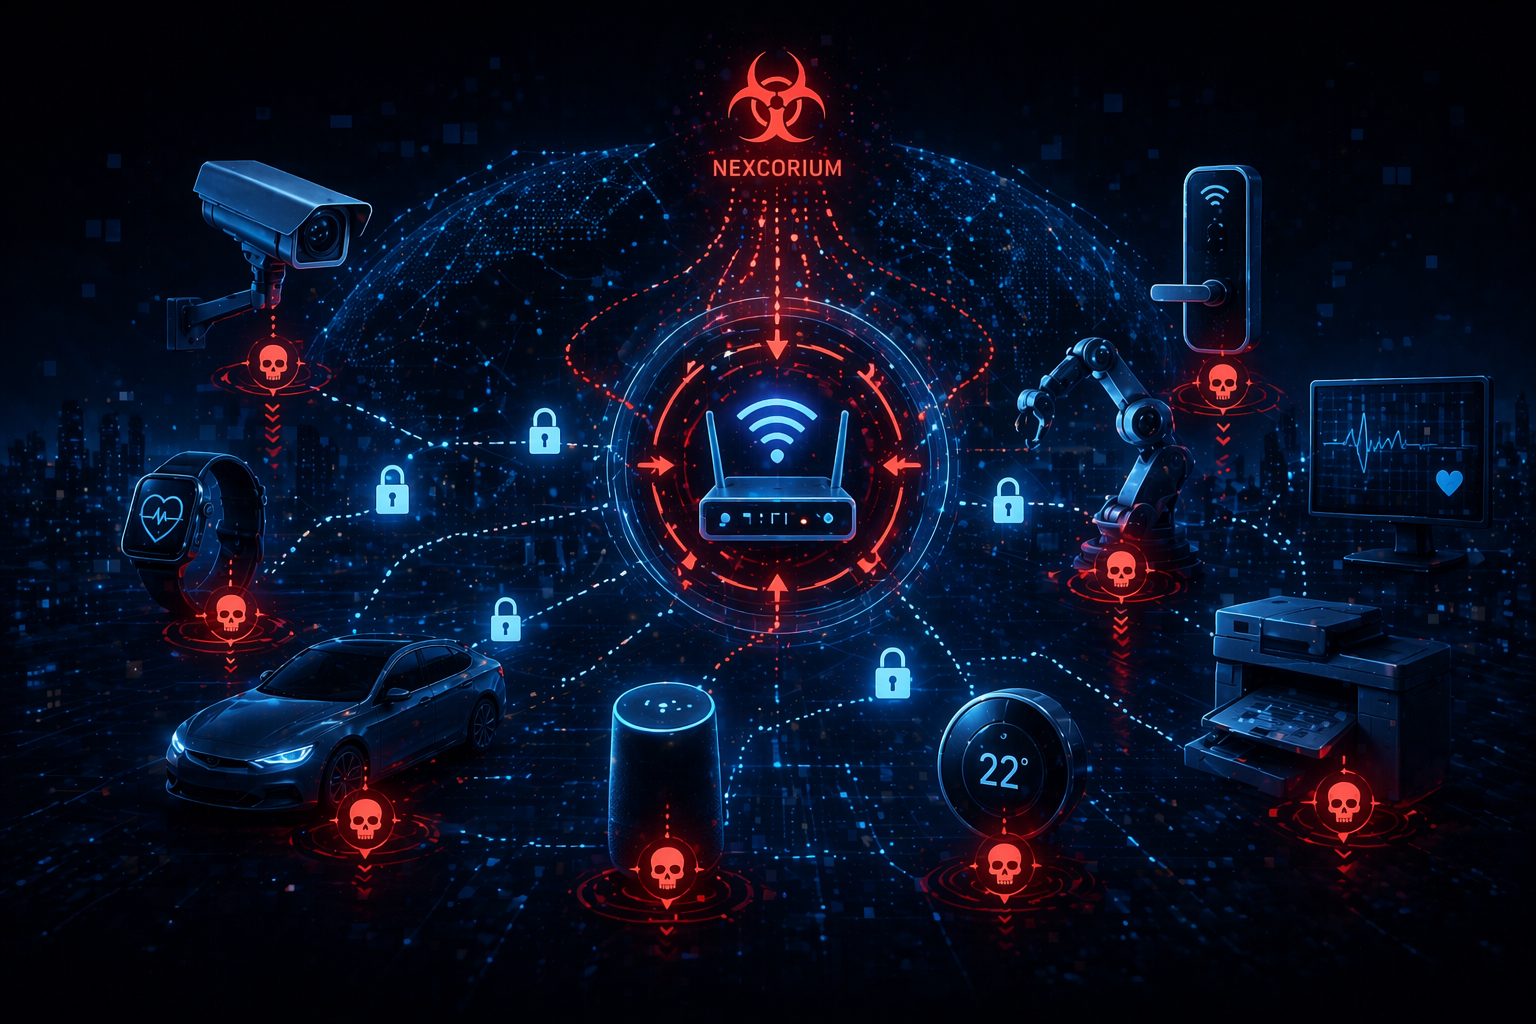
Exploring how Nexcorium targets IoT devices for attacks, their tactics, and strategies to mitigate these cyber threats.
How AI vulnerabilities expand your attack surface, and how External Attack Surface Management helps your organisation mitigate the risks.
Explore how External Attack Surface Management (EASM) safeguards AI systems against vulnerabilities, ensuring robust cyber resilience.
React2Shell allows unauthenticated remote code execution in React and Next.js. Learn the risk to your attack surface and how EASM helps remediate it.
Security debt builds up like technical debt and gets harder to manage over time. Learn how EASM, visibility and security culture keep it in check.
Subdomain takeover, dangling DNS and orphaned IPs are low-effort, high-impact attacks. Learn why mapping and monitoring your footprint matters.
Threat intelligence is often too noisy to use. Learn how DarkInvader's upcoming Global Threat Intelligence modules curate data so teams can prioritise.
EASM will not replace the testing a PSN ITHC needs, but it gives clear external risk visibility, simplifies pre-check clean-up and helps year-round.
Supply chain attacks are rising as hackers use OSINT to target weak suppliers. Learn how stronger third-party risk management closes the gap.
SOC 2 is about ongoing security and risk management. Learn how EASM finds external exposures early and keeps you ready for audits year-round.
How EASM supports DORA compliance for financial institutions, from ICT risk management to third-party oversight and incident reporting.
EASM supports ISO 27001 compliance with real-time visibility, risk assessment and vulnerability management, making audits and accreditation simpler.
Cyber intelligence gives IT teams actionable insight, yet adoption is slow. Explore its impact and the barriers of cost, integration, skills and privacy.
EASM and penetration testing work best together: continuous monitoring of exposed assets plus the depth of manual testing for proactive security.
This blog highlights the top 5 tips in Continuous Threat Exposure Management and how it works, talking through the stages and benefits of this.
This post summarises what External Attack Surface Management is and the benefits as well as the challenges that come with it.
This blog outlines the new DORA requirements, specifically navigating third-party risks due to the new DORA compliance set for January 2025.
A cyberattack on NHS hospitals in London led to more than 200 operations being cancelled, including for cancer patients. Recovery may take months.
How threat actors choose their victims, the tactics they use to find and target them, and how to spot these methods and avoid becoming a target.
browse by tag
browse by category
browse by year
free trial
Try DarkInvader Pro free. No payment details required.