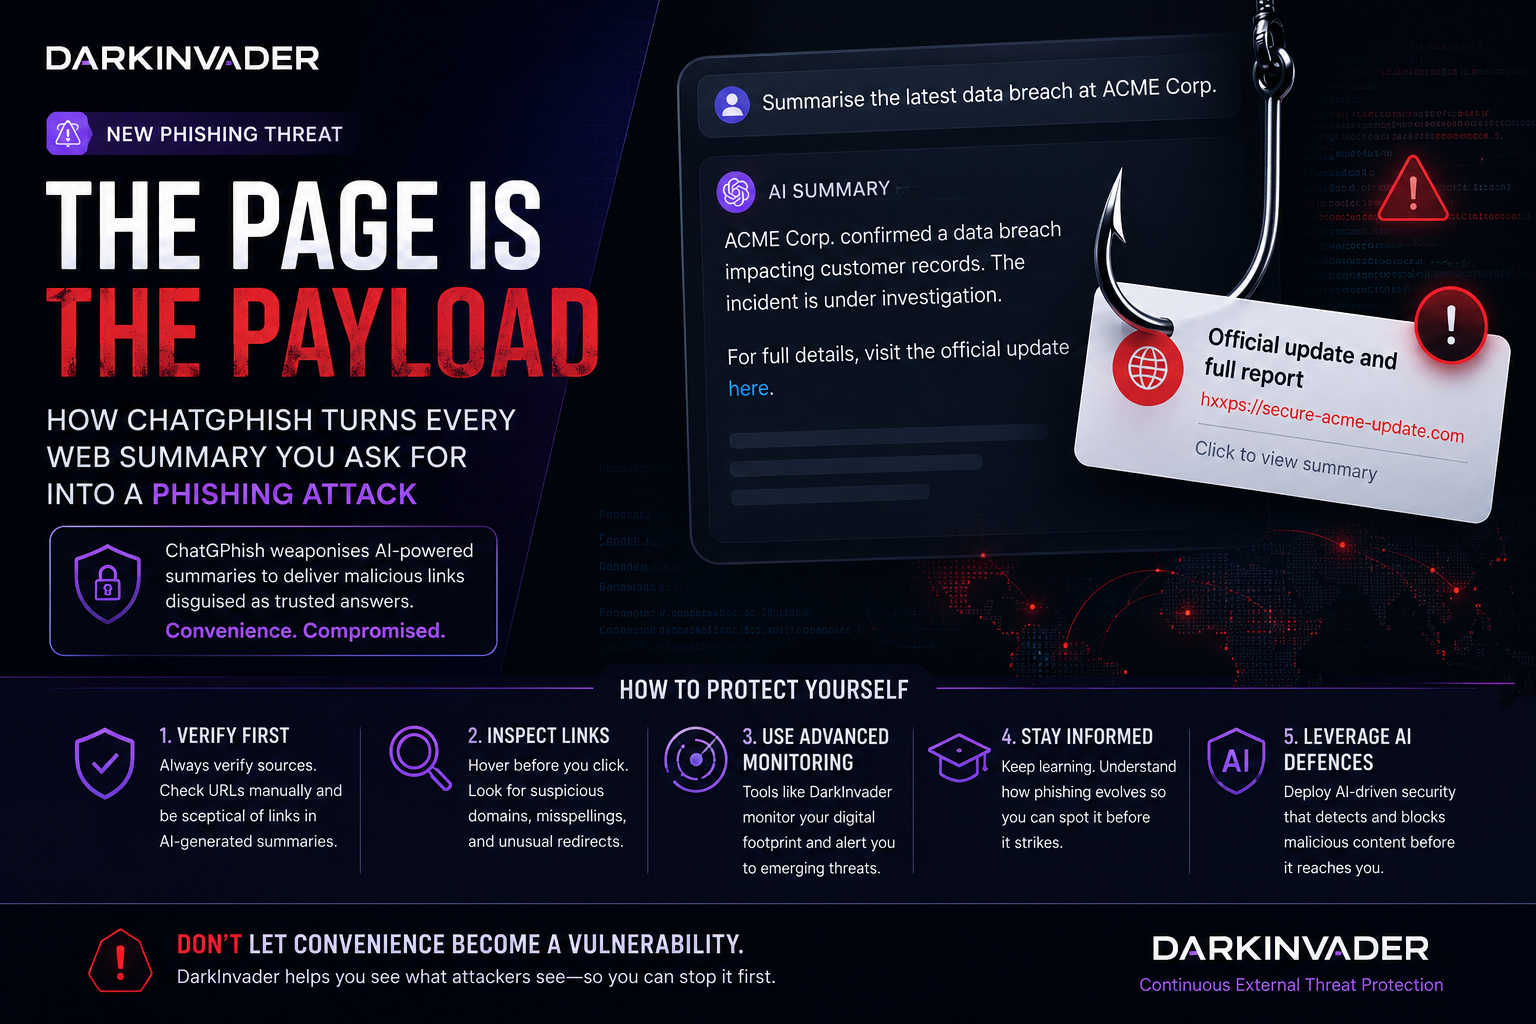
The Page Is the Payload: How ChatGPhish Turns Every Web Summary You Ask For Into a Phishing Attack
17 Million Routers, One Dutch Raid, and the Quiet Economy of Disguising Cybercrime as Your Neighbour's Wi-Fi
Forged Cookies on the Front Door: Why CVE-2026-0257 Is the Worst Possible Bug in Your VPN Right Now
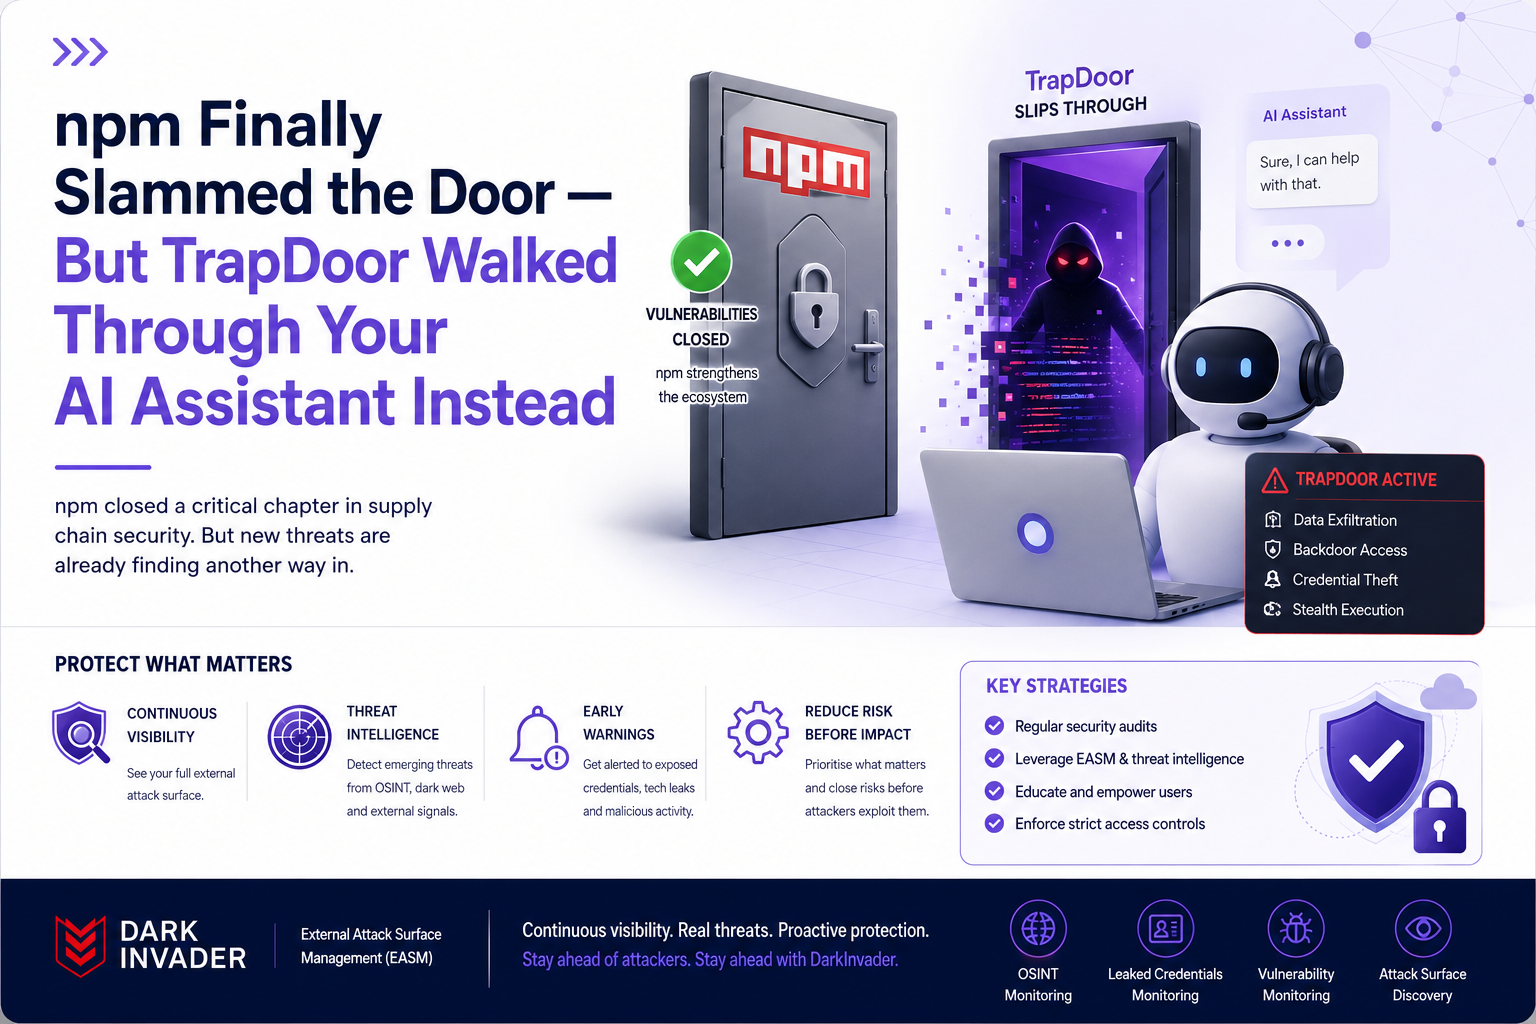
npm Finally Slammed the Door - But TrapDoor Walked Through Your AI Assistant Instead
48 Hours From Patch to Exploit: Why CVE-2026-9082 Is Hunting Your Drupal Sites Right Now
Hackers Used AI to Develop First Known Zero-Day 2FA Bypass for Mass Exploitation
Most Remediation Programs Never Confirm the Fix Actually Worked
What 45 Days of Watching Your Own Tools Will Tell You About Your Real Attack Surface
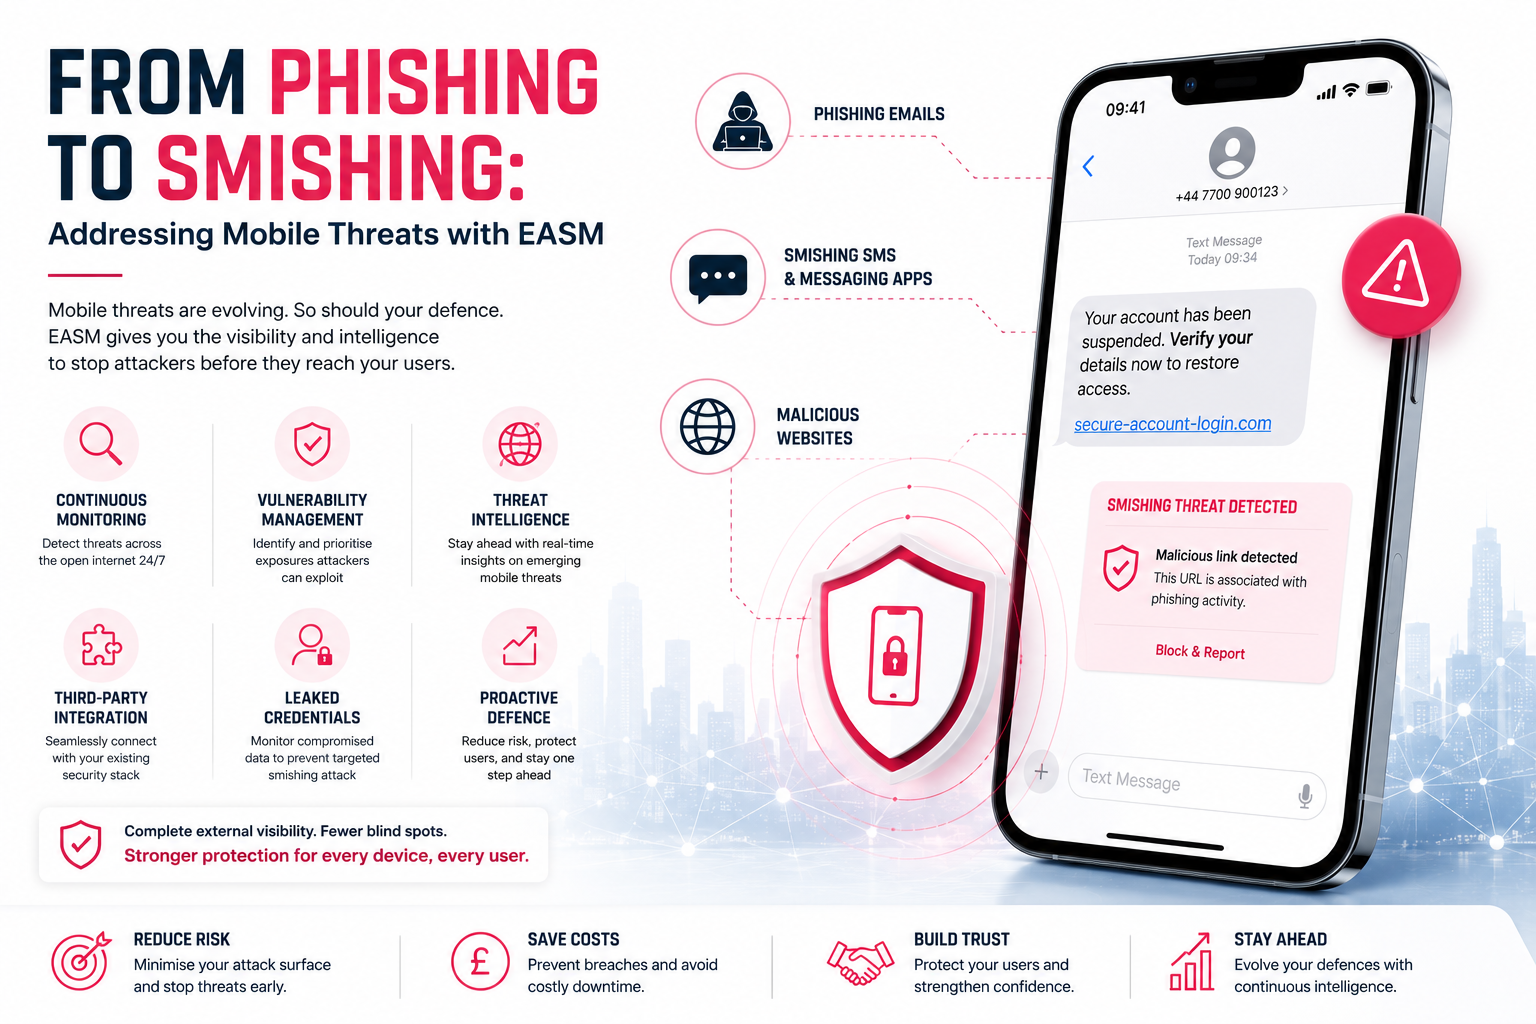
From Phishing to Smishing: Addressing Mobile Threats with EASM
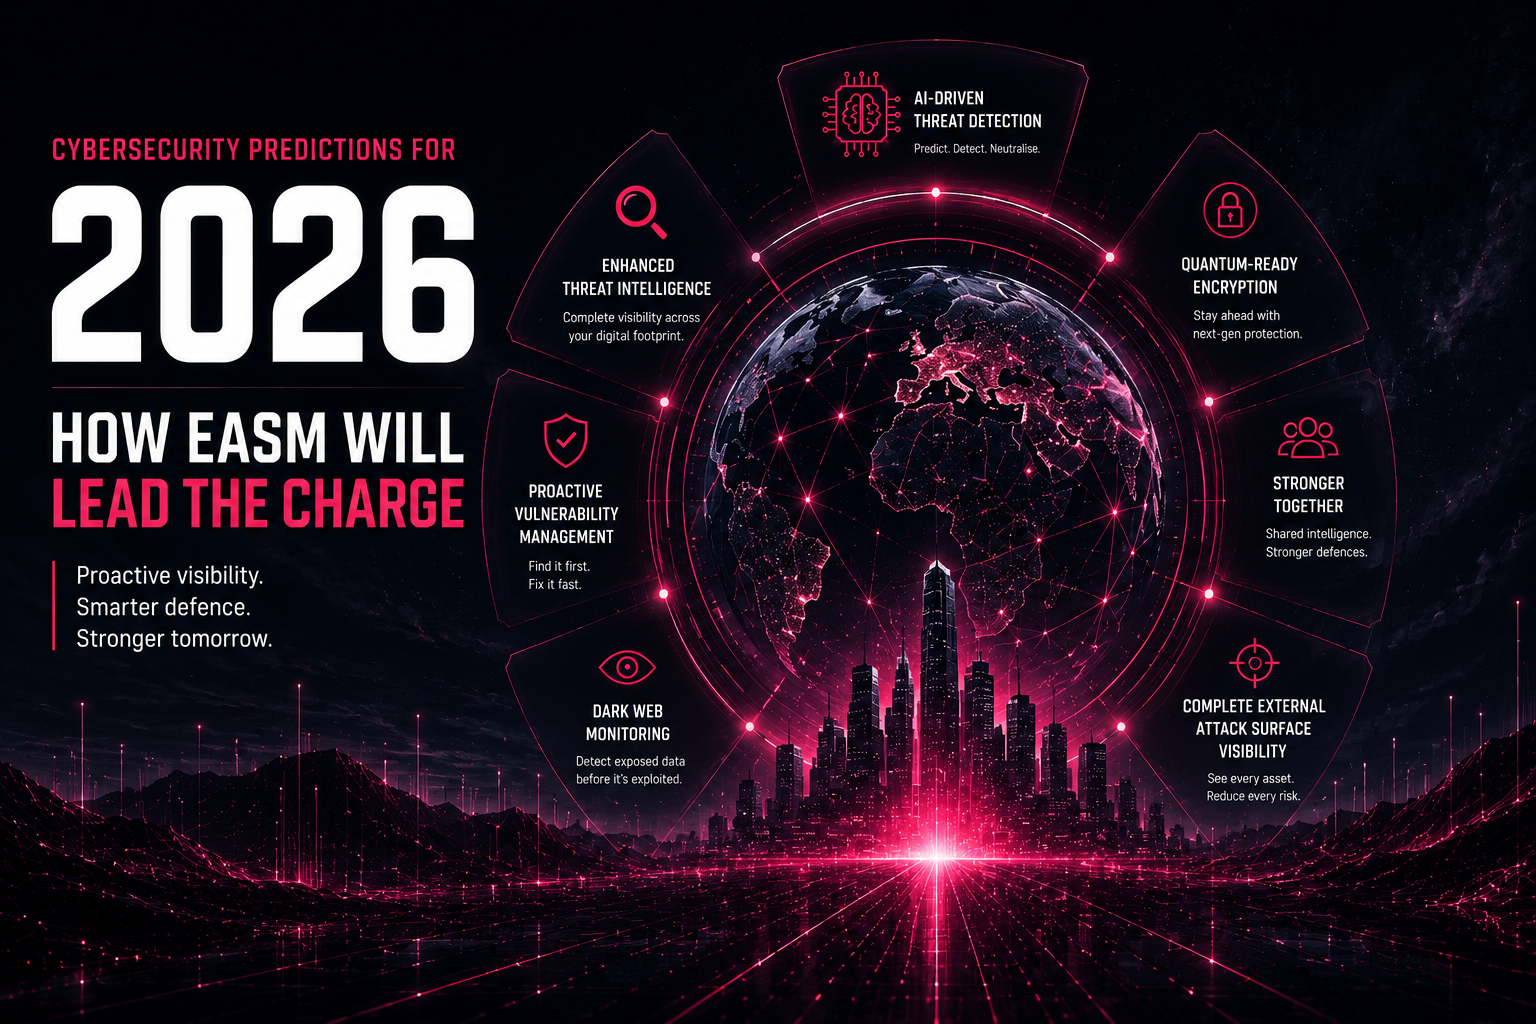
Cybersecurity Predictions for 2026: How EASM Will Lead the Charge
Navigating Complex Geopolitical Threats: Defence Strategies Against China-Linked Cyber Networks
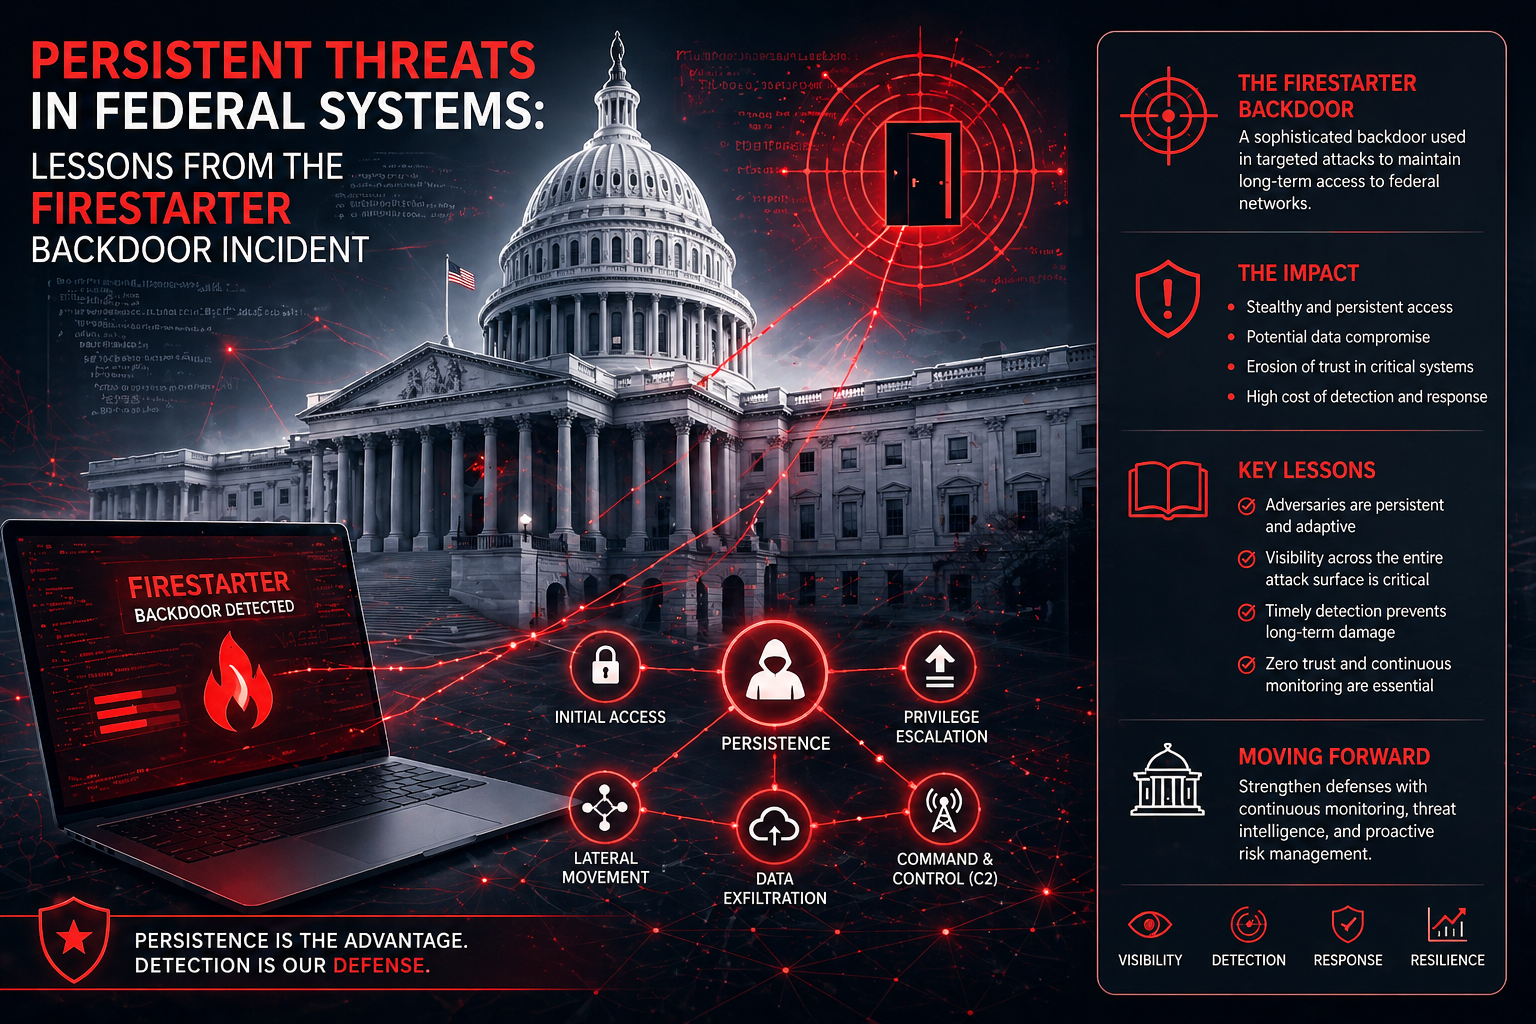
Persistent Threats in Federal Systems: Lessons from the FIRESTARTER Backdoor Incident
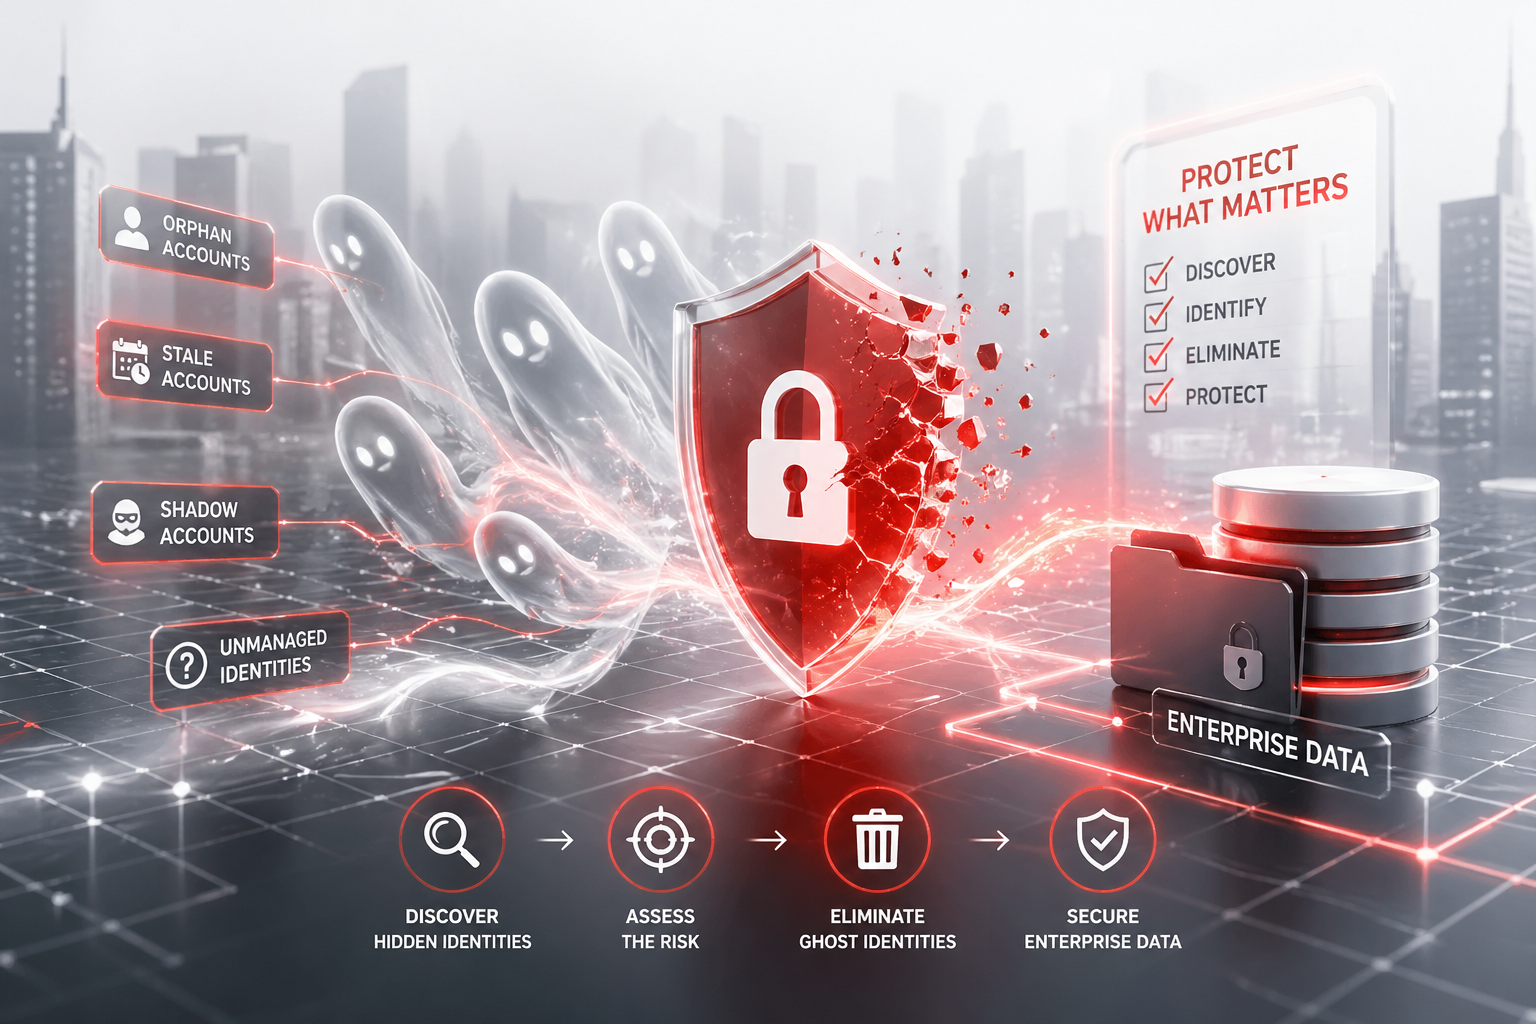
Eliminate Ghost Identities Before They Expose Your Enterprise Data
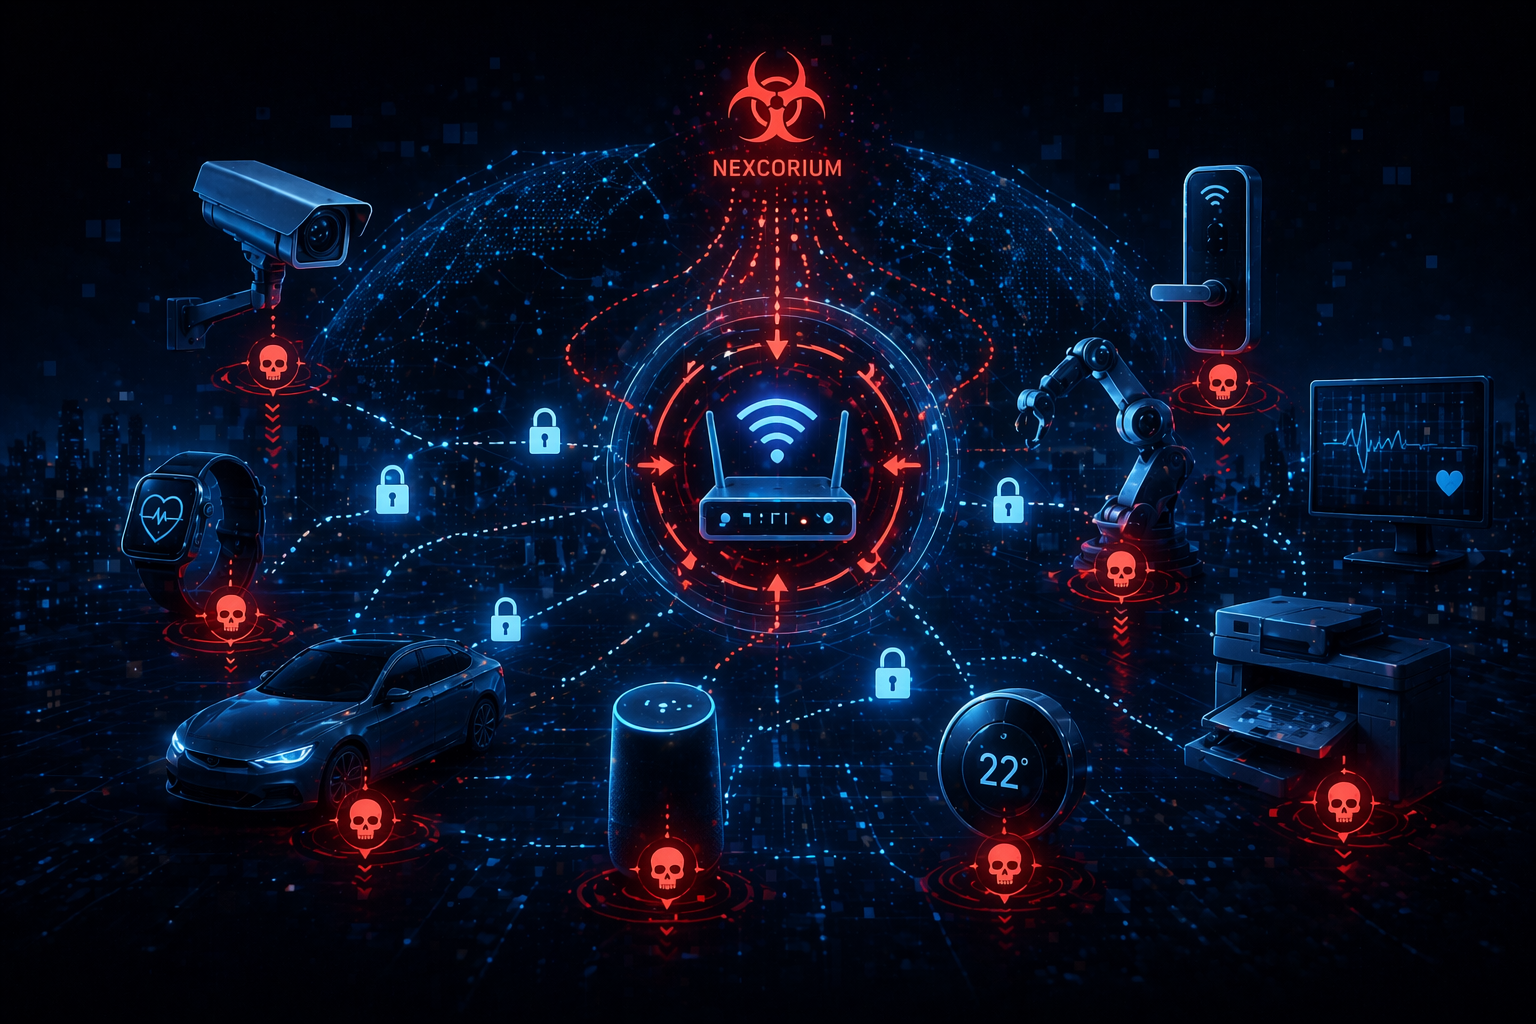
How Nexcorium Targets IoT Devices for Cyber Attacks
Expanding Your Attack Surface Visibility: New Features and Future Innovations
Real-Time Threat Intelligence: The Impact of AI and EASM on Modern Security Practices
Unveiling Hidden Threats: How EASM Enhances Security Posture in 2026
The Role of EASM in Protecting Against the Latest Phishing Techniques
Securing the Conversation: The Imperative of Telegram Monitoring in EASM
Mitigating Supply Chain Threats with Effective Supplier Risk Management