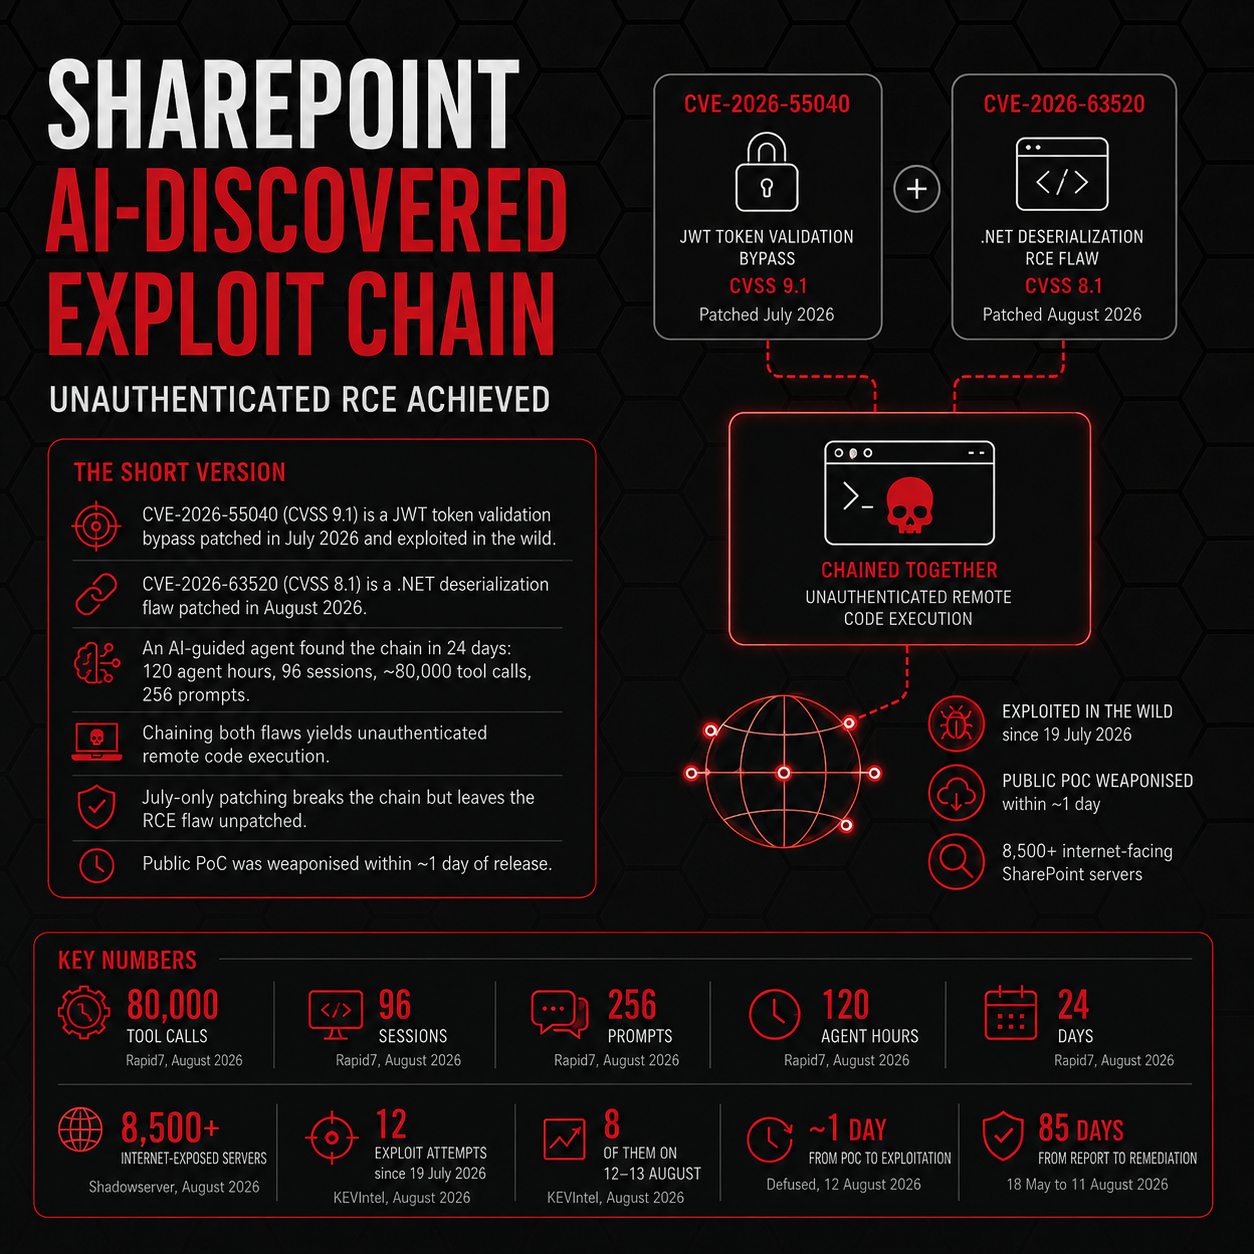
What an Agent-Discovered SharePoint Chain Tells Us About the Next Decade of Exploitation
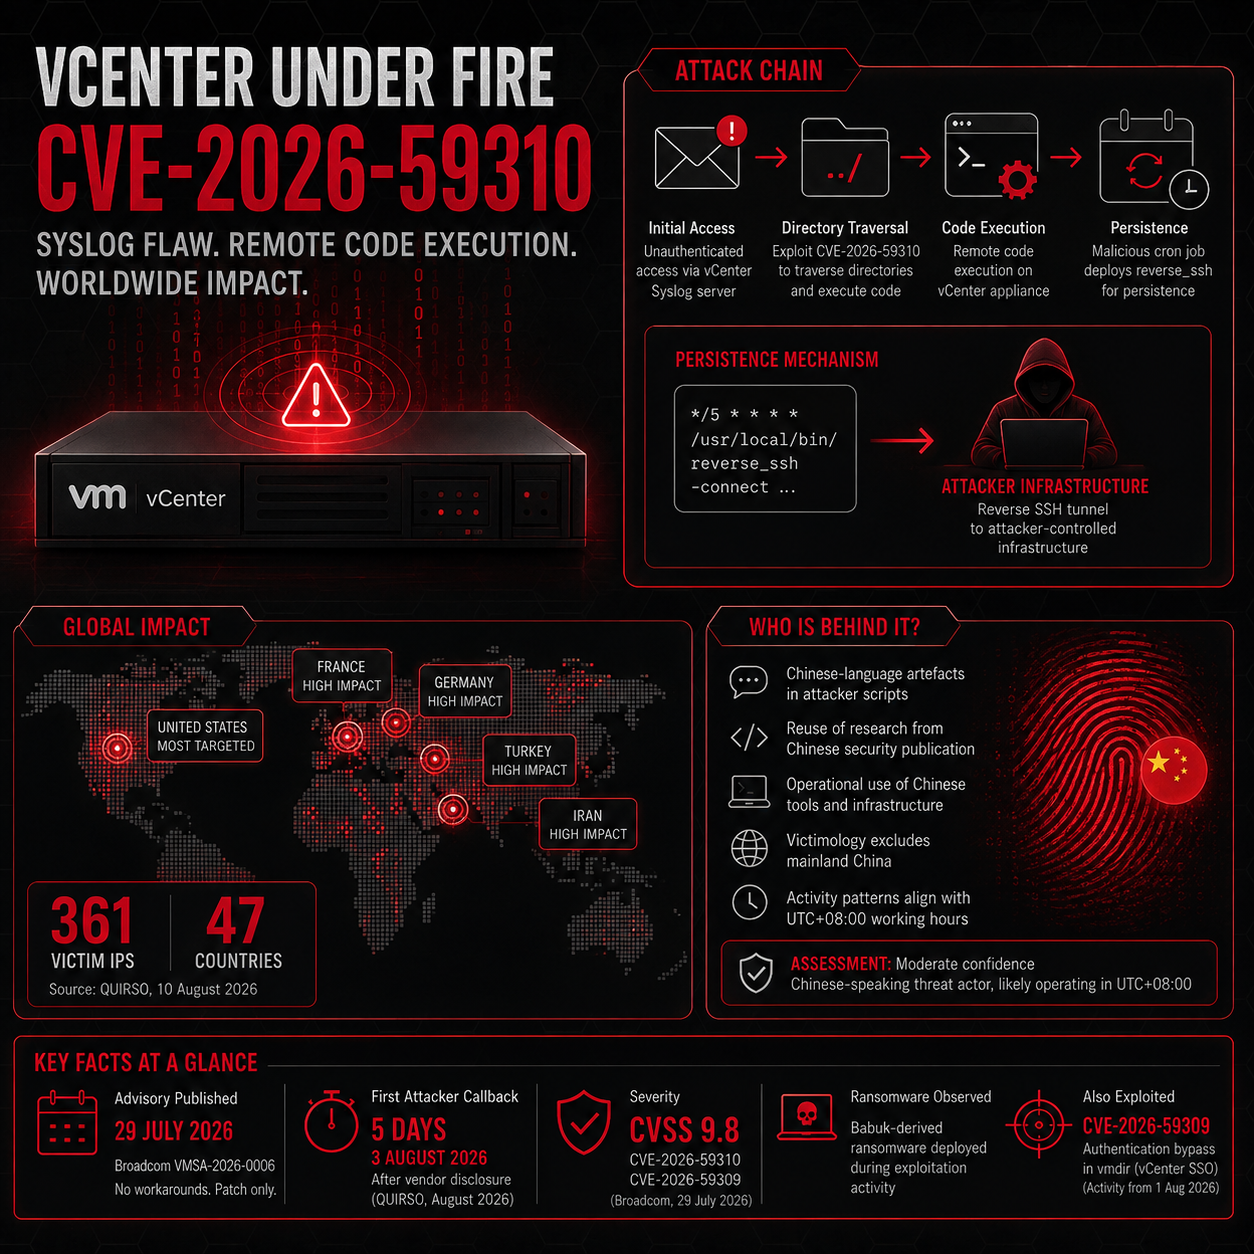
Inside the vCenter Syslog Flaw Being Used to Backdoor Virtual Estates Worldwide
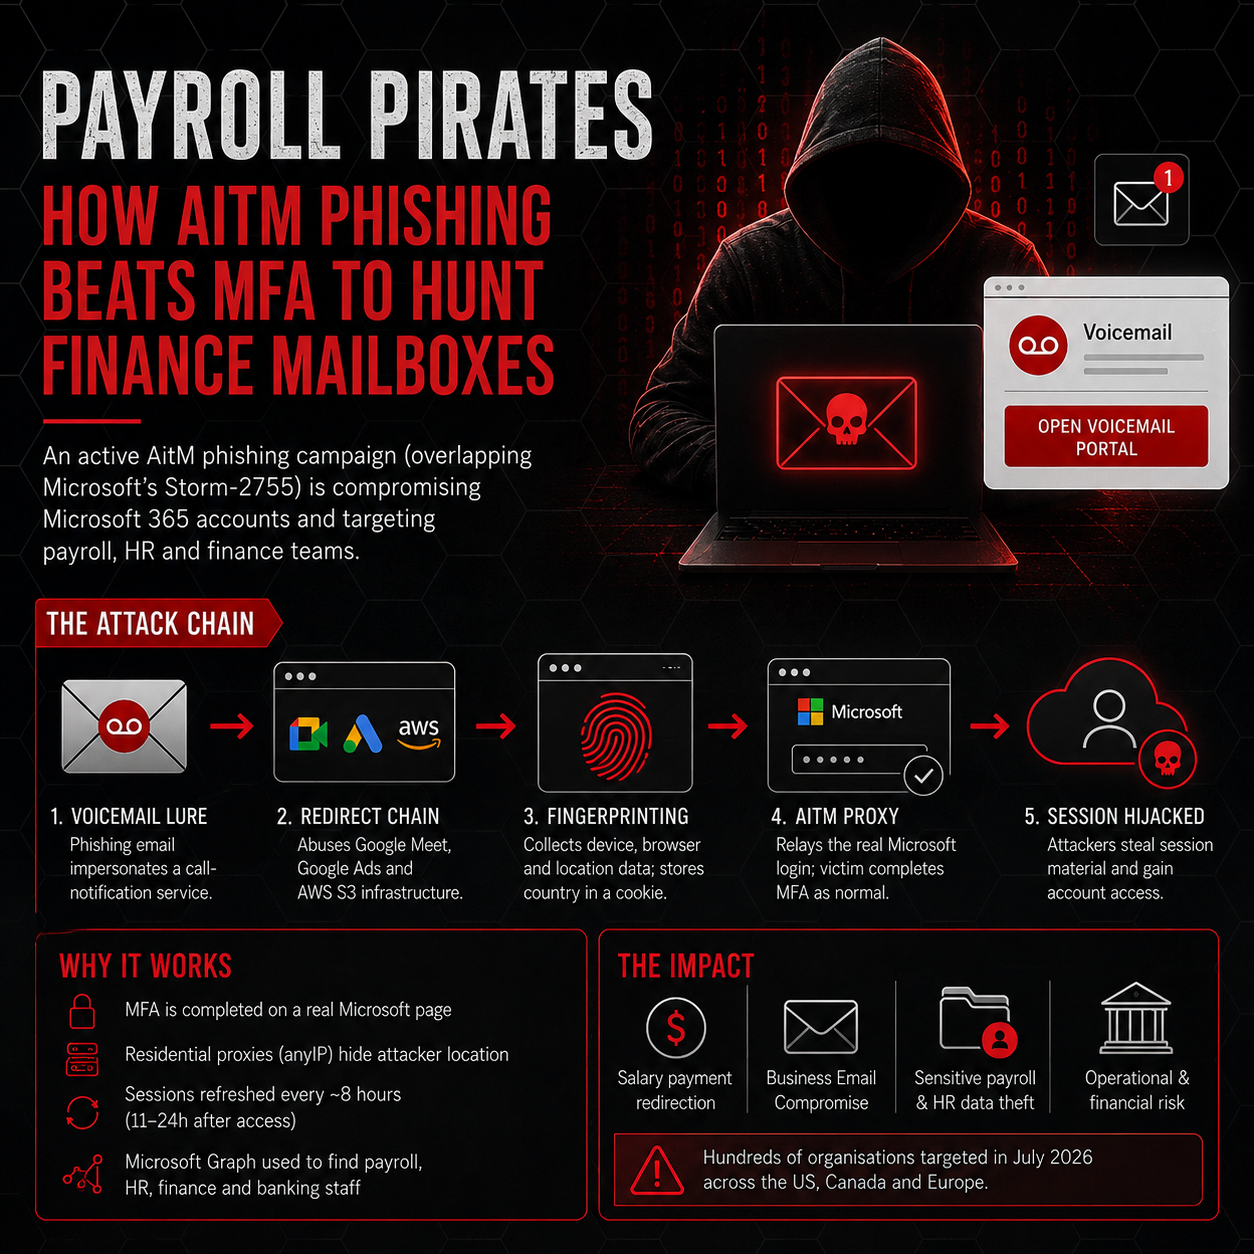
Payroll Pirates: How AitM Phishing Beats MFA to Hunt Finance Mailboxes
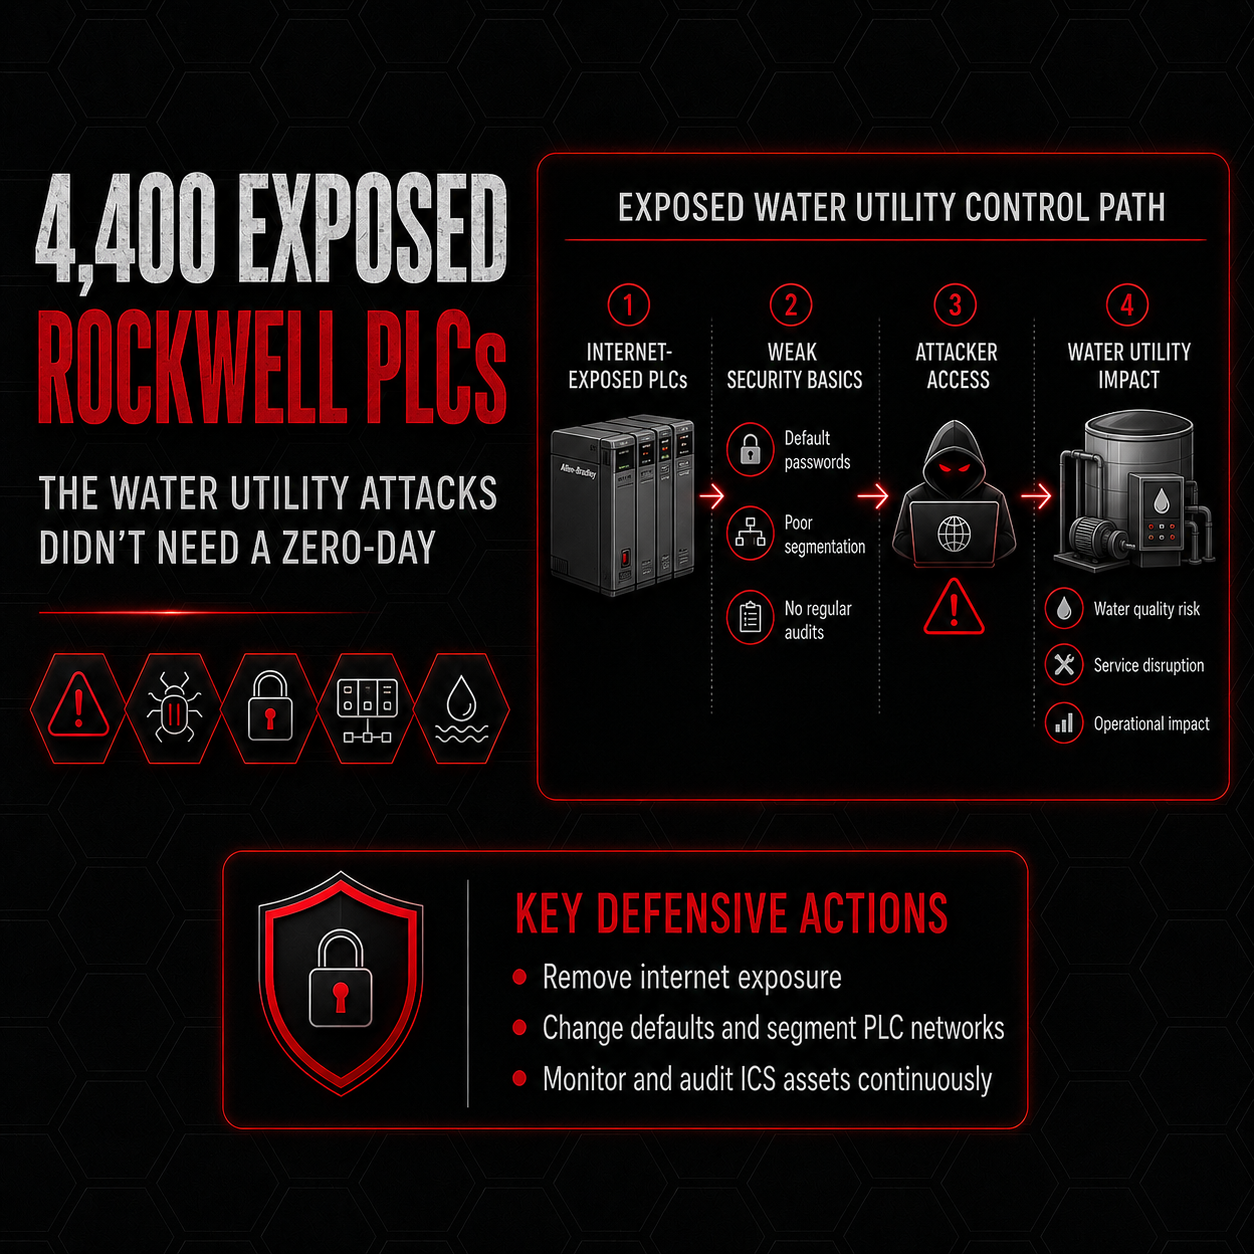
4,400 Exposed Rockwell PLCs — The Water Utility Attacks Didn't Need a Zero-Day
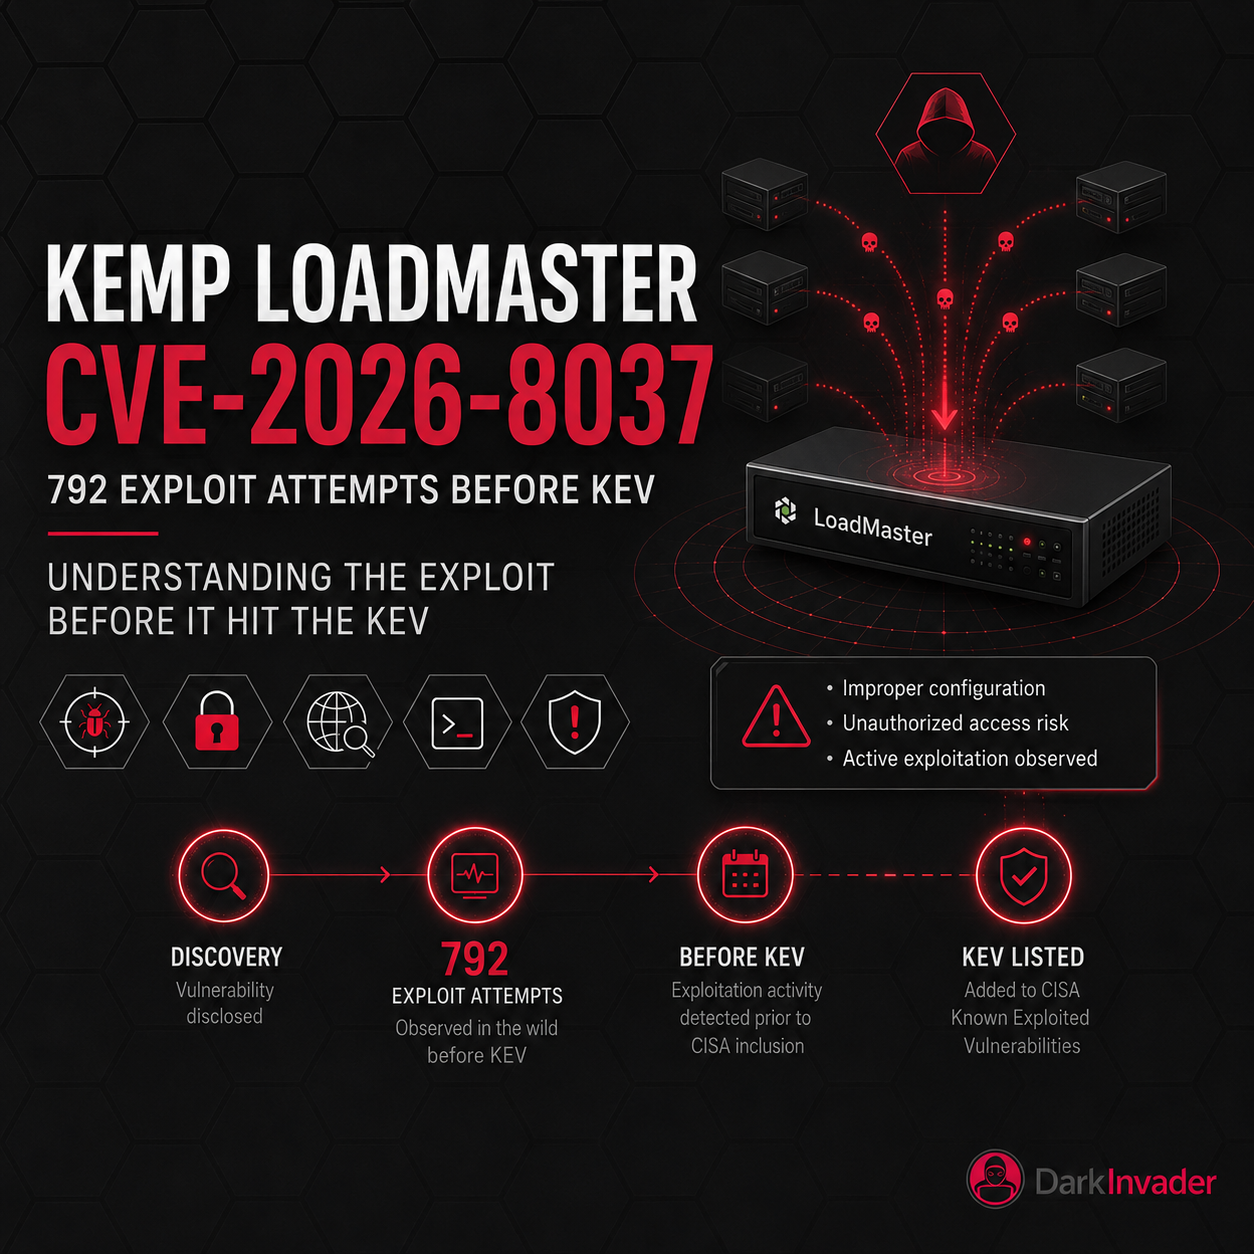
Kemp LoadMaster CVE-2026-8037: Understanding the Exploit Before It Hit the KEV
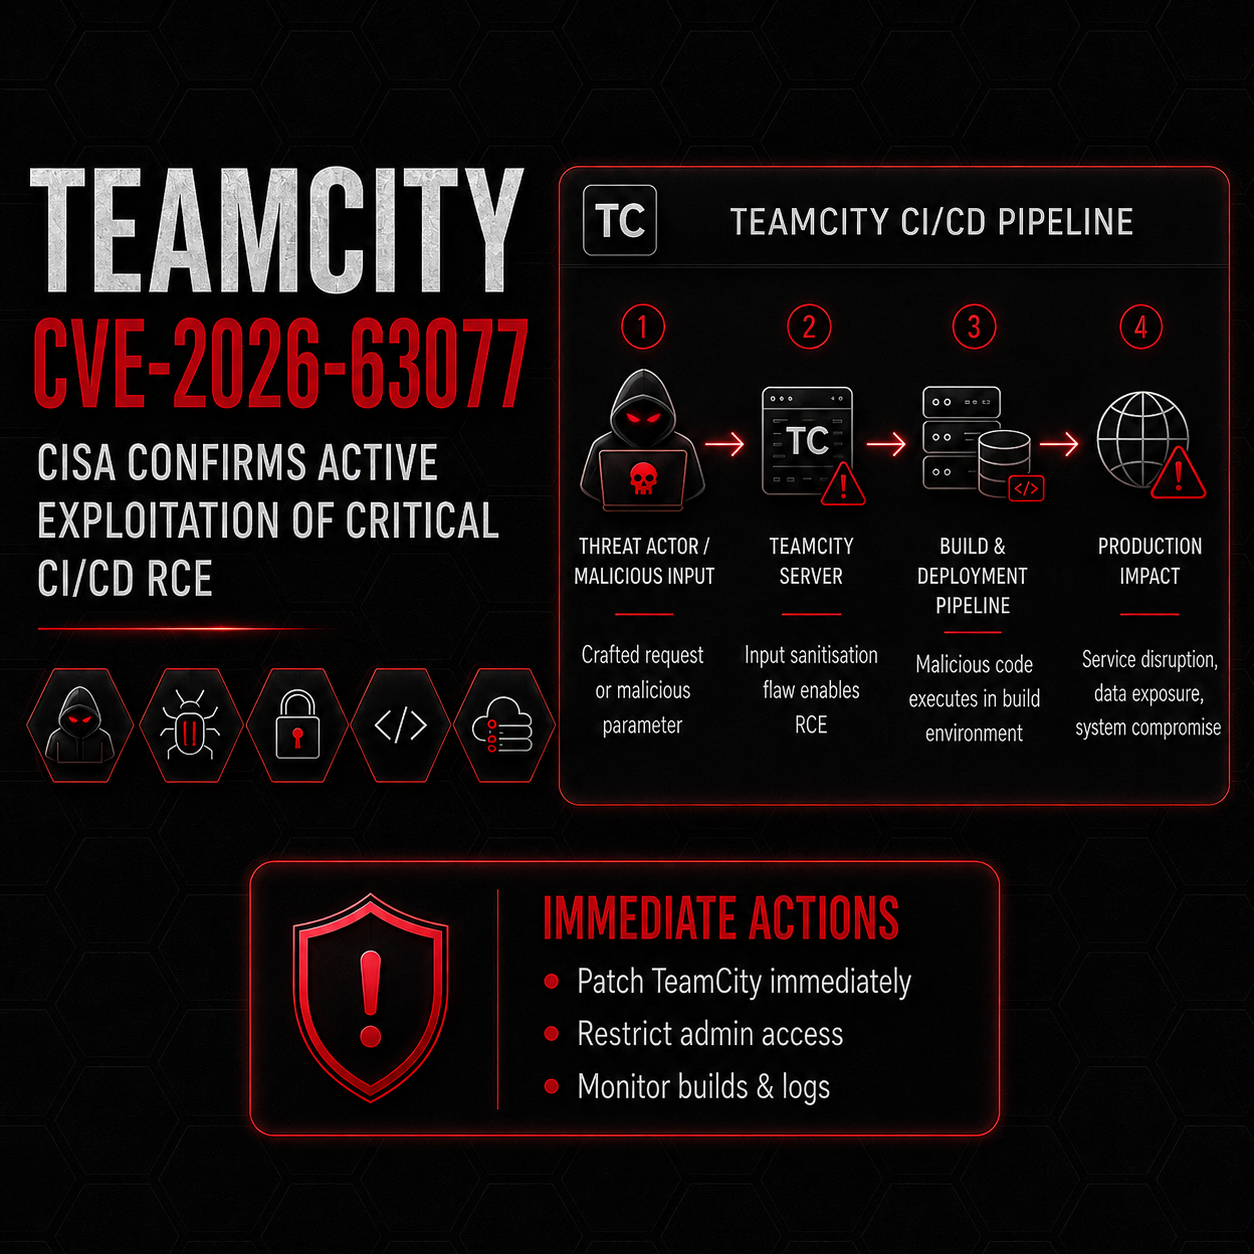
TeamCity CVE-2026-63077 — CISA Confirms Active Exploitation of Critical CI/CD RCE
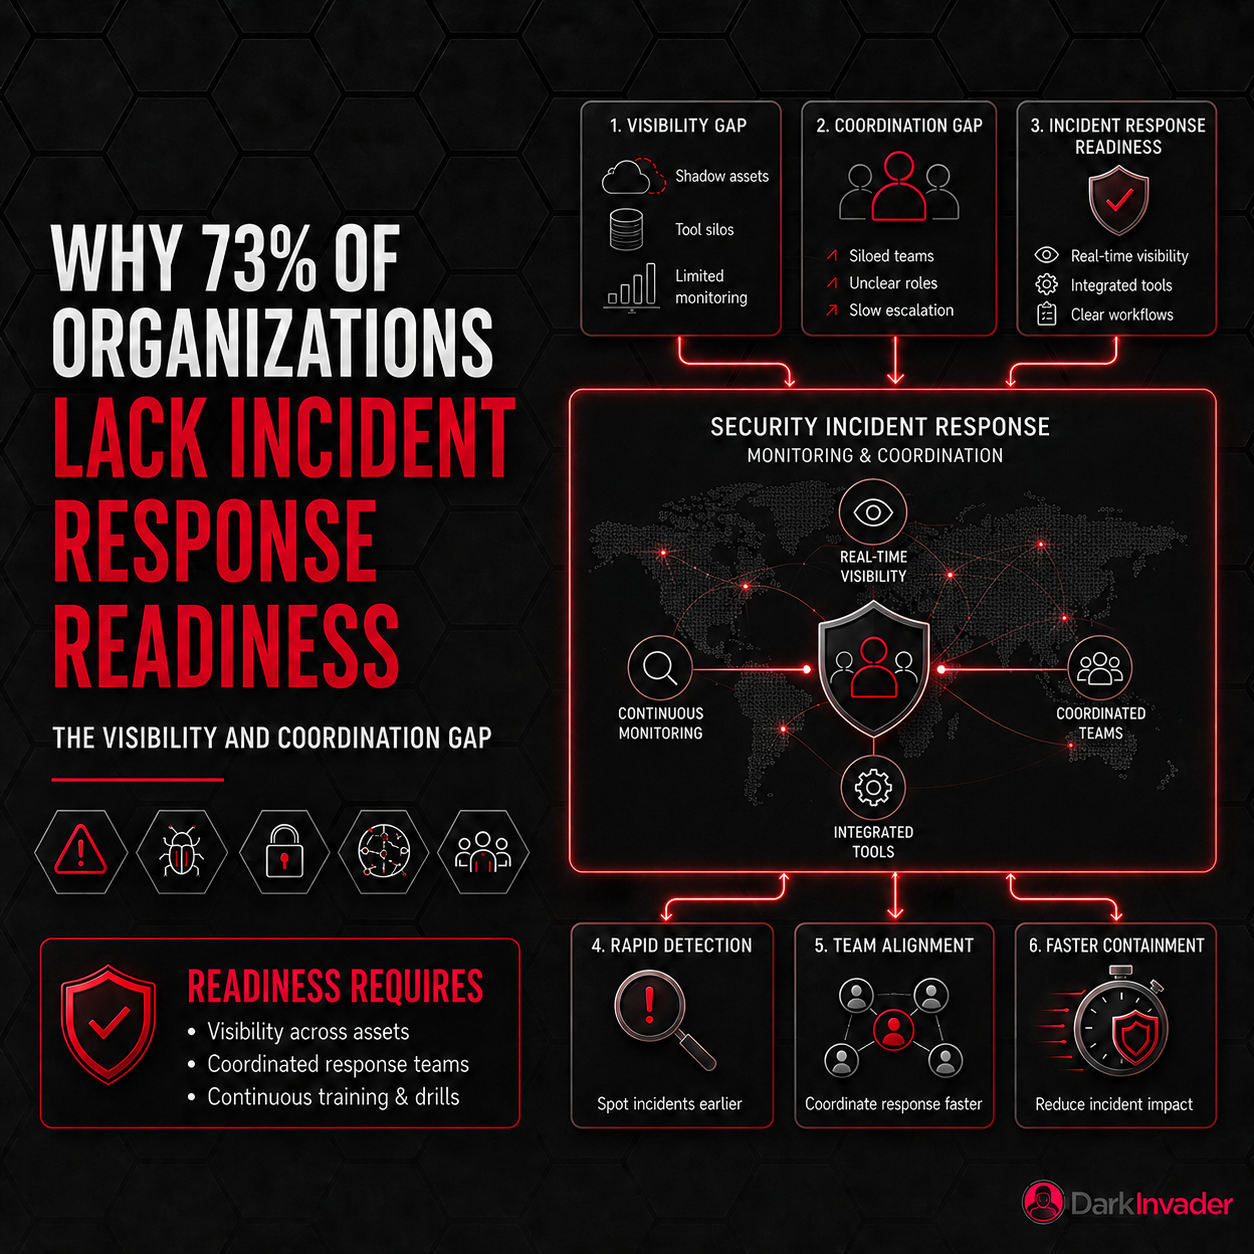
Why 73% of Organizations Lack Incident Response Readiness: The Visibility and Coordination Gap
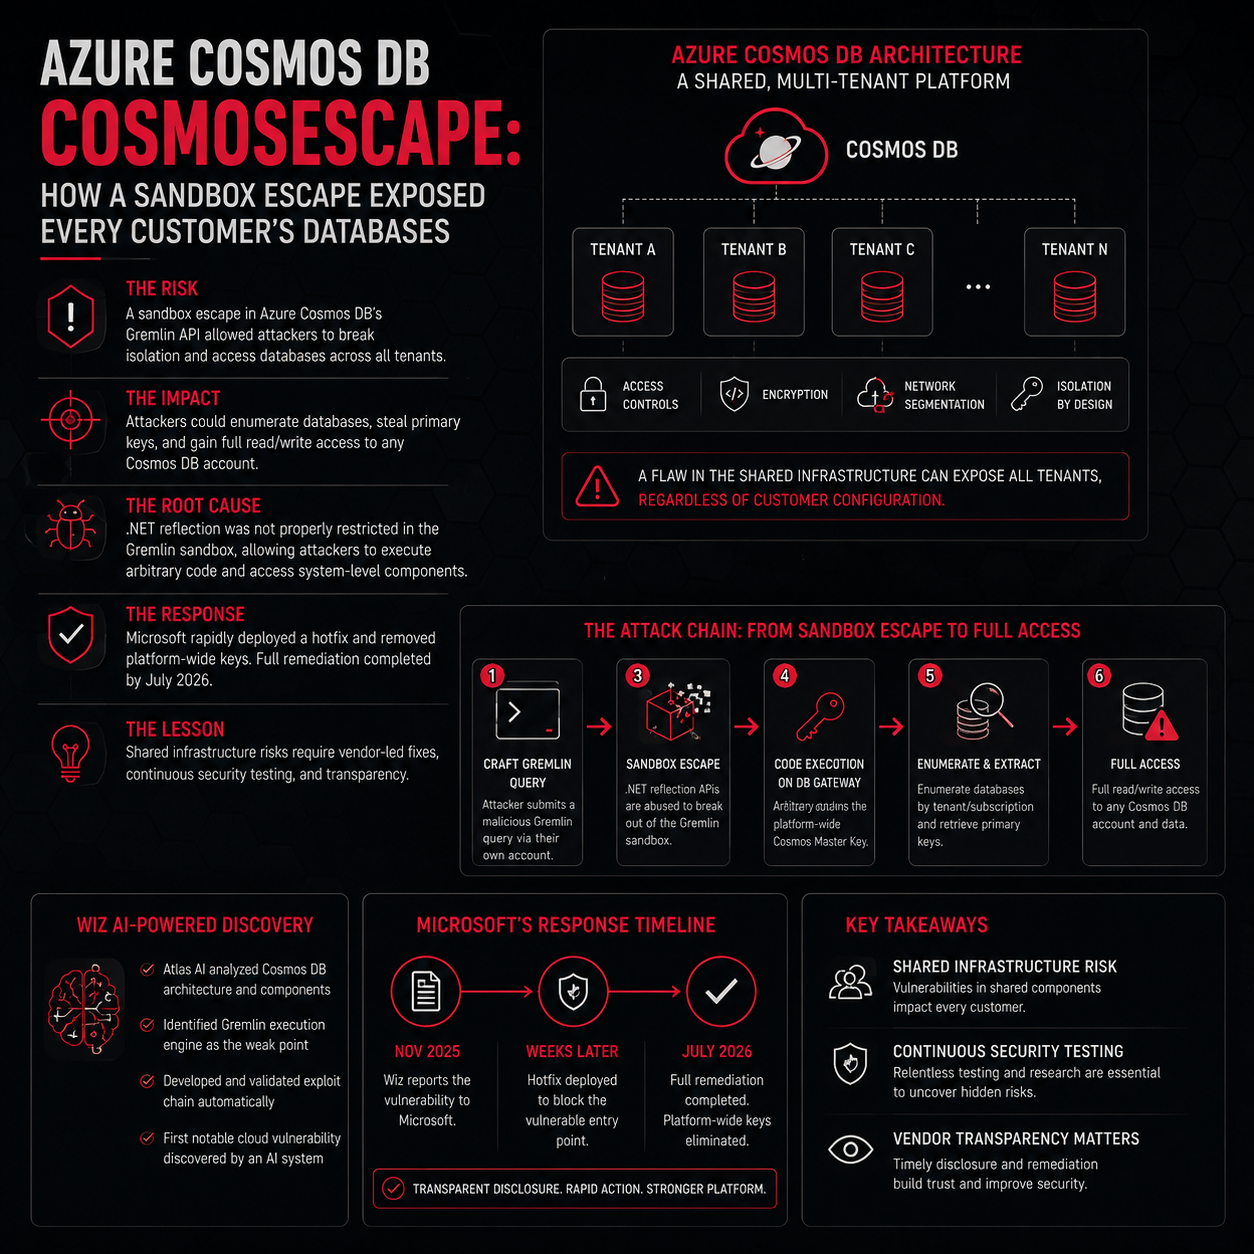
Azure Cosmos DB CosmosEscape: How a Sandbox Escape Exposed Every Customer's Databases
Minnesota Water Systems Under Attack: How External Asset Visibility Stops Critical Infrastructure Breaches
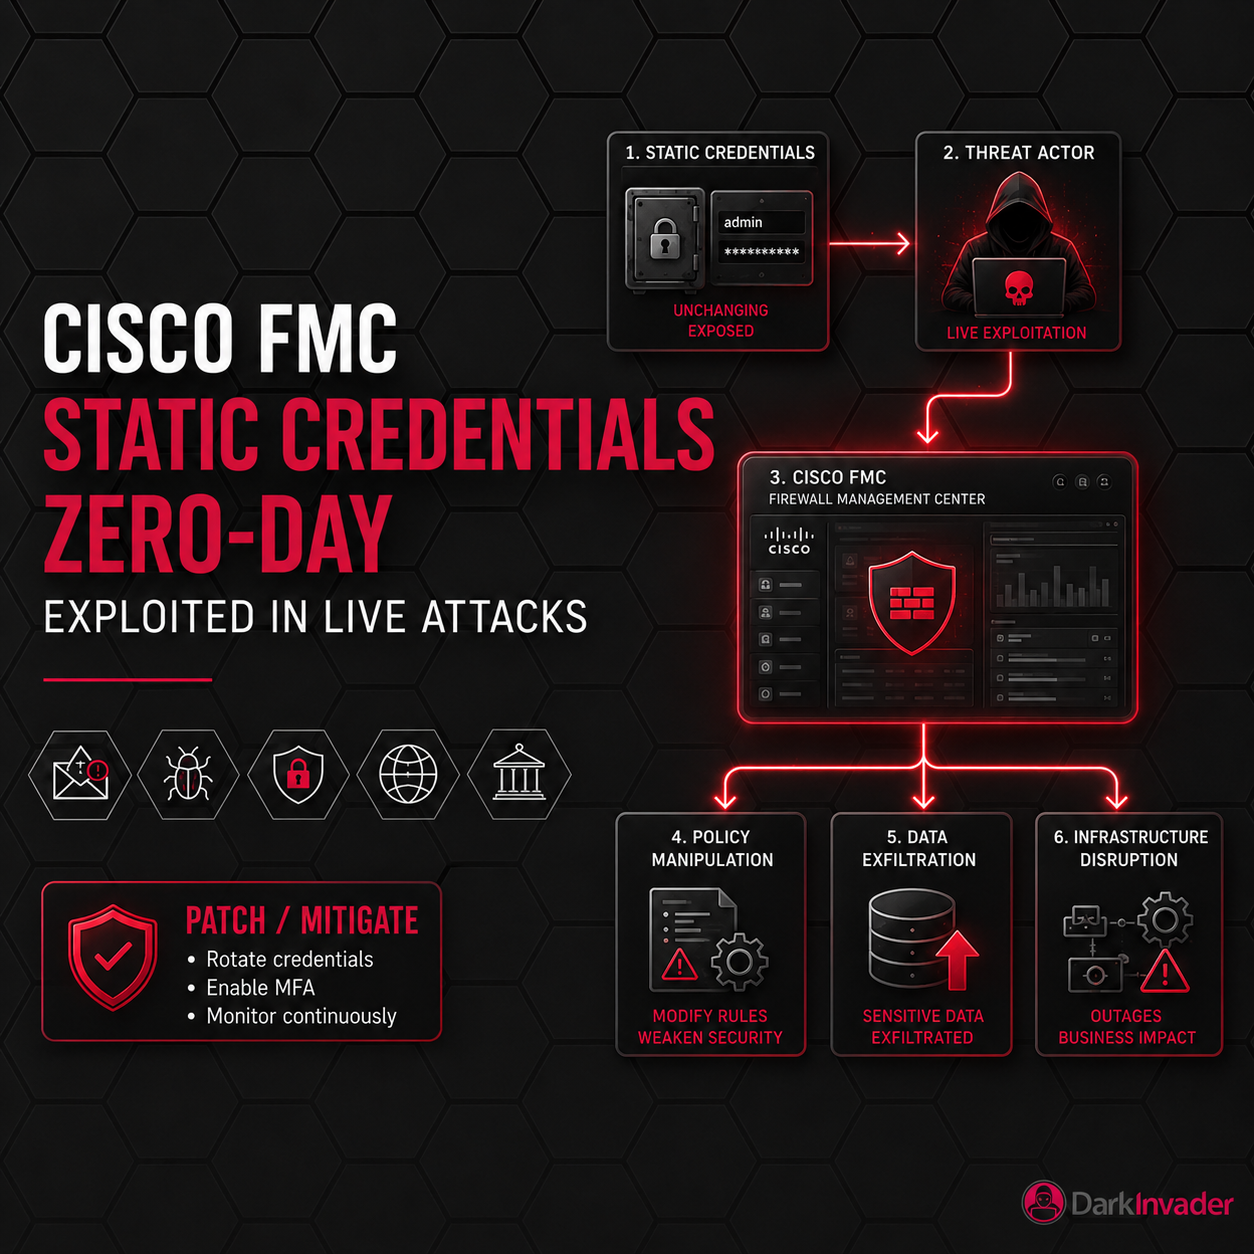
Cisco FMC Static Credentials Zero-Day Exploited in Live Attacks
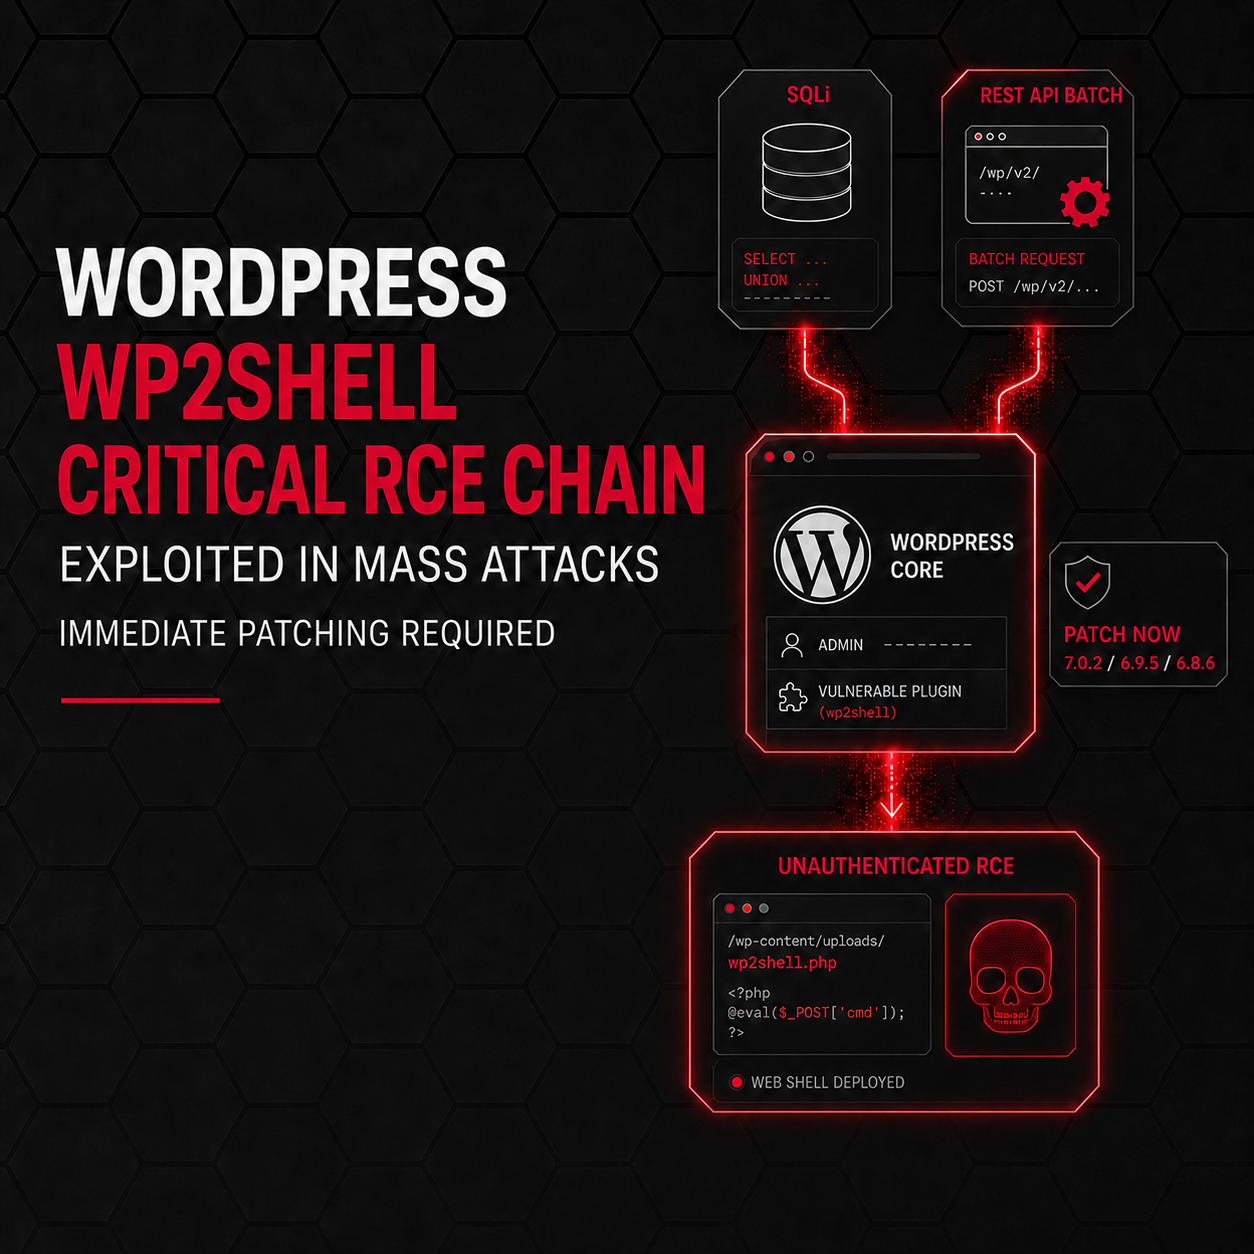
WordPress wp2shell Critical RCE Chain Exploited in Mass Attacks: Immediate Patching Required
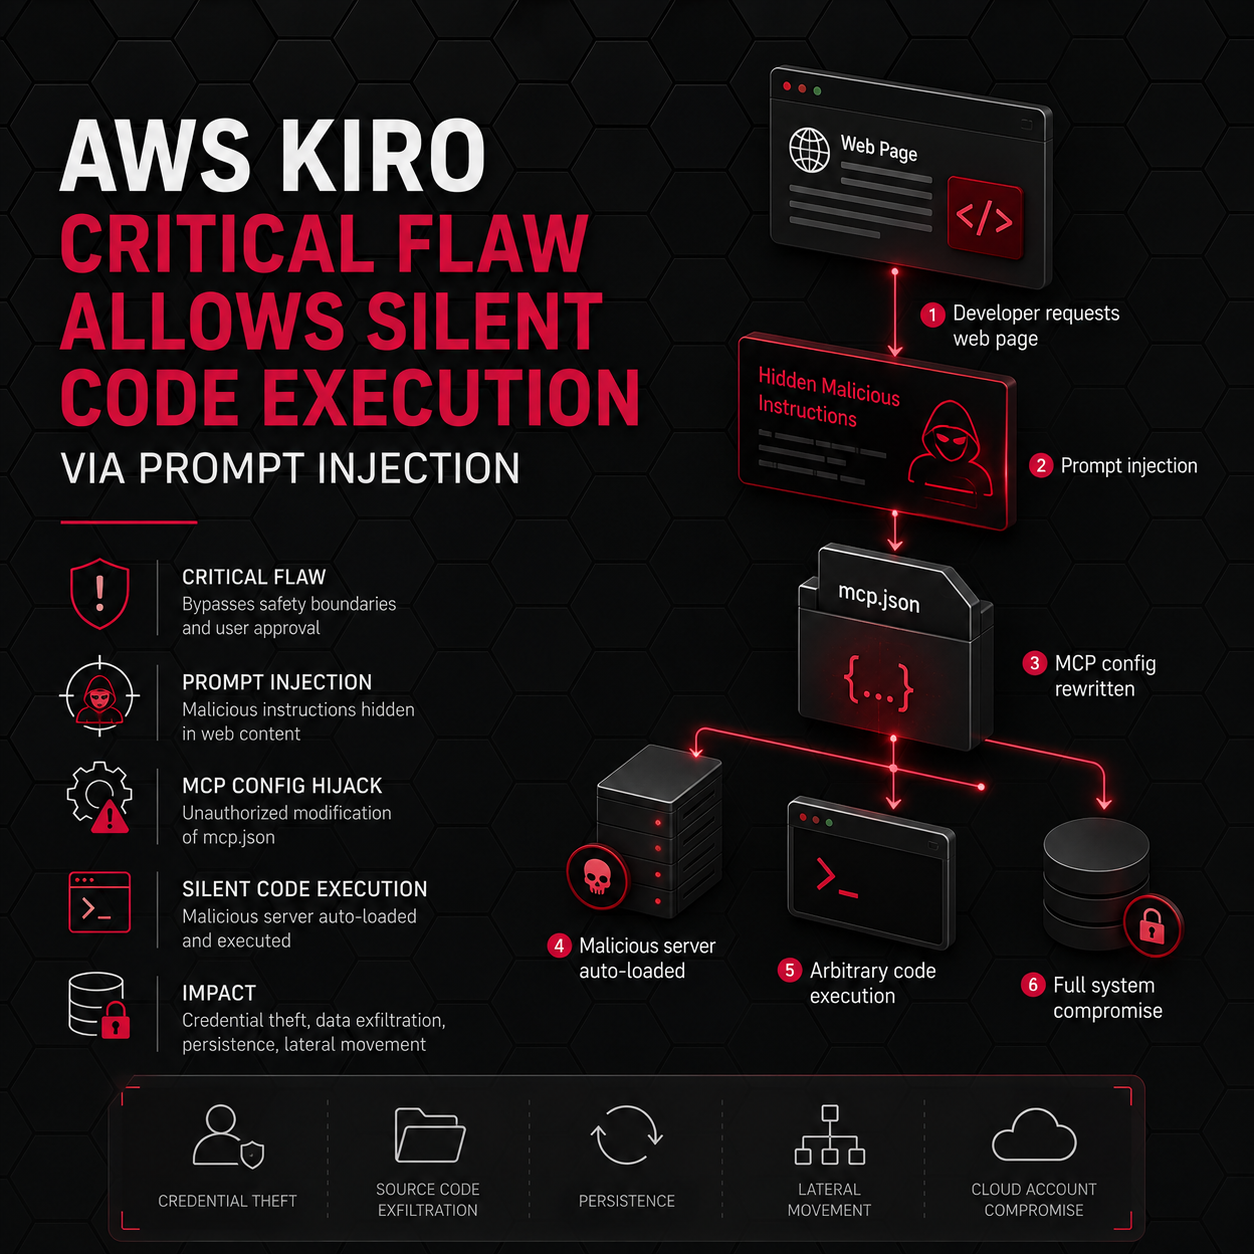
AWS Kiro Security Flaw: Prompt Injection Bypasses Safety Boundaries and Enables Silent Code Execution
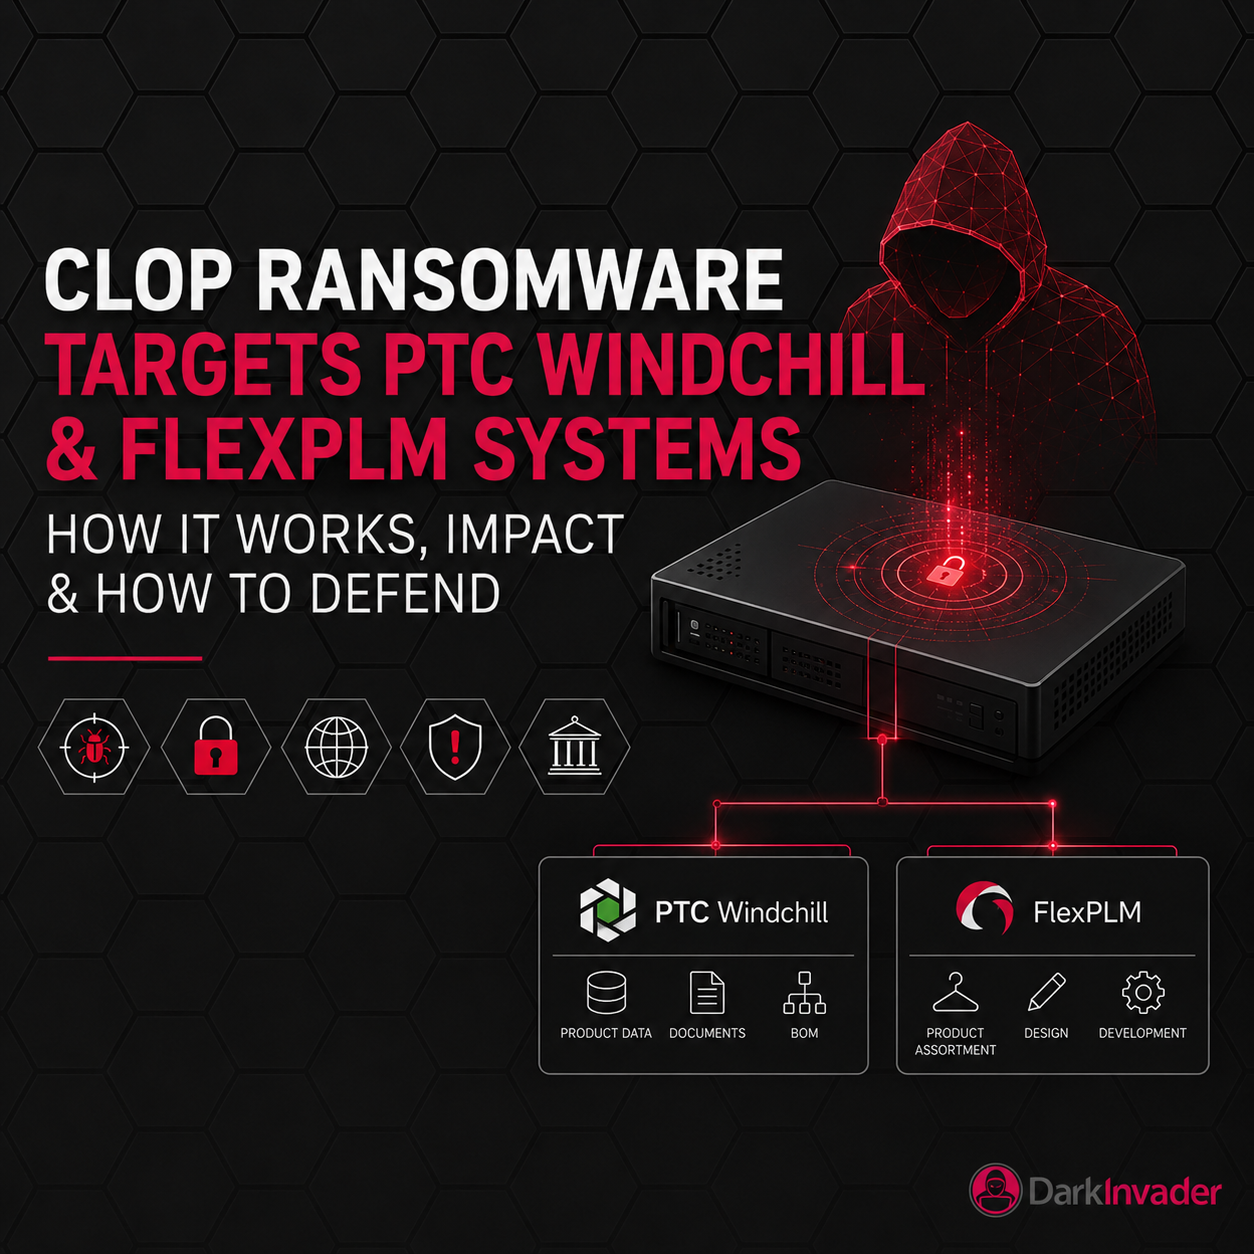
Cl0p Ransomware Exploits Internet-Exposed PTC Windchill & FlexPLM
Russian State-Backed Threat Actors Deploy Zero-Click Phishing Against Western Organisations: How to Detect and Defend
Cloud Misconfiguration and Exposed Services: The Quiet Attack Surface
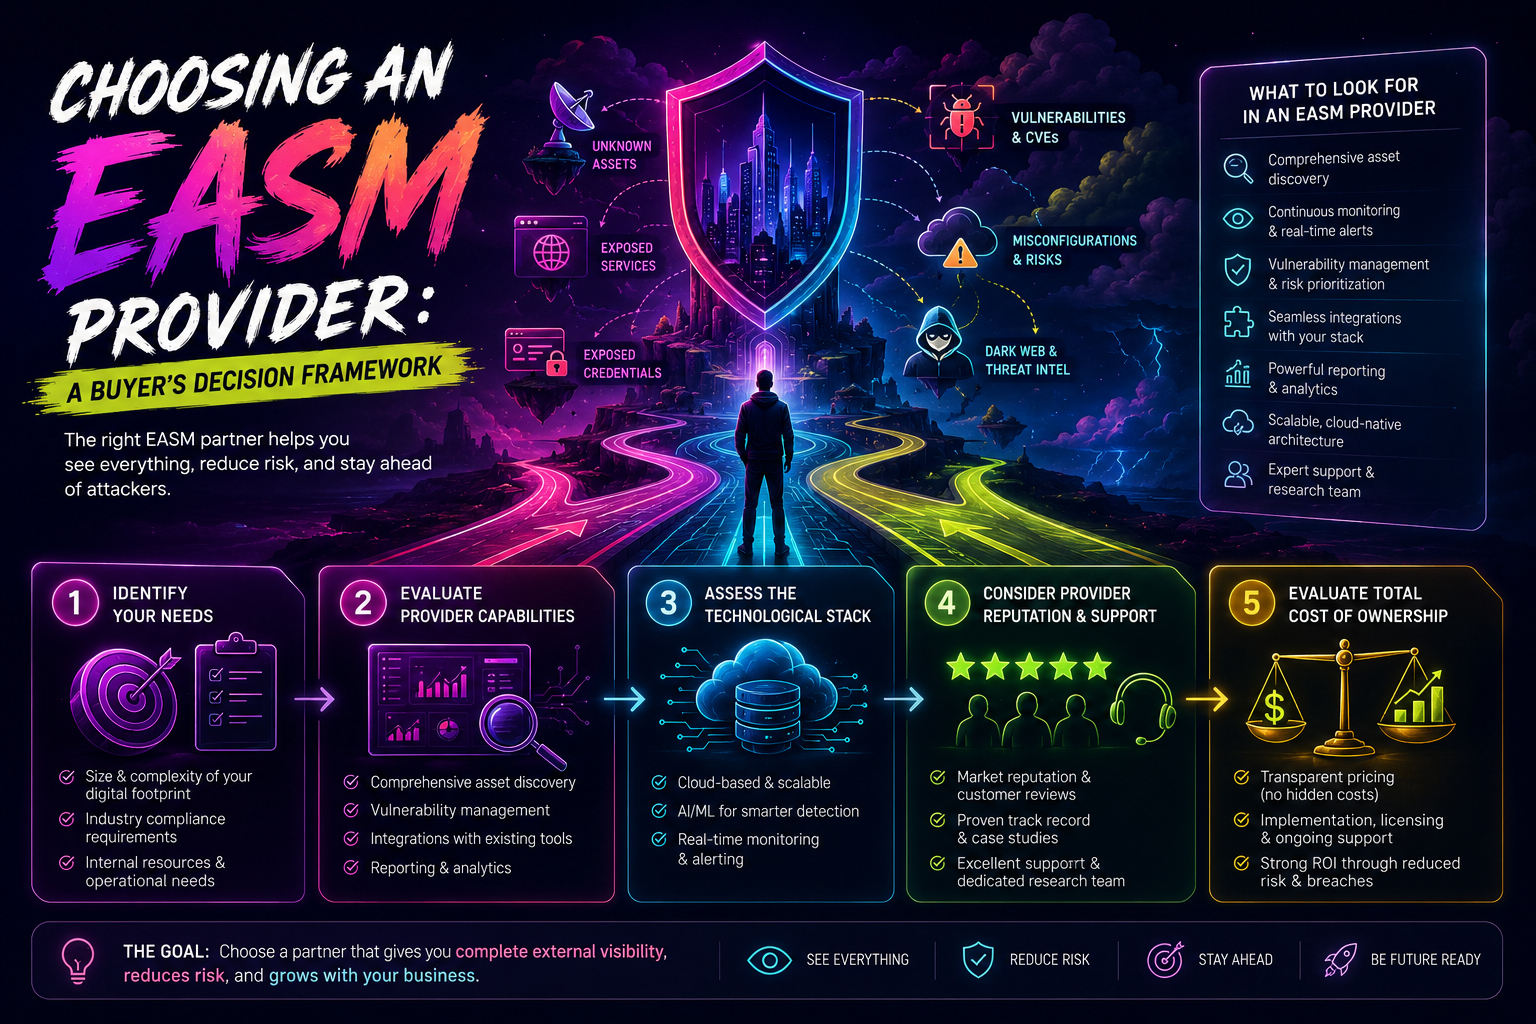
Choosing an EASM Provider: A Buyer's Decision Framework
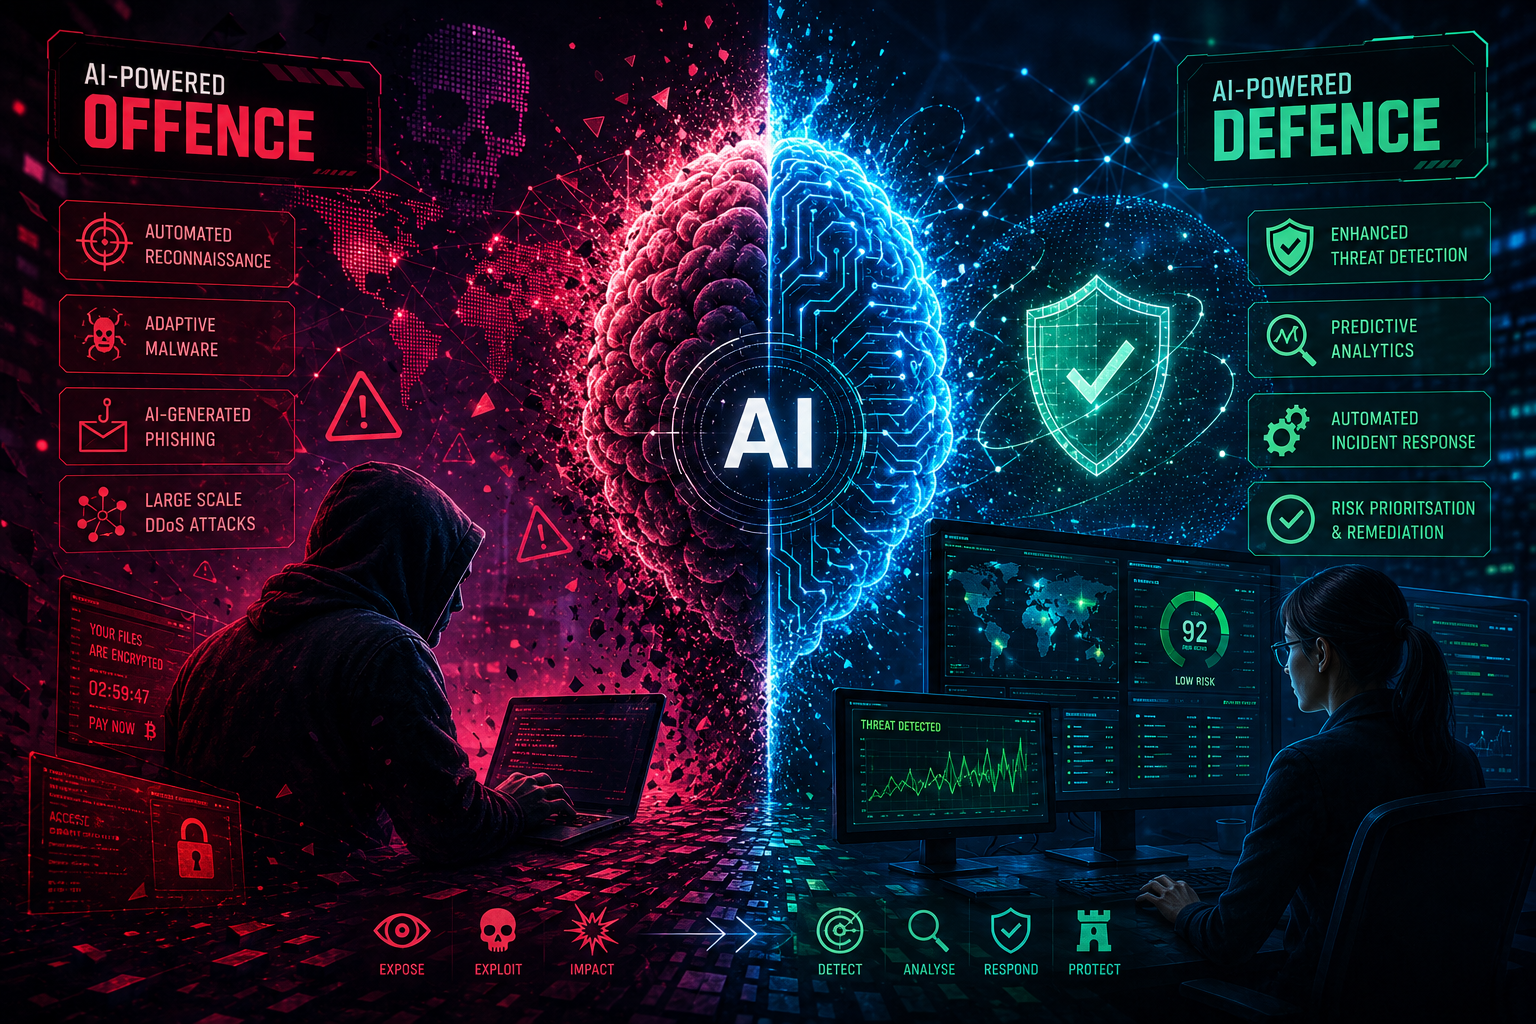
AI in Offense and Defence: The Double-Edged Attack Surface
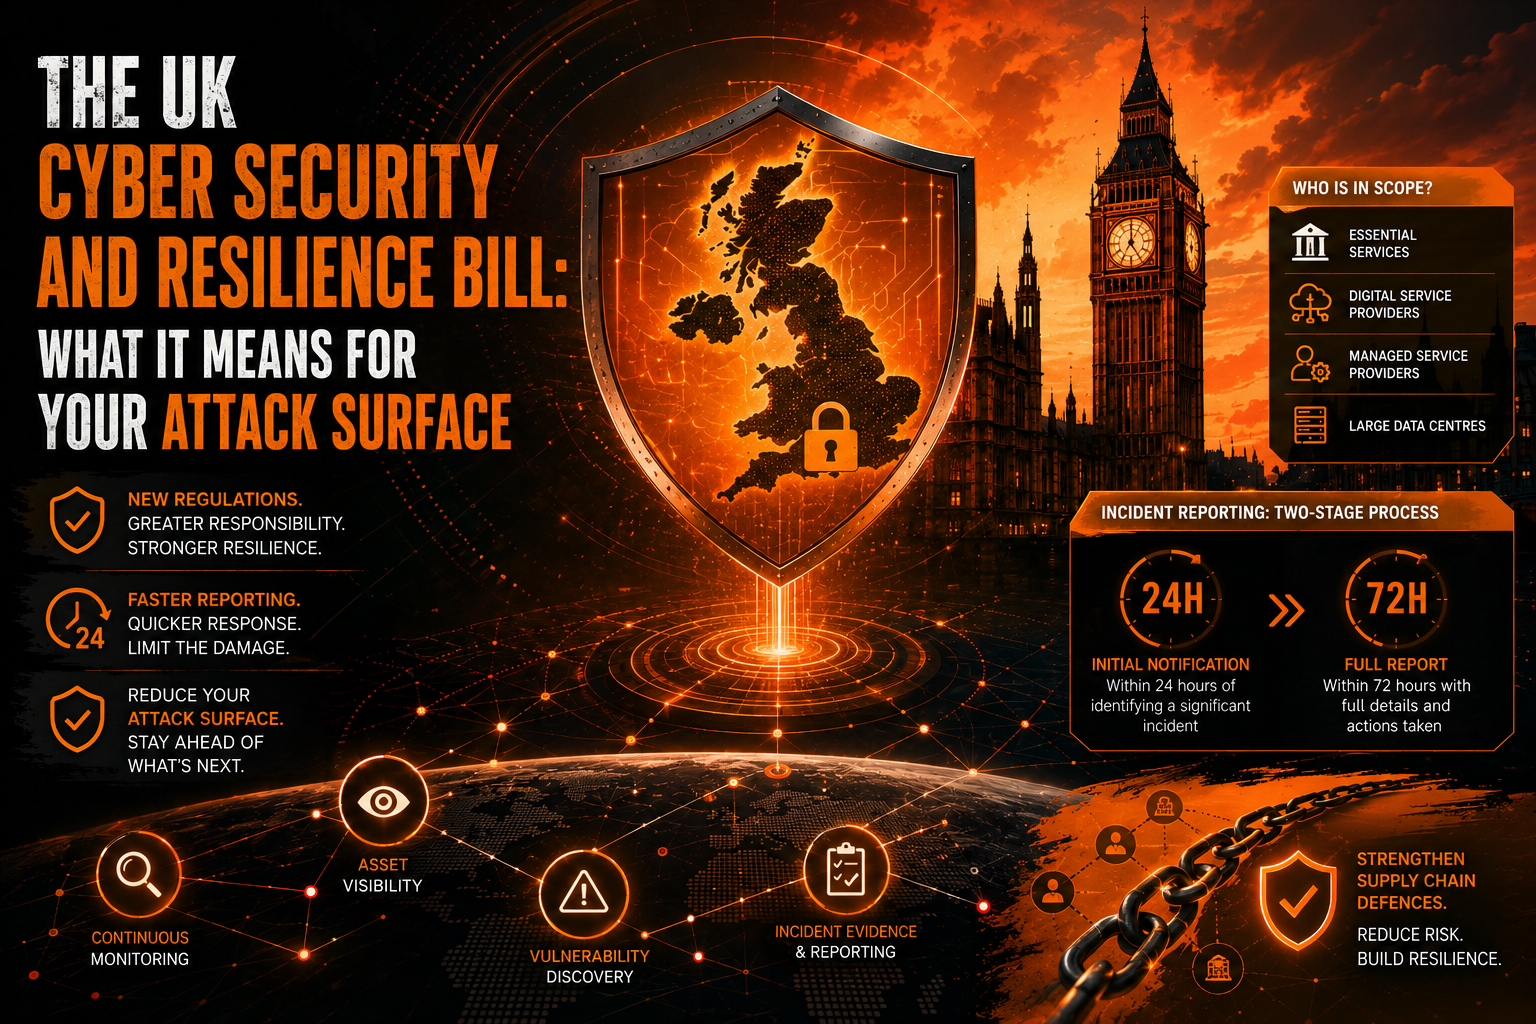
The UK Cyber Security and Resilience Bill: What It Means for Your Attack Surface
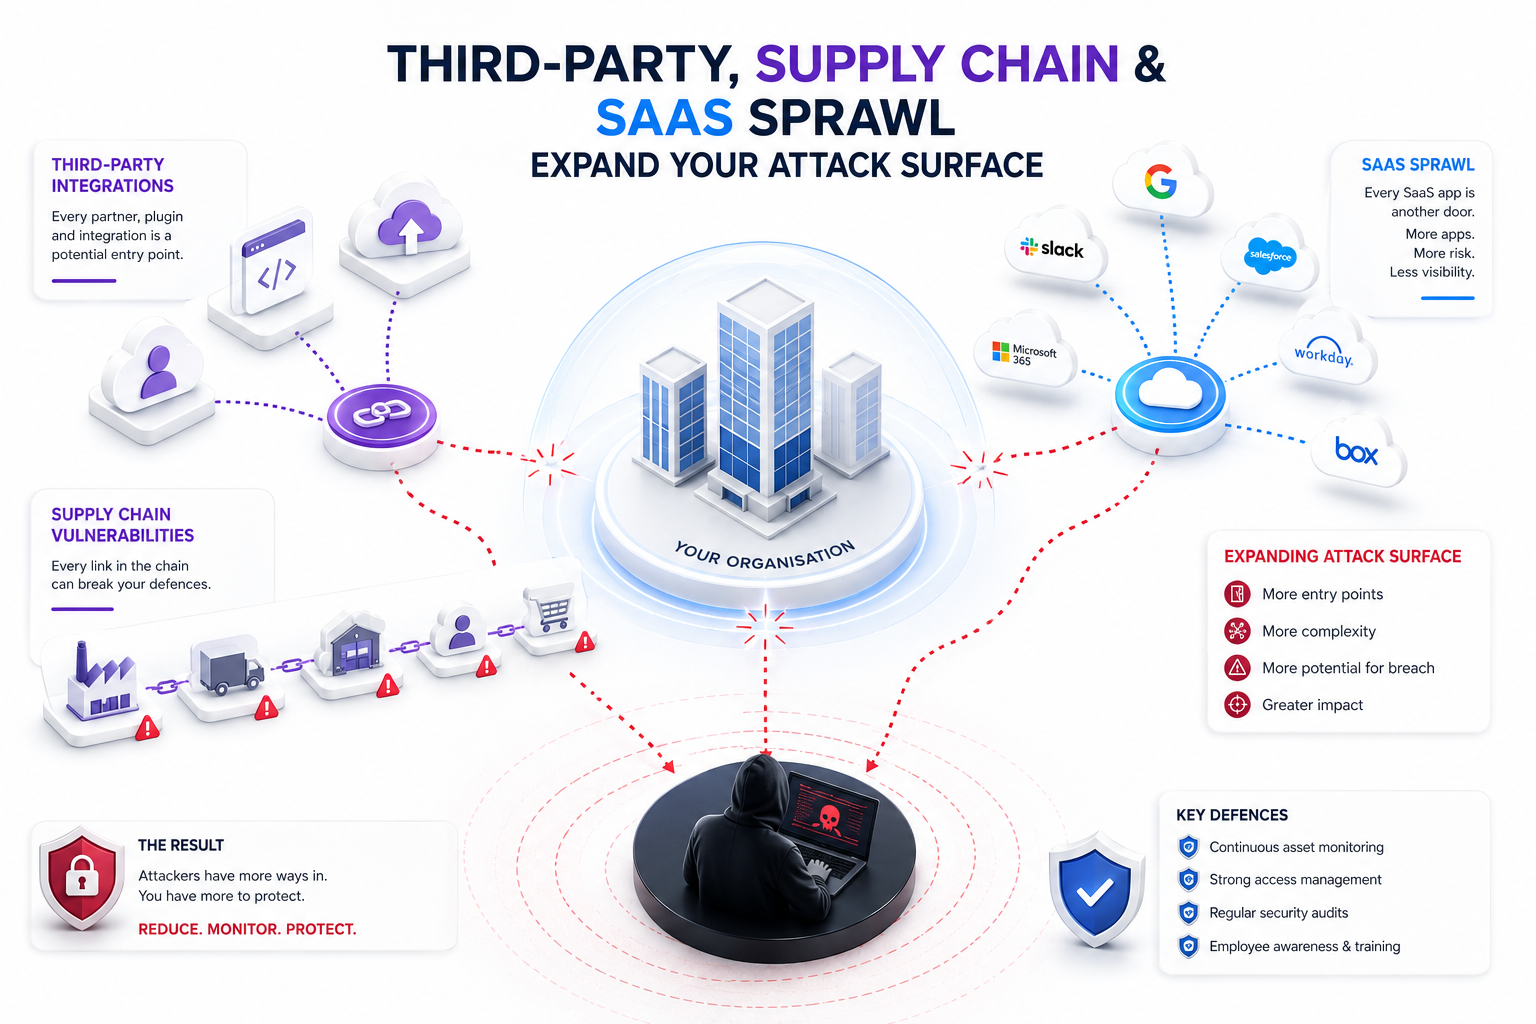
How Third-Party, Supply Chain and SaaS Sprawl Expand Your Attack Surface
What Is EASM? External Attack Surface Management Explained