• tagged
Every post filed under this tag, newest first.
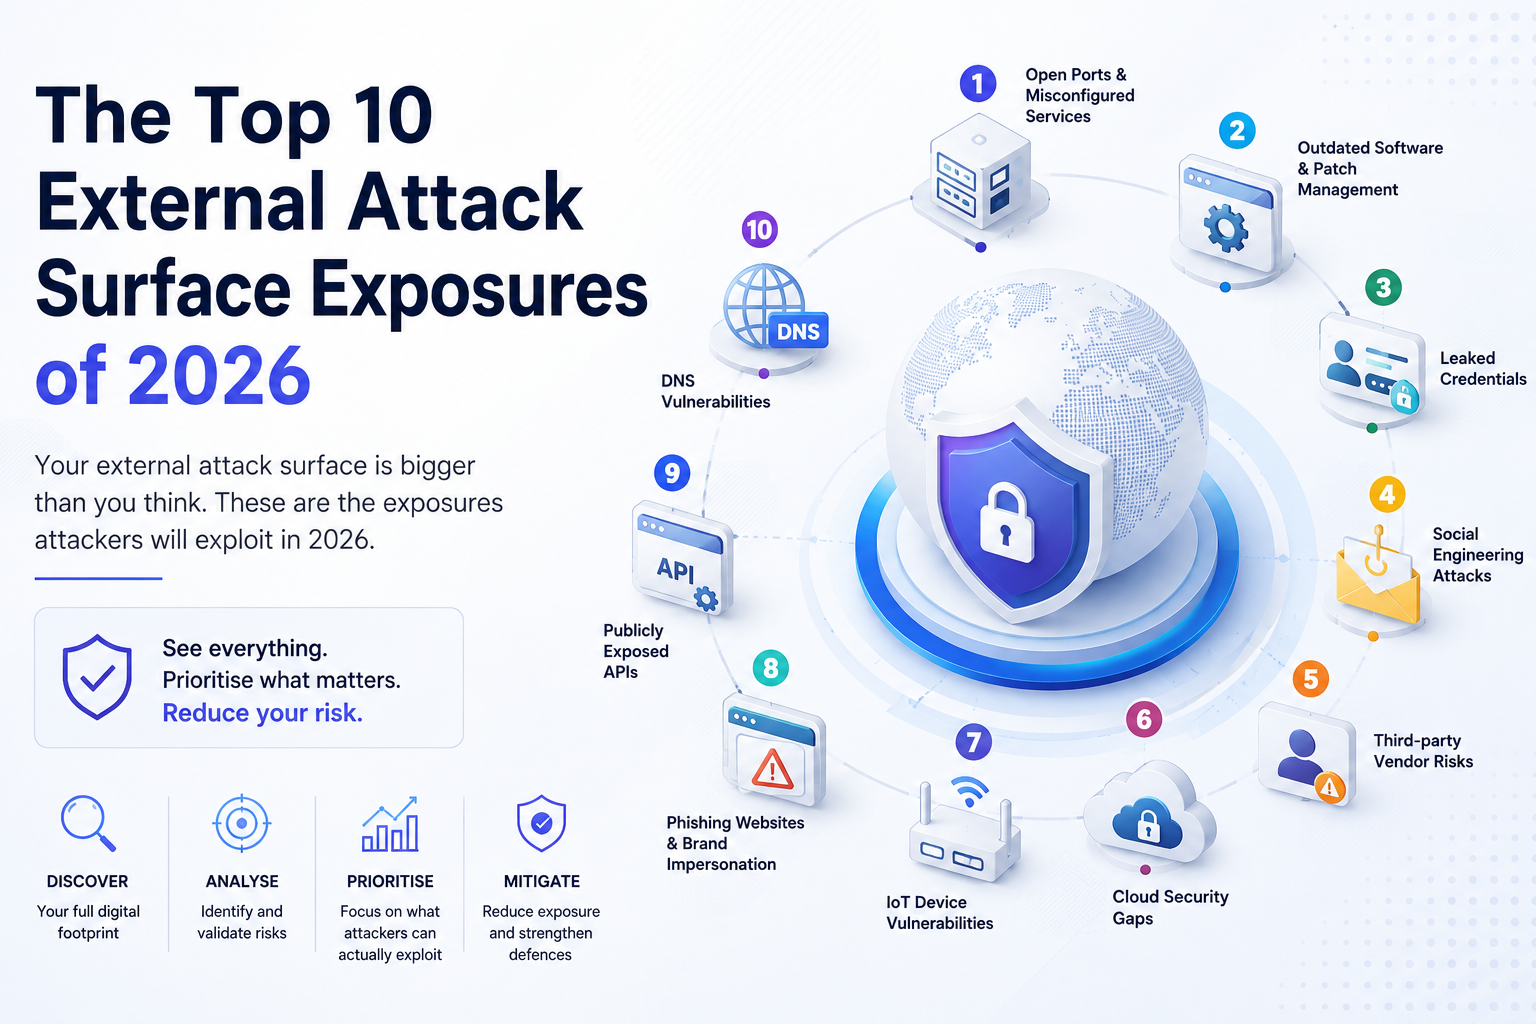
The top 10 external attack surface exposures of 2026, from exposed networks and devices to misconfigurations, and how to mitigate each risk.
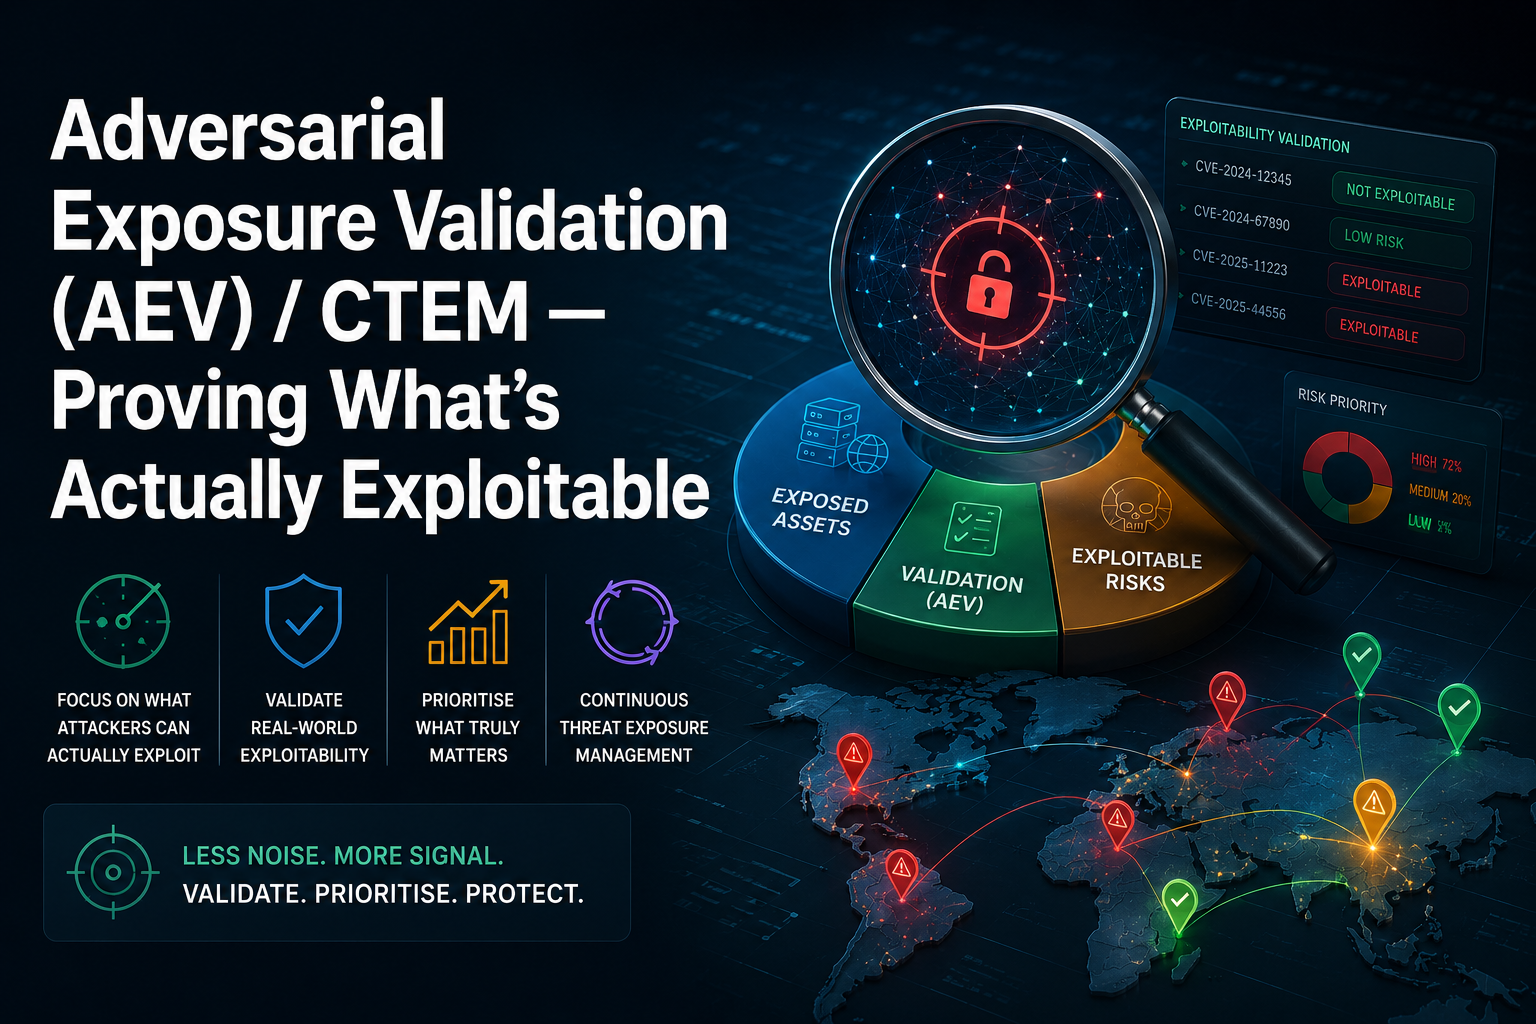
Adversarial Exposure Validation (AEV) within CTEM proves what is actually exploitable, so teams prioritise real risk over mere visibility.
Explore the FortiBleed mass Fortinet credential-harvesting campaign, its impact, and how to defend against such threats.
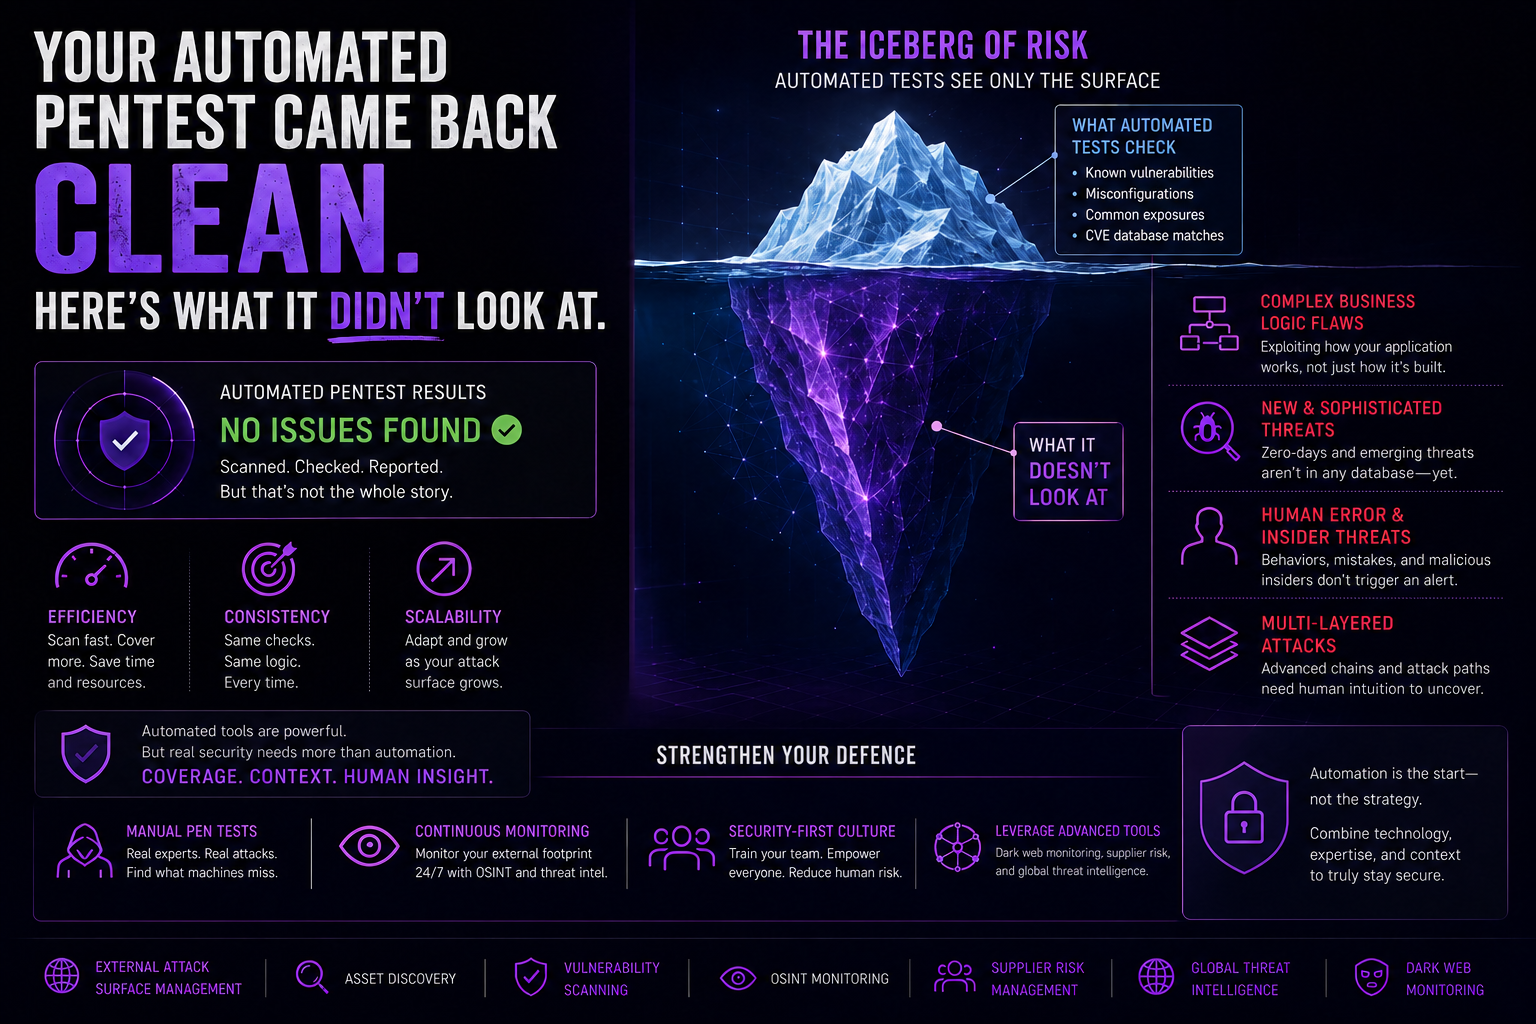
Explore the unseen gaps in automated pentesting and discover how continuous EASM can enhance your cybersecurity strategy.
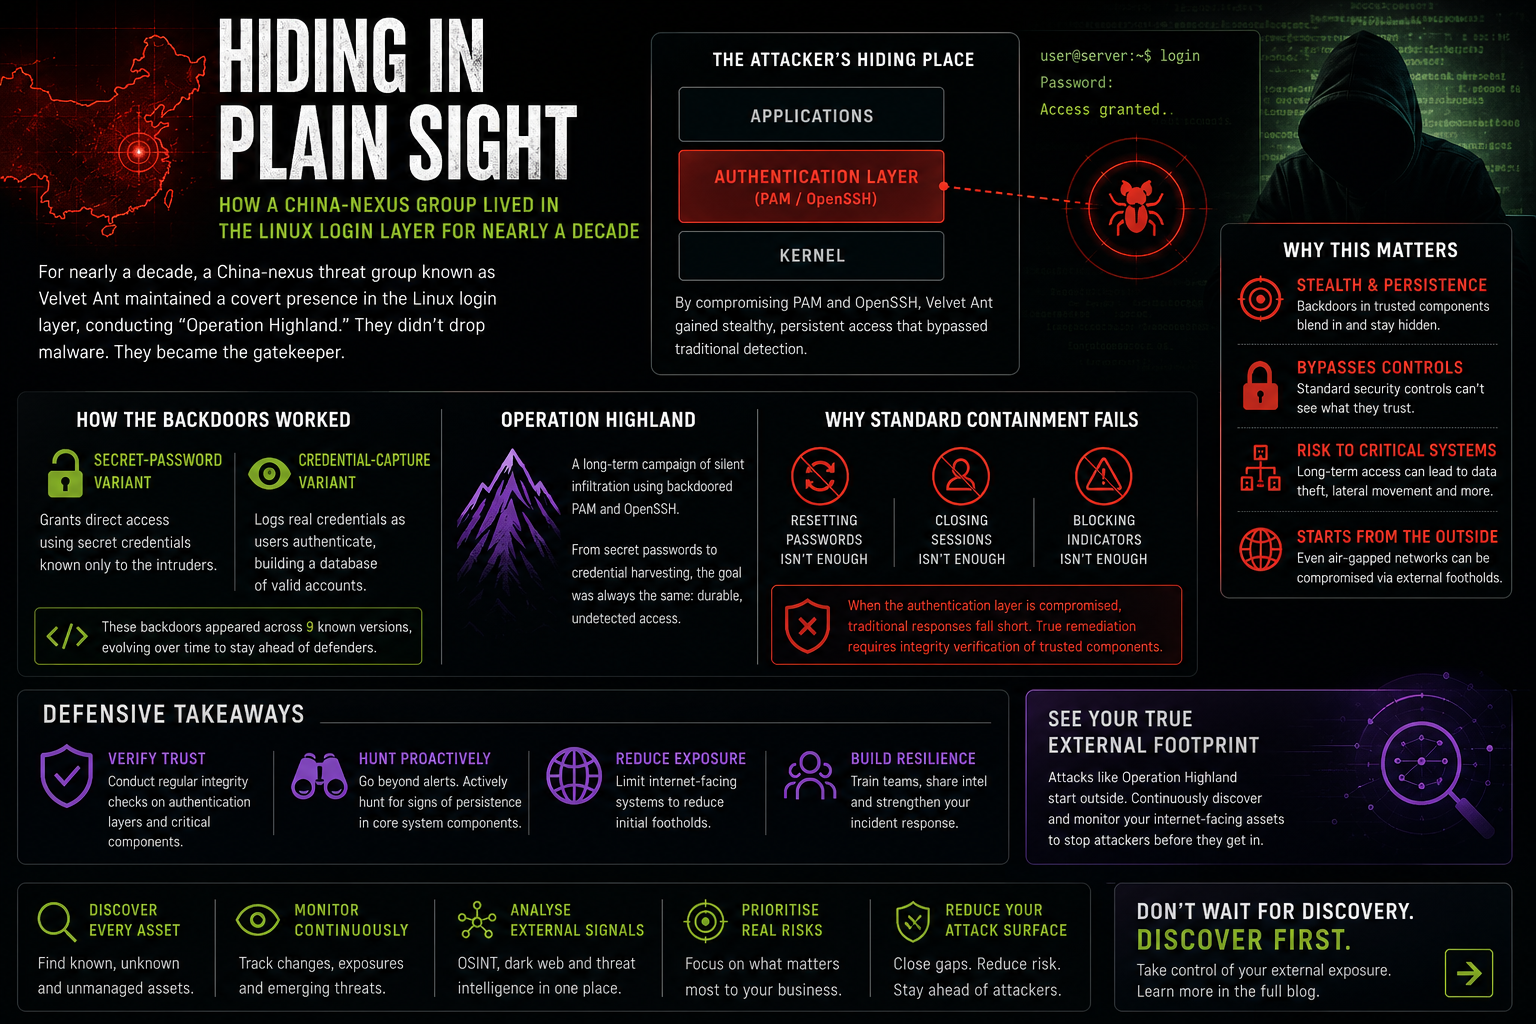
How China-nexus group Velvet Ant spent nearly a decade inside Linux login systems, using PAM and OpenSSH backdoors to keep persistent access.
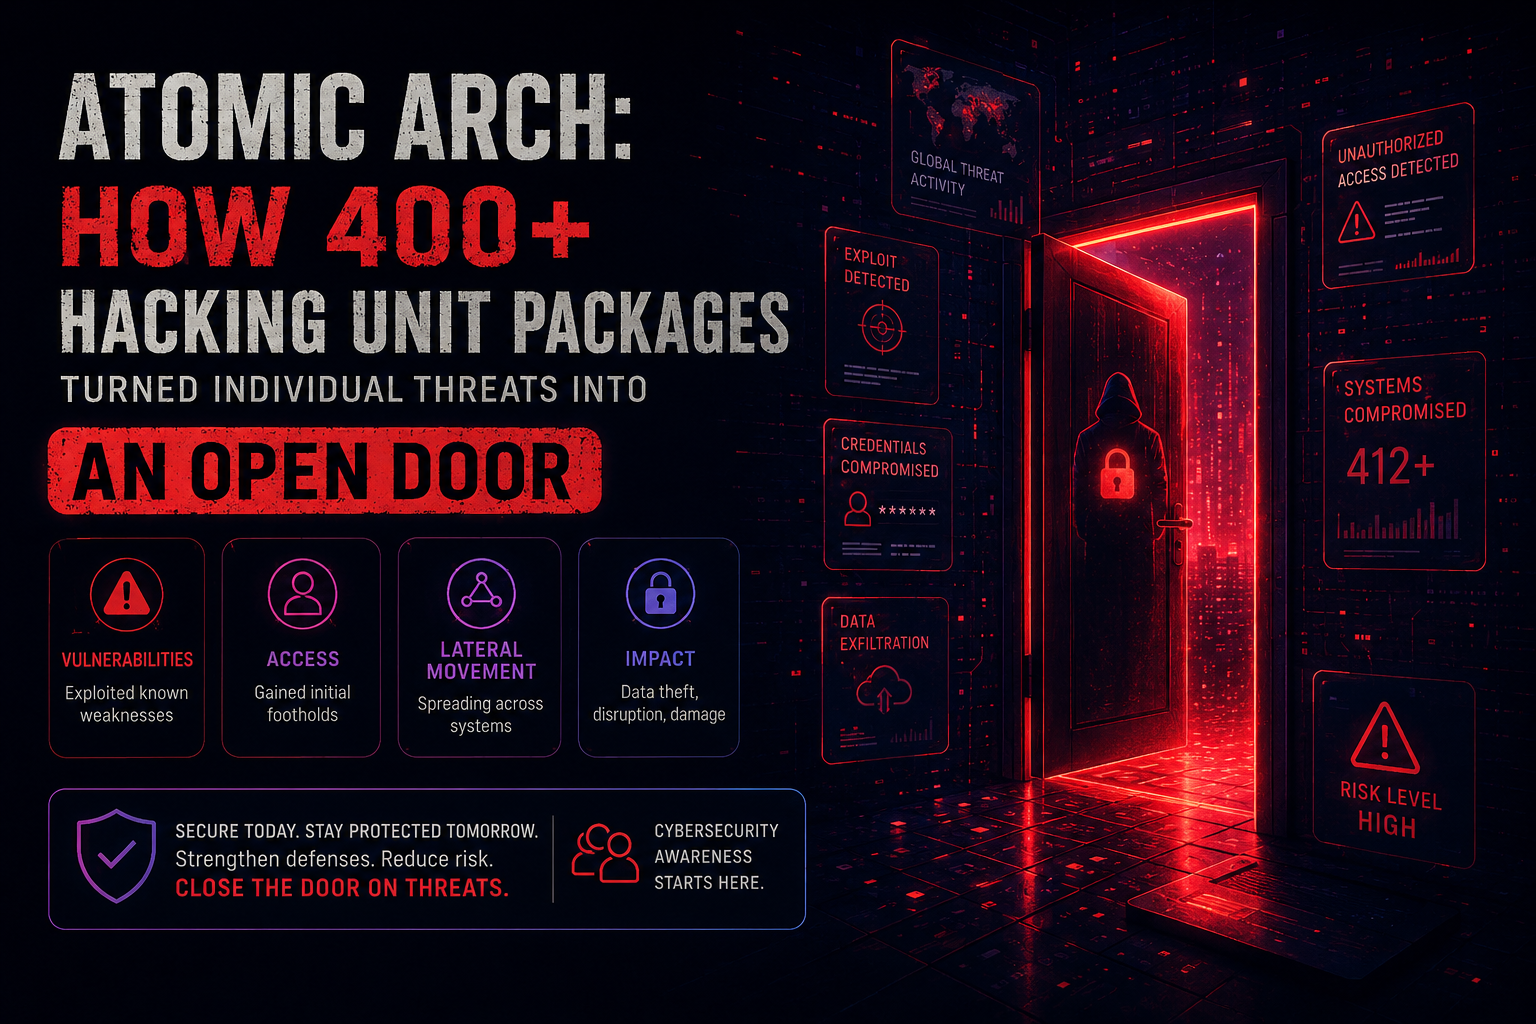
How over 400 hijacked Linux packages turned developer machines into an open door for attackers, and the measures needed to protect your ecosystem.
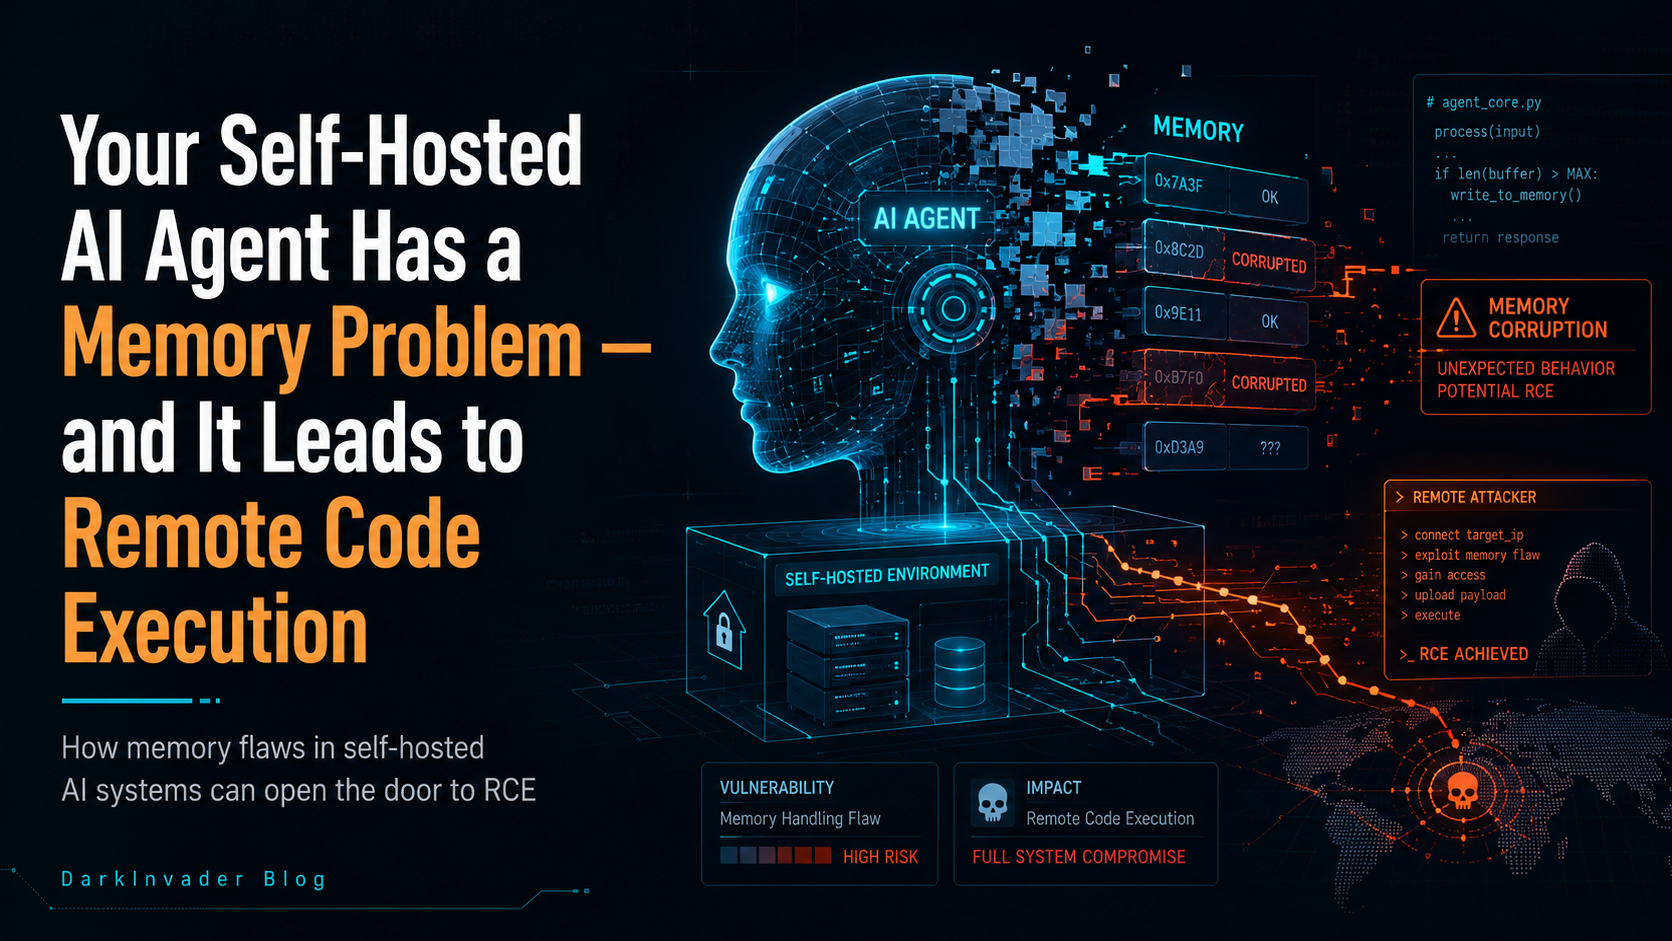
Explore how memory issues in self-hosted AI agents lead to vulnerabilities like remote code execution, and discover strategies to mitigate these risks.
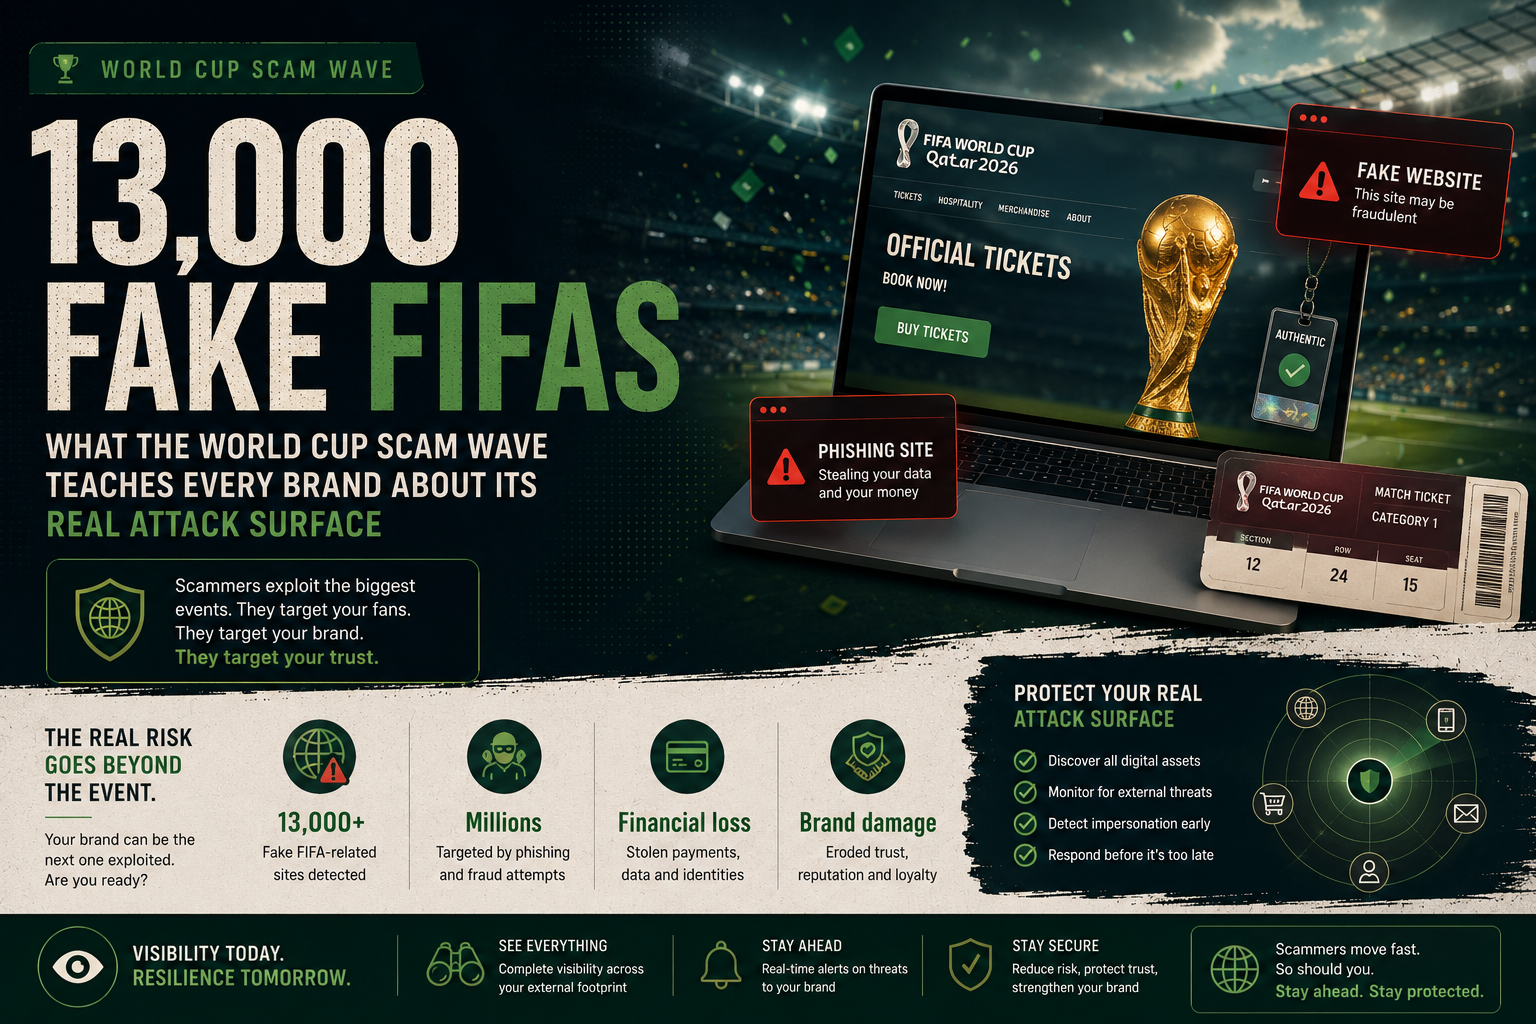
Explore how the World Cup scam wave reveals vulnerabilities in domain protection, and learn effective EASM strategies for brand safety.
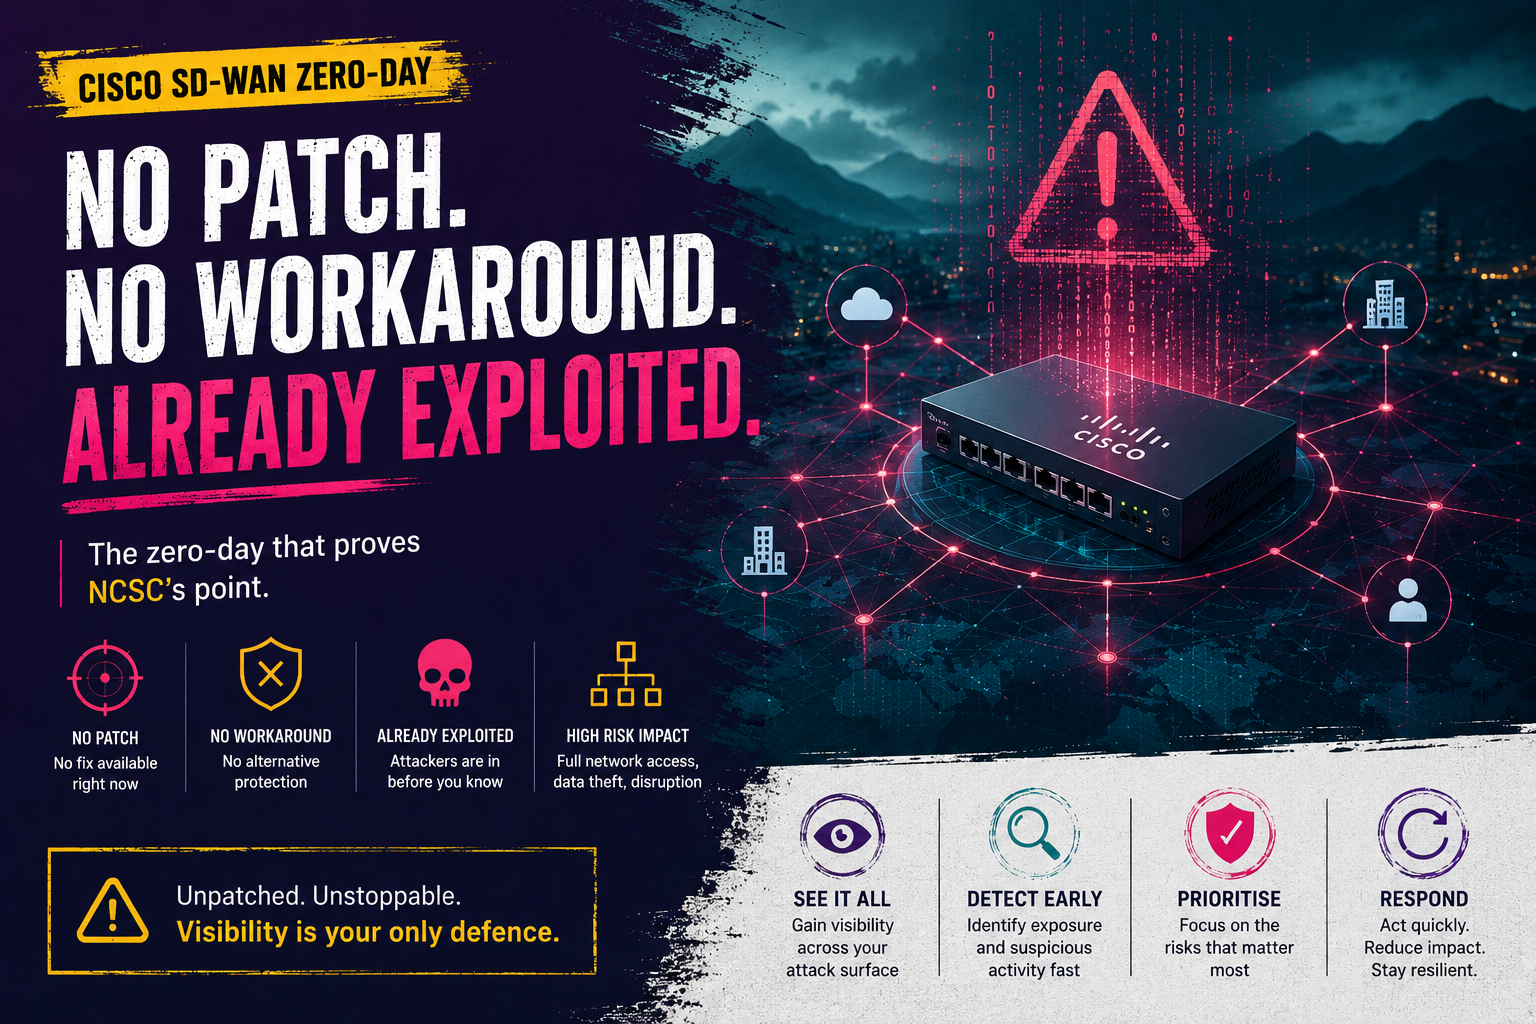
A zero-day vulnerability in Cisco’s SD-WAN has been exploited, stressing the urgency of proactive cybersecurity measures as per NCSC’s warnings.
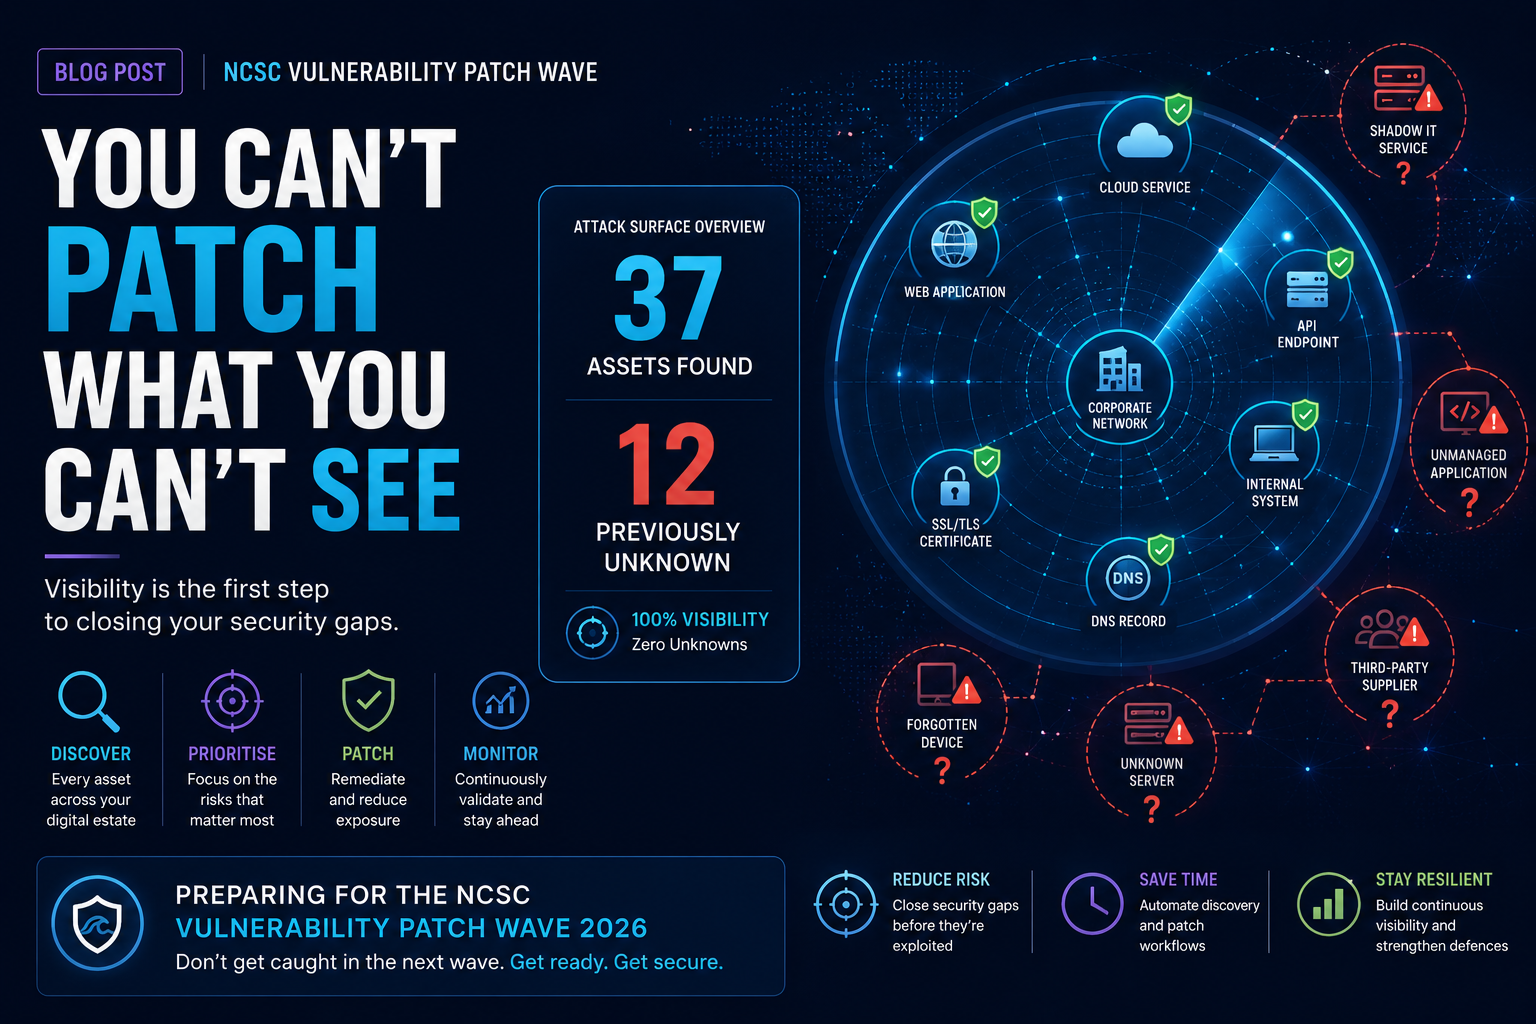
The NCSC's Vulnerability Patch Wave campaign explained: why visibility and prioritisation of your exposed assets are key to effective patching.
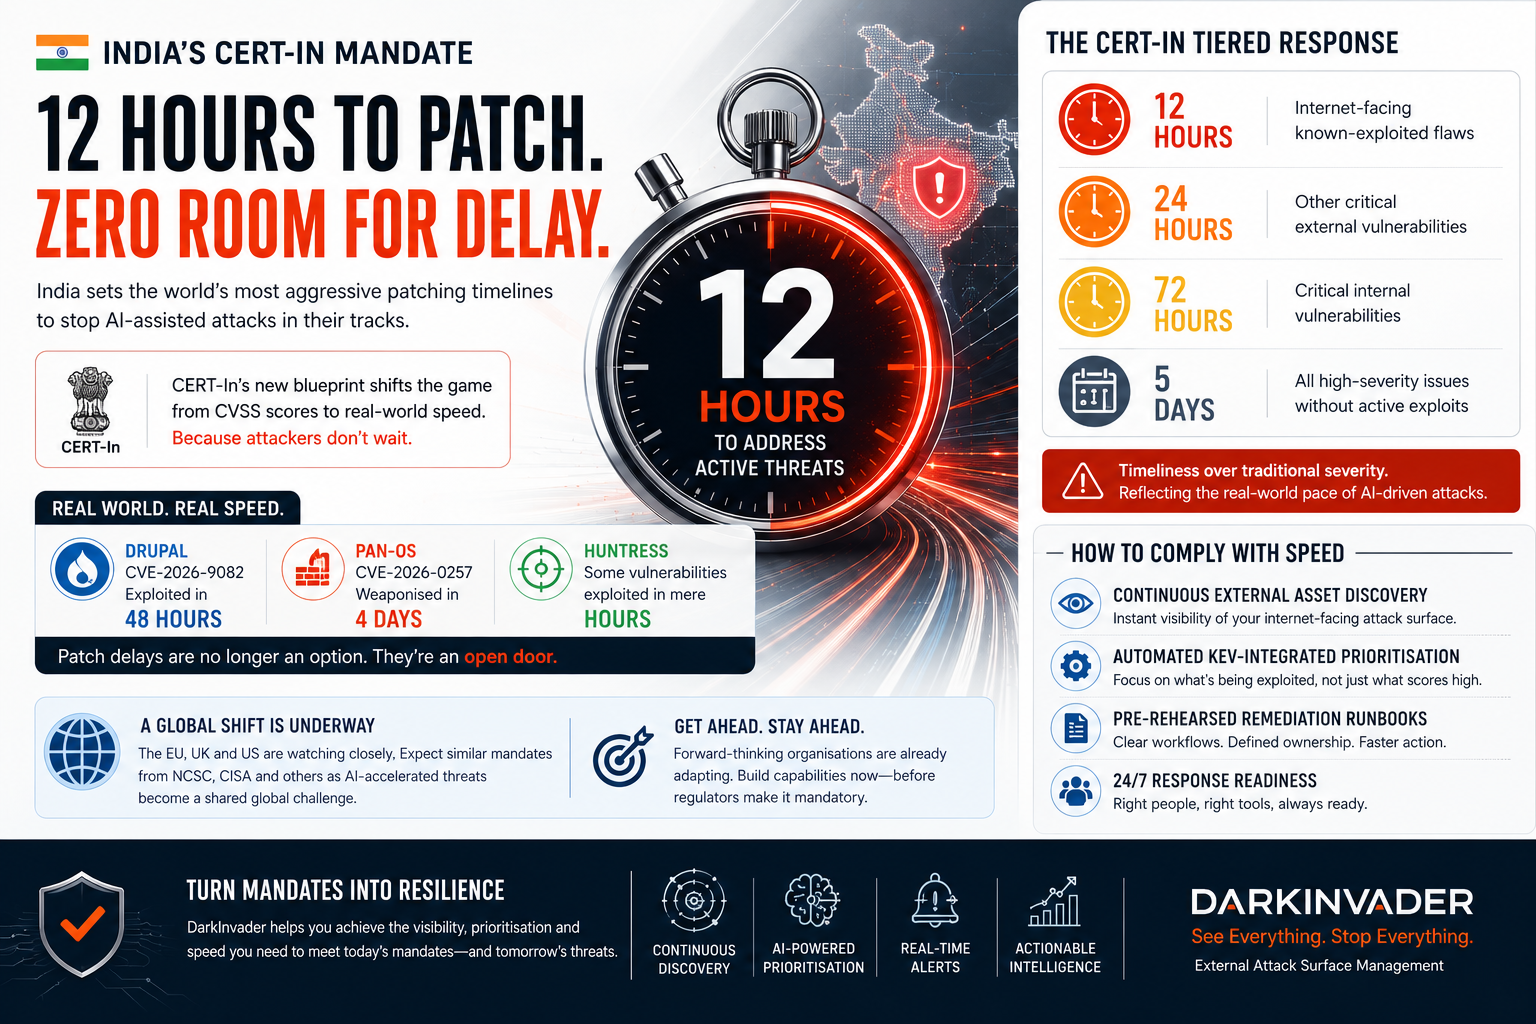
India’s CERT-In introduces a 12-hour critical patching mandate, reshaping global cybersecurity protocols in response to AI-driven threats.
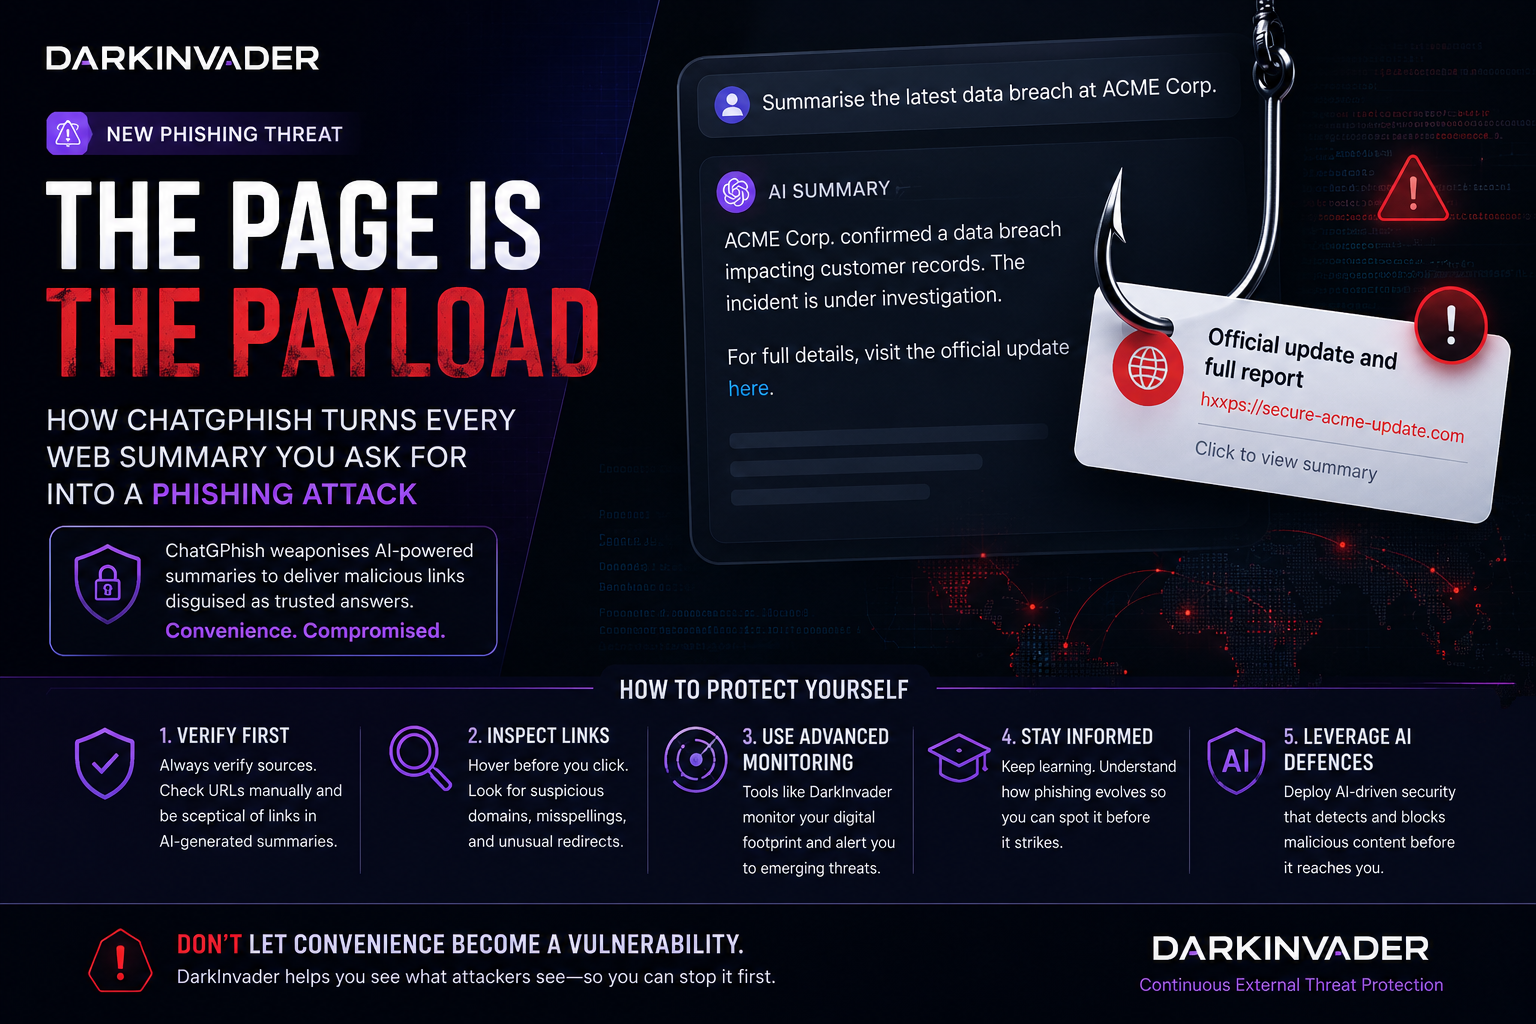
Explore the emerging threat of ChatGPhish, a phishing attack exploiting AI-generated summaries, and learn how to protect yourself.
A Dutch raid uncovered 17 million routers used to disguise cybercrime as ordinary home traffic. Learn how the scheme worked and how to protect yourself.
Explores CVE-2026-0257, a critical vulnerability in VPNs that could allow forged cookie attacks, posing serious security threats.
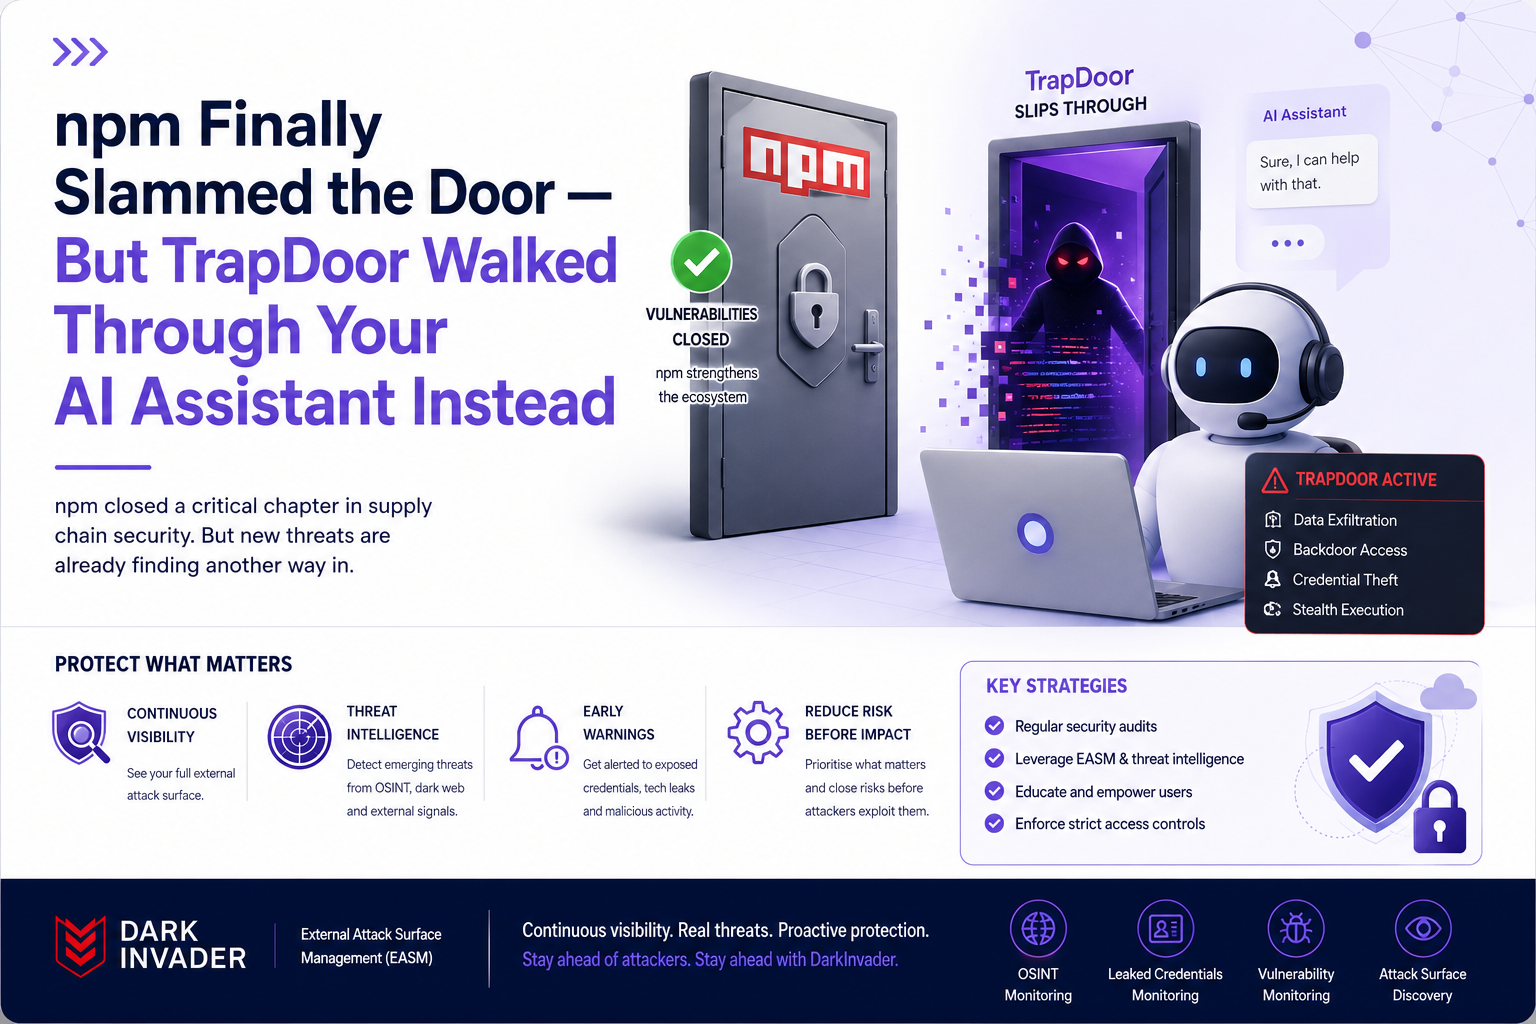
npm has tightened its security, but the TrapDoor threat now targets AI coding assistants instead. Learn how it works and how to protect your estate.
An analysis of the May 2026 GitHub breach, highlighting the vulnerabilities it exposed and lessons about software security.
CVE-2026-9082 is a critical Drupal vulnerability. Exploitation began within 48 hours of disclosure. Act now to protect your sites.
Most remediation programmes never verify that a vulnerability fix worked. Learn the risks of this verification gap and a framework to close it.
What 45 days of monitoring your own tools reveals about your real attack surface, from hidden vulnerabilities to gaps in your security measures.
Cybersecurity predictions for 2026 and why External Attack Surface Management (EASM) will play a central role in shaping digital security.
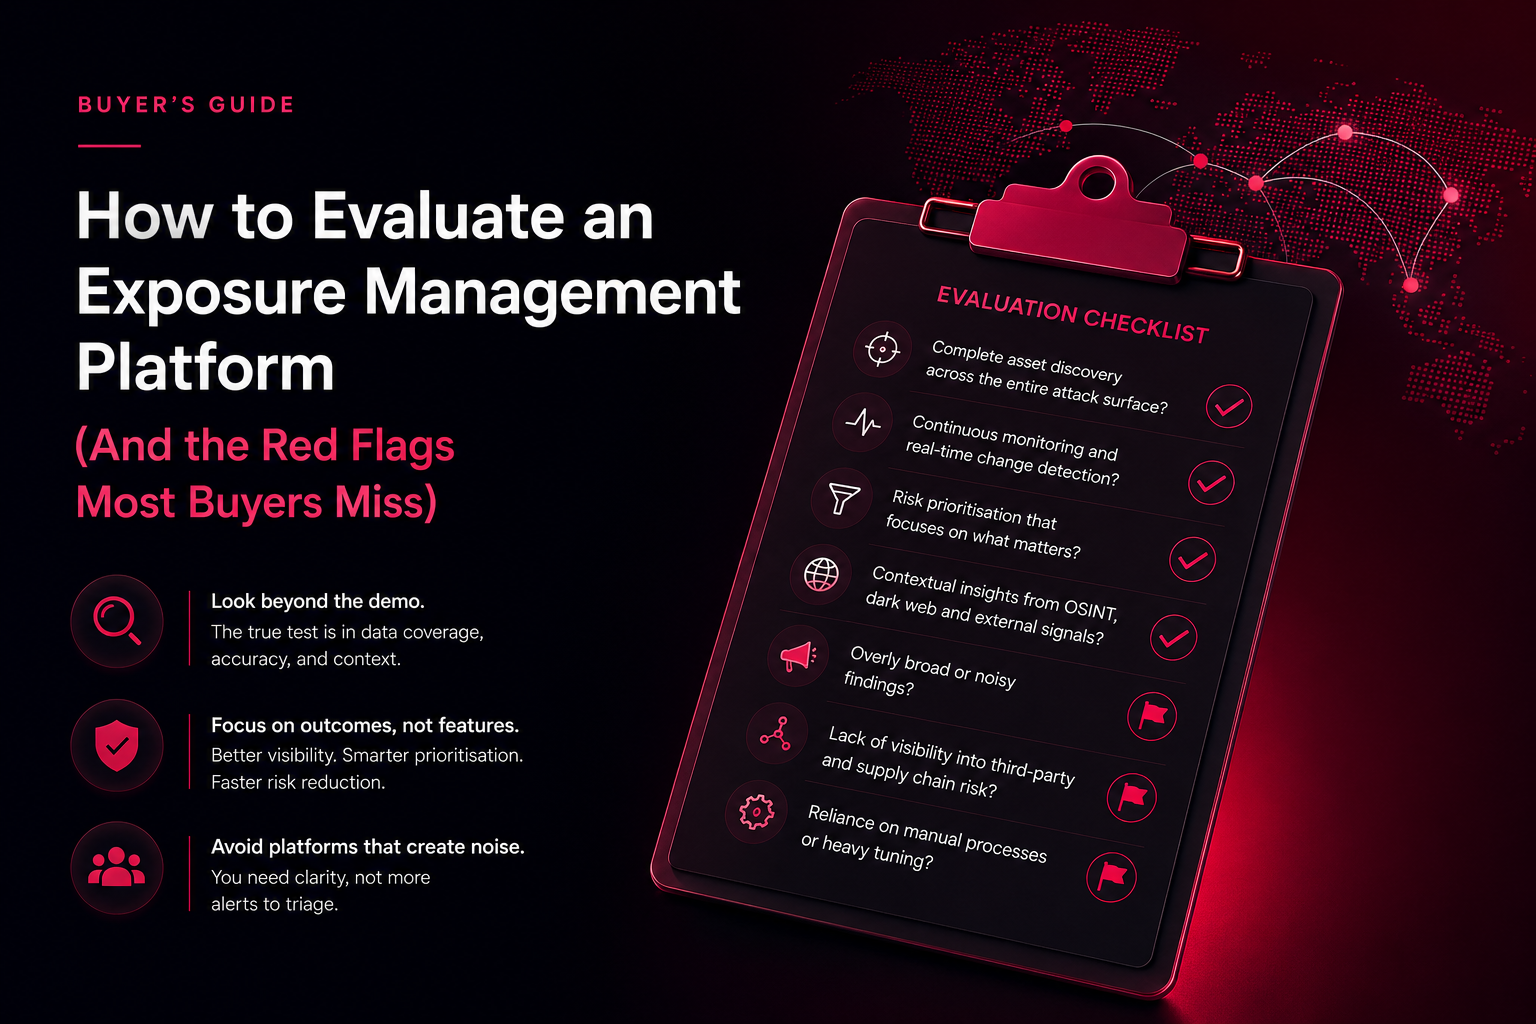
A contrarian buyer’s guide to evaluating exposure management platforms, highlighting the critical features and red flags most buyers overlook.
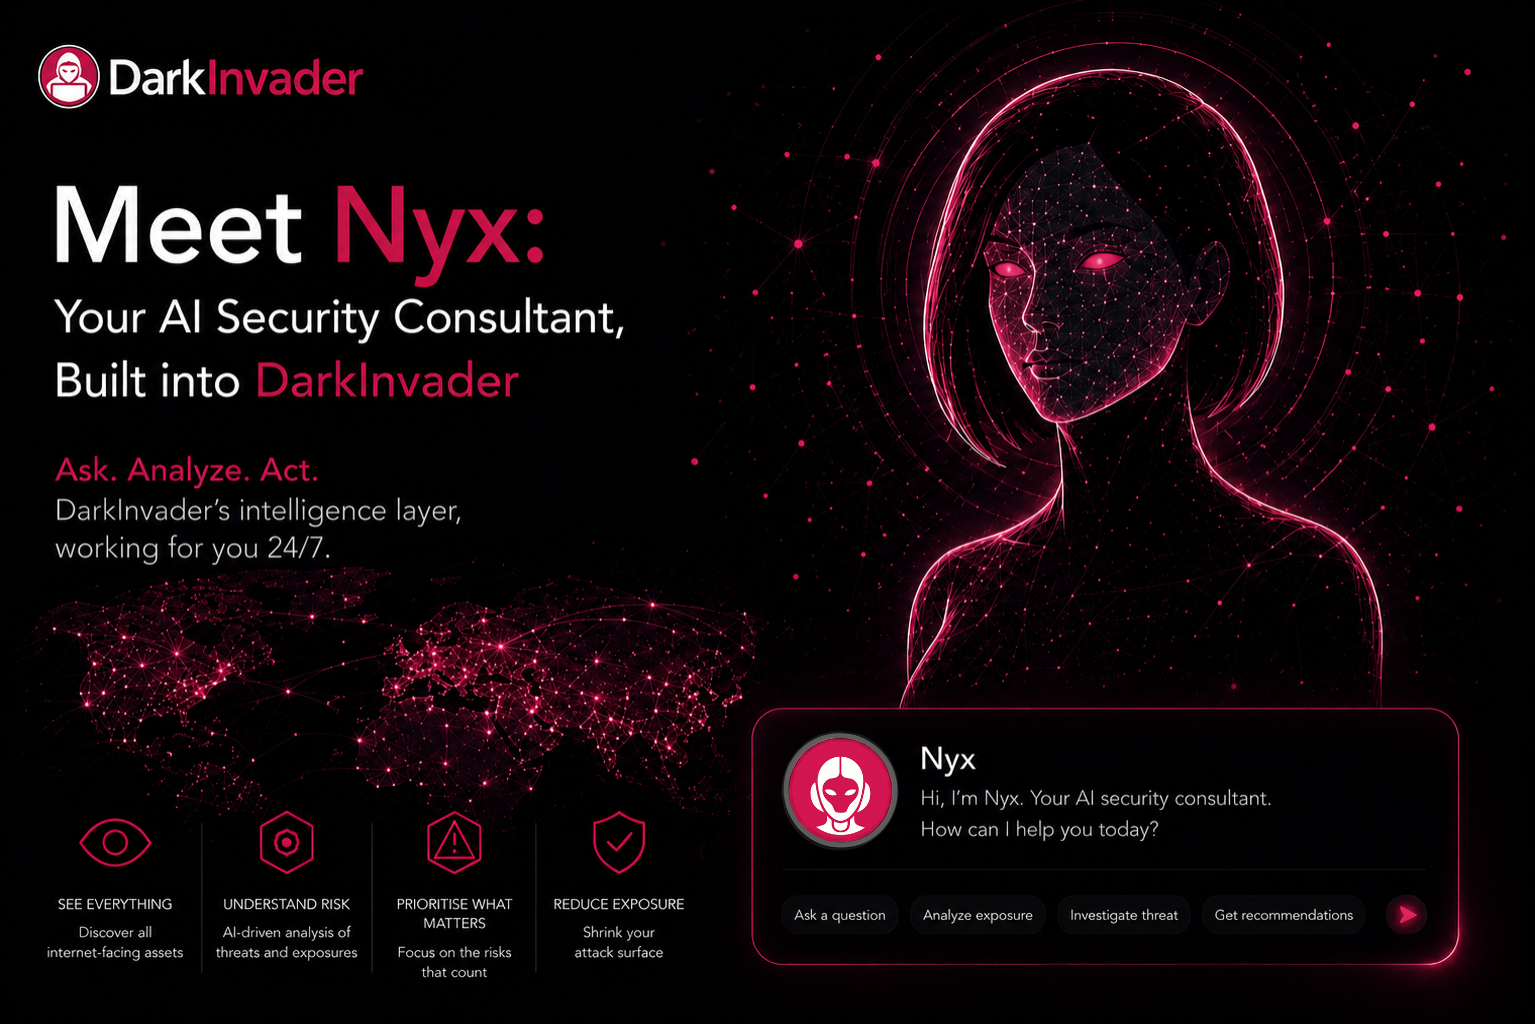
Nyx is the AI security consultant inside DarkInvader. It analyses every risk on your external attack surface, explains it and suggests what to ask next.
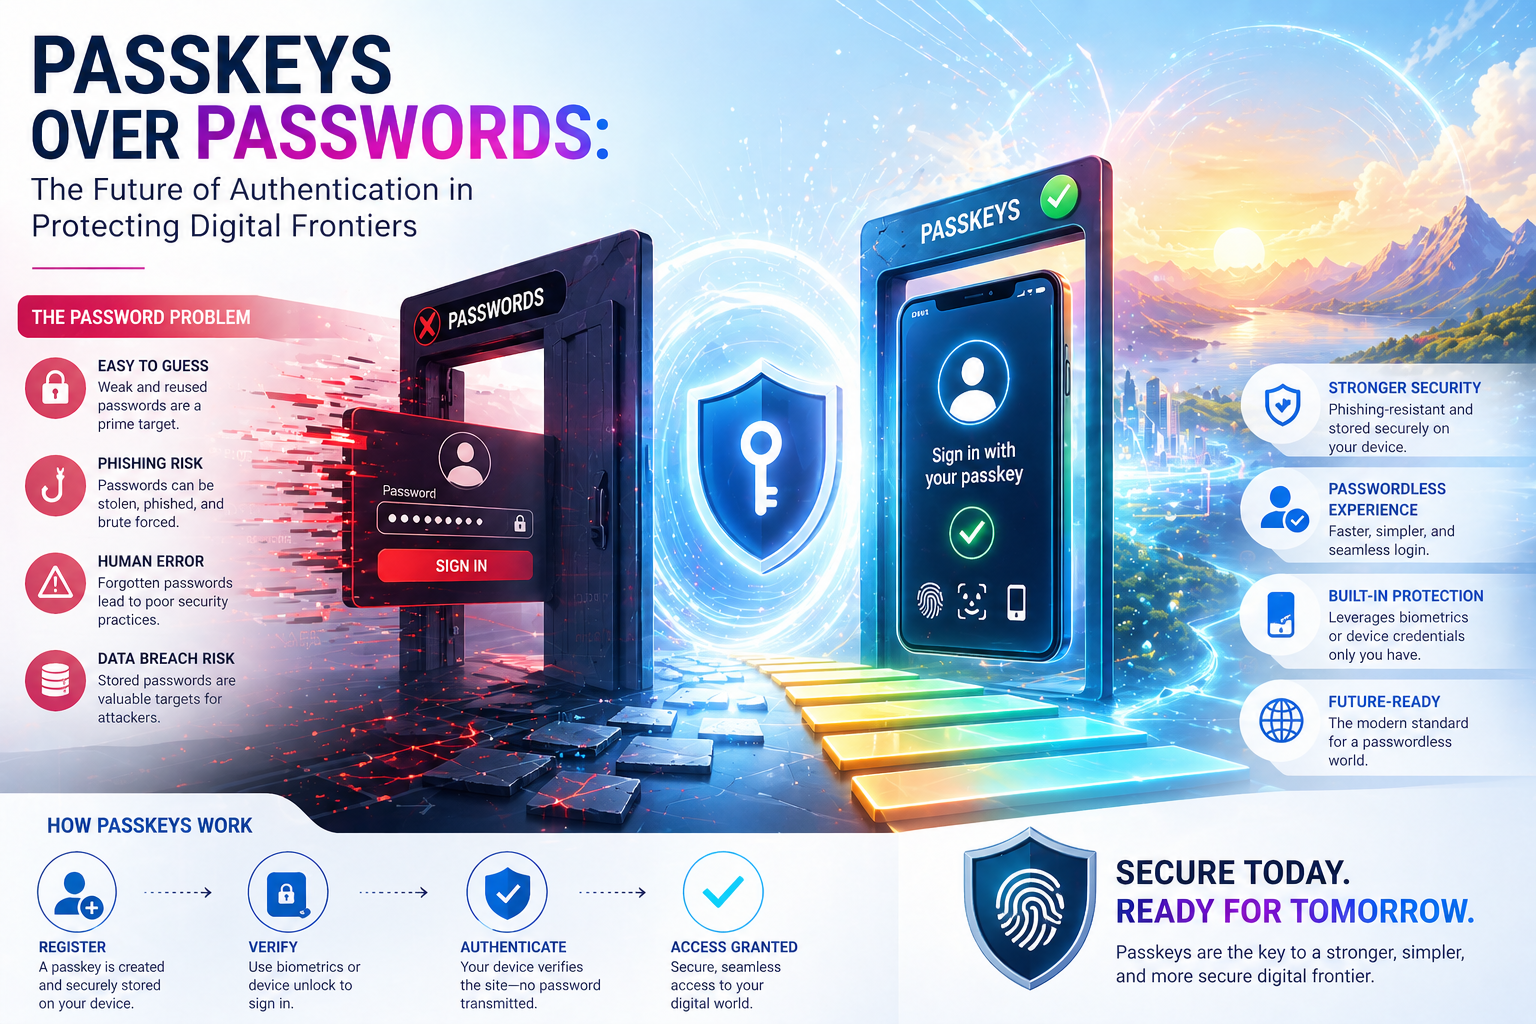
Passkeys replace vulnerable passwords with device-specific cryptographic keys and biometrics, offering stronger security and easier sign-in.
New AI regulations are changing your attack surface. Learn how they affect complexity, monitoring, data protection and vendor risk management.
browse by tag
browse by category
browse by year
free trial
Try DarkInvader Pro free. No payment details required.